BREAKING: GOAT Network and KOSDAQ-listed @Squaretech_HQ have signed an MOU to advance AI agent-powered stablecoin payments in South Korea 🇰🇷
The first focus is a stablecoin payment program for foreign tourists that Square Tech is developing with Lordsystem. It aims to let visitors verify their identity with a mobile passport and pay participating merchants in US dollar stablecoins, and the partners will explore bringing GOAT's AI agent payment technology into it.
Under the agreement, Square Tech will lead business development, merchant partnerships and regulatory engagement in Korea. GOAT Network will provide its AI agent payment technology and Bitcoin-secured network infrastructure, and DAC Labs, the core infrastructure developer behind GOAT Network, will support technical integration, security reviews and network operations.
Full announcement below.
https://t.co/2GEKqtEFSh
KOSDAQ-listed Square Tech has signed an MOU with @GOATNetwork to explore AI agent-powered stablecoin payments in South Korea.
The partnership will leverage GOAT Network’s Bitcoin-secured infrastructure for agentic commerce.
Learn more👇
https://t.co/swmWdV7s33
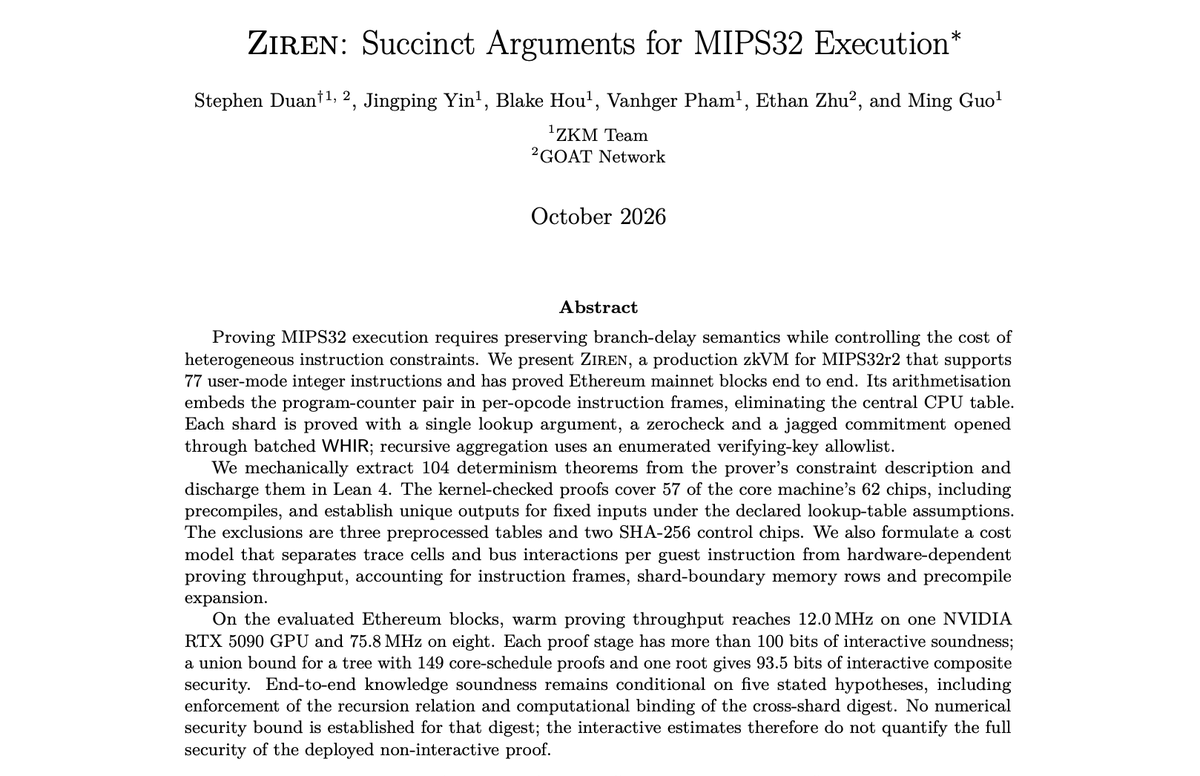
Ziren has proved Ethereum mainnet blocks end to end. The paper puts numbers on the security of those proofs - more than 100 bits of interactive soundness per stage, 93.5 bits composite across a 149-proof tree - and lists the five hypotheses the end-to-end claim still rests on.
What’s about to be superseded is the stated throughput. More on that soon.
Full paper on the IACR Cryptology ePrint Archive: https://t.co/QjjnkkiTZ1
Good thread.
One data point on depth, from our Ziren paper (https://t.co/DVcokUjAFk):
Our recursion is not open-ended (unlimited depth). A block proof is one leaf per shard, a compose tree of arity ≤ 3, and a single root: depth 2 + ⌈log₃ N⌉, about 7 levels for our largest test block. The recursion keys are not inputs either. Every leaf and compose key must sit in a fixed allowlist committed under one root, and the verifier fixes the schedule rather than reading it from the proof. That's a bounded, closed set of verifier circuits, a different risk profile from unlimited-depth recursion with the aggregated vk passed in as input.
We also state the recursion assumption as an open hypothesis rather than a belief. Our composition theorem works in the ROM, where Fiat–Shamir costs log(Q) bits for Q oracle queries: a 150-proof tree has 93.51 interactive bits, 53.5 at Q = 2^40. It holds under hypotheses including that "each node's extractor succeeds on the transcripts its parent's extractor produces".
The item on this list that will take the longest to satisfy is the third: the security of the proof system itself.
That work is slower and less visible than performance work, and it is where most of the effort behind Ziren has already gone.
Big congratulations to the @zksync airbender team for this milestone.
At this point, I consider the battle for speed to be definitively won, and the top priority for zkEVMs should shift fully to security.
To me that means formally verifying
(i) equivalence of the arithmetization to the ethereum spec
(ii) a hard maximum bound on (prover cost) / (amount of gas in block)
(iii) security of the proof system itself
https://t.co/cgtFXBpicf
Something Vitalik hasn't mentioned yet: Ziren is the first zkVM to prove Geth without modifying the Go compiler.
@ProjectZKM's R&D team has worked closely with the @ethereumfndn on it for around a year.
The speed battle Vitalik calls won was fought almost entirely on Rust clients. Ethereum's most widely used execution client is written in Go, and proving it is a different problem - Ziren patches the Go runtime's garbage collector and scheduler to do it.
If the top priority is now security - for Ziren it always was - then prover-side client diversity belongs on that list. The Foundation has spent years on client diversity for Ethereum itself; proofs that all run through one client reproduce the monoculture problem one layer up.
Congratulations to @zksync!
Also would love to mention Ziren V2 @ProjectZKM here!
1. Ziren are proving Reth and Geth, to make sure the client diversity works for Ethereum protocol. Ziren is the first zkVM proving Geth.
2. Ziren also finished the constraint determinism by Lean4 for its 57 VM chips with 104 theorem proofs.
3. Ziren proof system has >100 interactive proven soundness, within unique-decoding radius.
Decentralized sequencer set
Custom zkVM
Type-1 zkEVM
BitVM3 bridge
Agent economic stack
All built for one reason: commerce, whether human or agent driven, should settle on Bitcoin through decentralized, trust-minimized infrastructure.
https://t.co/nwS9JFR2CI
A note on the ZK-STARK line in Europol’s quantum report, which this piece is right to flag.
The report’s claim: ZK-STARKs validate transactions without revealing key information, limiting what a harvested public key is worth to a future attacker.
Where that holds is the commitments. FRI and the hashing inside a STARK rest on hash functions, which quantum computers weaken but do not break. But, importantly, it stops at the statement being proved and the verifier that checks it.
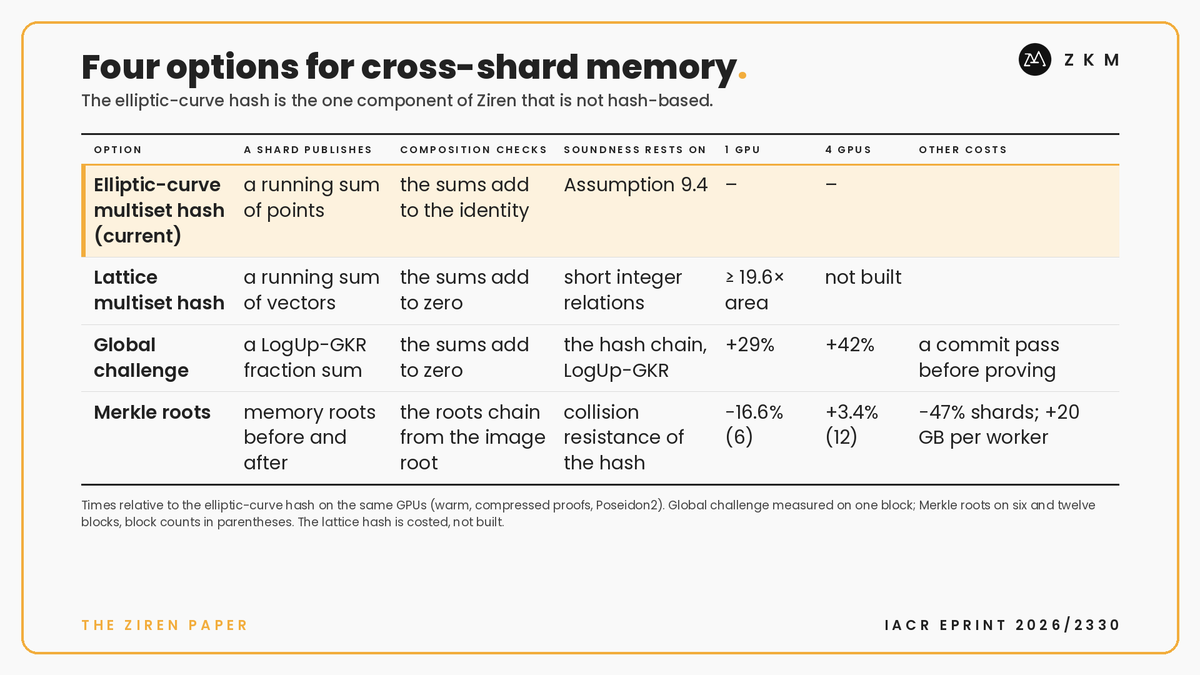
In our own stack, Ziren’s STARKs are wrapped into Groth16 over BN254 so that Bitcoin can verify them, and the wrap is pairing-based, which Shor’s algorithm breaks. Ziren’s memory-consistency check rests on an elliptic-curve hash, tracked openly at https://t.co/HSPJagCDKj, and discrete-log falls the same way.
So Ziren is hash-based today, but not post-quantum until both are replaced. Read any system that cites a STARK as quantum safety the same way: find what the hash layers are carrying.
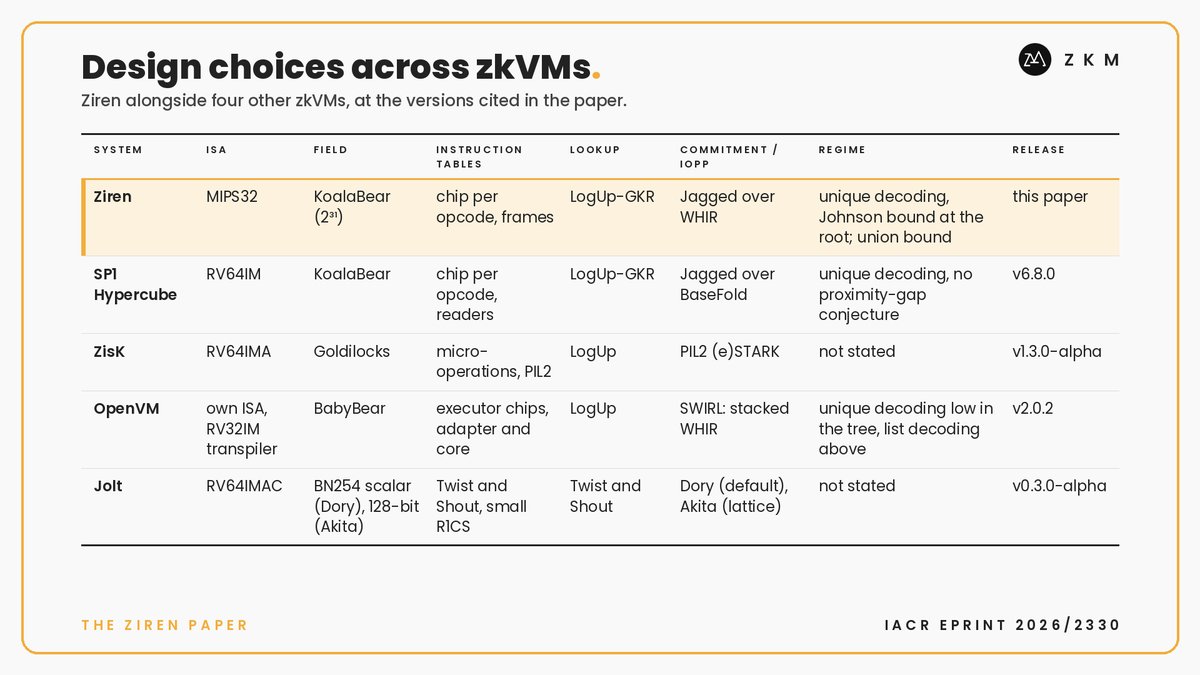
Five zkVMs, compared on their design choices: instruction set, field, instruction tables, lookup argument, commitment scheme, and the basis on which each states its soundness level.
The table is from the Ziren paper, recently published on the IACR Cryptology ePrint Archive (https://t.co/smhYYh5qan).
These are design axes, not a scoreboard: no performance claim follows from them, and soundness levels stated under different regimes are not comparable without the accounting the paper gives alongside it.
The column worth reading slowly is the regime column. Ziren counts query soundness in the unique-decoding regime, uses the Johnson bound at the root, proved rather than conjectured, and states its composite level as a union bound over every proof in a block's tree of about 150.
The full accounting behind the table: https://t.co/ww7TCL6oOW
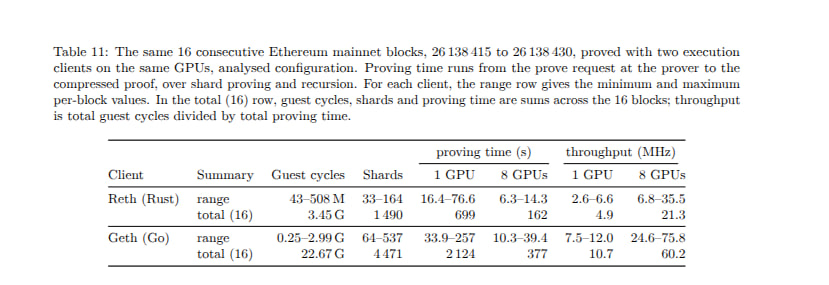
Share some numbers about multi-client proving for Ethereum with Ziren V2.0 @ProjectZKM, which can prove 75.8MHz with 8X5090, and 12MHz with 1X5090.
And the instruction efficiency of Geth/Reth is around 7x, which seems larger than 5 months ago, because we did more guest side optimizations on Reth:
> Witness and trie: arena nodes, compact digest references, borrowed input slices, faster RLP decoding, and fewer allocations and clones.
> Memory and hashing: word-wise comparisons, a cheaper hash-map hasher, and Keccak input buffers built directly, using the stack for short inputs.
> 256-bit arithmetic: multiplication and modular multiplication use zkVM precompiles; division uses hints checked inside the guest.
> Cryptography: syscall-backed BN254 and BLS operations, cached KZG preparation, and accelerated modular exponentiation.
> EVM interpreter: MIPS32 fast paths for gas accounting, stack swaps, and memory loads/stores.
PS. the number in the picture will be updated in our next release of our paper.
@go_ethereum@ethereumfndn
The secure parameters and advanced protocols Stephen is pointing at are public on our side. Ziren proves with hash-based cryptography, its one remaining elliptic-curve dependency is tracked in the open, and the replacement options are measured.
Why a hash-based system is not automatically post-quantum, and what we are doing about the difference, is explained here: https://t.co/ACOHQJsQLt
Can't agree with this more. No matter whether the attacks from PQ or AI, serious crypto projects are always placing more attentions to application of cryptography, more secure parameters, more advanced protocols.
when i create @appliedpqc, the first co-author is a phd from Communication Security, and we also did lots of research on the TLS related PQ updates.
ZKM's new paper, published on the IACR Cryptology ePrint Archive, is a testament to the world-class work @sd_eigen and our R&D team have done on Ziren.
Importantly, we know exactly where we stand on quantum resistance and exactly what the options are. Our highest security priority is a post-quantum secure BitVM3 bridge between @GOATNetwork and Bitcoin.
Ziren: Succinct Arguments for MIPS32 Execution has been published on the IACR Cryptology ePrint Archive.
→ https://t.co/QjjnkkiTZ1
It is a complete design reference, covering the proof system, the formal verification of the machine itself, and the production record.
Ziren is a CPU-less chip architecture: every executed instruction is one row of its opcode's chip. Each shard is proved with one lookup argument and one zerocheck, then a jagged sumcheck reduces tens of thousands of columns of differing heights to a single evaluation, opened with one batched WHIR proof. A recursion tree composes the shard proofs under an enumerated allowlist of verifying keys.
All 104 extracted determinism theorems are proved in Lean 4, generated from the same constraint description the prover evaluates, and the security analysis states its bounds with every assumption listed.
The same machine runs in production. It proves 77 user-mode MIPS32r2 instructions, has proved Ethereum mainnet blocks end to end, and reaches up to 7.3 MHz on a single RTX 5090, scaling to 24 MHz across four.
Securing Ziren has been and continues to be an extensive effort. Our deepest thanks go out to @ethereumfndn, @ConsensysAudits, and @VeridiseInc for working with us so closely on it.
Code: https://t.co/njWKvtM9fF
Docs: https://t.co/0qiG7Aaulm
Happy to share our latest work on Ziren @ProjectZKM@GOATNetwork. Feedback welcome!
A summary:
1. A new proof system based on Jaggled reduction and WHIR(including recursion proof over binary field and Blake3). Acknowledgements to SP1 team and Plonky3 contributors.
2. 4x proving efficiency, 10x emulation efficiency improvement over previous v1.2. Speedup is happening every day with AI assistant.
3. >100-bit proven security
4. A fully Lean 4 assisted constraint determinism proof, covering 104 chips.
5. A complete end-to-end zkVM design reference.
A zkVM constraint system is correct when every execution admits exactly one valid trace - no forged proofs, no rejected valid runs. That is the criterion this ACM CCS paper formalizes, and the bar Ziren was measured against.
Of the five production zkVMs evaluated, Ziren posted the highest verification coverage and no critical findings. And as of v2.0, now merged, constraint determinism checks in Lean4 are built into the Ziren repo.
Congrats to @Koukyosyumei and the @Columbia team. Independent work like this makes every zkVM stronger.
My first-author paper, "Efficient Branch-and-Bound Testing and Verification of zkVMs", has been accepted to ACM CCS
If you’ll be in Hague this November, I’d love to chat! The arXiv version is already available online: https://t.co/m3c6kq8dLU
@Koukyosyumei Congrats! thanks for the work on Ziren @ProjectZKM, also happy to share that our v2.0 release is merged today, and the constraints determinism by Lean4 is built-in in Ziren repo now.