Moment some Nigerian police officers seized a man’s earrings for no reason but didn’t know they were being recorded💔
Policeman: Why did you use earrings? It’s a crime to do so, you’re not a woman. Go there and meet my Oga
*Man Proceeds to meet the superior*
Superior police man: Are you a woman ? Are you a musician? Are you a footballer? Remove those earrings and put it in my hands
What the hel is wrong with Nigerian police ??is this not abuse of power and theft ? 💔💔💔
If white people are evil, how come they allow African immigrants to win elections and join their government?
No Arab or Asian country will ever do that.
You fools hate the wrong people.
You go creche
You go nursery school
You go primary school
You go secondary school
You go university
You do masters
All to become an APC slave
Omo, akọsẹjaye ẹ o da rara
Imagine a US President filing a suit against the FBI to stop them from releasing his criminal records ahead of a presidential election...
Omo! We too dey tolerate for Nigeria.
CNN claims the attempted bombing in NYC was directed at Mamdani
It was literally two isis islamists who shouted “allahu akbar” and threw the bombs at anti-Mamdani protesters
This attempt to rewrite history is INSANE
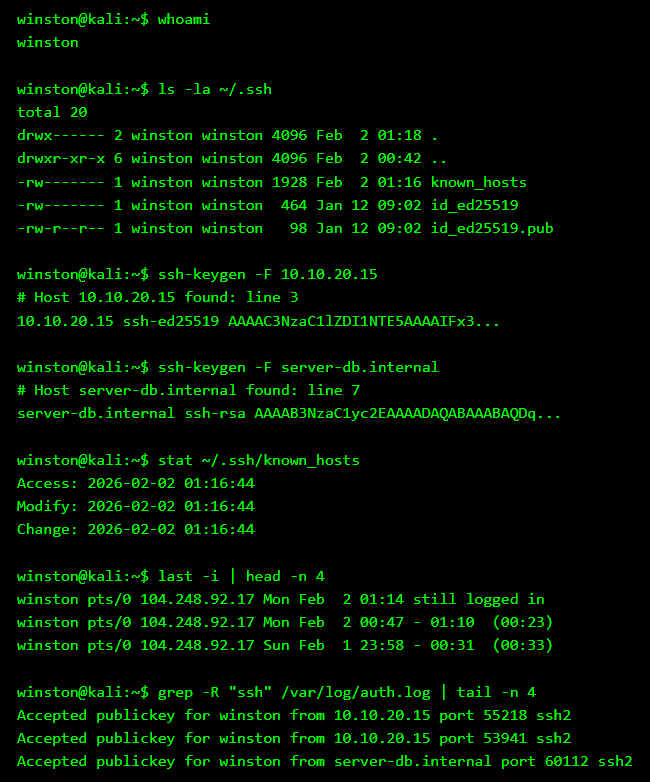
Linux records SSH trust in a quiet but powerful way. Every time a user connects to a new server, the system stores the server’s fingerprint in the known_hosts file. This file is not a log and is rarely cleared, which makes it a goldmine during investigations. Even if session logs are wiped, known_hosts still reveals where the user has connected before.
Attackers who move laterally across a network often forget about this file. They might delete command history, rotate logs, or remove binaries, but SSH trust entries remain unless deliberately scrubbed. Each entry ties a user account to a specific IP address or internal hostname, effectively mapping the attacker’s path through the environment.
In the terminal below, the investigator(me) inspects the .ssh directory and finds a recently modified known_hosts file. Using SSH tooling, specific hosts are queried and confirmed as trusted by the system. Timestamps align with login activity, and authentication logs corroborate successful SSH access to internal servers. Even without full session logs, the evidence shows where the user went, when they connected, and which systems were trusted exposing lateral movement attackers assumed was invisible.
@johnnymaga I'm a Nigerian. I like beans.... But even I wouldn't eat this. Too dry, no oil... It's just wrong on so many levels I can see in this video...