Silk Typhoon is an espionage-focused Chinese state actor whose activities indicate that they are a well-resourced and technically efficient group with the ability to quickly operationalize exploits for zero-day vulnerabilities in edge devices. https://t.co/1DT3NfRi2O
🚨 THIS JUST IN: The ultimate #Linux guide is here!
Created by @4enzikat0r & @tazwake this must-have forensic poster is your go-to resource for detecting rootkits, tracking attacker persistence, & analyzing timestamps.
📄 Get your FREE copy! https://t.co/ej87CYkYc7
#DFIR
This is a brilliant repository that demonstrates typical PowerShell Obfuscation techniques.
It should be a #mustKnow reference for every blue teamer.
[Repo] PowerShell Obfuscation Bible
🔗 https://t.co/FKAKHtM4Oa
#CyberSecurity#BlueTeaming#PowerShell
🚀 Big News! We launched CISA Learning, a centralized platform for all things #CyberTraining! With classroom courses, virtual sessions, and self-paced modules, CISA Learning supports our evolving cybersecurity workforce. Learn more: https://t.co/mapQOypTv7
#INCRansomware evolves rapidly by leveraging vulnerabilities in Netscaler ADC & Gateway for initial access.
Our latest #RansomwareSpotlight provides valuable insights into this evolving threat: https://t.co/Nbobv4W3k6
⚛️ https://t.co/cZhrIXPqRm got a facelift! Our new #AtomicRedTeam testing interface features improved search and filtering, easier test execution, and more!
📽️ Here's a guided tour: https://t.co/hgdLbFOGFZ
NEW: Google Chrome's new application-bound encryption has shifted the stealer landscape, forcing malware authors to implement new features to bypass the control and steal cookies. https://t.co/AHsvhwNlt7
🚨 SaaS Misconfigurations Are a Major Threat!
With so many apps and integrations, the risk of data breaches has never been higher. Here are 5 common misconfigurations you need to address NOW!
Read: https://t.co/fas5A5eljq
#SaaSSecurity#DataProtection
Sophos detailed to me its 5-year cat-and-mouse game with Chinese hackers repeatedly exploiting its firewalls. The company resorted to installing spy "implants" on devices the hackers were testing on—tracing them to a university and contractor in Chengdu. https://t.co/L75jQS71dN
A new piece of information I came across in this reporting: @zachxbt and other investigators were able to recover $12 million of the $15 million Caesar's paid to the Scattered Spider ransomware group last year.
That's very likely the biggest-ever clawback of a ransom payment.
ChromeLoader and SocGholish remained our top threats in September, but a new technique stood out, tricking users into copying a PowerShell script, pasting it into Windows Run, and executing malicious code that leads to LummaC2: https://t.co/4yJGznAsBR
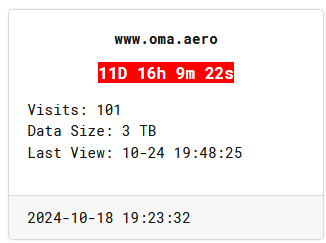
🚨Cyberattack Alert ‼️
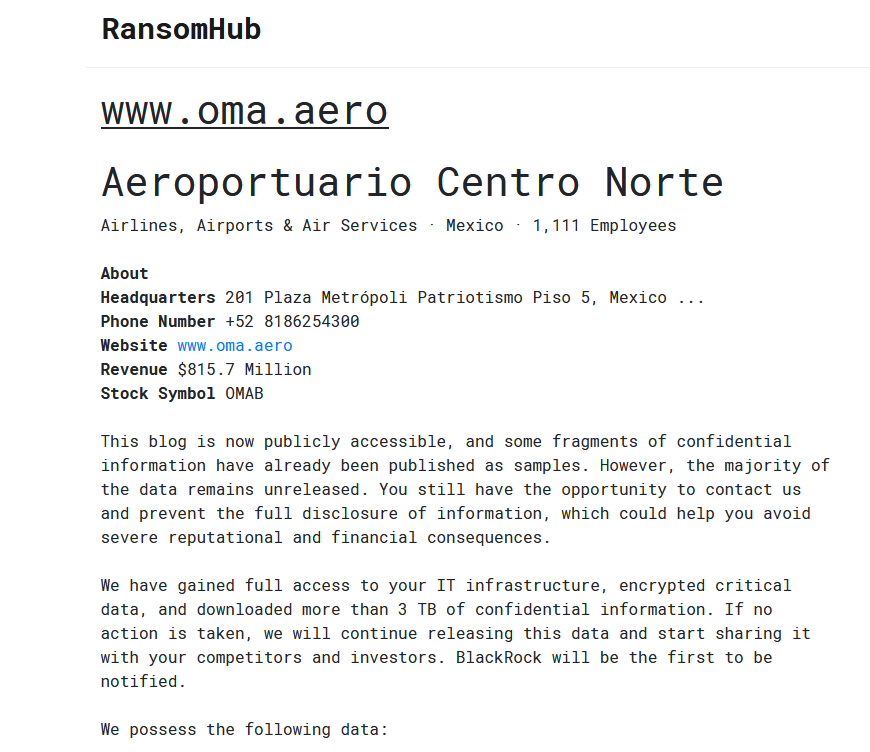
🇲🇽Mexico - Grupo Aeroportuario del Centro Norte (OMA)
RansomHub ransomware group claims responsibility for the attack on Grupo Aeroportuario del Centro Norte (OMA).
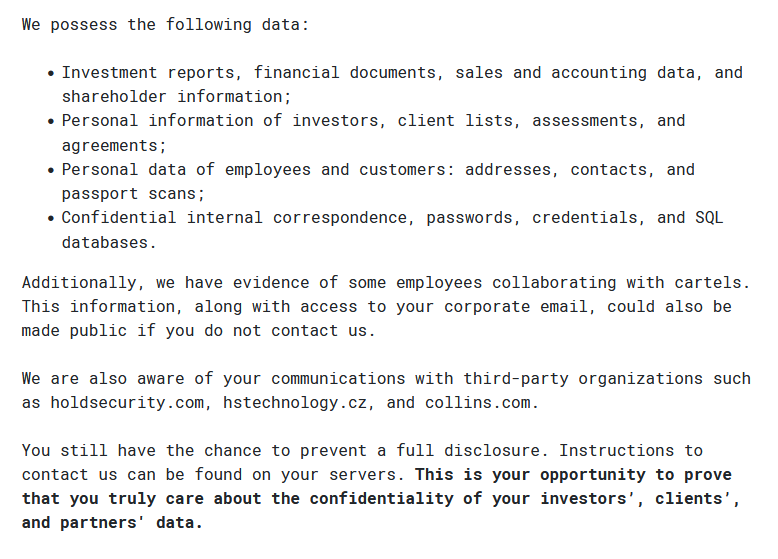
Allegedly, exfiltrated data includes investment reports, financial documents, sales and accounting data, and shareholder information. Personal information of investors, client lists, assessments, agreements, and personal data of employees and customers—such as addresses, contacts, passport scans, confidential internal correspondence, passwords, credentials, and SQL databases—were also compromised.
Additionally, the group makes bold claims, stating they have evidence of some employees collaborating with cartels.
Ransom deadline: 2nd Nov 2024.
A new advanced Qilin #ransomware variant, Qilin.B, features enhanced AES-256-CTR and RSA-4096 encryption, making recovery nearly impossible without the attackers' keys.
Read → https://t.co/ljA8lZfTRG
#malware#infosec




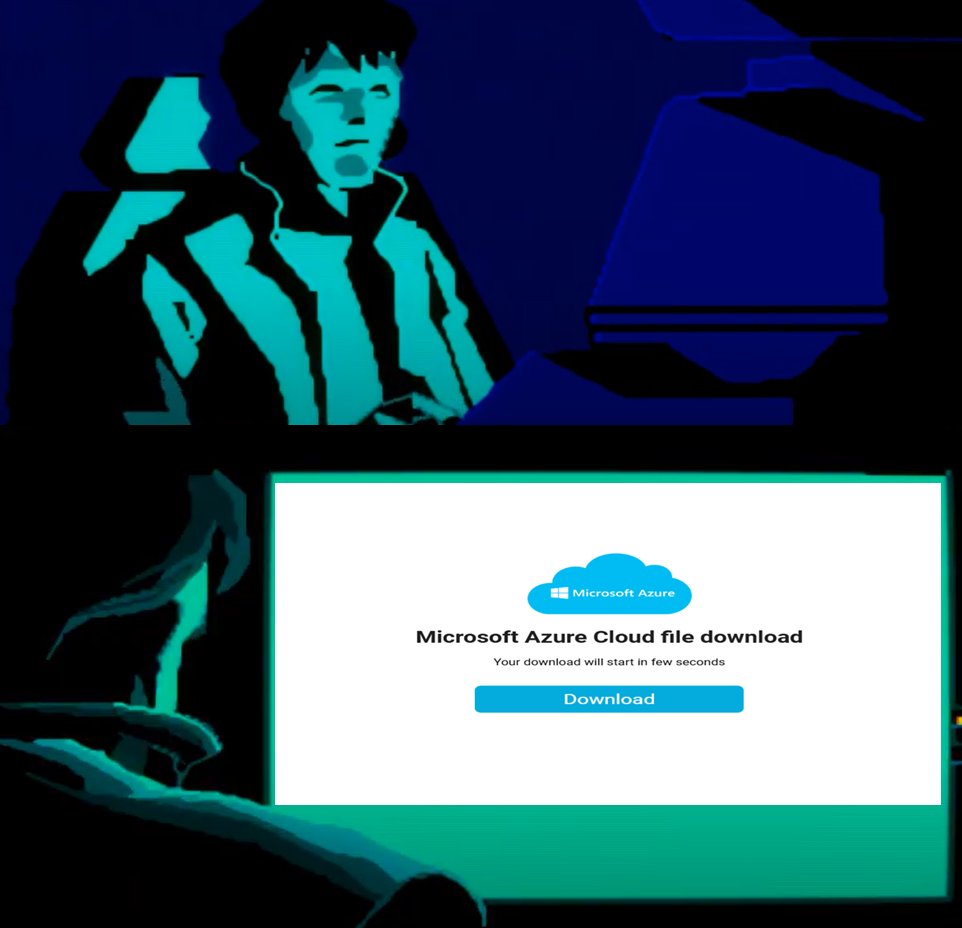
![JAMESWT_WT's tweet photo. ZIP>SVG>URL>ZIP>PW LOP852>#AsyncRat
⛔️C2
powerupsnew.]dynuddns].com
Drop
⛔️https://i0004.clarodrive.]com/s/siEsdDALjZ665wE/
Samples
❇️https://t.co/lxtwCNzqtD
AnyRun
🔱https://t.co/dp6wLeVJsN https://t.co/Z3ZlGjzEDS](https://pbs.twimg.com/media/Gcgt8Q4XYAAeTHC.jpg)
![JAMESWT_WT's tweet photo. ZIP>SVG>URL>ZIP>PW LOP852>#AsyncRat
⛔️C2
powerupsnew.]dynuddns].com
Drop
⛔️https://i0004.clarodrive.]com/s/siEsdDALjZ665wE/
Samples
❇️https://t.co/lxtwCNzqtD
AnyRun
🔱https://t.co/dp6wLeVJsN https://t.co/Z3ZlGjzEDS](https://pbs.twimg.com/media/Gcgt7qFXYAAhywp.jpg)







![JAMESWT_WT's tweet photo. ZIP>SVG>URL>ZIP>PW LOP852>#AsyncRat
⛔️C2
powerupsnew.]dynuddns].com
Drop
⛔️https://i0004.clarodrive.]com/s/siEsdDALjZ665wE/
Samples
❇️https://t.co/lxtwCNzqtD
AnyRun
🔱https://t.co/dp6wLeVJsN https://t.co/Z3ZlGjzEDS](https://pbs.twimg.com/media/Gcgt8wwXwAE2n6D.jpg)


