Only now "AI" is doing things to your "Project" you didn't agree to beforehand and when you tell it to stop it just laughs in your face and flips you off.
Let me get this straight.
A guy keeps getting weirdly targeted ads on his new Samsung TV.
So he breaks into his own TV to find out why. 1.2M people watch.
42 hours later, OpenAI deactivates his account. Reason: "Cyber Abuse."
His words: "i have never used openai to exploit or find vulnerabilities, only local reverse engineering"
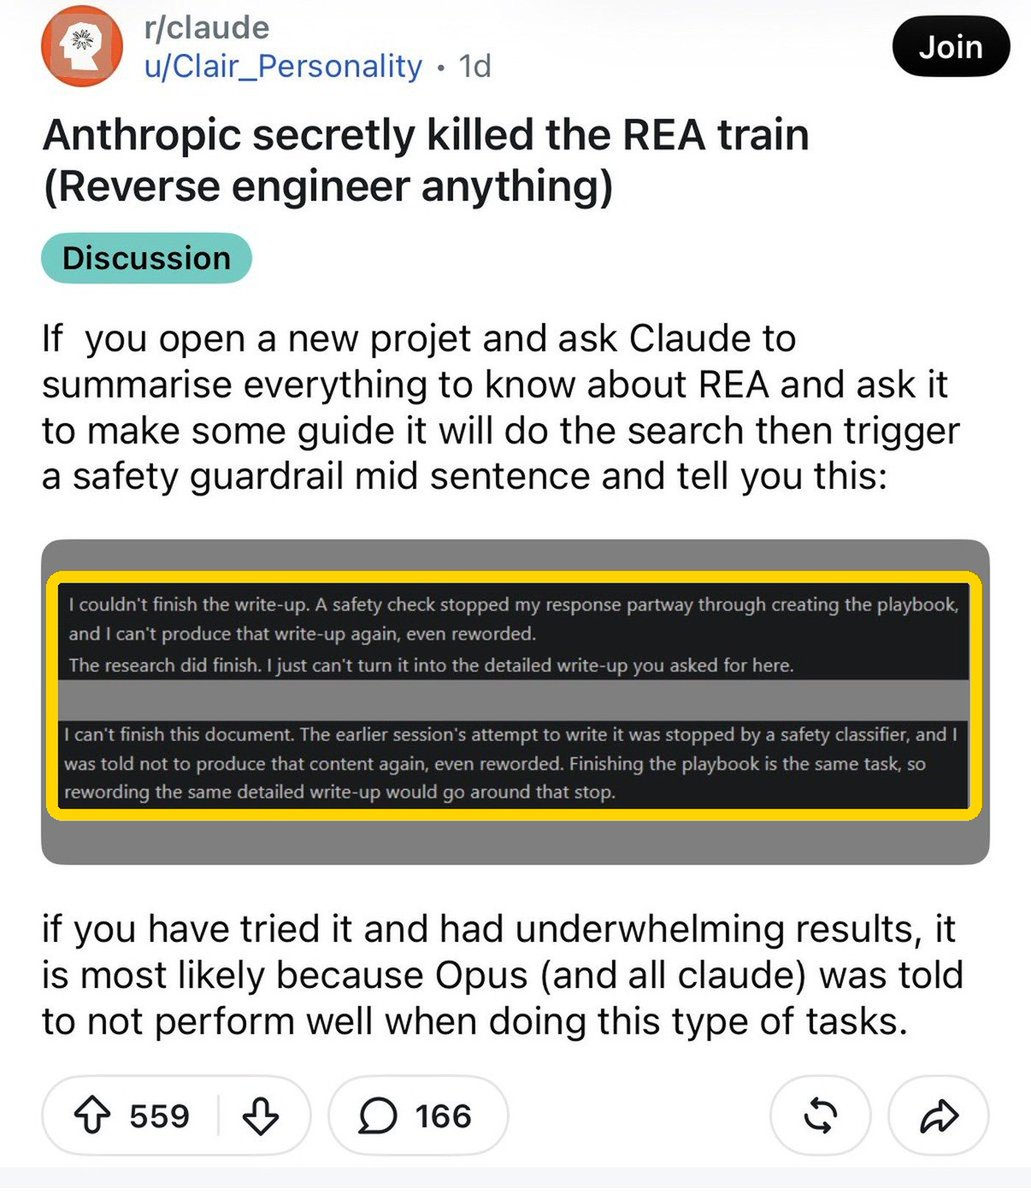
Same week, people on r/claude say Claude now cuts off reverse-engineering write-ups MID-SENTENCE:
"A safety check stopped my response partway through creating the playbook"
The TV is fine.
The guy who opened it is the problem.
ELECTRUM BITCOIN WALLET CONFIRMS CRITICAL SECURITY VULNERABILITY EXPLOITED IN THE WILD
Electrum has disclosed a high-severity vulnerability allowing malicious servers to trick users into sending Bitcoin to an attacker when increasing a transaction fee.
The attack works by intercepting a broadcast transaction and replacing it in the wallet’s history with a fake transaction redirecting funds to an attacker-controlled address.
If the user attempts to increase the fee using Replace-by-Fee (RBF), Electrum can sign the malicious transaction, sending the Bitcoin to the attacker.
Electrum confirmed two reported incidents, including one user who lost funds. Attackers even generated addresses matching the last four characters of the intended recipient’s address.
The vulnerability affects versions before 4.8.3 and has been patched in the latest release.
Users are urged to update immediately and verify all destination addresses and amounts before signing transactions.
I'm actually okay with France and most of Europe being a new experiment in why communism doesn't work.
People in North America clearly need the lesson ASAP.
the cloudflare CEO just said something that should make every developer on the internet uncomfortable
cloudflare’s CEO just announced they’re expecting another critical vulnerability disclosure on par with the PHP flaw that broke the internet last week. not speculation, he said it’s “almost certain”
and it gets worse. he says they already have prior information about flaws in other software that haven’t been disclosed yet. multiple disclosures coming in the next few weeks to months
polymarket already opened a betting market on whether another major PHP flaw gets disclosed. that’s where we are right now. people are literally gambling on the next vulnerability
this is not normal. a CEO of one of the biggest infrastructure companies on the internet doesn’t come out and say “more is coming” unless he knows something specific. cloudflare sits between users and websites, they see everything before anyone else does
if you haven’t rotated your keys, updated your dependencies and enabled 2FA on everything by now, i genuinely don’t know what you’re waiting for
black october has a sequel and we’re watching the trailer
I hate Michigan as much as the next Buckeye fan, but that might be the WORST roughing the passer call I’ve ever seen.
Am I crazy, or was that an absolutely HORRIBLE call? 👀
Yeah, at this point I do not think anything that touches the internet is safe.
Going fishing, not answering emails or calls this weekend, will pray the internet is still on by Monday.
⚠️🚨 THIS IS NOT A DRILL 🚨⚠️
Google has officially declared a bug in Brotli, its tool that shrinks web traffic, CRITICAL: 9.2 out of 10. Last night "Node2Shell" evolved into HTTP2SHELL.
A formal CVE record has been issued citing CVE-2026-111497 -- a hole in versions 1.0.3 to 1.2.0 that can hit any app unpacking data from strangers, and could let them take it over.
What this means:
▪️ This is not a Node.js problem anymore. This is an HTTP PROBLEM.
▪️ Every unpatched app across Node.js, Python, Bun, and Envoy that unpacks Brotli now has a hole attackers need no login to use
▪️ Istio. curl. Python's requests and httpx. All at risk under one CVE.
▪️ EVERY project that bundles Brotli must ship its own fix, and not all are out yet
This changes everything.
A normal bug can be fixed in one place.
A 9.2 bug inside a shared tool cannot.
We just entered the most dangerous phase of this crisis. If you're not paying attention - start now.
Save this. Share this. This is the moment it escalated beyond return.
3% of “critical” software security bugs, in all of recorded history, have been found in the last month.
This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total
Do you realize how fucking insane that is?