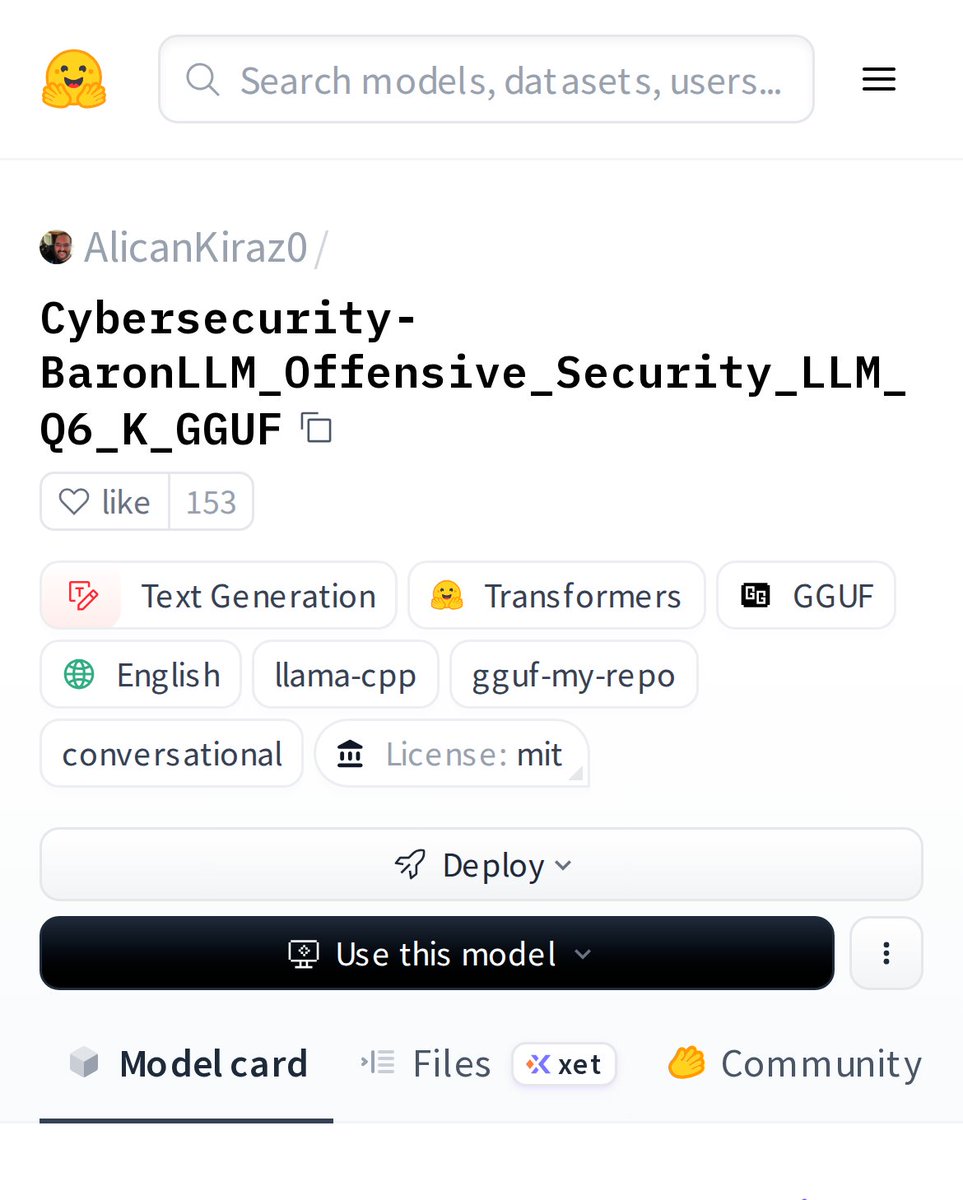
Meet the Cybersecurity Baron: a specialized LLM fine-tuned for offensive security. This isn't your average chatbot. It's a quantized, 6-bit GGUF model built on Llama 3.1 Instruct, designed to think like a penetration tester. Perfect for ethical hackers and security researchers.
If I told you there was a digital forensics and IR platform that gives security teams deep visibility into Windows, macOS, and Linux endpoints, would you believe me?
What if I said it’s open source, lightweight, scalable, and designed for flexible investigations?
Welcome to Velociraptor 101!
Download Rapid7's Velociraptor DFIR - https://t.co/1GPHxHwxPe
Velociraptor 101:
Rapid Windows Endpoint Investigations with Velociraptor & KAPE - https://t.co/PAzqnHANqD
AASLR: Playing with Velociraptor! - https://t.co/q6d92bgDpM
🚨 Top 5 Live Intelligence Dashboards You Should Be Watching
If you're tracking cyber threats, geopolitical tensions, or OSINT signals in real time, these platforms provide a powerful “single pane of glass” into what’s happening globally:
🌍 LiveUAmap – Real-time conflict and geopolitical event tracking
🔗 https://t.co/HV7wR0jxD4
📊 GDELT Project – Global event monitoring powered by AI across dozens of languages
🔗 https://t.co/Y3468LUhoI
🌐 WorldMonitor – Live global incidents, disasters, and security alerts
🔗 https://t.co/1qMzK0Dtaq
🛡️ SOCRadar Cyber Conflict Dashboard – Focused cyber threat intelligence (Iran–Israel context)
🔗 https://t.co/d4MNtnQ1OM
🧠 Pizzint – OSINT-driven monitoring of leaks, dark web activity, and threat signals
🔗 https://t.co/GutduD8Bif
These dashboards highlight how OSINT + real-time data + visualization are reshaping situational awareness for both cyber and physical threats.
👉 If you know other high-quality live intelligence dashboards, drop them in the comments — always looking to expand the list.
#OSINT #CyberThreatIntelligence #ThreatIntel #Geopolitics #DarkWeb #CyberSecurity #DDW #InfoSec #OpenSourceIntelligence
#Siberman, Kamu yakin kebiasaan digitalmu sudah aman? 💻
Di balik setiap akun, komentar, dan pesan yang kita kirimkan, ada manusia nyata dengan perasaan yang bisa tersakiti atau justru dikuatkan. 🤍
Di Ramadan ini, mari tingkatkan kepekaan dan menumbuhkan empati—tidak hanya
Automation blueprints for Red Team & Pentest, Blue Team (SOC/DFIR/TI), Application Security (AppSec/DevSecOps), and Platform/General Security — all using n8n.
https://t.co/2wF9jBs6QA
🧪 DFIR Labs | BlueSky Ransomware Lab
Dive into a real investigation where a SQL brute force attack led to rapid BlueSky ransomware deployment.
Explore how attackers compromised MSSQL, then used Cobalt Strike and Tor2Mine to spread ransomware!
👉 https://t.co/2fyIxXm9WC
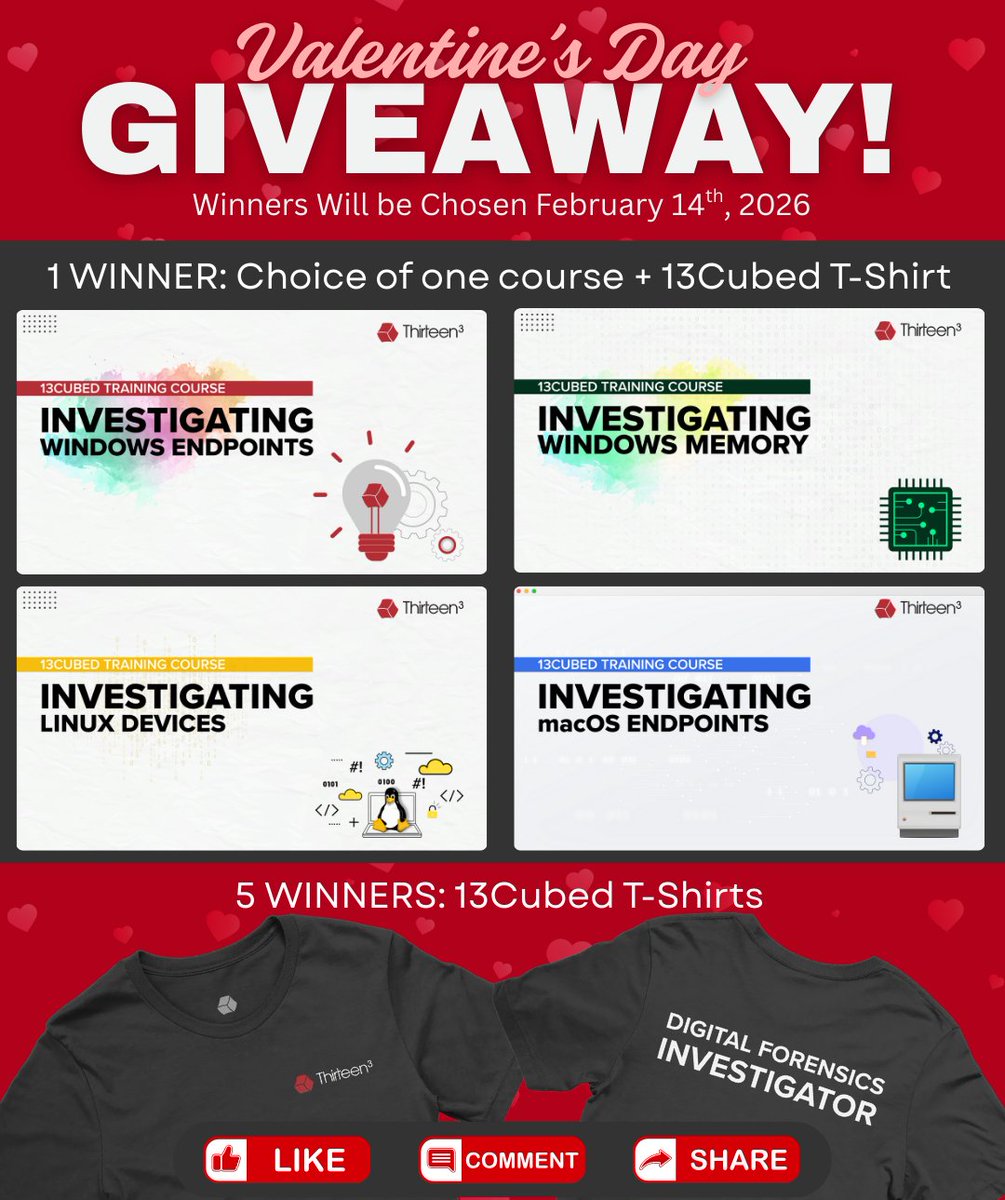
📣 I partnered with @13CubedDFIR for a Valentine's Day Giveaway! 🎁
🏆 1 Grand Prize winner will receive one course of their choice from the list below + a 13Cubed Investigator T-Shirt.
Courses:
- Investigating Windows Endpoints
- Investigating Windows Memory
- Investigating macOS Endpoints
- Investigating Linux Devices
Each course comes with a Certificate of Completion as well as Certification attempts.
👕 5 winners will receive 13Cubed Investigator T-Shirts.
To Enter:
✅ Like
✅ Comment with the name of the course you want to win
✅ Repost
On Valentine's Day (February 14th, 2026) entries from across three social media platforms will be combined and winners will be selected.
For more info check out:
13Cubed Courses: https://t.co/xbinmzzOdI
Certification Information: https://t.co/IVM2zdyp62
T-Shirts: https://t.co/021POuAXQL
#DFIR #DigitalForensics #IncidentResponse
⚠️ Illegal Gambling Operator Identified in Phnom Penh, Cambodia 🇰🇭 Targeting Indonesian Users 🇮🇩
Our investigation identified an illegal gambling operator operating from Phnom Penh, Cambodia 🇰🇭, deliberately targeting Indonesian users 🇮🇩.
By analyzing dark web stealer logs using our LLM-based investigation framework, we uncovered actionable intelligence linked to the operator — including admin panel access, operational infrastructure, and financial management records.
⚠️ These findings mean the operator is no longer anonymous and can be technically and operationally traced.
Government agencies seeking further intelligence are encouraged to contact us.