5 days only! Get upto 180 USD off on DevSecOps Courses.
That’s the biggest discount we have ever offered.
This sale will end on Dec 1.
https://t.co/1DHw5QnNsc
#DevSecOps#BlackFriday2021#CyberMonday2021
#mensxp Stop spreading misinformation! Have you performed verified analysis by security professionals? Validations can be bypassed at client side! Where is PII? Don’t make #infosec as #tiktok videos or #clickbait! 🙏🏻
@Mirror_ur_self @Joker122018 @DaleSteyn62 It was a grand win for SA. Like it was a grand win for India against SA. Respect it buddy. Its not easy playing at home or away. These players represent their country. Hats off....
To help keep you safe online, @googlechrome will now warn if your username & password have been compromised when you type them into a website. We’re also enhancing phishing protections to be real-time on desktop to alert you when visiting malicious sites. https://t.co/XuStf4sKQP
New sensitive breach: The zoophilia and bestiality forum Zooville had 71k records breached last month. Impacted data includes usernames and email addresses. 36% of addresses were already in @haveibeenpwned. More (NSFW website): https://t.co/oRGijwBzxx
Geez @zynga, starting a data breach notification with “Cyber attacks are one of the unfortunate realities of doing business today” really doesn’t read well. Was the breach really an “unfortunate reality”? Or was it due to bad code / config somewhere?
https://t.co/yz7VVZR6ax
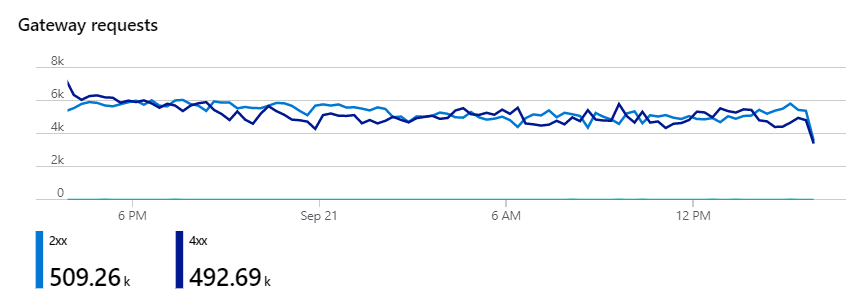
Seeing super solid performance from the V3 @haveibeenpwned API now. I've seen zero evidence of abusive patterns and had zero reports of false-positive blocks on requests. Also interesting to see that more than half of all requests find the email address in a breach (200 v 404)