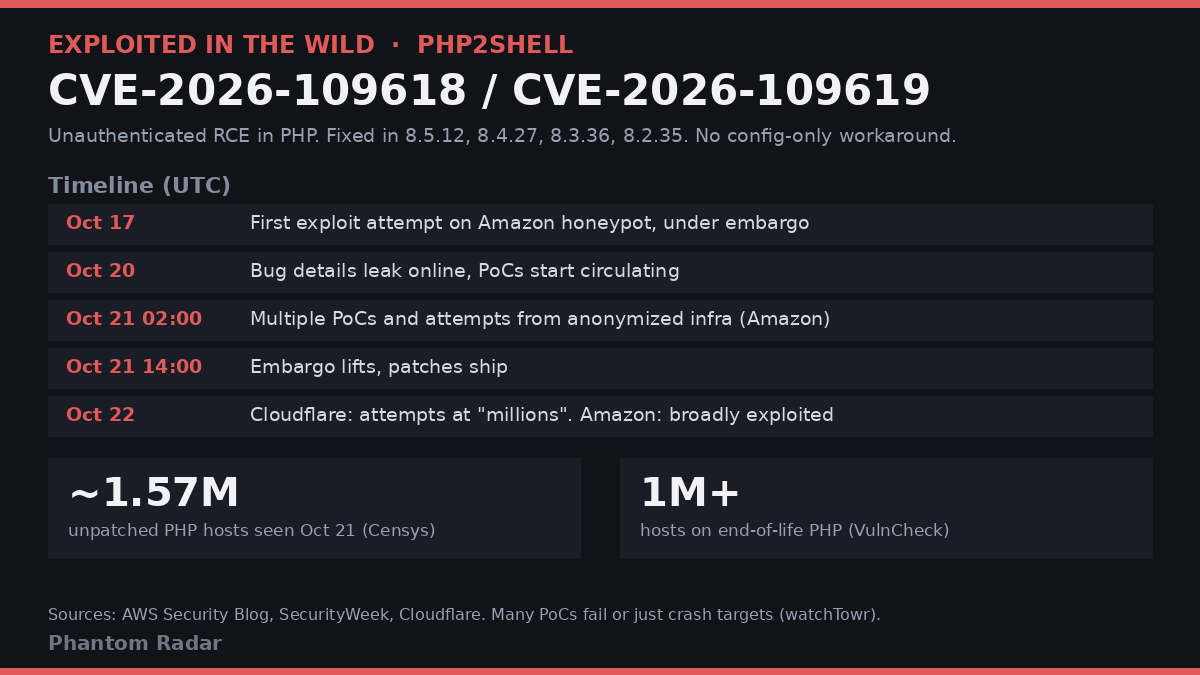
PHP2Shell update: Amazon's honeypots caught an exploit attempt on Oct 17, four days before disclosure. After the patch, attempts went from thousands to millions per Cloudflare, and Censys counted ~1.57M unpatched PHP hosts. Hunt from Oct 17, not release day. #ThreatIntel
The Cloudflare's writeup on our php2shell response is up.
Rules went live at 03:02 UTC, about 9 hours before disclosure. Unfortunately the vulnerability leaked early, so we were already watching attackers mutate payloads against the rules and updating as variants appeared.
New rules keep landing in the WAF changelog.
Expect updates through out the day. We will have a more thorough post of what we had to build to better protect people coming shortly.
PHP runs almost 70% of websites. The flaw is in the runtime, so updating plugins won't fix it. Patch PHP.
https://t.co/qzAiN2wGVl
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.