Holy shit... Microsoft open sourced an inference framework that runs a 100B parameter LLM on a single CPU.
It's called BitNet. And it does what was supposed to be impossible.
No GPU. No cloud. No $10K hardware setup. Just your laptop running a 100-billion parameter model at human reading speed.
Here's how it works:
Every other LLM stores weights in 32-bit or 16-bit floats.
BitNet uses 1.58 bits.
Weights are ternary just -1, 0, or +1. That's it. No floats. No expensive matrix math. Pure integer operations your CPU was already built for.
The result:
- 100B model runs on a single CPU at 5-7 tokens/second
- 2.37x to 6.17x faster than llama.cpp on x86
- 82% lower energy consumption on x86 CPUs
- 1.37x to 5.07x speedup on ARM (your MacBook)
- Memory drops by 16-32x vs full-precision models
The wildest part:
Accuracy barely moves.
BitNet b1.58 2B4T their flagship model was trained on 4 trillion tokens and benchmarks competitively against full-precision models of the same size. The quantization isn't destroying quality. It's just removing the bloat.
What this actually means:
- Run AI completely offline. Your data never leaves your machine
- Deploy LLMs on phones, IoT devices, edge hardware
- No more cloud API bills for inference
- AI in regions with no reliable internet
The model supports ARM and x86. Works on your MacBook, your Linux box, your Windows machine.
27.4K GitHub stars. 2.2K forks. Built by Microsoft Research.
100% Open Source. MIT License
Introducing the new @stitchbygoogle, Google’s vibe design platform that transforms natural language into high-fidelity designs in one seamless flow.
🎨Create with a smarter design agent: Describe a new business concept or app vision and see it take shape on an AI-native canvas.
⚡️ Iterate quickly: Stitch screens together into interactive prototypes and manage your brand with a portable design system.
🎤 Collaborate with voice: Use hands-free voice interactions to update layouts and explore new variations in real-time.
Try it now (Age 18+ only. Currently available in English and in countries where Gemini is supported.) → https://t.co/pmT9iHEpZa
Anthropic just made AI education free.
Universities charge $10,000+ for courses like this.
Here are 11 courses that put you ahead of 99% of people in 2026 and save you thousands of $:
(save it)
Oauth 2.0 Explained With Simple Terms.
OAuth 2.0 is a powerful and secure framework that allows different applications to securely interact with each other on behalf of users without sharing sensitive credentials.
The entities involved in OAuth are the User, the Server, and the Identity Provider (IDP).
What Can an OAuth Token Do?
When you use OAuth, you get an OAuth token that represents your identity and permissions. This token can do a few important things:
Single Sign-On (SSO): With an OAuth token, you can log into multiple services or apps using just one login, making life easier and safer.
Authorization Across Systems: The OAuth token allows you to share your authorization or access rights across various systems, so you don't have to log in separately everywhere.
Accessing User Profile: Apps with an OAuth token can access certain parts of your user profile that you allow, but they won't see everything.
Remember, OAuth 2.0 is all about keeping you and your data safe while making your online experiences seamless and hassle-free across different applications and services.
Over to you: Imagine you have a magical power to grant one wish to OAuth 2.0. What would that be? Maybe your suggestions actually lead to OAuth 3.
--
Subscribe to our weekly newsletter to get a Free System Design PDF (158 pages): https://t.co/FIzCeaWsZV
As CrowdStrike continues to work with customers and partners to resolve this incident, our team has written a technical overview of today’s events. We will continue to update our findings as the investigation progresses. https://t.co/xIDlV7yKVh
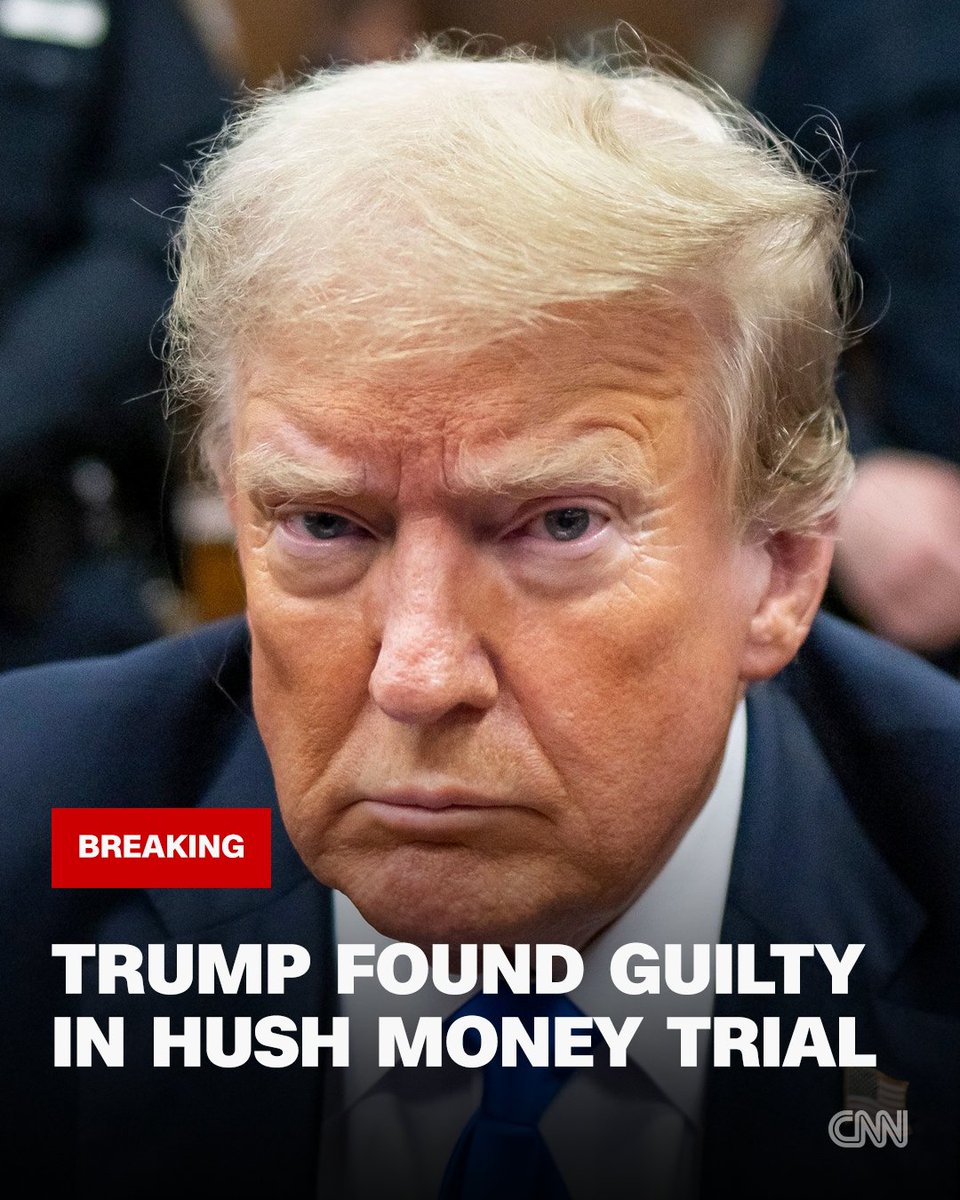
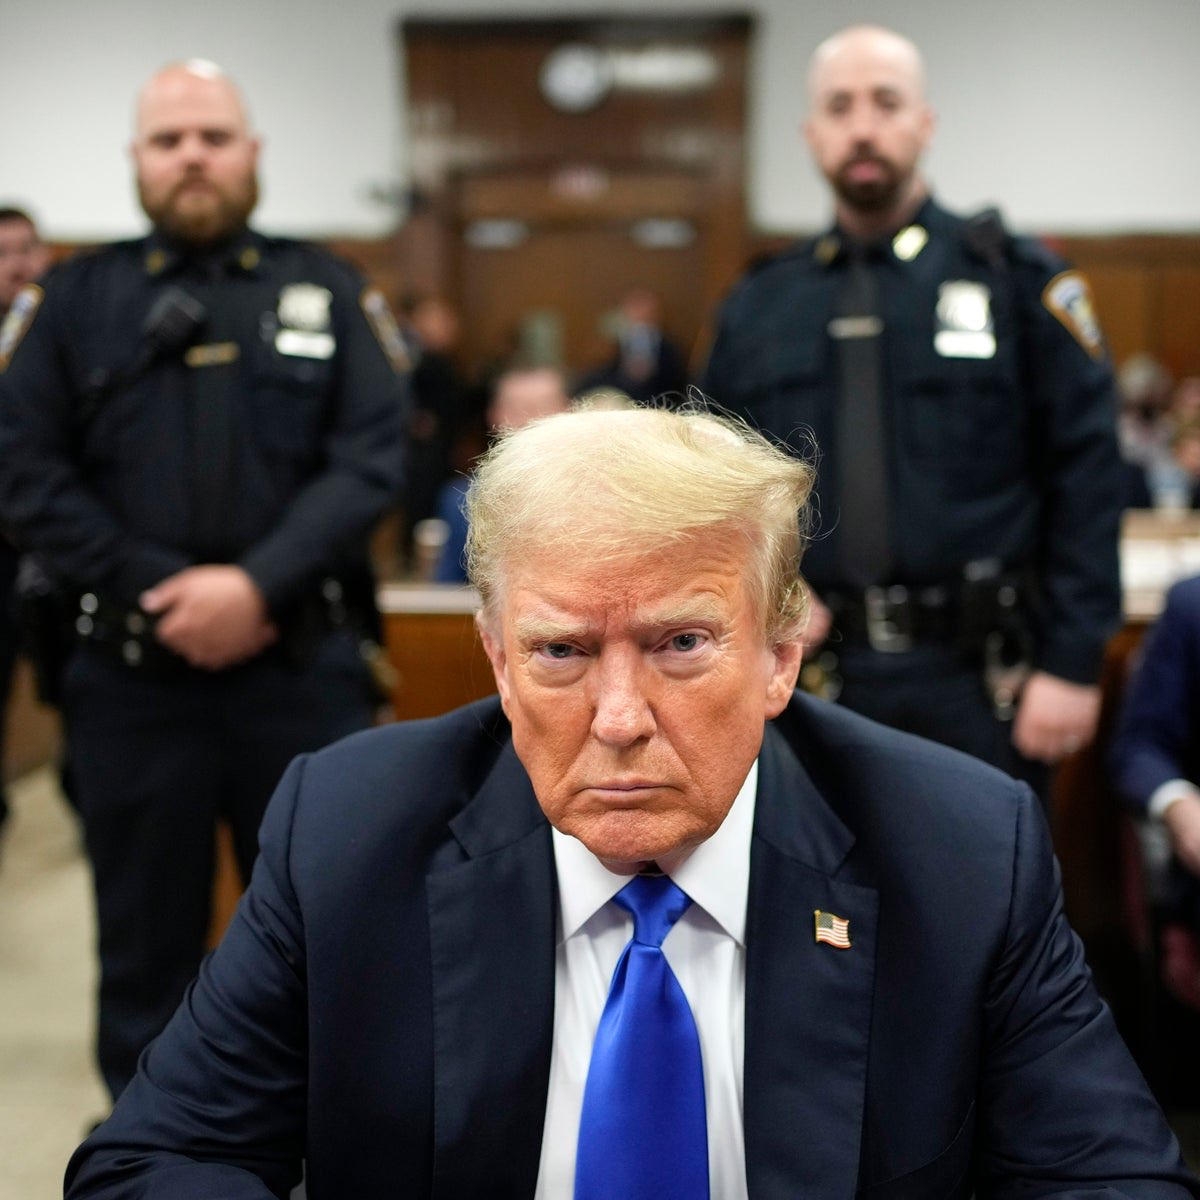
Jurors find Donald Trump falsified business records in New York hush money trial. He becomes the first former US president to be convicted in criminal court. https://t.co/XHvWHs9y8K
"If any of you meet me back home after you graduate, please remind me that we met in the Republic of Korea"
UAE President Sheikh Mohamed sat down with Emirati students while in South Korea for a state visit
JWT Explained
1. JSON Format: JWTs are represented as JSON objects, making them easy to read by both humans and machines. They consist of three parts separated by dots (`.`): the Header, the Payload, and the Signature.
- Header: The Header typically consists of two parts: the type of the token (JWT) and the signing algorithm being used (e.g., HMAC SHA256 or RSA). It's Base64Url encoded to form the first part of the JWT.
- Payload: The Payload contains the claims, which are statements about an entity (usually, the user) and additional data. Claims can be categorized into three types:
- Registered Claims: These are predefined claims with specific meanings, such as "iss" (issuer), "sub" (subject), "aud" (audience), "exp" (expiration time), and "iat" (issued at time).
- Public Claims: These are user-defined claims that can be freely used, but it's a good practice to avoid common names to prevent conflicts.
- Private Claims: These are custom claims used between parties that agree on their meaning.
- Signature: The Signature is used to verify that the sender of the JWT is who it says it is and to ensure that the message wasn't tampered with during transmission. The Signature is created by taking the encoded Header, encoded Payload, a secret (or private key in the case of RSA), and the chosen algorithm, then running them through the algorithm to produce a hash. This hash is used to verify the integrity of the token.
2. Encoding: Each of the three JWT components (Header, Payload, and Signature) is Base64Url encoded, which is a URL-safe variant of Base64 encoding. This encoding ensures that the JWT remains compact and can be safely transmitted in URLs, query parameters, or HTTP headers.
3. Usage: JWTs are often used in authentication and authorization workflows. Here's how it typically works:
- Authentication: When a user logs in or authenticates, the server generates a JWT and signs it with a secret key. This JWT is then sent back to the client, which can store it locally (e.g., in a cookie or local storage) and include it in subsequent requests to prove its identity.
- Authorization: The server, when receiving a request with a JWT, can verify the token's signature using the secret key. If the signature is valid, the server can trust the claims within the token to make authorization decisions, such as determining if the user has the right permissions to access a resource.
4. Statelessness: The server doesn't need to store session data because all the necessary information is contained within the token itself. This can simplify the design of distributed systems.
5. Expiration: JWTs can have an expiration time (specified in the "exp" claim), which means they are only valid for a certain period.
👍🏿 Subscribe to our newsletter - https://t.co/hxARDoA98l
Images creds @ManishPoduval
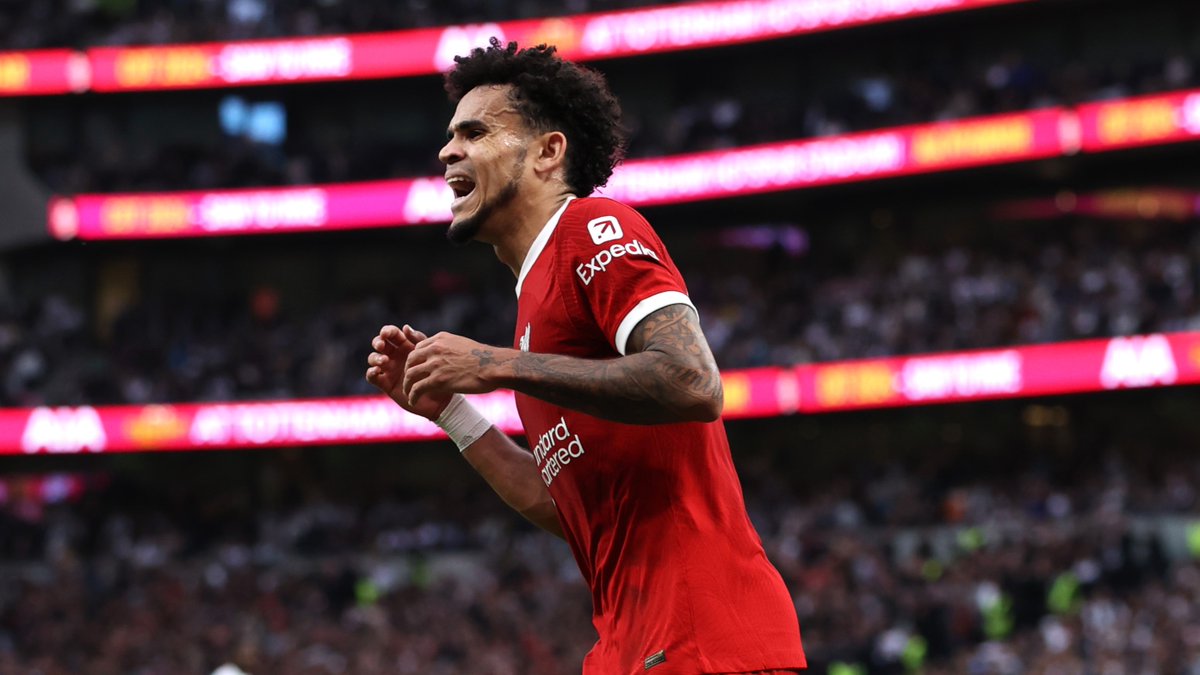
Referees' body PGMOL have released the full audio from the VAR hub relating to the Luis Diaz goal that was incorrectly disallowed in Spurs v Liverpool
➡️ https://t.co/3UGPAIrGW0
Explaining 8 Popular Network Protocols in 1 Diagram. The method to download the high-resolution PDF is available at the end.
Network protocols are standard methods of transferring data between two computers in a network.
1. HTTP (HyperText Transfer Protocol)
HTTP is a protocol for fetching resources such as HTML documents. It is the foundation of any data exchange on the Web and it is a client-server protocol.
2. HTTP/3
HTTP/3 is the next major revision of the HTTP. It runs on QUIC, a new transport protocol designed for mobile-heavy internet usage. It relies on UDP instead of TCP, which enables faster web page responsiveness. VR applications demand more bandwidth to render intricate details of a virtual scene and will likely benefit from migrating to HTTP/3 powered by QUIC.
3. HTTPS (HyperText Transfer Protocol Secure)
HTTPS extends HTTP and uses encryption for secure communications.
4. WebSocket
WebSocket is a protocol that provides full-duplex communications over TCP. Clients establish WebSockets to receive real-time updates from the back-end services. Unlike REST, which always “pulls” data, WebSocket enables data to be “pushed”. Applications, like online gaming, stock trading, and messaging apps leverage WebSocket for real-time communication.
5. TCP (Transmission Control Protocol)
TCP is is designed to send packets across the internet and ensure the successful delivery of data and messages over networks. Many application-layer protocols build on top of TCP.
6. UDP (User Datagram Protocol)
UDP sends packets directly to a target computer, without establishing a connection first. UDP is commonly used in time-sensitive communications where occasionally dropping packets is better than waiting. Voice and video traffic are often sent using this protocol.
7. SMTP (Simple Mail Transfer Protocol)
SMTP is a standard protocol to transfer electronic mail from one user to another.
8. FTP (File Transfer Protocol)
FTP is used to transfer computer files between client and server. It has separate connections for the control channel and data channel.
–
Subscribe to our newsletter to download the high-resolution PDF. After signing up, find the download link on the success page: https://t.co/keu1P0hhKI
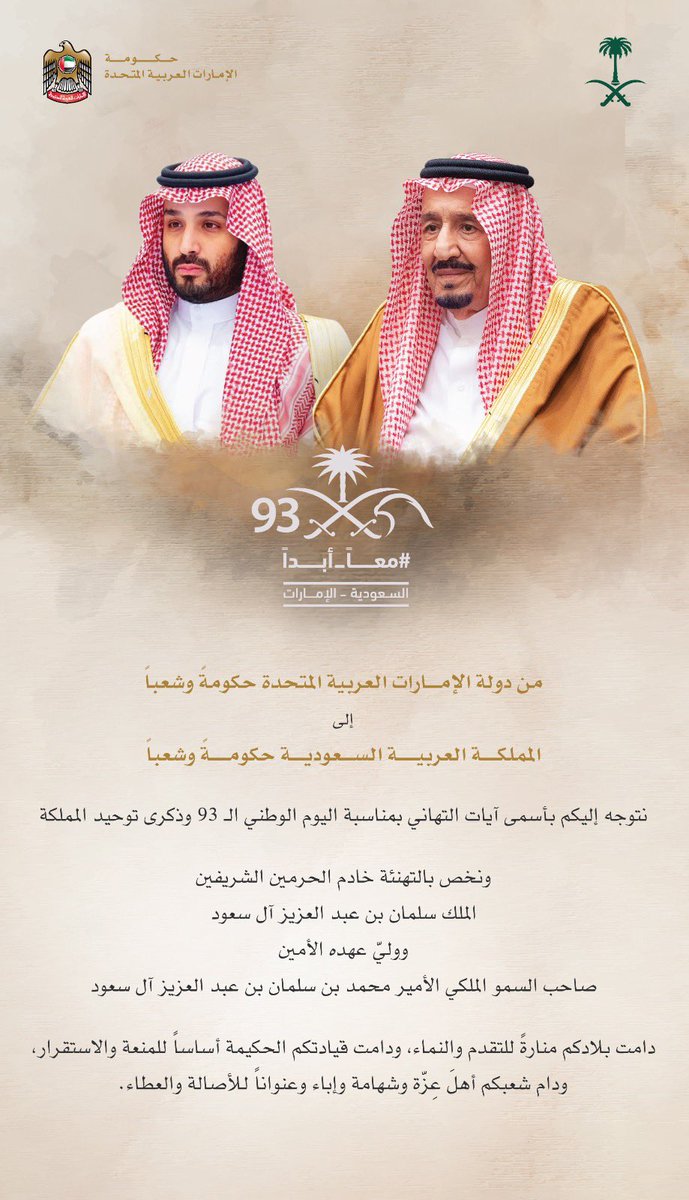
كل التهاني للمملكة العربية السعودية وشعبها وملكها وولي عهده الأمين بمناسبة اليوم الوطني السعودي .. نسأل الله أن يديم خيرهم وأمنهم وعزهم .. وأن يديم الأخوة والمحبة بين الشعبين الشقيقين .. كل عام وأنتم بخير .. وشعبكم إلى خير ..وراية مجدكم خفاقة عالية .
تابعت مقابلة أخي الأمير محمد بن سلمان مع قناة فوكس .. مقابلة عكست قوة الإنجاز في المملكة، ودقة الرؤية التي يتبناها سموه ..
متفائلين بنجاح المملكة .. ومتفائلين بقيادتها الطموحة الواعية.. ومتفائلين بشرق أوسط جديد بتعاون دوله ليعود مركزاً حضارياً واقتصادياً عالمياً باذن الله..