Pround dad moment tonight. My son and his band The Bridge will be on BBC Introducing debuting their new track Oprah. So if you are into indie music, check it out. Show starts at 9pm on @BBCRadioWales presented by @welshmusic.
I ran a poll about doing Halloween vs Black Friday and was reminded by a few of my mates that I'm Scottish not American(quite rightly so pulled up on it too!) therefore going with Halloween theme. Which is good news for everyone anyways, as 13.37% discount is live as of today till end of November:
GUISING1337 - 13.37% off because Leet
https://t.co/XxxUI2DRIG
https://t.co/gvGwReAfK5
A bit of info for some that might not be aware but the traditional 'trick or treat' terminology many associate with halloween is actually called guising in Scotland.
As a child I'd go round guising on halloween, unlike modern trick-or-treating where children receive sweets just for showing up to people's houses, by going guising you are traditionally expected to perform a "party piece", think of this like your 'trick' such as telling a joke, singing a song, or reciting a poem before receiving treats like fruit, nuts, or sweets.
All this to say, here have 13.37% off the course till end of November!
Cheers,
Andy
#RedTeam #BlueTeam #PurpleTeam #MAE #ZephrSec @ZephrSec
Here's some of the research I've done into AI and LLMs over the past year:
https://t.co/SUgxpGqGFr - Building MCPs
https://t.co/Jx4UpiTrD0 - What makes up a harness
https://t.co/7sFalfALNn - Building tooling
#infosec#llm#vulnerabilityresearch#MCP#harness
Someone reminded me the other day I'm speaking at @Hack_Thursday this month (Thursday 15th Oct!) ! It won't be recorded as it's a small event but I'll be talking about Blending into the Noise: Baselining windows to blend in, looking at windows telemetry from a red team perspective and all the fun that follows. Come along it'll be fun :)
If you're an IT admin and you have nothing to do, check for these issues in your Active Directory environment.
I promise if you fix these issues your environment will be harder to attack.
https://t.co/FFtYjV0UZV
Weekend project: I added IAKerb support to Rubeus. My god, this is going to open the floodgates.
Phase 2 of Microsoft's NTLM deprecation is targeted for H2 2026. IAKerb ships for Server 2025 / Win11 24H2 and is already on by default in the June Canary preview. It proxies Kerberos auth through exposed services via SSPI when a client can't directly reach a KDC.
Which means anonymous user enum via AP-REQs with no preauth (zero telemetry), kerberoasting over the open internet, Entra lateral movement through AZUREADSSO tickets and more. All against public facing services.
Blog post soon with potential abuse vectors.
Want to run an entire Tailscale daemon from memory inside a C2 implant with zero disk artifacts, no kernel drivers, traffic indistinguishable from HTTPS to a CDN, and relay connections from the victim network back through the tailnet.
Now you can. Enjoy!
https://t.co/WmBlShAnLr
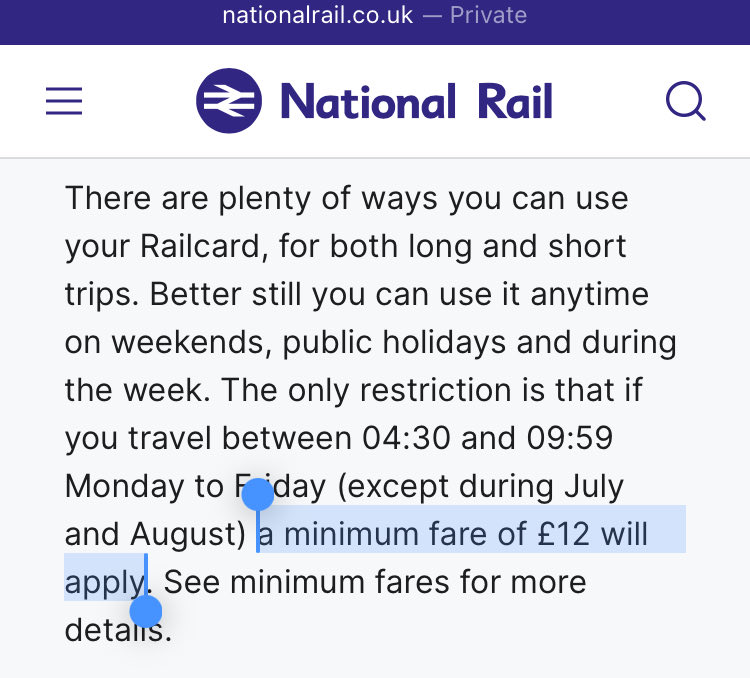
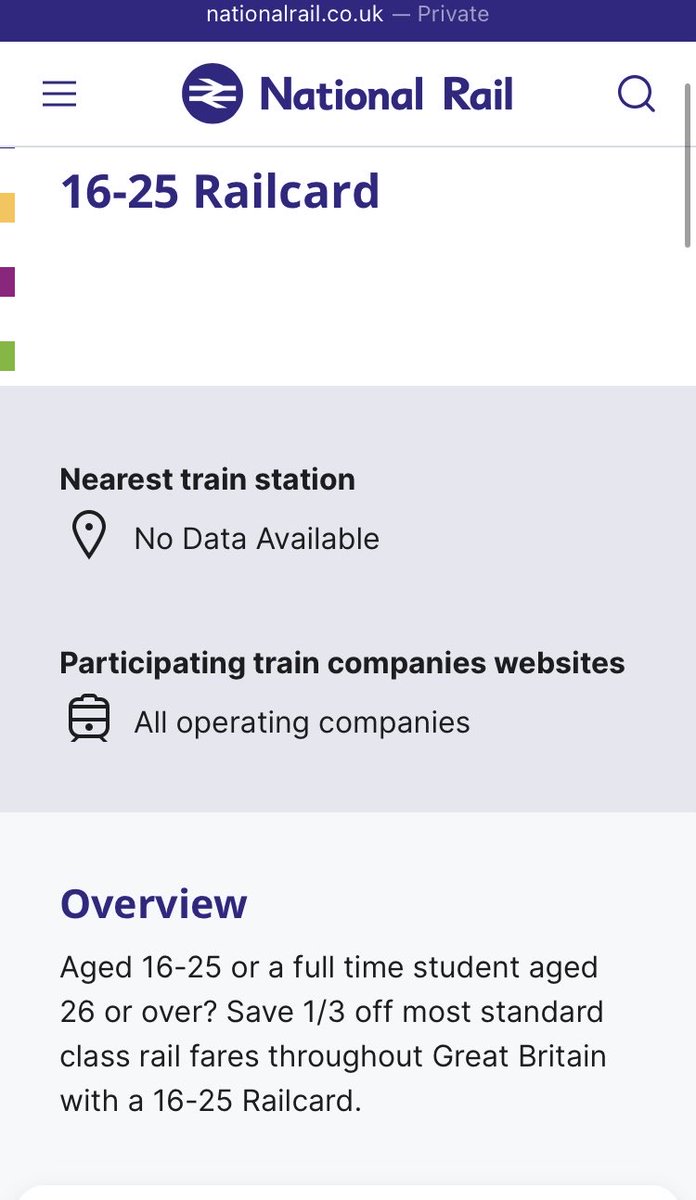
UK discount railcard for students, but can’t use it to get to college or university before 10am because this is the UK and we don’t encourage trains.
The National Rail 16–25 and 26–30 Railcards enforce a £12 minimum fare.
Short local commutes usually cost around £4 to £8. 🤦
Tomorrow is the day @Hack_Glasgow where I'll be speaking alongside @CaptainDjent about red and blue perspectives on adversarial patterns, if you're in Glasgow area and fancy coming along I believe there are still tickets avail!
https://t.co/31IrEqmIqQ
Also as has become a bit of a theme with UK cons, HackGlasgow are collecting for charity which is great, if you've got a few quid spare you should totally throw it at:
https://t.co/PB1CRHAf1Y
Also @ZephrSec is sponsoring too, I'll probably have stickers if folks want them!
#HackGlasgow #HackThursday #RedTeam #BlueTeam #PurpleTeam
Proudest moment of my life so far.
My daughter who went to a state-funded school, dyslexic, doesn’t come easy for her, fought every day to get to the top.
She’s just been accepted in to one the greatest universities in the UK.
Genuinely I’m crying but also delighted.
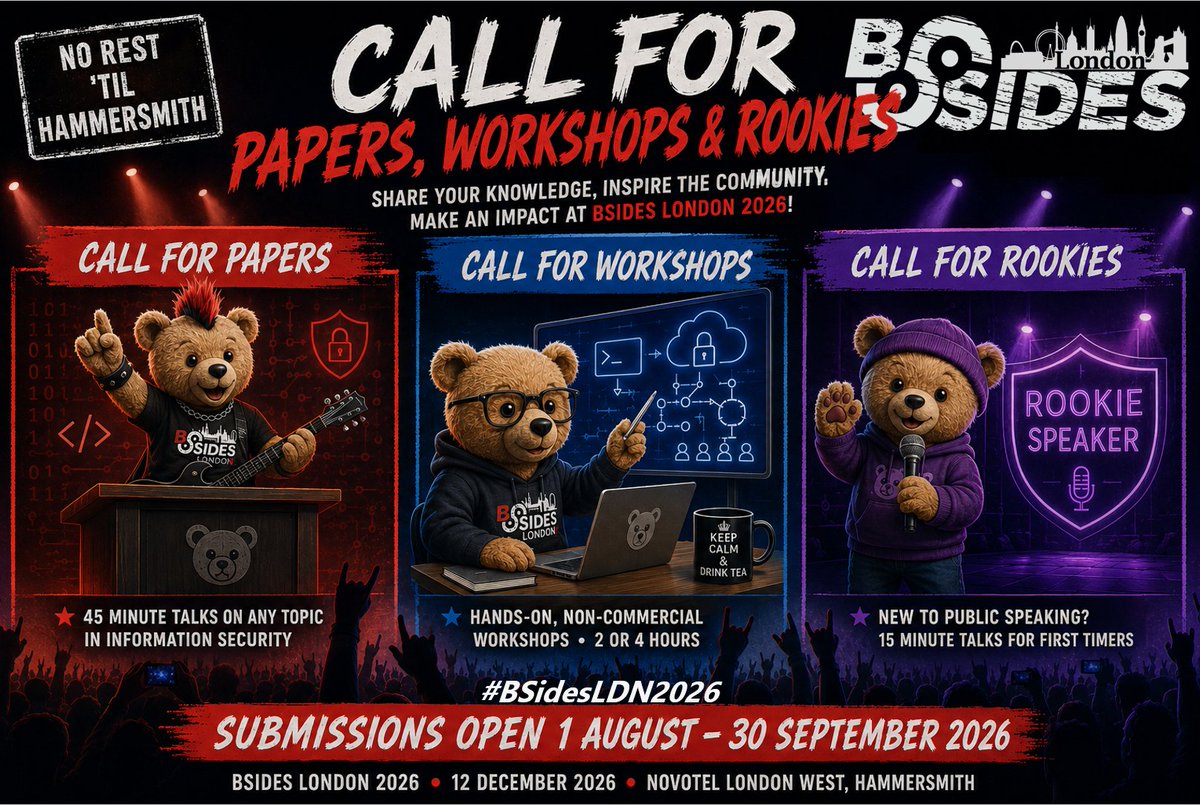
The #BSidesLDN2026 CFP opens at 1337hrs this Saturday (1st August), and you have until the 30th September to get your proposal in!
Call for Papers - 45 min presentations
Call for Rookies - 15 mins, 1st time speakers only!
Call for Workshops - 2hr or 4hr non commercial workshops
A week off so far and a few days to go left of PTO, can mean only one thing...
...blog post and research time!
Here's a post and tool I've had in drafts for a while and not had a chance to finish, https://t.co/pWCDygc6XD
BrokerLine is essentially a PoC using Azure's PubSub service for C2 and demonstrating how it's possible todo (bonus points the header image is from my first week of PTO as I spent last weekend at Tomorrowland)!
#RedTeam #SecurityResearch #BlueTeam #ProofOfConcept
@_RastaMouse I did the same last year, far too much choice, ended up on agreeing to one, few months later a mint green thing, made of woven mesh, turned up at my house.
It’s hard buying a sofa these days.
My @Steel_Con talk on compromising hybrid domains is now live!
The talk explains real-world attack paths spanning:
Active Directory
Microsoft Entra ID
Azure & M365
All based on real techniques I perform on authorised red team engagements.
https://t.co/LiFRCkuaom
Want a Monday morning treat?
Our videos are now online:
https://t.co/RqQdYmPCt8
We are missing a couple which will be added soon, and @ZephrFish is keeping his private.
Enjoy!
Thanks @Ministraitor
I've not done any deep dives on bugs in a while so here's a walkthrough of where the #wp2shell bug exists in code, constructing a PoC and highlighting the signs to search for if you're seeing exploitation in the wild.
https://t.co/Bf5cN0TYLZ
#blueteam#vulnerabilityresearch
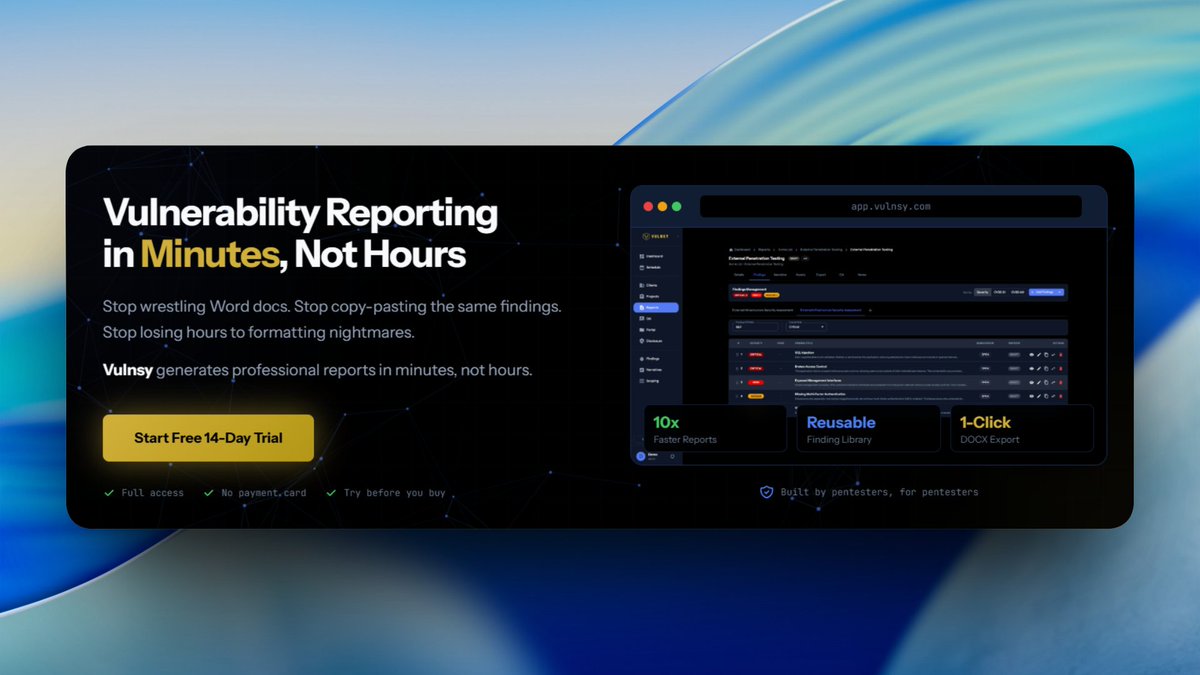
✨14 Day Free Trial: No card details required ✨
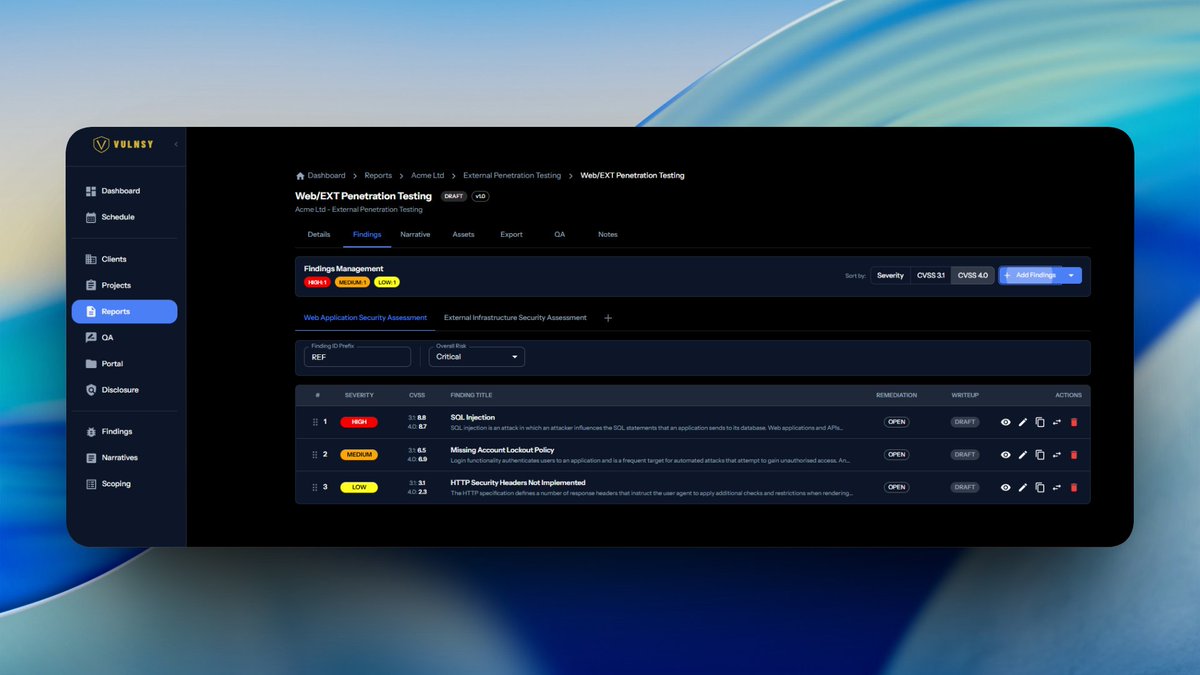
Vulnsy.. The Vulnerability Reporting Platform.
If you love it after 14 days, take out a subscription. If you don't love it, thanks for trying it😊
Sign up in 4 simple steps https://t.co/Aayf7gDyQB