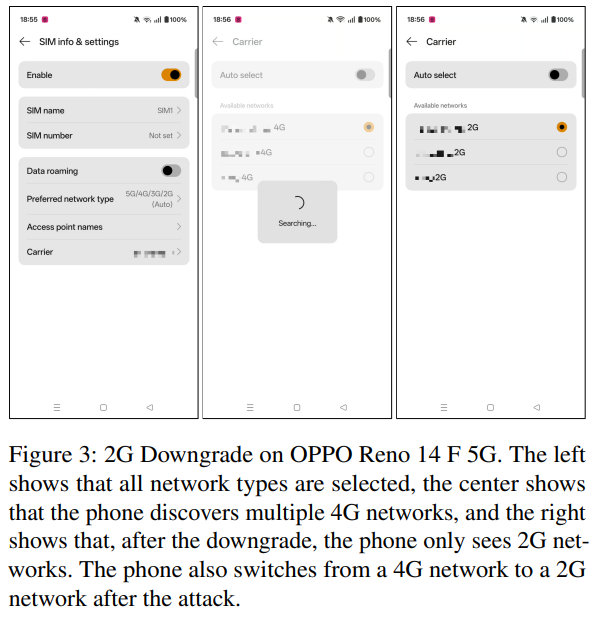
@AliceInDisarray Disclaimer here: we could just test the phones we have physically around, there may be other models affected as well.
The Reno 14F is even more recent
Our USENIX Security'26 Paper "Download More RAM" is now available!
In this paper, we introduce a new memory aliasing attack, fully from software and completely subverting Windows OS Security.
Full paper with more information and case studies at: https://t.co/lwgs07R0Kj
Our @wootsecurity'26 paper "CATana" is now available: https://t.co/cfkMearbBF!
In the paper, we find that some phones and many IoT devices execute AT commands sent by the SIM, leading to a wide range of consequences from DoS over 2G downgrade to device compromise.
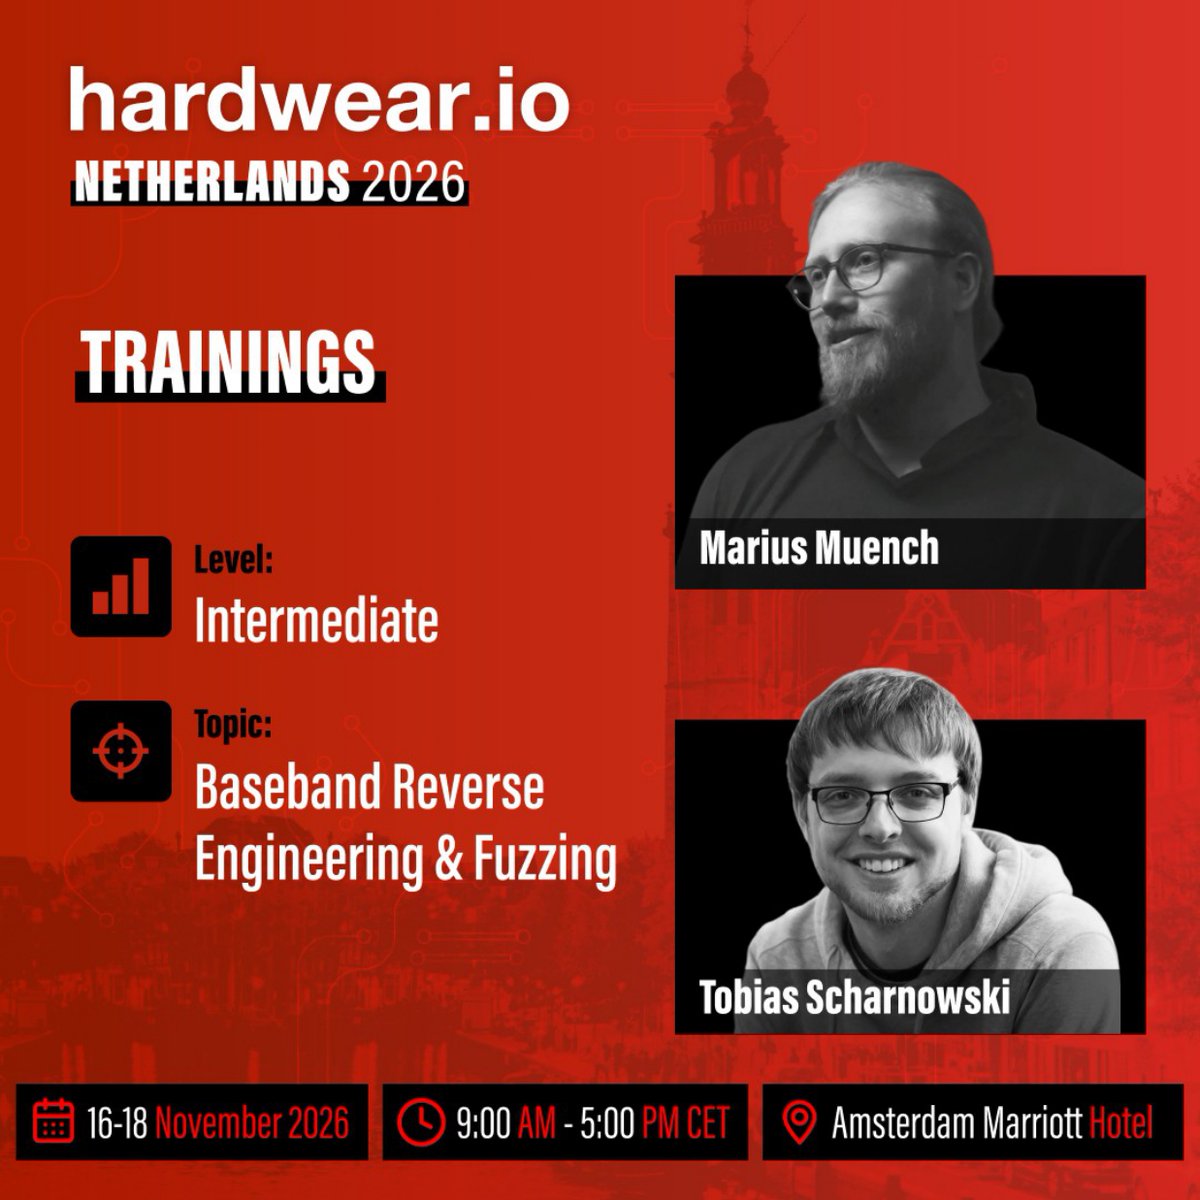
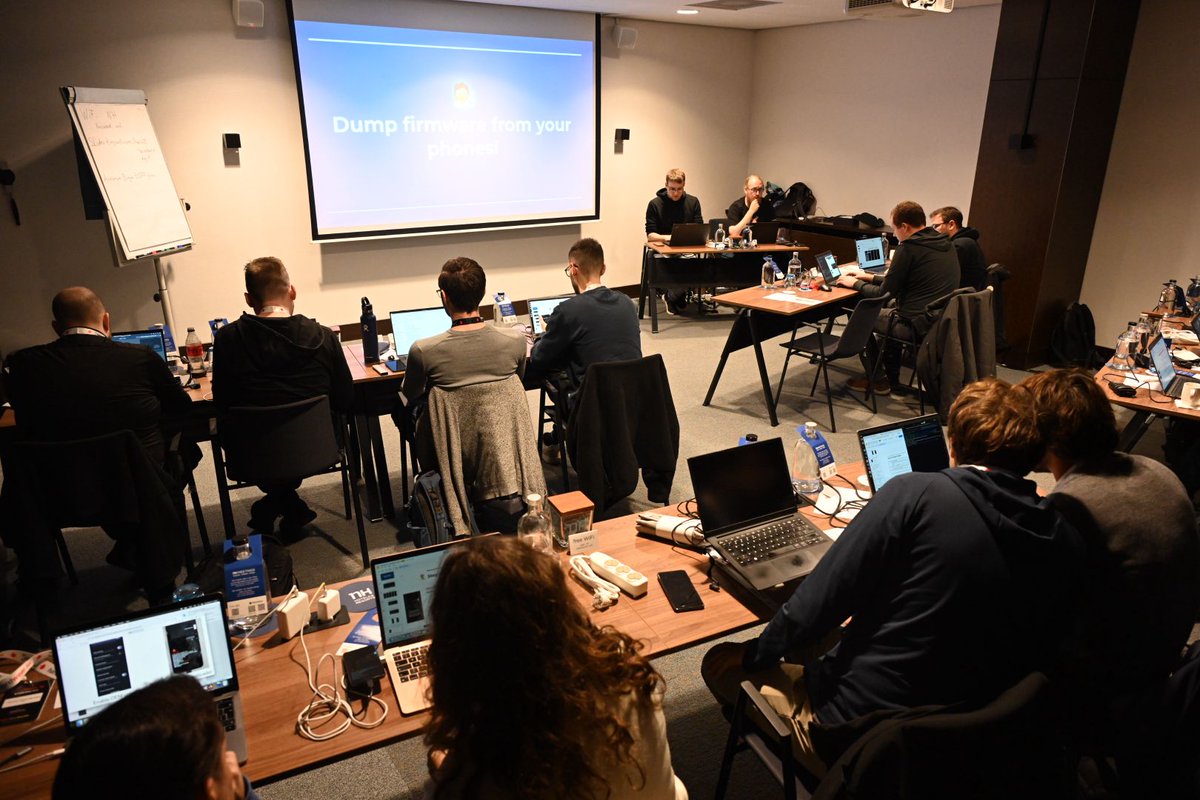
Learn how to reverse engineer cellular firmware, build emulation environments, and fuzz real-world protocol parsers with Marius Muench and Tobias Scharnowski at https://t.co/PVi7u42ZZR Netherlands 2026.
🎟️ Register now: https://t.co/cxsDX8BM1k
#HardwearNL2026#HardwearTrainings
The recording of our @WEareTROOPERS'26 talk is online!
In "A SIM Hacking Odyssey: Can a SIM hack YOU", Tomasz and I describe our journey in SIM-originating attacks, which started more than 4 years ago!
Video: https://t.co/JaqrsrWsN8
Slides: https://t.co/EmOkQcSbJq
Great summary of the work we recently shared at @WEareTROOPERS.
For everyone interested in this, stay tuned for our upcoming @wootsecurity paper "CATana: On the Dangers of SIM-Originating AT Commands": https://t.co/FIKOzoyKbp
How a SIM can (and will) hack you: Security analysis of SIMs, attacks, and tools for research. 👨🏻💻🎫📱🩻👾
More details on:
LinkedIn: https://t.co/F6dPXNHhrA
Substack: https://t.co/0ImBiCuzkh
A virtual iteration of our training on fuzzing custom embedded systems is coming up end of March.
One cool story about this: The participants of our training in 2024 exploited a bunch of devices at Pwn2Own Tokyo 2026!🔥
Details: https://t.co/D0nGEpnPS6
En route to #39c3 - come to our talk at 4pm!
I will only be there today and tomorrow, but happy to meet-up & chat.
Also, if you are at #39c3 and often dump SPI flash-chips please let me know, I might have something for you that I'm looking for feedback on 🙂
En route to #39c3 - come to our talk at 4pm!
I will only be there today and tomorrow, but happy to meet-up & chat.
Also, if you are at #39c3 and often dump SPI flash-chips please let me know, I might have something for you that I'm looking for feedback on 🙂
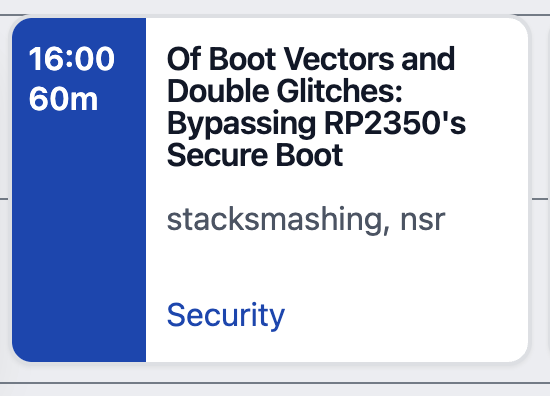
🤩A hush settles as the RP2350’s challengers—Marius Muench and Thomas Roth—begin their story
What started as a public hacking challenge became a trail of breakthroughs, from unverified vector boots to secrets pulled straight out of OTP memory.
👉https://t.co/F4p6bUrekw
#RP2350
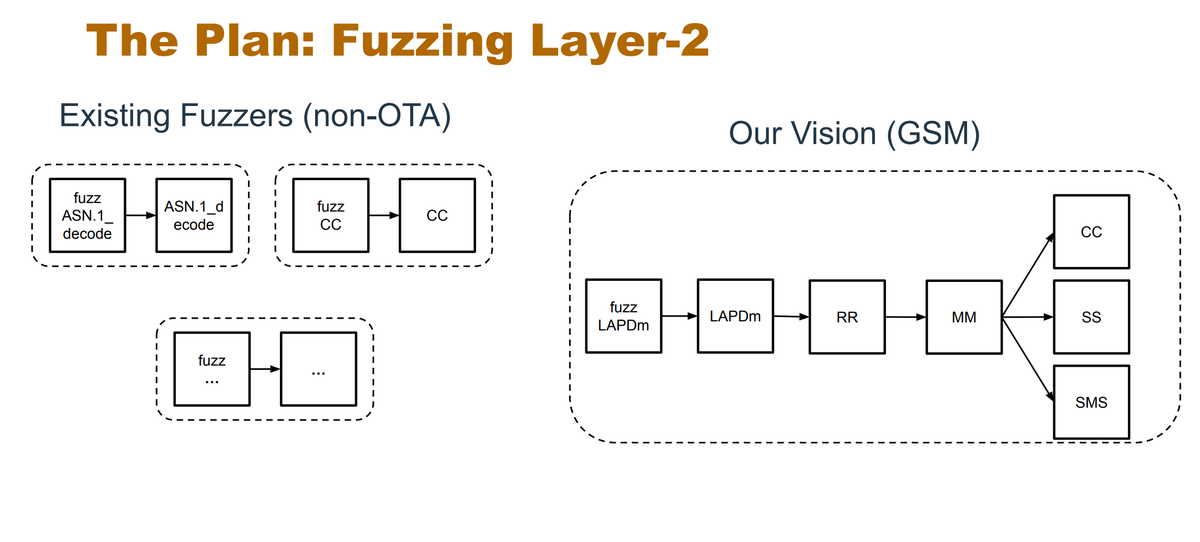
🔍 It’s reverse engineering mayhem as participants trace how basebands whisper to each other inside the Shannon modem, mapping flows that feel straight out of a sci-fi network core.
In action Marius Muench; Tobias Scharnowski at #hw_ioNL2025
👉https://t.co/JE9xdoqHVu
#fuzzing
Our @defcon'33 talk is online:
https://t.co/RPY7WZx8Qz!
Ever wondered how to get banned from online games without cheating? We've got you covered! Check out this talk for fun hacks tripping off modern anticheats.
Joined work with @Cowtickle & @TomChothia.
I absolutely love this paper, so much reverse engineering alpha
the researchers who won the rpi hacking challenge came together to describe in detail how they overcame the defenses of a secure-by-design chip, incl. custom laser fault injection and single instruction skips
We have an exciting piece of vulnerability research 🕵️♂️ to share, conducted in collaboration with external researchers from VU Amsterdam. Find out more about the L1TF vulnerability, a CPU vulnerability on some Intel CPUs (Skylake and older).
https://t.co/n6X5FoRJCR