Soit il pouvait trouver des profs remplaçants depuis le début et il se moque des lycéens.
Soit il fait une annonce qu’il ne peut pas respecter et il se moque des lycéens.
En gros, il se moque des lycéens.
En France, le gouvernement s’apprête à donner un «permis de tuer» aux policiers.
Le 7 juillet, l’Assemblée nationale doit voter une loi qui considèrerait légal TOUT TIR de policier ou gendarme.
Ce serait une bascule historique. Voici en 5 points ce que cette loi changerait.👇
Apple and Google are gradually expanding their use of hardware-based attestation. They're convincing a growing number of services to adopt it. Google's Play Integrity API and Apple's App Attest API are very similar. Apple brought it to the web via Privacy Pass, which Google intends on doing too.
Google's Play Integrity API requires hardware attestation for the strong integrity level and is gradually phasing in requiring it for the more commonly used device integrity level. Apple already has it as a requirement. Over the long term, this will increasingly lock out hardware and OS competition.
The purpose of these systems is disallowing people from using hardware and software not approved by Apple or Google. This is wrongly presented as being a security feature. Banks and government services are the main ones adopting it but Apple and Google are encouraging every service to use it.
Apple's Privacy Pass brought hardware attestation to the web to help with passing captchas on their own hardware. Many people saw that as harmless since few sites would be willing to lock out non-Apple-hardware users. Apple and Google are both likely to bring broader hardware attestation to the web.
Google's reCAPTCHA is planning an approach where they use Privacy Pass on Apple hardware, their own approach on Google Mobile Services Android devices and a QR code scanning system to require an iOS or Google certified Android device for Windows and other systems:
https://t.co/7rQnioRa8A
Banking and government services increasingly require using a mobile app where they can use attestation to force using an Apple or Google approved device and OS. Apple's privacy pass, Google's 'cancelled' Web Environment Integrity and now reCAPTCHA Mobile Verification are bringing this to the web.
Current media coverage for reCAPTCHA Mobile Verification misunderstands it and the impact of it. They're bringing a hardware attestation requirement to Windows, desktop Linux, OpenBSD, etc. by requiring a QR scan from a certified smartphone to pass reCAPTCHA in some cases. They could expand it more.
Control over reCAPTCHA puts Google in a position where they can require having either iOS or a certified Android device to use an enormous amount of the web. Google defines certification requirements for Android which includes forcing bundling Google Chrome, etc. It's enormously anti-competitive.
Google's Play Integrity API bans using GrapheneOS despite it being far more secure than anything they permit. It also bans using any other alternative. This isn't somehow specific to an AOSP-based OS. You can't avoid this by using a mobile OS based on FreeBSD instead. You'll just be more locked out.
Google's Play Integrity API permits devices with no security patches for 10 years. The device integrity level can be bypassed via spoofing but they can detect it quite well and block it once it starts being done at scale. The strong integrity level requires leaked keys from TEEs/SEs to bypass it.
It doesn't provide a useful security feature, but it does lock out competition very well. Services requiring Apple App Attest or Google Play Integrity are primarily helping to lock in Apple and Google having a duopoly for mobile devices. Play Integrity is more relevant due to AOSP being open source.
Governments are increasingly mandating using Apple's App Attest and Google's Play Integrity for not only their own services but also commercial services. The EU is leading the charge of making these requirements for digital payments, ID, age verification, etc. Many EU government apps require them.
Instead of governments stopping Apple and Google from engaging in egregiously anti-competitive behavior, they're directly participating in locking out competition via their own services. Requiring people to have an Apple device or Google-certified Android device is anti-competition, not security.
reCAPTCHA Mobile Verification will currently work with sandboxed Google Play on GrapheneOS but it clearly exists to provide a way for them to start using hardware attestation on systems without it. People without an iOS or Android device will be locked out when this is required even without that.
This isn't about security or any missing functionality. GrapheneOS can be verified via hardware attestation. Google bans using GrapheneOS for Play Integrity because we don't license Google Mobile Services and conform to anti-competitive rules already found to be illegal in South Korea and elsewhere.
Services shouldn't ban people from using arbitrary hardware and operating systems in the first place. Google's security excuse is clearly bogus when they permit devices with no patches for 10 years but not a much more secure OS. It's for enforcing their monopolies via GMS licensing, that's all.
🔴🇫🇷 Donc là en 3 jours, on a des millions de documents confidentiels de mineurs qui se baladent : CNI, passeports, actes de naissance…
Des institutions entières piratées, des données ultra sensibles exposées, et toujours aucune réaction sérieuse.
Pendant ce temps, on nous parle de contrôler l’accès aux réseaux avec nos pièces d’identité ou de lancer des “missions d’État” concernant les jeux vidéo pour les mineurs 🤡
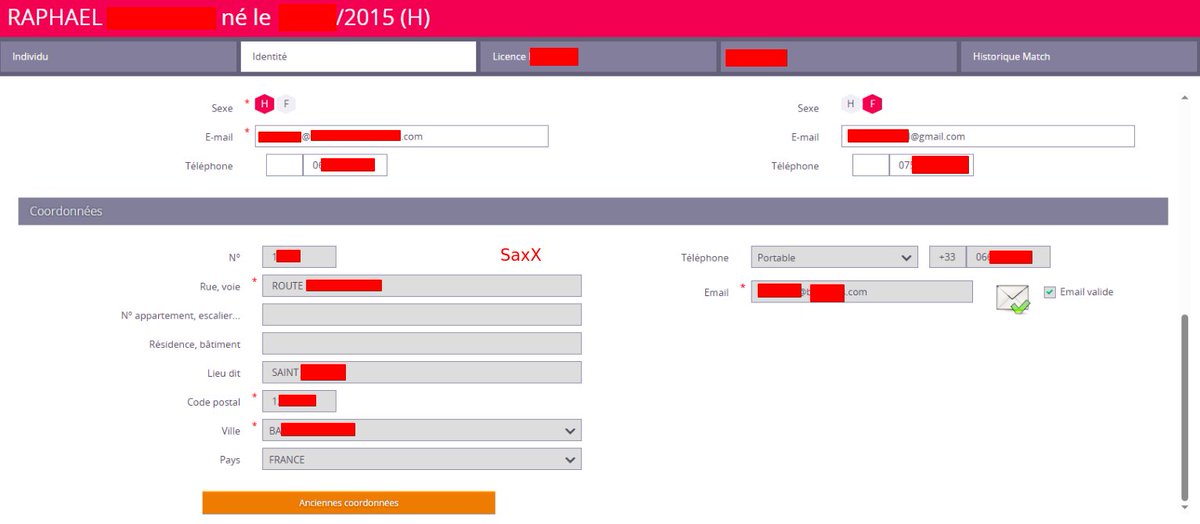
🚨🔴CYBERALERT 🇫🇷FRANCE🔴 | Les Fédérations Françaises du Sport et Associations sportives (toutes) piratées... ⤵️
Ce week-end j'en pouvais plus ! Sidéré de recevoir à la chaîne plusieurs échantillons de données piratées, captures d'écran et mode opératoire de Fédérations et Associations Sportives, de structures étatiques et autres entreprises qui se sont fait pirater ces dernières semaines !
Le pire, bcp de ces structures ne le savent pas...
Le plus angoissant, des millions de personnes ne savent pas que leurs données, leur identité est exploitée et pire encore celles de leur enfant -pour ces petites gens qui inscrivent leur progéniture au sport-
Quand ces jeunes cybercriminels (français pour la majeure partie) viennent me parler -pour plusieurs raisons...- et que j'apprends les moyens de compromission qui sont d'une facilité déconcertante, je me dis WTF !
On s'en fout pas mal de la sécurité des données en France en tout cas pour bcp de structures !
[...]
Conséquences...
👉🏾 2026 sera un record en terme d'arnaques
👉🏾 On pourra désormais facilement récouper les informations sur une personne et son entourage... conjoint(e), enfants...
👉🏾 Des candidats pour les municipales en 2026 recevront hélas des coups de pression ou se feront doxxer, pcq toutes ces informations personnelles que l'on minimise dans la nature
Je n'ai pas bcp de moyens et de temps pour alerter ! Mais j'aimerais bien en faire plus avec déjà des idées concrètes !!
La seule chose que je puisse faire, c'est bien ces posts que vous lisez de plus en plus pour vous alerter !
Au ministère des Sports et de la Santé, renforcez et sensibilisee les personnels.
Ces données personnelles "associatives" semblent minimisées mais se révéleront être le tendon d'Achille des prochaines semaines et mois en France...
Cybèrement vôtre,
SaxX ¯\_(ツ)_/¯
For the French.
Use monero to get anonymous number.
Use signal
Obtain a pixel to install GOS
Use session if you have too.
Use Nostr
Use Tor
Use I2P
Look for Local first apps
Fight against chat Control
Encrypt everything
Use PGP if you have too.
Find a decent email provider.
Reject this nonsense.
Reject chat control
Reject Backdoors.
Je rappelle que la jeunesse Française s'est confinée lors du COVID pour protéger ses aînés, va assumer des décennies de gabegies financières dont elle n'est pas responsable et le climat.
Je suis écoeuré par le jugement que certains de ces aînés ont pour nos jeunes.
✅️ Un des stands/workshops incontournables de #lehack, c'est bien entendu l'arrêt chez @RatZillaS !
Quelle passion !
Quel engouement !
Quel partage !
Parler de drônes - de maritime - de voitures connectés - d'automobile - de cybersécurité - d'open source - d'open hardware - de transmission à travers de cools ateliers avec des collégiens et lycéens - ...
N'hésitez pas à y aller ! Vous apprendrez énormément de choses à défaut d'avoir des précisions/éclaircissements 👌🏽
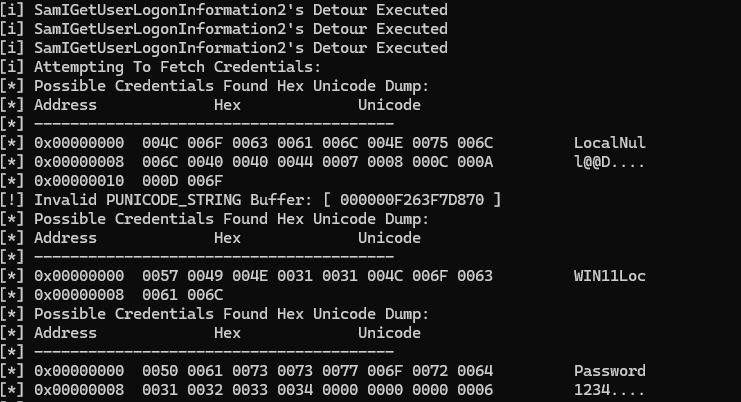
After today’s talk at #TROOPERS25 I’m releasing BitlockMove, a PoC to execute code on remote systems in the context of a loggedon user session 🔥
https://t.co/zXbngHQZDD
No need to steal credentials, no impersonation, no injection needed 👌
Following @ShitSecure's TROOPERS talk and release of BitlockMove, we're releasing our internal DCOMRunAs PoC made by @SAERXCIT last year.
It uses a similar technique with a few differences, such as DLL hijacking to avoid registry modification.
https://t.co/yq80EAtSEo
JOUR 2 | LEHACK
Le week-end continu et nos équipes sont plus que jamais mobilisées sur notre stand Osint-fr dans l'espace associations.
Vous vous demandez ce qui se cache derrière l'osint ? Nos experts sont là pour vous éclairer.
OSINT-FR | leHACK
Cette année encore, OSINT-FR s’installe au cœur de l'événement leHACK. Rendez-vous dans l’espace associations.
Projets en cours, rencontres… passez nous voir ! On est là pour échanger, partager et faire vivre la communauté.
- Don’t trust EDR alone to protect your organization
- Enforce MFA everywhere
- Audit AD regularly with PingCastle, ScriptSentry, Locksmith, and ADeleginator
- Perform external & internal pentesting annually
- Find an MDR vendor you trust and pay them to help you monitor your environment
- Security starts and ends with people and exists to protect the business