The #1 Danger Isn't Roblox
Ryan Montgomery on the #1 thing parents get wrong about protecting kids from online predators.
Check out the FULL VIDEO here: https://t.co/b1YQYKYx0k
‼️ Researcher Erica Windisch skipped coordinated vulnerability disclosure and published 11 unpatched Tailscale flaws.
In her lab, Tailscale SSH race conditions let one hacked device get root on other servers and add a rogue node.
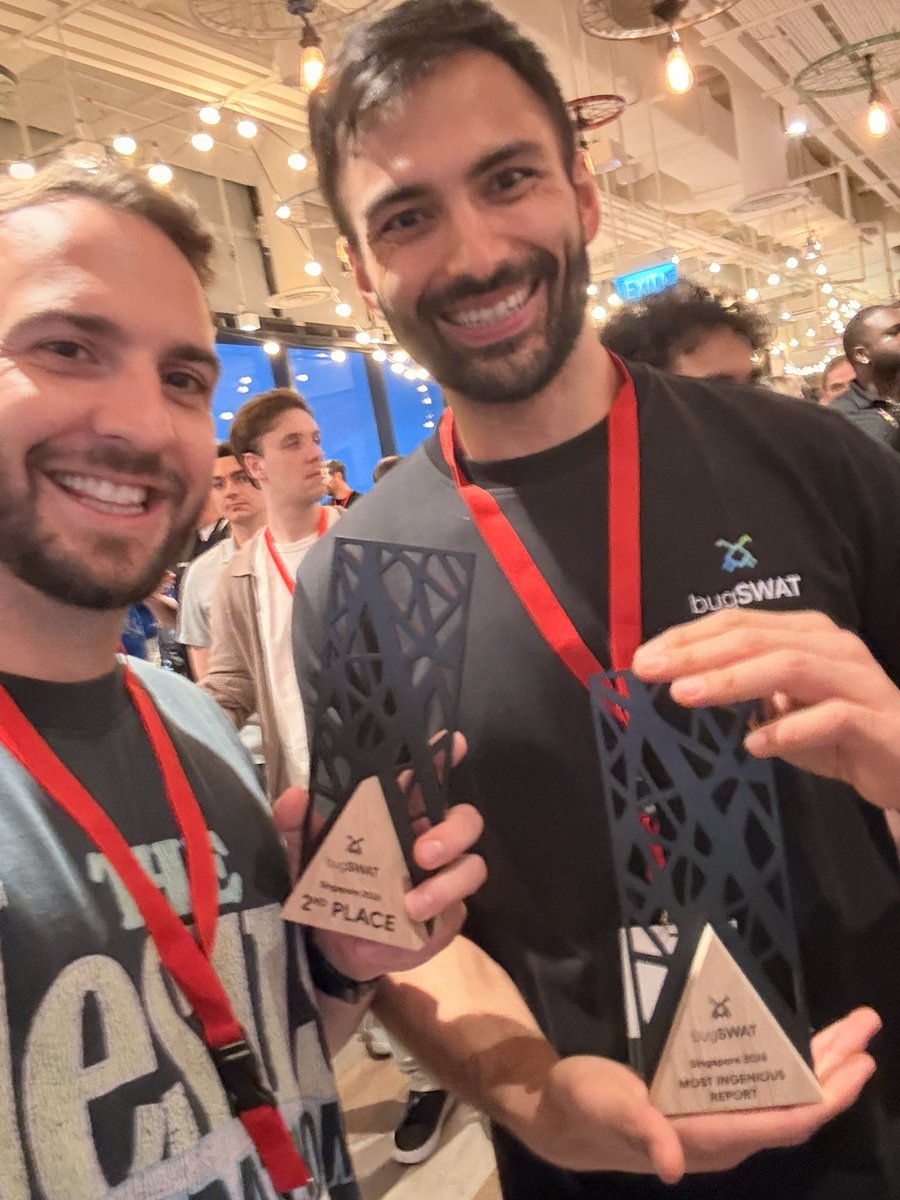
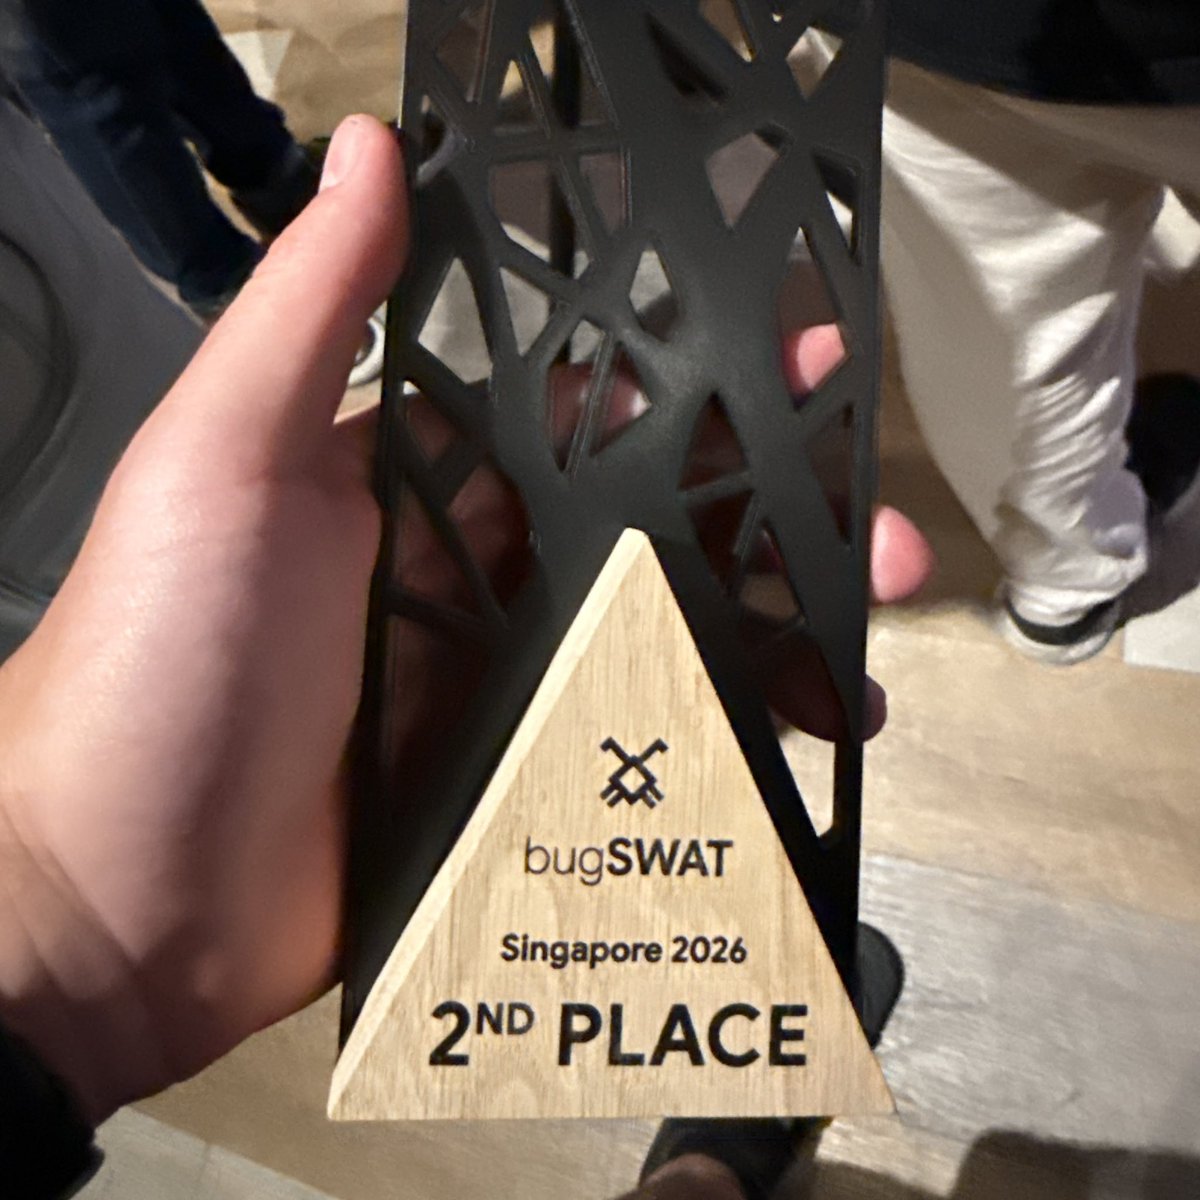
I got second overall at the Google Bugswat in Singapore!! 🎉☺️
It was a talented group of almost 50 hackers so I am really proud of the findings and thankful to have been invited!
I want to type faster than I talk.
I know that the move now is voice, typing is legacy...blah blah blah.
But I still really enjoy typing. It's just a different way to get your thoughts out.
What's your favorite site/app for getting faster at typing?
Right now my favorite way to talk with my agents is through iMessage.
Claude code, Hermes, codex -----> all setup to talk via text.
It's so simple and doesn't rely on me having a remote session or anything. I'll often talk to my agents via a terminal app on my iPhone but there is this one dead zone on my morning walks that kills the connection. iMessage just works.
Setting it up is relatively easy.
- Use photon
- Hermes has a built in way to connect
- Claude Code and other terminal-based harnesses will need a bridge that you can have your agent put together pretty quick.
Imagine an AI agent that grows with you and continuously upgrades itself in the background⚡
——-> That’s exactly what the Curator feature in Hermes does. It helps you refine and improve your skills, removing the ones that don't work and creating new ones automatically.
Check it out! 👇
https://t.co/dBkBjzPYNB
Rule of thumb for MOST of you right now ———-> don’t expose anything to the internet.
- Close all those ports
- Put everything behind a firewall
- Use VPN for access
Keep coding all that personal software but keep your attack surface small.
Windows doesn't save your real password... it saves an NTLM hash.
Grab that hash, feed it into a password cracker (like Hashcat), and crack it back into plain text
-----> Watch how easy it is to grab that hash.
🚨 Nightmare day for cybersecurity
Multiple major security incidents, active exploits, supply chain compromises...
If you run production systems, start patching NOW.
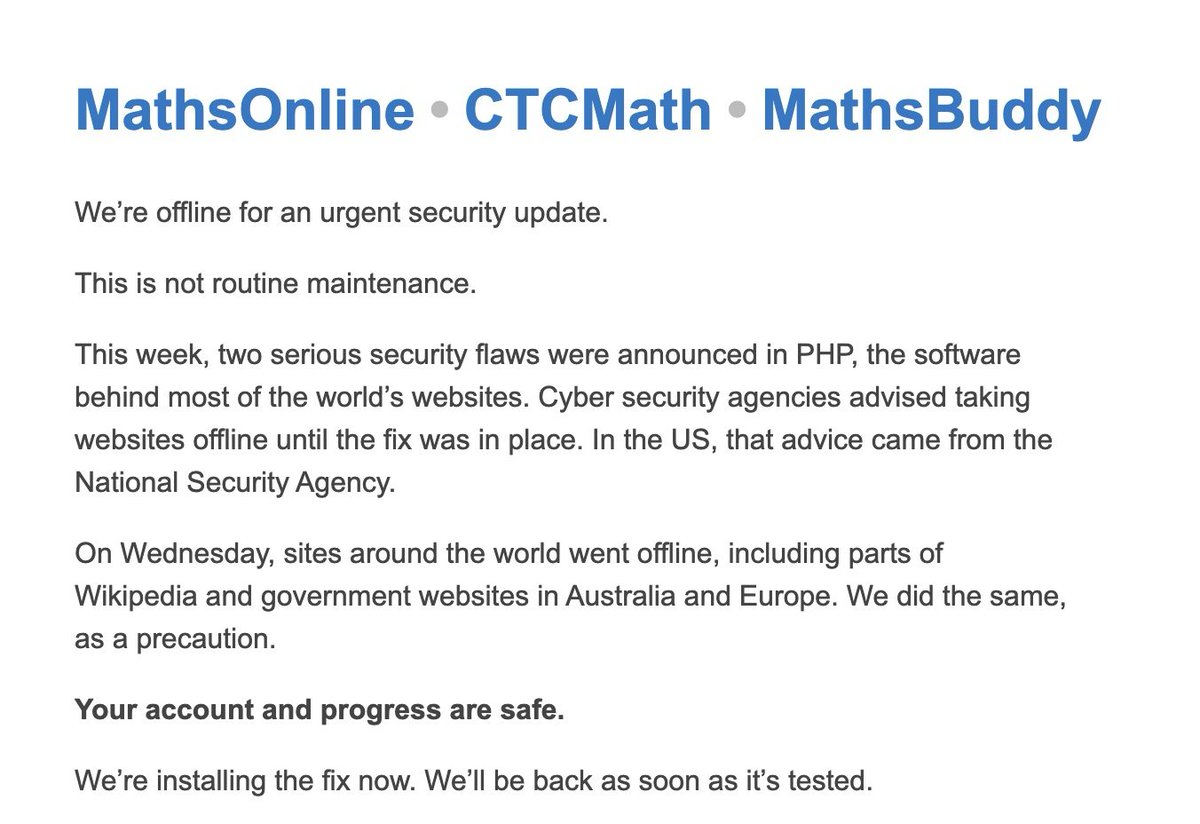
PHP: Two critical unauthenticated RCEs. Attackers already exploiting them. Patch NOW
LiteLLM: v1.107.0 on PyPI and Docker is BACKDOORED. Steals cloud, SSH, and AI credentials. Pin 1.106.2. Rotate secrets.
eMudhra: A certificate authority's keys were crackable. Update your browsers, systems, and trust stores.
Node.js / Next.js / React: Security releases for Brotli RCE, TLS bypasses, and TWO critical Next.js RCEs.
TiDB Cloud: PingCAP breached through stolen credentials. Customer information and other sensitive data exfiltrated. Read the attacker's release, fun stuff.
Plex2Shell: Weaponized within HOURS of the PoC. Attackers already deploying cryptominers and proxy backdoors.
BeyondTrust / Ivanti: Actively exploited zero-days added to CISA's KEV catalog. BeyondTrust attacks linked to a China-nexus campaign.
And that's not even the full list.
Patch. Audit. Rotate. NOW.
We were at DEF CON and found child predators just around us. We chatted with one. Hackers, listen up. We need your help. Watch the interview with @0dayCTF (link in the reply)