😱 I watched @GodfatherOrwa 's insightful talk "The Power of Shodan - Leveraging Shodan for Critical Vulnerabilities" at @NahamSec 's #NahamCon2023 and have condensed the ~25 minute talk for you to read in 2 minutes.
Here's some interesting bug bounty tips and tricks ⬇️
I still see hackers and bug hunters debating this with triagers or programs so I'm reposting my blog from late last year.
One other tip from @ArchAngelDDay is to explain it as an Access Control issue (it is) rather than immediately saying IDOR.
https://t.co/NXnYKtPJgq
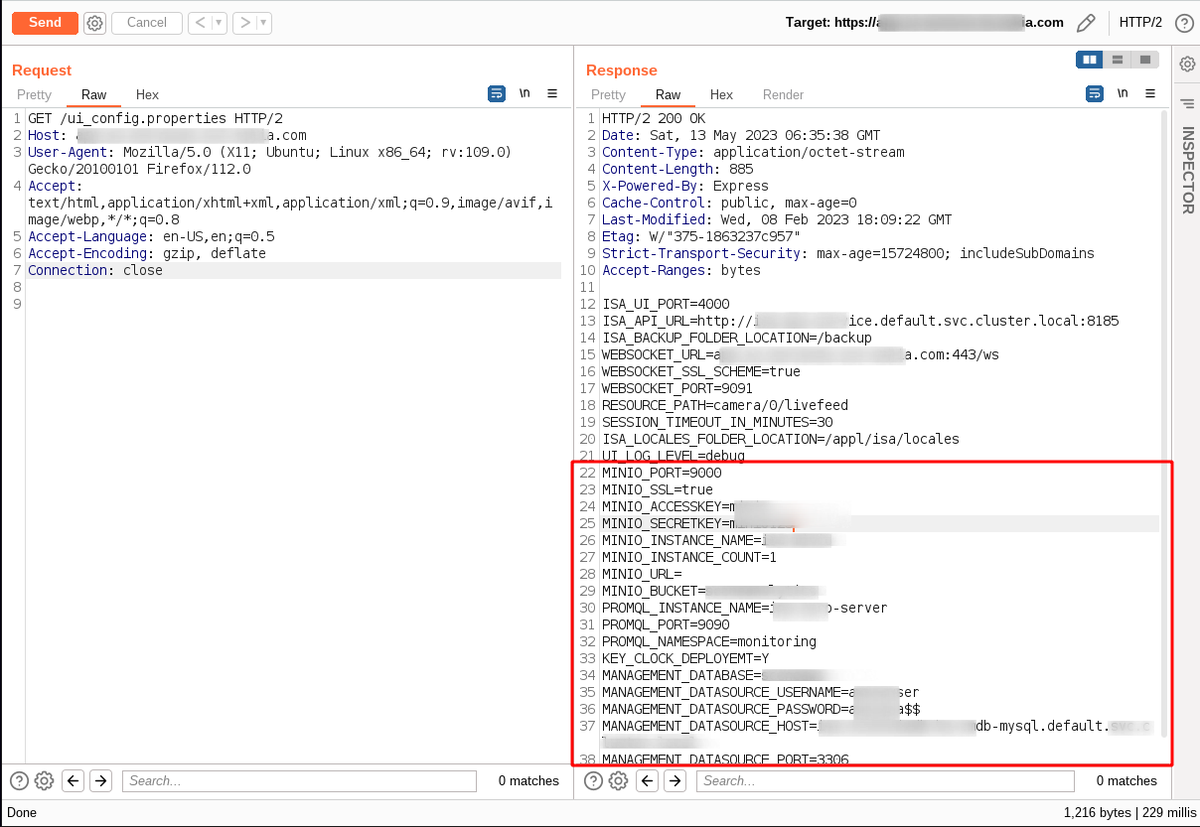
Testers! Add "ui_config.properties" and "https://t.co/wUiA1n8VnO" files to your wordlist, these files contain juicy info like secret tokens and passwords. Excitingly, discovered two on production servers of multinational telecom and IT giants!
#security#Pentesting#Hacking
10 handy practical #hacking tools I've developed over the years 🧰
Check out this thread for the most valuable ones, along with a brief overview of their functions! 🧵👇
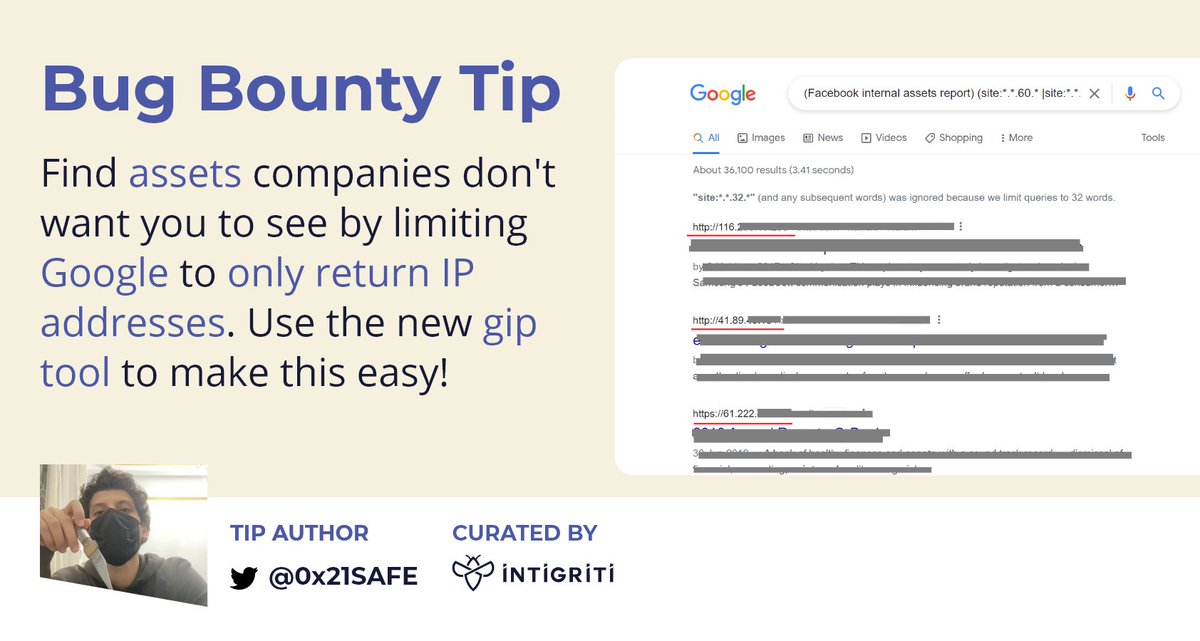
Recon has just become easier! Find hidden assets by using this powerful Google dork to only return IP addresses! 🕵️♀️
Be sure to use the 'gip' tool to automate the process 😎
Thank you @0x21SAFE for providing this one!💪
#bugbounty#bugbountytips 👇
Just found 2 IDORs with the help of authorize
Tip-Don’t test IDOR manually,try to semi-automate using authorize
Check these blogs for better understanding
https://t.co/XGA9lkrbo2
https://t.co/sDNDVCcbBH
https://t.co/q2n8TrAmFD
#bugbounty#bugbountytips
I can't believe PDF journals cost £10-30, here's a free one I made in Word, comes with yearly, monthly, weekly, daily spreads, plus meal plan, habit tracker, goals and video content planning, has links too - designed for bullet journals + Goodnotes (iPad) https://t.co/GW4wwtGLvA