@natolambert What I'm curious to understand is how they deduced that the ultimate motive was distillation. Except if one of the frontier labs notified them, they shouldn't be in a position to see this.
Grab your headphones and join more than 250,000 listeners for the thrilling finale to The Hacker Chronicles. From insider threats, to #supplychain attacks, to #ransomware hostages – each episode is a #cybersecurity lesson. Listen now! https://t.co/1kdqpxyEor
Meet Alice: colleague, neighbor, friend, reluctant hacker. Grab your headphones. Tenable launches The Hacker Chronicles—a new podcast series written by cybersecurity professionals, for everyone. Now available on all major podcast platforms worldwide. https://t.co/rHO6xuKVyx
“While the coronavirus dealt #Travelex the fatal blow, administrators @PwC specifically called out the impact of January’s cyberattack – something which should act as a wake-up call for businesses everywhere." Read our take at @ifsecglobal: https://t.co/dYw63vpByV
Image is everything? #Canon is seemingly the latest in a long list of high-profile attacks against brands effectively being held hostage by the #Maze cybercriminal group. Read our take at @ComputerWeekly: https://t.co/UOztwmOjmG
Or at @thetimes: https://t.co/vyckdr8AAv
We are excited to be a part of Google's Next OnAir Session, and @AlsidOfficial is proud to offer enhanced security to @Google customers using Managed Service for Microsoft Active Directory. View the live session now: https://t.co/LwW539t1nC
LIVE session only! Join global analyst firm @forrester and AD security leader @AlsidOfficial on Tuesday, July 21 at 4 p.m. (CET) to get the latest insights into Active Directory Security and learn how it relates to your IAM strategy. Reserve your spot now: https://t.co/j3nHYxdW6C
We are pleased to announce the newest release of Alsid for AD, Version 2.7! To discover all v2.7 has to offer, get in touch with @AlsidOfficial:
https://t.co/7Bnh5yUkqt
Say hello to the 2020 French cyber startup radar, hot off the press from @wavestoneFR and @Bpifrance. We are proud to count @AlsidOfficial among the innovators driving the future of #cybersecurity.
Explore the latest innovations in #AD Security at https://t.co/G7QKIERHGn
New site. New logo. More security.
Alsid is evolving faster than the $1.5-trillion cybercrime economy. In 2020, our branding reflects the future of security and the simplicity of our solution.
Explore the new site: https://t.co/6vRHNuetV9
Join the security experts of Frost & Sullivan and Alsid on June 4 at 11:30 a.m. (EST) for an exclusive North American webinar:
Reserve your spot at the Frost & Sullivan webinar now: https://t.co/NgQC8ZRuSu
2020 is off to a rocky start for the world. Cybersecurity is no exception. Register now for the Q1 2020 Threat Intel webinar from the Microsoft MVPs at Alsid: https://t.co/m6htxNT2td
Don't forget your roots. Or your vulnerabilities. Check out Alsid's latest interview with Place de l'IT as I break down the forgotten backbone of big enterprise: #ActiveDirectory. (Article in French)
Place de l'IT: https://t.co/7YED9UW9Zv
PDF: https://t.co/JEHBmfZROJ
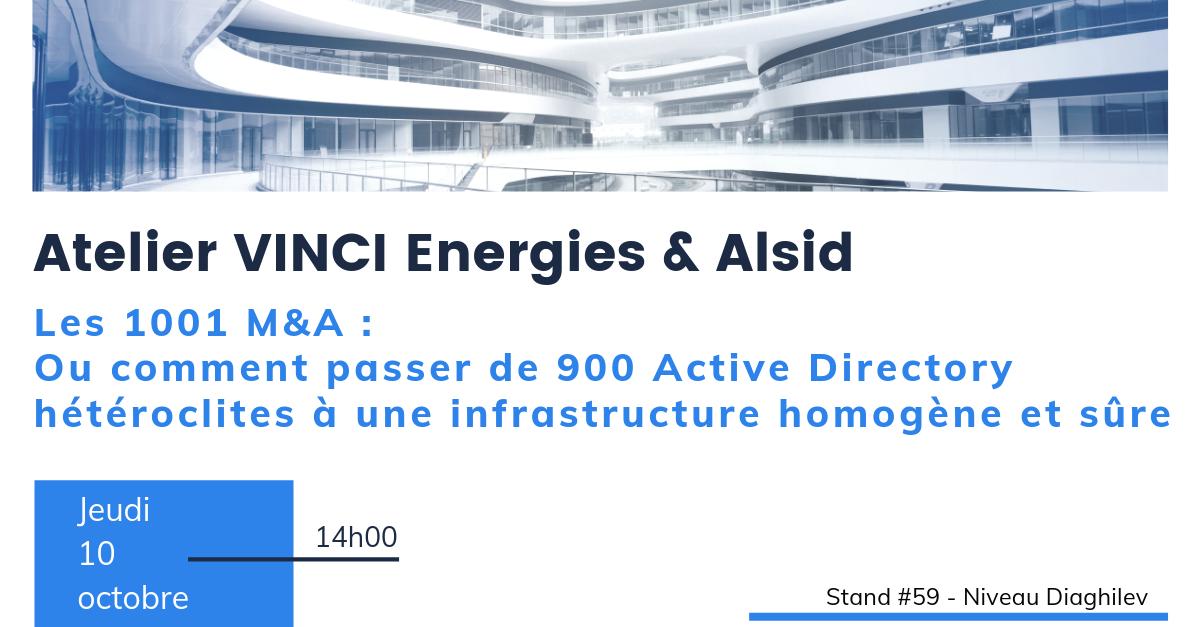
It's only the biggest security event of the year. Join us in Monaco on Oct 10 for "Les Assises de la sécurité 2019" (hint: it's in French). Don't miss @AlsidOfficial's conference exploring how @VINCIEnergies transformed 900 Active Directories into a single, secure infrastructure.
Nice to see @msftsecurity finally adopting #Bloodhound, the open source-tool inspired by the research @AlsidOfficial's co-founder pioneered back in 2014. Five years... not bad.
Here's how Microsoft is hunting for reconnaissance activities: https://t.co/tOLjDCR4SC
#AD#security
You can leave what you know about hackers next to your collection of cassette tapes. These are the 3 hacking trends that will define 2020 and beyond:
#1: Hackers are casting smaller, more tightly-woven nets.
#2 - #3: https://t.co/LUYUTUqoY0
#ActiveDirectory#AD#cybersecurity
There's a decent chance hackers know your shoe size. Oh and your name, email, and shipping address. #ActiveDirectory isn't yet confirmed as the target of the StockX attack, but patterns don't change overnight.
Get the full story from Engadget: https://t.co/qUZC5NRIlr
Call it the 1-2 punch.
A month after its court system was crippled by #Ryuk#ransomware, Georgia has another black eye. If you're sick of just treating the symptoms, here's how to convince key decision makers to invest in real #AD security: https://t.co/BFfUYsPkzw
Take a guess. How long does a hacker need to infect your network after the first compromised system? A 30k-breach analysis by @CrowdStrike revealed the answer: less than 20 minutes.
Shore up your #AD defenses with these indicators of exposure: https://t.co/zJ0rj9AaZy