🚨 Threat actor claims to be sharing 100,000 new Coinbase user records on a dark web forum.
📌 United States 🇺🇸
Industry: Cryptocurrency
Type: Data Leak
Threat Actor: Lud
Samples: Yes
Data fields included:
▪️ Names, Email addresses, Phone numbers, Country
Sample data visible showing user records with personal information.
⚠ Read this. Then read it again. Understand what it implies. Basically: A TA found a way to abuse commercial residential proxies to query your local network and attack local devices.
This is a super spreading event!
It bypasses NAT completely.
https://t.co/EJWazxKfa4
There is a restaurant in the United States called "Waffle House". Waffle House is notorious for it's poor customer service, history of violence breaking out in the restaurant, it being open primarily in dangerous areas, and it also being open during severe weather events.
Waffle House is typically open during severe hurricanes and tornadic weather. The restaurants willingness to remain open during potentially life threatening weather has resulted in meteorologists creating a scale which measures weather severity based on whether or not Waffle House is open.
Despite the restaurants poor reputation, it has a cult like following in the United States. People go to the restaurant expecting poor service because the restaurant is ridiculously affordable and the food is pretty good.
One time I visited Waffle House with a friend. When we were waiting on our food the staff became frustrated with a customer who had locked themselves in the bathroom. Eventually one of the cooks busted down the door. They discovered the customer, a homeless looking person, was overdosing on narcotics on the floor.
While eating our food, EMTs and police officers were performing CPR on the customer. Staff were arguing about the door being broken. Nobody eating seemed bothered by the situation unfolding. It was a surreal experience.
This situation is not unique to me. If you take a moment of your time to lookup Waffle House footage online you'll see hundreds of videos depicting situations similar to mine.
I recommend everyone visit Waffle House.
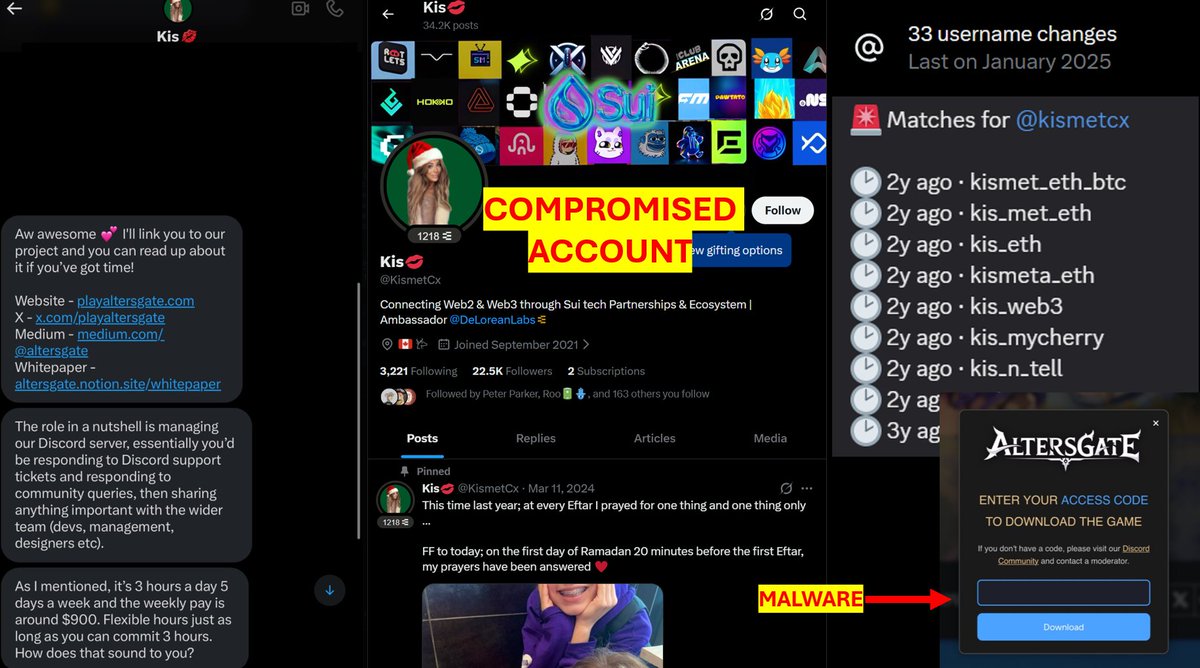
⚠️Compromised Account Sending Malware⚠️
An X account with some @SuiNetwork influence is compromised and sending DMs with links leading to malware downloads...
Scammer got a few victims, so if you receive a DM from @KismetCx ignore it!!!!
New video dropped! 🤓
Vibe hunting through @ValidinLLC with no preparation at all, just pivoting on whatever looks interesting and seeing where it takes us 🐇🕳️ We stumbled across SmartApe, SmokedHam, Mintsloader ... Also caught up with Kenneth, the mind behind Validin! 🧠
https://t.co/rbANaslmPN
Latest #Endgame episode about #Rhadamanthys takedown.
Funny how they not even subtly hint that Rhada Admins are/where stealing (high value) data from their customers. Potentially with customers never seeing the logs. Criminals will be criminals.
https://t.co/TWefW9XdFP
‼️🇰🇵 And another North Korean state-sponsored hacker caught trying to get that sweet Western money for the great, yet petty, Kim Jong-un.
Meet “Jesús Sebastián” from Barranquilla, Colombia. Does he speak Spanish? I don’t think so.
If you didn’t get locked out of X this morning (due to X re-enrollment bug) then your security sucks. Get a yubikey (security key) for 2FA and stop being dumb.
More rumours! (⌛️?)
Rhadamanthys customer message:
Dear <redacted>,
International law enforcement agencies have designated Rhadamanthys as a target under OPERATION ENDGAME.
Our data points to your possible involvement with Rhadamanthys. This information has been recorded by global law enforcement agencies. The seized customer data is currently being analyzed. Anyone involved should carefully consider their position.
Be sure to check out the Operation Endgame website for the Rhadamanthys-themed episode on Thursday, November 13th.
Think about (your/our) next step.
Contact:
Telegram: @operationendgame
Website: https://t.co/InVdgfzLDq
My team @HuntressLabs is hiring a Senior Hunt & Response Analyst (West Coast, 3-5 years exp).
Not going to lie, this is one of the best teams I have worked for in my entire career.
We want the person who:
😰 Makes threat actors sweat
🎯 You hunt threats for fun
🔥 Actually enjoys incident response
😴 You can timeline an incident while half asleep
💀 Knows their way around a compromised system blindfolded
Cultural fit? We protect ALL businesses, not just the 1%. If you think every company deserves good security and you get genuinely hyped about kicking bad guys' asses, we want you.
You know who you are. This is your calling, come work with us💙
https://t.co/SRbBXDuURR
They actually had thousands.
Each got paid $3-9k/year.
Rarely would make it a year though bc the biggest cost advantage to outsourcing CX is scaling it up and down like it’s fuckin AWS.
As should be expected, the piles of Indians sold lookups and clicks for $50-$500/pop instead of answering tickets.
First thoughts about #Rhadamanthys Stealer "disruption" (?) and what to expect in the next days with the current information as of November 13th:
The same way I did with Lumma I want to share some words (https://t.co/dWAQNKnjv1)
Leaving to one side from the discussion anything related to VenomRAT, and focusing on Rhadamanthys (and indirectly on the Elysium Botnet, which is in fact allegedly a product developed and offered by the same people behind Rhadamanthys and a product which I don't have much knowledge with), talking about a complete disruption, dismantling and whatever synonym as for now, should be wrong.
Short answer - Was Rhadamanthys completely disrupted? As far as I understand, NO. It's maybe too soon to talk big words.
Is Rhadamanthys working as for now? a completely YES for yesterday, still not see clear evidence about today, need time. See photo 1.
What are we observing on major malware traffic networks (the first ones to respond to changes )? A shift towards other traditional malware solutions such as StealC or Vidar, also newer ones such as AURA.
This is probably provoked by the words of the Rhadamanthys administration after the operation endgame was noticed. Rhadamanthys advised customers to stop work for some days (see photo 2). Some customers related that were personally messaged by Rhadamanthys administration stating that "he need some days for opsec", currently he is not active since yesterday after leaving last messages.
These quick changes happened before, for just some little time to not stop installation networks while the main malware project is having issues. If the original malware provider is back, it will be changed back again following the patterns.
I observed that the last days direct message from LE to some customers, as well as Rhadamanthys advices provoked some panel owners to wipe servers and accounts, so the malware work at some point was stopped momentarily just to be replaced by these other solutions.
Is there a possibility that some customers of Rhadamanthys have not been affected by the last events? YES. Due the naturality of the stealer, that I think is clearly differentiated by two installation methods (to summarize, Rhadamanthys offer a local installation to their customers, where server is controlled by customer and other service where panel is given already ready-to-use), customers that have a local installation may have not been affected as much as other people. This is just my hypothesis over what I observe. Can the people who are not affected be identified any way? YES, as long as Rhadamanthys administration saved any records from their customers.
About the information on victims retrieved by LE and submitted to platforms such as HIBP (2 million impacted email addresses and 7.4 million passwords to HIBP). These numbers reaffirm the scope of the operation and the major probability that
customers data on the whole meaning has not been affected by recent LE operation. These numbers feel small for the complete threat of what Rhadamanthys has represented over these years. If we observe other malware families busted over these years, I took for example Raccoon Stealer, the news talked about 50 million unique credentials (https://t.co/B0OgDwHUIT) something more reasonable, and this happened in 2022 where I believe victim traffic numbers were not as high as the following years. So I estimate the 7 million credentials retrieved over Operation Endgame now (considering that all came from Rhadamanthys that is not clearly stated as they could be from VenomRAT too) under the 20% range volume of all Rhadamanthys operation so far, being optimistic. It has been verified very quickly how some credentials originated from Rhadamanthys victims from publicly available sources are not included in this dataset retrieved by LE, so although you can search yourself if you have been pwned and show no results, you still could have been a victim of Rhadamanthys because not all data (and sincerely not a considerable amount) from Rhadamanthys servers has been retrieved.
There is also a interesting point over the Rhadamanthys reputation on the malware community. He is a trusted individual, that has recovered from many reputation incidents in the past. It is one of the major infostealers that no provides geo-block to the CIS countries (probably the biggest one doing this) and this feature provoked being banned from promotion on all major Russian-speaking forums, and also being very appreciated ironically by other people just because this, also because of a higher development side than other MaaS solutions . Although reputation kickbacks, it hold a user base and in the last months it dominated the market massively.
What to expect on the next days?
There's two possibilities, as seen before with other people:
1. Rhadamanthys owner never returns from hold by external pressures, attacks against honor and reputation and if the "opsec issues" has any more deep meaning, customers left with no reply and project left to death.
2. Rhadamanthys reach customers again, fix problems, get to work promptly as usual, nothing happened. (Lumma Style)
Time will tell how things turn out⌛️