I currently do analysis of PKU2U protocol which is used by joined clients to Azure AD during an authentification. For my part, this protocol is very interest because we can call it "The Kerberos of Web" lol.
hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: https://t.co/0ffrO586PJ
Download: https://t.co/Grn4jZmAWr
One must assume a universal PHP RCE exists, paired with the current state of Linux LPEs (everyone has a stash of LPE 0days), plus the CVE-2026-99999 KVM escape... What a time to be an APT.
That said, the universal PHP RCE is not easily clanked. Proof: https://t.co/obeBmvO5KT
Calling it now: Chrome and Mozilla will remove eMudhra as a G1 root, nulling them as a CA.
On 20 Oct, eMudhra had 24 hours to give an explanation of what exactly happened with the mis-signed certificate. They did not; asked for more time; and now blame “investors/customers” 🤡
Set session.upload_progress.enabled=0 till next PHP release to block an unlikely RCE vector (CVE-2026-115560). Already recommended for CVE-2026-109619 Wed, keep disabled. Only apps with non-default serialize_handler switching it to "php" at runtime can be affected. #php#phpc
🚨 UPDATE: A public PoC demonstrates RCE on PHP 8.5.12, even after the October 21 security patches.
The attack is separate from the patched php2shell CVEs and requires specific session configurations and application weaknesses.
Our earlier concerns about PHP session handling remain relevant.
We've updated php2shell-protection with additional hardening guidance.
#php #cybercurity
https://t.co/UAHmYdVr7V
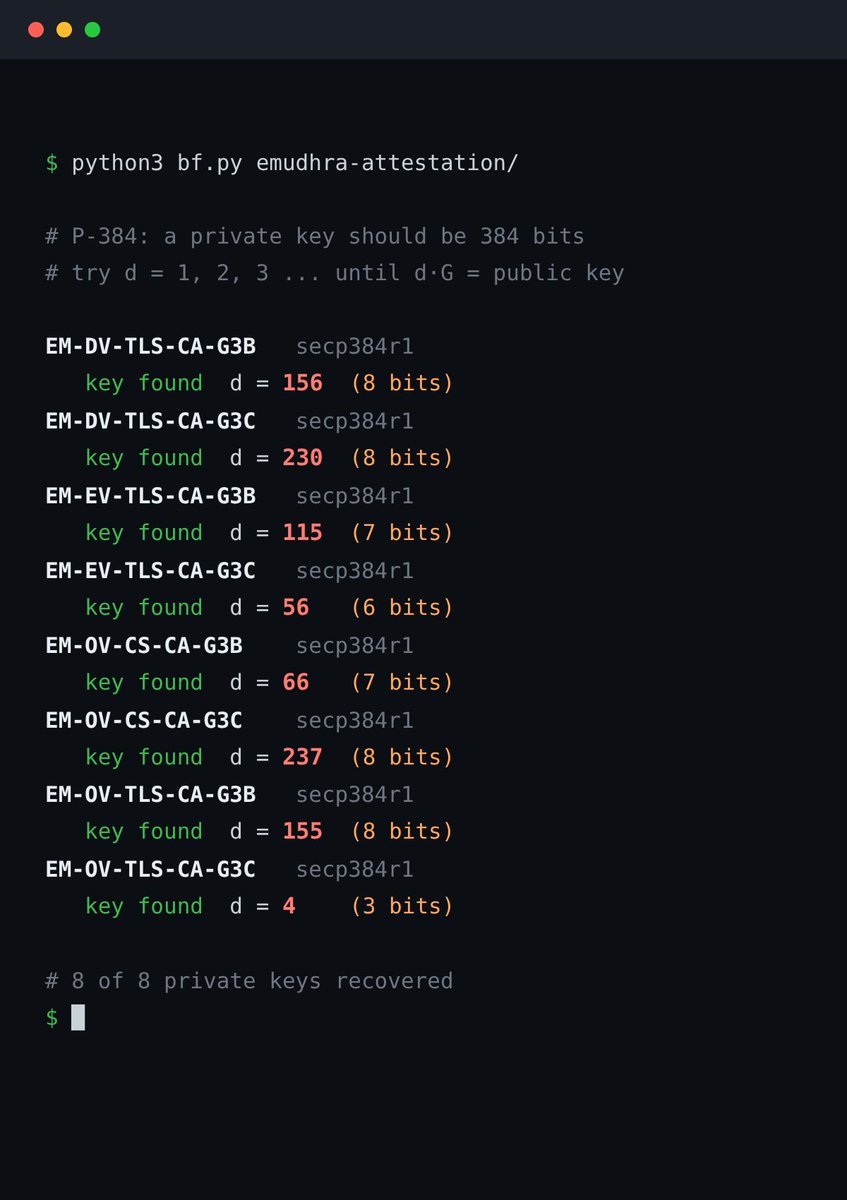
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
You COULDNT HAVE FUCKING WAITED 14 Hours.
i hope your forever blacklisted from cybersec/related industries for dropping a unpatched critical 1day on twitter you fucking idiot
Si vous avez téléchargé aujourd'hui la dernière version de CLI d'OVHcloud, merci de la mettre à jour à nouveau très rapidement. Sinon effacer. Il s'agit de repo:
https://t.co/mSILpJyTEq
La version CLI de 14h47 a été compromise par un hacker. Nous l'avons détecté et bloqué à 16h21. Merci au client qui nous a remonté le souci. La version compromise est v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0.
La version v0.10.0 et la future 0.16.0 est clean.
On vient de finit les premières vérifications et aucun autre repo n'est affecté. Nous avons aussi retracé l'incident. Le hacker a utilisé le compte github d'un des développeurs et a ajouté un binaire dont le job est récupérer les secrets sur le disque. La qualité du binaire est médiocre mais il peut aller jusqu'au bout. Si vous êtes concernés, merci de changer tous les secrets sur votre disque.
On continue les recherches sur le binaire et on va publier les détails additionnels sous peu.
A former senior cybersecurity researcher with Microsoft’s Detection and Response Team received a care package of Russian trinkets on his doorstep after investigating Midnight Blizzard 😯: https://t.co/fUQ7Q2ZsOn
Je trouve près de 3000 adresses IP 🇫🇷 exposant une console Danfoss Storeview. Quand on explique qu'exposer directement sur Internet une interface d'administration, c'est pas bien, c'est pas juste pour les équipements réseau... 😘
This hacker is truly legendary. A complete amateur.
1. He left directory listing enabled on his own server, so researchers could figure out who he was with barely any effort.
2. They found files like CLAUDE.md and went through his Claude Code sessions.
3. There were questions like, “Where can I sell this data?”
4. He’d also asked, “Can you write my résumé?” That pretty much handed them all his personal information.
5. Apparently, he’s a student at South China University of Technology living in Guangdong. His name, phone number, and where he lives have all been identified.