My first module is now avaiable on @metasploit framework that exploit an object injection (CVE-2019-9055) with a nice payload on @cmsms! 🎉🎉🎉 Try it now🤓 #infosec#CyberSec#hacking
https://t.co/n3MsyUVzPX
NEW: Apple is preparing to implement a kernel level EDR system in iOS
When activated, the watchdog, known as https://t.co/dohCGrRsH1.iokit.EndpointSecuritySE, which is still in beta, will monitor deep system telemetry in order to spot signs of exploitation
More details:
Al Council of Europe con @sk4pwn e Marco Musumeci per due talk, presso la conferenza internazionale #UndergroundEconomy a Strasburgo, sulle analisi forensi di #smartphone infetti da #malware.
Ringrazio Sandro Rossetti - il quarto relatore, che non compare nella foto di gruppo - oltre a Matteo Vinci - che non è potuto venire con noi ma è uno dei principali ricercatori del team Forenser da cui nascono i nostri interventi qui in Francia - il @teamcymru e tutti gli organizzatori di #UE26.
Come ogni anno, è un onore avere la possibilità di presentare in un contesto internazionale i risultati delle ricerche svolte dal team @forensersrl, dai quali sta scaturendo un interessante confronto tra professionisti della sicurezza e forze dell'ordine di decine di paesi.
NEW INVESTIGATION: Serbia's pro-democracy movement hit with spyware in runup to 2026 elections.
📱iPhone: Newly confirmed Pegasus zero-click
🤖Android: Stealthier NoviSpy
+ Wave of Apple mercenary spyware notifications.
14+ targets already IDd: students, activists, opposition MP, etc.
Investigation ongoing. 1/
By @ShareConference w/forensic support from us @citizenlab & @AmnestyTech
https://t.co/QIXRYveABL
tmp.0ut #5 is out!
Fresh ELF research and binary exploitation goodness: polyglot ELFs for anti-forensics, Brainfuck as a ROP compiler, a deep dive into how the Linux kernel loads executables and more😄.
https://t.co/VaNcn2c8PQ
ALERT: Did you get a notification like this today?
Seek expert security help asap!
Apple just sent out a fresh round of threat notifications about mercenary spyware.
That means tech like Pegasus used by governments to spy on you.
Here are steps to take right now 1/
Have the publicly accessible #ChatGPT "shared chats", which drew much attention after @henkvaness investigation, really disappeared from the web? Apparently not: @OpenAI deindexed and excluded the chatgpt[.]com URLs from the Wayback Machine… but they forgot another domain! 😅
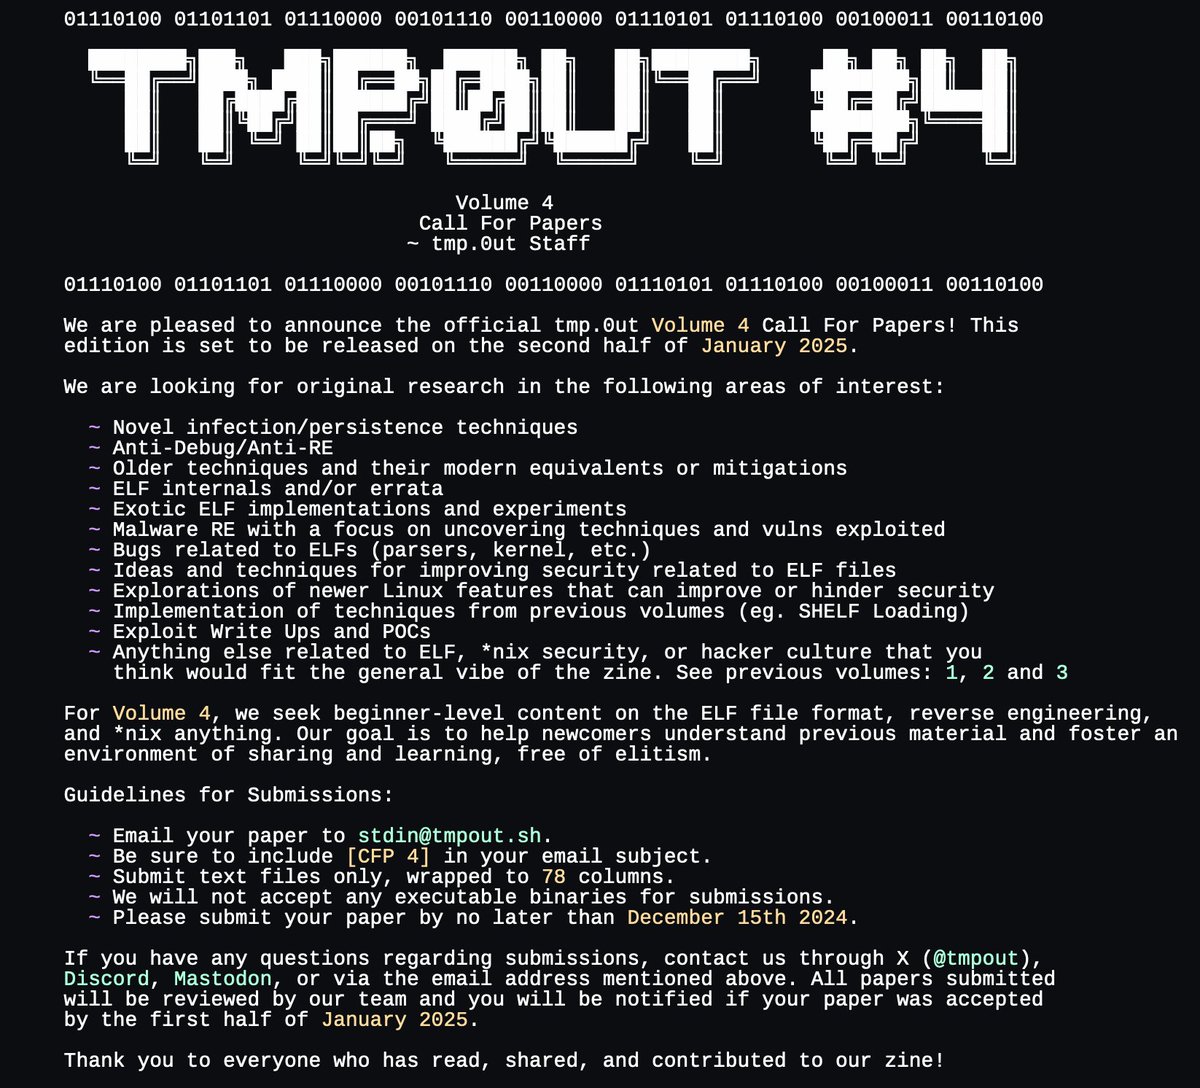
tmp.0ut Volume 4 is happening! Our call for papers is now open, and we're excited to see what you've been working on 👀 read the full announcement here: https://t.co/95d9RLYzZV
Oggi io e @bytevsbyt3 abbiamo pubblicato l’articolo sul blog di @SoterITSecurity sulla ricerca condotta sul client VPN di #Zyxel, che ci ha portato ad ottenere un privilege escalation su Windows, tramite il CVE-2023-5593
https://t.co/iYAcBfUJDQ
Through the vulnerability we were able to obtain a local privilege escalation on Windows. In the coming weeks we will publish an article on our blog where we will show the vulnerability in detail, analyzing the exploit. For now, update your #Zyxel VPN client!
Stay tuned
This morning a #security advisory was published by Zyxel, with CVE-2023-5593, of a memory corruption vulnerability found during a research conducted by me and @bytevsbyt3 on their VPN client for Windows.
https://t.co/iQG7RrbnUO
@BlackHatcker@metasploit@cmsms I think the problem is due to using python2 because the script was written using that version but as of today it is no longer supported so it may not work. I suggest you convert it for python3, removing unnecessary things like the termcolor library (then using only print func)
My first module is now avaiable on @metasploit framework that exploit an object injection (CVE-2019-9055) with a nice payload on @cmsms! 🎉🎉🎉 Try it now🤓 #infosec#CyberSec#hacking
https://t.co/n3MsyUVzPX
🔥 Brace yourself #LocalPotato is out 🥔
Our new NTLM reflection attack in local authentication allows for arbitrary file read/write & elevation of privilege.
Patched by Microsoft, but other protocols may still be vulnerable.
cc @decoder_it
Enjoy! 👇
https://t.co/3Lge45hb7L