THIS IS F**KING DANGEROUS.
I JUST FOUND A WAY TO TURN CLAUDE INTO AN AUTONOMOUS PENTESTER.
HEXSTRIKE AI connects an LLM to 150+ cybersecurity tools through MCP and lets AI agents actually use them.
→ 12 specialized agents
→ 150+ security tools
→ Web + network security testing
→ Automated pentesting workflows
→ Local execution on Kali Linux
And this is where it gets crazy.
Claude can analyze a target, choose the right tool, generate the payload, run the test, and reason through the result.
It even demonstrated solving a PortSwigger SQL injection lab autonomously.
This is no longer just AI explaining cybersecurity.
AI IS STARTING TO ACTUALLY DO THE WORK.
REPO BELOW
Are you struggling to pay a huge amount on paid courses?
I'm giving you access to 20+ FREE Courses
1. Artificial Intelligence
2. Machine Learning
3. Cloud Computing
4. Ethical Hacking
5. Data Analytics
6. AWS Certified
7. Data Science
8. BIG DATA
9. Python
10. MBA
To get it, just:
1. Like & Retweet
2. Comment "Free"
3. MUST be Following (so that I can dm)
🔥 Filter out noise in Burp Suite 🔥
➡️ While you are testing with Burp Suite, you may want to add these patterns into the Burp Suite > Proxy > Options > TLS Pass Through settings:
.*\.google\.com
.*\.gstatic\.com
.*\.googleapis\.com
.*\.pki\.goog
.*\.mozilla\..*
📃 Now all underlying connections to these hosts will go to them directly, without passing through the proxy.
No more noise in our proxy logs!
#bugbounty #bugbountytips #bugbountytip #cybersecurity
Easy Account Take Over
1.Go to https://t.co/4UNLtLoII1
2. Put the domain and search for urls
3. Type in the filter ( %40 ) and search
4. Get a lot of urls that have a parameter leaks the email and password of the users
By: @Sayed_v2
credit: @RootMoksha
#BugBounty
🔥 Found SQL Injection to Account Takeover Manually :)
1. Enter mobile number to login intercept
{"mobile_number":"8888888888"} >> 200
{"mobile_number":"8888888888'"} >> 500
{"mobile_number":"8888888888''"} >> 200
credit: @bbr_bug#bugbountytips
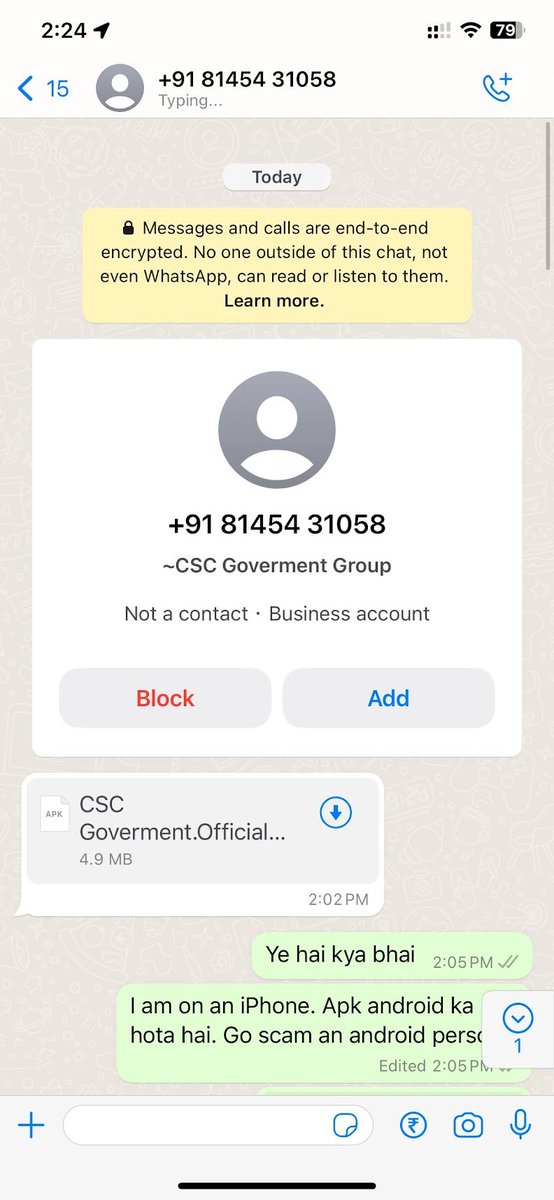
I spoke with yet another scammer today. I don't know why I do this, but here we go.
It all started with a few annoying Whatsapp messages trying to scam me. But we ended up wishing each other good luck 😂
1/n
Planning to add a bypassing secuity controls primer and a payload mutation section to https://t.co/nn3yrEJVsf
I dont know if it will fit in 2 days anymore! 😬😅