🎯 𝗛𝗶𝗴𝗵-𝗙𝗶𝗱𝗲𝗹𝗶𝘁𝘆 𝗢𝘂𝘁𝗹𝗼𝗼𝗸 𝗭𝗲𝗿𝗼-𝗗𝗮𝘆 𝗗𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻
Microsoft’s November 2026 Patch Tuesday updates include 𝗖𝗩𝗘-𝟮𝟬𝟮𝟲-𝟭𝟮𝟰𝟭𝟵𝟰, an Outlook zero-day vulnerability reported as 𝗮𝗰𝘁𝗶𝘃𝗲𝗹𝘆 𝗲𝘅𝗽𝗹𝗼𝗶𝘁𝗲𝗱, according to 𝗖𝗜𝗦𝗔’𝘀 𝗡𝗼𝘃𝗲𝗺𝗯𝗲𝗿 𝟭𝟬 𝗮𝗱𝘃𝗶𝘀𝗼𝗿𝘆.
https://t.co/07prs1IiCv
An unauthenticated attacker could send a specially crafted message file and convince a user to open it in an affected version of Microsoft Outlook. Opening the malicious file could cause Outlook to connect to an attacker-controlled network location 𝘄𝗶𝘁𝗵𝗼𝘂𝘁 𝗱𝗶𝘀𝗽𝗹𝗮𝘆𝗶𝗻𝗴 𝘁𝗵𝗲 𝘂𝘀𝘂𝗮𝗹 𝗲𝘅𝘁𝗲𝗿𝗻𝗮𝗹-𝗰𝗼𝗻𝘁𝗲𝗻𝘁 𝘄𝗮𝗿𝗻𝗶𝗻𝗴, potentially exposing the user’s 𝗡𝗧𝗟𝗠𝘃𝟮 𝗵𝗮𝘀𝗵.
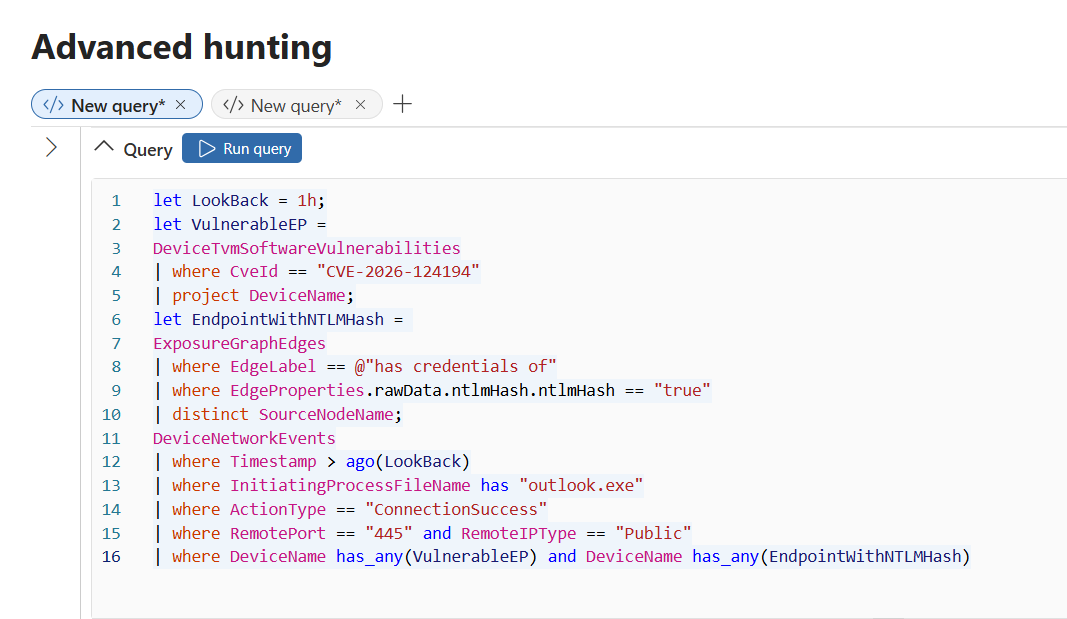
🛡️ I’m sharing a 𝗵𝗶𝗴𝗵-𝗳𝗶𝗱𝗲𝗹𝗶𝘁𝘆 𝗞𝗤𝗟 𝗱𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻 for fellow Microsoft Defender for Endpoint (MDE) defenders to help identify potential exploitation attempts while organizations work toward fully patching affected system.
KQL Detection:
https://t.co/g2WPCuwESu
#Outlook #ZeroDay #MicrosoftDefender #ThreatDetection #ThreatHunting
To all my Windows DFIR friends out there! 🔥
Have you ever wished for a single Windows forensic artifact parsing tool that could parse just about anything, while being blazing fast, stable, well-organized, memory-safe, standalone, and cross-platform?
Well, I certainly have!
So, I spent the past month obsessively building one! 😎
Say hello to "Juntei" (准胝)! 🎉
https://t.co/3Xf7ZbXYyo
https://t.co/ntazHaljHw
Think of it as "Hayabusa, but for non-EVTX artifacts!"
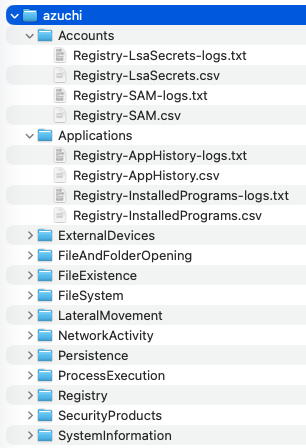
It can scan regular directories, VHDX, and E01 files directly, without even having to mount them.
I just ran a performance test on 30 Windows triage data collections (125 GB total), and my MacBook Pro M4 cranked out 40 GB of parsed data in less than 5 minutes! 🚀
It's trivial to use. Just run the "auto-parse" command, and Juntei will automatically parse all supported artifacts for you.
Want a super timeline? No problem! Simply run "super-timeline" against the parsed output directory, and you're good to go!
But here's a little warning! ⚠️
The "SUPER" in super timeline is no joke! 😂
At the moment, the generated timelines can be about 5 times larger than the parsed data directory!
So here's my recommendation: Run Hayabusa first to pinpoint when an incident occurred, then filter your timeline to the relevant time period.
By the way, JSONL super timelines are generated in a Timesketch-compatible format by default, so you can import them directly!
For analyzing CSV output, I highly recommend IRFlow Timeline!
I've created dedicated templates to ensure the different field types are correctly recognized and displayed.
https://t.co/iczzGaD7NV (Wait for v2 to be released, or use one of my forks!)
macOS:
https://t.co/wh51vxwcOU
Windows:
https://t.co/Vav5rnVJ2v
Linux:
https://t.co/yAg9aBk4sp
I hope you enjoy using it! 🔥
If you find Juntei useful, please help spread the word to your fellow DFIR friends!
And don't forget to give us a star on GitHub! ⭐ 🙏
Enjoy! 🤗
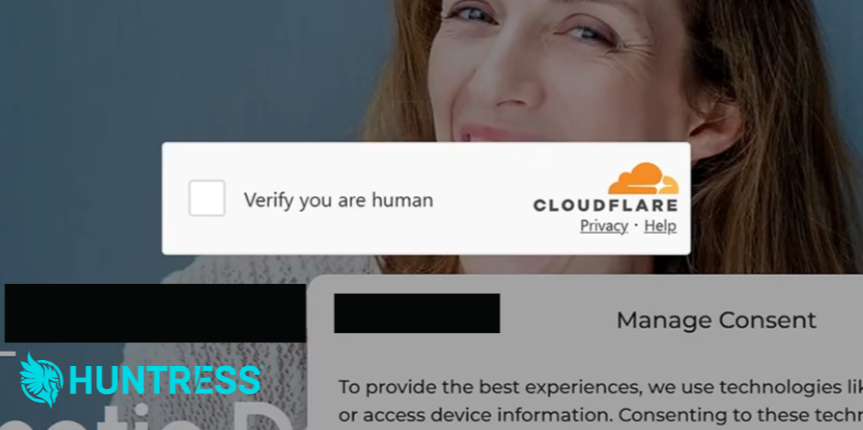
ClickFix has expanded beyond simple malware delivery into complex attack chains that establish persistence, support lateral movement, and enable reconnaissance and credential theft.
🖇️ Read our round-up of the latest ClickFix variations we’ve seen:
https://t.co/Dpwf4hnd3l
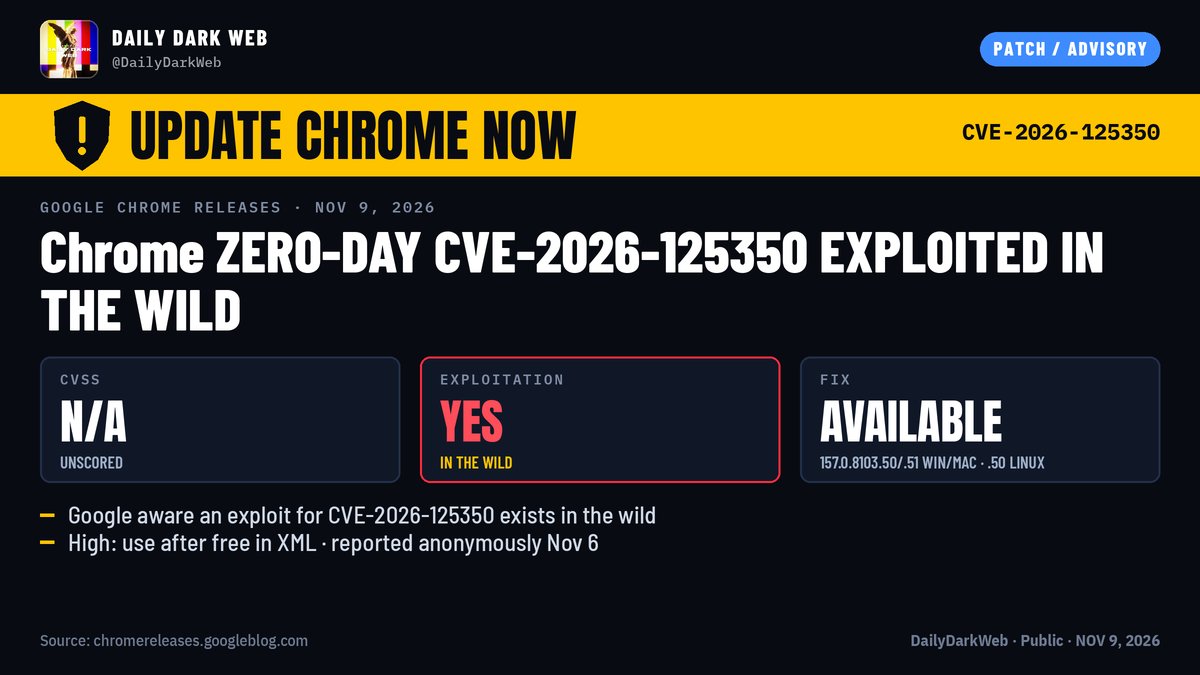
🚨 CHROME ZERO-DAY CVE-2026-125350 EXPLOITED IN THE WILD (XML USE-AFTER-FREE)
Google’s Nov 9, 2026 Stable Channel Update for Desktop patches a High-severity use-after-free in Chrome’s XML component that Google says is already exploited in the wild.
• CVE-2026-125350 — High — Use after free in XML — reported anonymously on Nov 6, 2026
• Google: “aware that an exploit for CVE-2026-125350 exists in the wild”
• Fixed in Stable 157.0.8103.50/.51 (Windows/Mac) and 157.0.8103.50 (Linux); rollout over coming days/weeks
• This update includes 9 security fixes total (no attribution or target details disclosed)
⚠️ Analyst Note:
Treat this as an actively exploited browser zero-day until your fleet is on 157.0.8103.50+ (or the matching managed channel). Bug details stay restricted until most users update. No CISA KEV listing at packaging time. Update via Help → About Google Chrome, or push the Stable build through your enterprise channel.
Official:
https://t.co/va0zT6Bys5
#DDW #Chrome #ZeroDay #CVE2026125350 #PatchNow
jokes komika lahir dari keresahan, kalo menyuarakan karhutla aja dilarang? berarti blio belum merasa resah
udah bisa dipanggil beliau lu bangpo, mas hizmi, rigen🔥🔥🔥
UPDATE DARI P4PU4 SELATAN ‼️‼️
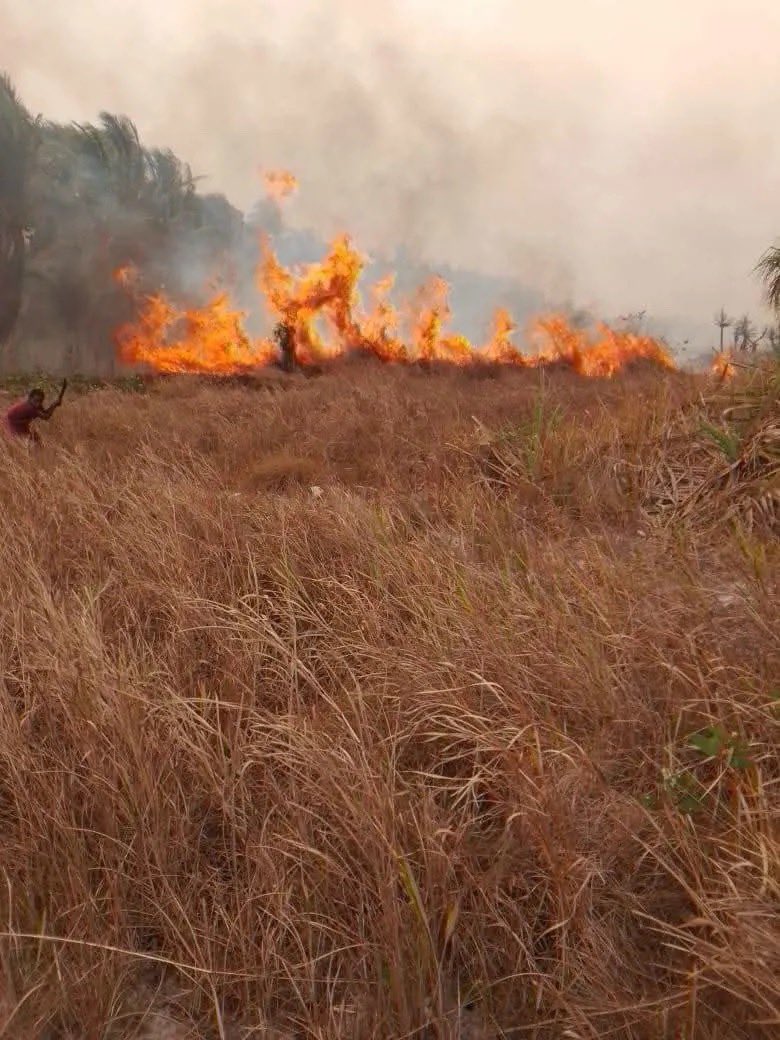
Terjadi kebakaran sabana yang menyebar hingga memasuki pemukiman warga di Kampung Bamol, Distrik Padua, Merauke, Papua Selatan.
UP UP P4PU4 GUYS !!
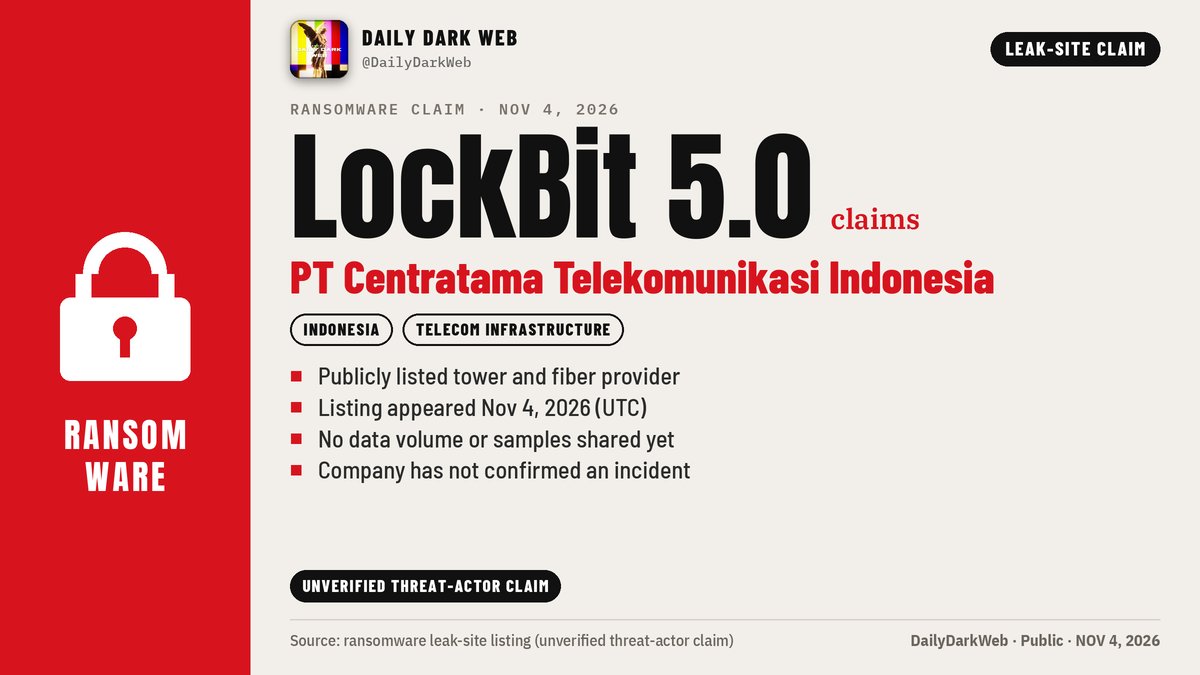
🇮🇩 🚨 INDONESIA: LOCKBIT 5.0 CLAIMS ATTACK ON TELECOM INFRASTRUCTURE FIRM CENTRATAMA
The LockBit 5.0 ransomware operation has listed PT Centratama Telekomunikasi Indonesia Tbk, a publicly listed Indonesian telecom infrastructure provider that runs telecom towers and fiber networks for mobile operators, on its data-leak site.
The listing appeared on Nov 4, 2026 (UTC). No details on the volume or type of data allegedly stolen have been shared so far.
The claim has not been independently verified, and Centratama has not publicly confirmed a cyber incident.
⚠️ Analyst Note:
A breach at a tower and fiber operator could expose network site data, carrier contracts, engineering documents and staff records that are useful for follow-on attacks on Indonesian mobile networks. LockBit has repeatedly hit Indonesian targets. Partners and staff should watch for targeted phishing and invoice fraud. Unverified ransomware claim, NOT confirmation of a breach.
#DDW #DarkWeb #Indonesia #LockBit #Ransomware #Telecom #CriticalInfrastructure #ThreatIntelligence #CyberSecurity
50 legendary internet rabbit holes you can spend hours exploring👇
1. https://t.co/2iUvbwAaCZ — Watch the world via live satellite imagery
2. https://t.co/GfiOjxFI73 — See every plane currently in the sky
3. https://t.co/lEn3nLTR9R — Track all ships at sea in real time
4. https://t.co/I5yGaOEzZO — Live map of winds and storms
5. https://t.co/rvw3ZC5gGa — Watch lightning strikes hitting Earth in real time
6. https://t.co/gnNBRdkYQy — Live list of recent earthquakes
7. https://t.co/prL5T0Dpxx — Ocean cables carrying the internet
8. https://t.co/4JgzOhWVYZ — Watch forests disappear from space
9. https://t.co/qWpItwjYUw — The world's statistics, second by second
10. https://t.co/1TbpxTW9nF — Current number of tweets and searches being posted
11. https://t.co/Ej4QmfSrvU — Compare the true sizes of countries
12. https://t.co/nYqN3SLx6C — Maps from centuries ago
13. https://t.co/eXg5b9rWC8 — Archive of 150,000 historical maps
14. https://t.co/bsHPtbdl0L — World map drawn by volunteers
15. https://t.co/ScUyS7NNFT — Look out the window of a random person around the world
16. https://t.co/SY76MtAzsl — Virtual walks through cities
17. https://t.co/NiKsXOOTJA — Teleport to a random spot on Earth
18. https://t.co/FsYoqLXsd3 — Catalog of the world's strangest places
19. https://t.co/GnqZs3nGjj — Interactive knowledge experiences
20. https://t.co/OB8ieZfrnn — Scale journey from atom to universe (Updated HTML5 link)
21. https://t.co/6mqUtZqjzr — Explore the solar system in 3D
22. https://t.co/9azHcz9lDn — Real sky map in your browser
23. https://t.co/tS2okfo4u0 — NASA's astronomy picture of the day
24. https://t.co/Cs0gGcTmpV — NASA's entire visual archive, free
25. https://t.co/RHUdIMZxV7 — Visual articles told through data
26. https://t.co/ijgPBxU9nQ — The state of the world with real data
27. https://t.co/v2KyXZkVy7 — What we mistakenly think we know about the world
28. https://t.co/lrU9R5vi4k — Visualizing complex data
29. https://t.co/F12XTkFdyx — World Bank's open data
30. https://t.co/FzmzlR49Pw — Turkey's official statistics database
31. https://t.co/q5krwYeWKg — Archive of millions of books, films, and software
32. https://t.co/ZAFtGi7PTc — 70,000 free books whose copyrights have expired
33. https://t.co/f28Cu3uGV7 — Record of every book in the world
34. https://t.co/ogtflMWo7S — U.S. Library of Congress digital archive
35. https://t.co/IglXUCC6pz — Europe's cultural heritage archive
36. https://t.co/0UoxsvmXtw — America's digital library collection
37. https://t.co/IsGlgNRavH — Tour museums from home
38. https://t.co/wmmDOguOJl — Download artworks in high resolution
39. https://t.co/WF1hlql3Bk — Archive of 250,000 artworks
40. https://t.co/FTtnzTGbwT — Forgotten visual treasures of history
41. https://t.co/vqZy1agOw7 — Free archive of culture and education
42. https://t.co/vGySSOQXJA — Met Museum's open collection
43. https://t.co/Ou8jaeEBLI — Family tree of music genres
44. https://t.co/RIxHvtOKU9 — Pick a country and decade to listen to that era
45. https://t.co/0bx2sSji2I — Turn Wikipedia edits into audio
46. https://t.co/8veaRsmfgy — Random knowledge well
47. https://t.co/T1O6SlfvZ7 — Time, sunrises, and sky events
48. https://t.co/AZ4Jgnp71S — Live stream of science news
49. https://t.co/8FwUpofYsv — Free preprints of scientific papers
50. https://t.co/mQNbzpZ634 — Visualize data with live code
Save this. You’ll definitely need some of these later. 🔖
Follow @jara2426for more useful websites, AI tools & tech resources.
Video banjir Aceh ini adalah video paling dibenci dan selalu dihapus komdigi, selain video karhutla Papua, video Prabowo dicuekin warga dan berita korupsi 500M suami mentri komdigi.
bener kata dr. tirta
jangan terus terusan meremehkan rakyat
jika rakyat bisa kompak ga bayar pajak, pemerintah bisa apa? toh ya kalian digaji pake uang rakyat
LogsTotal - a self-hosted log analysis platform.
1⃣ Drop a log file (Windows EVTX or Event XML, Winlogbeat/EVTX JSON, auditd, syslog, a journald export, Sysmon for Linux)
2⃣ Several detection engines run Sigma rules over it and report what each one found https://t.co/w93VcV3yuq
Publik itu pernah "ditipu" Polisi ketika seorang Kapolrestabes beserta jajarannya memberikan keterangan pers, menampilkan berbagai sajam hingga celurit yang panjang berwarna merah.
Kapolrestabes itu bilang bahwa salah satu anggotanya, Robig, hendak melerai tawuran antara Geng Seroja dan Geng Tanggul Pojok.
Robig diklaim diserang sehingga melepaskan tembakan dua kali untuk membela diri.
Jajaran Polisi, bersama Kapolrestabes itu, juga menampilkan rekaman kelompok remaja membawa celurit serta mengamankan senjata tajam sebagai barang bukti.
Saya akhirnya menonton video yang diunggah @TirtoID, sebuah rekaman CCTV yang ditemukan keluarga di depan Alfamart Jalan Penataran, Ngaliyan, Semarang.
Robig berhenti di jalan, mengadang tiga motor yang melintas, lalu menembak. Tidak terlihat tawuran atau pengacungan senjata tajam ke arahnya pada detik-detik penembakan.
Bahkan Robig terlihat sempoyongan dan sempat jatuh. Pengaruh alkohol? Polisi lagi-lagi membantah bahwa anggotanya ini dalam pengaruh alkohol atau obat-obatan.
Memang, sejauh berita yang saya baca, tidak ada tes urin waktu itu. Akan tetapi, ketika Robig mau dipindahkan ke Nusakambangan, ternyata dia positif memakai narkoba.
Nah, siswa SMK yang ditembak Robig itulah yang dituduh Kapolrestabes itu sebagai anggota geng yang sedang tawuran. Namanya Gamma, dan pernah ada keramaian untuk menuntut keadilan untuk Gamma dengan tagline: Gamma Dibunuh Polisi.
Bayangkan jika tidak ada CCTV waktu itu? Bayangkan pula jika @TirtoID (maaf, saya hanya tahu dari @TirtoID, ya) tidak menyebarkannya? Bayangkan jika yang bersuara hanya polisi saja?
Tentu Gamma "dibunuh" dua kali. Pertama, dibunuh oleh Robig yang sempoyongan itu. Kedua, "dibunuh" narasi Polisi.
Peristiwanya masih terbilang baru, persis dua tahun lalu, di bulan yang sama, yaitu November 2024.
Kalian tahu nasib Kapolrestabes itu? Setahun kemudian, pada akhir 2025, ia naik pangkat menjadi Brigjen dan dipindahkan ke posisi Widyaiswara di Sespim.
Jadi, dari Kapolrestabes Semarang yang "menangani" penipuan kasus itu, kariernya justru naik ke jenjang perwira tinggi di lingkungan pendidikan Polri.
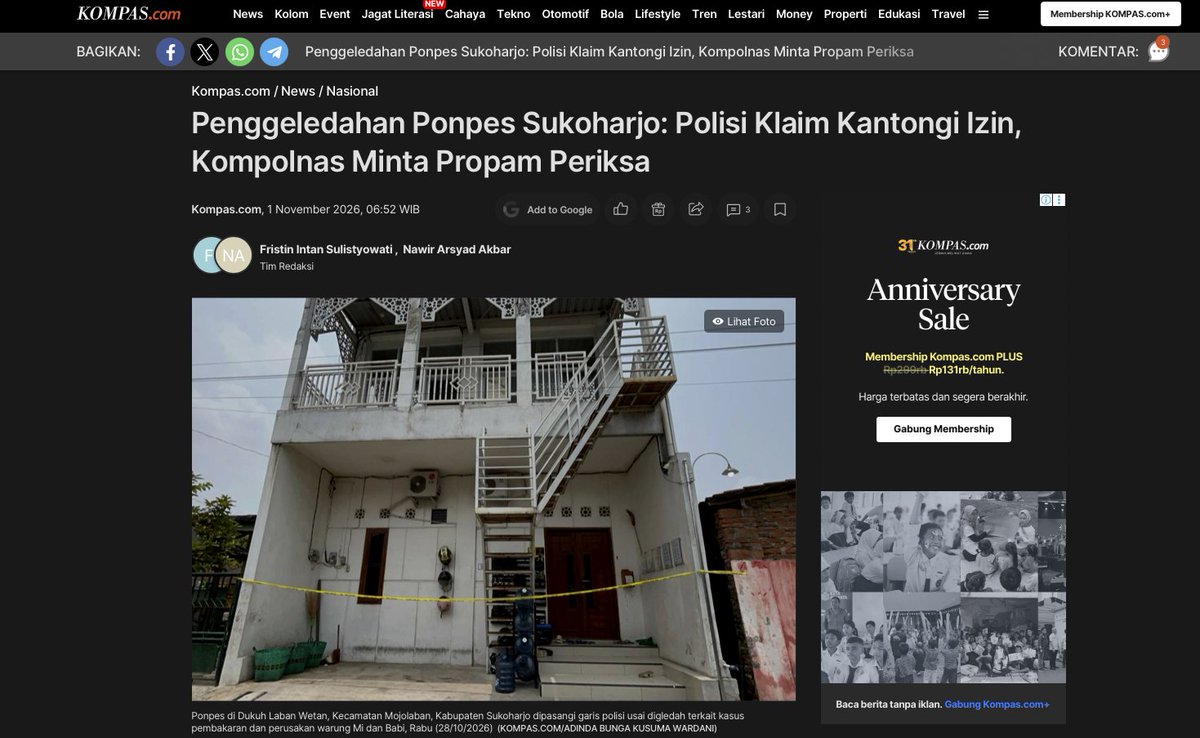
Maka ,wajar pasca pesantren di Sukoharjo digrebek Polisi (tengah malam dengan laras panjang!), banyak orang akhirnya tidak percaya. Kendati Kapoldanya memberikan keterangan pers bersama wakil gubernur yang tidak lain adalah putra kiai.
Saya juga tidak percaya. Lawong dalihnya cuma "tidak terdaftar di Kemenag". Sementara dalih pencarian DPO, yang tahu cuma Polisi.
Kasus Gamma juga yang tahu Polisi. Beruntung saja ada CCTV.
I updated the IR report template to incorporate some of what I've learned from @joswr1ght's amazing and free book, Dynamic Incident Response. https://t.co/4bnOLVYMig
Investigate Windows Intrusions With KAPE and EZ Tools.
Learn to collect, process and interpret Windows forensic evidence using KAPE and Eric Zimmerman's tools.
Examine key artifact families, reconstruct user and attacker activity, correlate evidence across systems and develop defensible timelines and investigation findings.
Full Course: Practical Windows Forensics with KAPE and EZ Tools
https://t.co/26jqYoHGq8