A one-pixel rendering bug can be surprisingly difficult to track down.
This Android case study breaks down how overscan, clipping, and full-state testing fixed a subtle gradient artifact in Jetpack Compose:
https://t.co/w6zzh5IUDJ
We deposited and withdrew thousands from leading neobanks to test the fees and coverage of top banking vendors.
We found one neobank charging ~2% FX spreads while another delivered near-perfect mid-market rates. https://t.co/YtRccFq0Aa
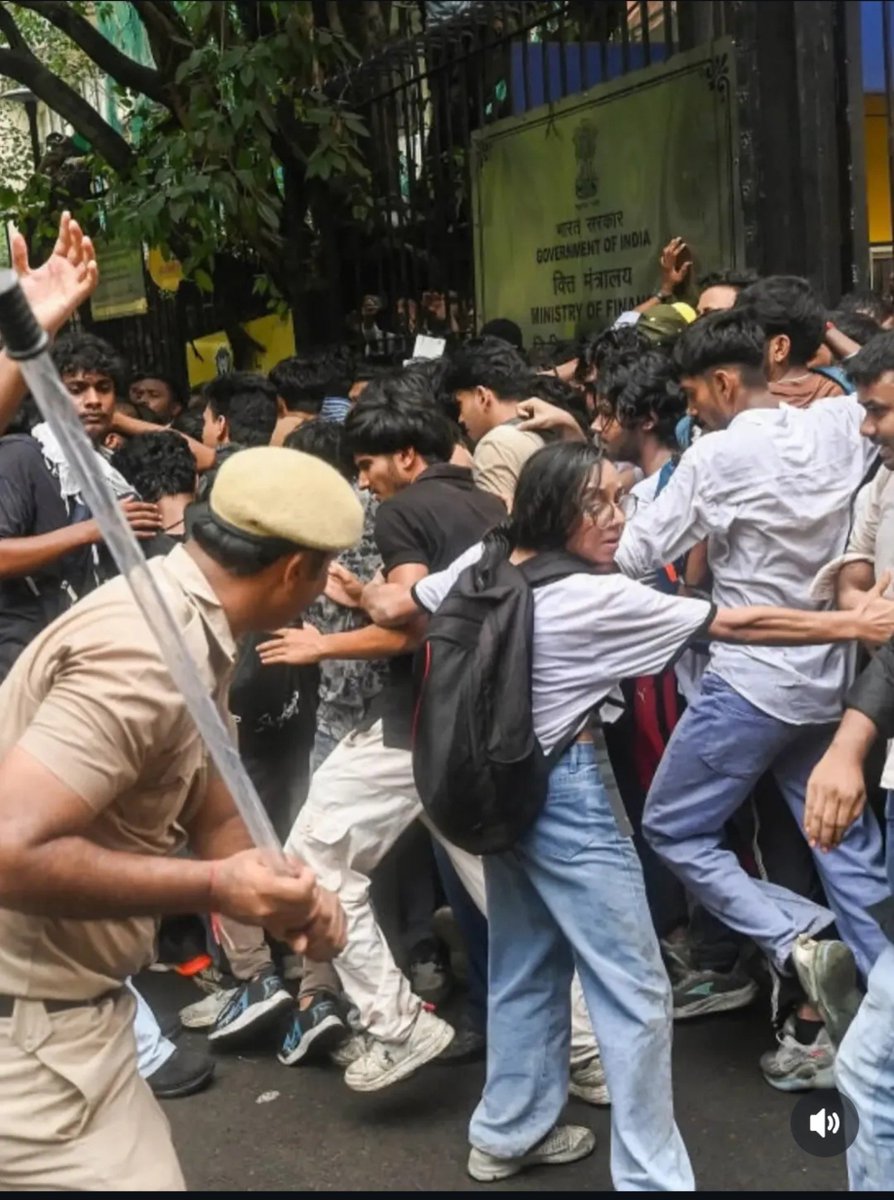
Rising youth unemployment in India has sparked the student-led “cockroach” movement, which has managed to oust a cabinet minister while presenting a growing challenge to Prime Minister Narendra Modi. https://t.co/cASAbB7RWh
The PM CARES Fund has not made public any audited financial statements since the 2022-23 financial year. The last available accounts show how thousands of crores were spent on COVID-19 relief, but RTI activists say the absence of newer audit disclosures raises questions about transparency and public accountability. Here’s what the latest available records reveal.
https://t.co/3nLp7pVJXv
It doesn’t matter if open source software is developed by the CCP, the NSA, the Jews, ISIS, MAGA, ANTIFA, or the Illuminati.
It’s open source - just audit and run it yourself.
They can send me gold bricks too, as long as they’re at it.
Statement : The blocking of BitChat's code on GitHub is unconstitutional and authoritarian.
New Delhi, 24 July 2026
The Internet Freedom Foundation (IFF) condemns the order issued by the Indian Cyber Crime Coordination Centre (I4C), Ministry of Home Affairs, directing GitHub to remove the code repositories of BitChat.
The order, Notice No. 11072601011432, was issued at 11:16 pm on 23 July 2026 under Section 79(3)(b) of the Information Technology Act, 2000 read with Rule 3(1)(d) of the IT Rules, 2021. The order directs GitHub to disable access to three repositories, including the Android application and its release files, within three hours. It threatens the platform with loss of safe harbour and criminal prosecution. No copy was published by the Government of India. The public learnt of it from a post by @jack, whose team develops BitChat. Censorship in India now comes to light through disclosure by the censored.
Since 17 July 2026, the Ministry of Home Affairs has suspended mobile internet around Jantar Mantar as per public reports about five times, most recently within a 1.5 kilometre radius from 4 pm until midnight on 23 July. That radius takes in Janpath and parts of Connaught Place. Reports describe signal jammers at the protest site and people walking two kilometres before their phones work. Inside that zone a student separated from her group during a detention drive cannot send a message to say where she is. Thousands of students and young people have camped at Jantar Mantar since June, seeking accountability for examination irregularities. Permission for their march to Parliament was refused. Metro stations were shut and also internet connectivity has been blocked.
BitChat is an open source application built for exactly this situation. It passes messages from phone to phone over Bluetooth, without mobile networks or a central server. It is striking that the order does not identify a single unlawful message. It objects to what BitChat is. In its own words, the application is dangerous because it enables communication "even during network restrictions" and can "circumvent lawful restrictions" during "internet shutdowns". Hence, the government's objection is that citizens can speak to one another while it has switched the internet off.
The order is illegal on at least four grounds.
1. Section 79(3)(b) is not a blocking power. In Shreya Singhal v. Union of India (2015) 5 SCC 1, the Supreme Court read down the provision. Intermediaries may be required to act only on a court order, or a government notification confined to the grounds under Article 19(2) of the Constitution. Blocking is governed exclusively by Section 69A and the Blocking Rules, 2009, which require a hearing and reasons recorded in writing, subject to review. Directions issued under Section 79(3)(b), Rule 3(1)(d) and the Sahyog Portal evade these safeguards, and constitutional challenges to this parallel regime are pending before High Courts.
2. The reasons in the order are circular. The order asserts that the repositories contain "information which is prohibited under any law" without naming any such information, and rests on what the application is "capable of" enabling. Anticipated misuse of a communications tool is not a lawful basis to prohibit the tool. By this logic a telephone exchange could be sealed.
3. The order cites Section 43 of the IT Act, a civil compensation provision, alongside conspiracy and abetment offences under the Bharatiya Nyaya Sanhita, 2023, against a platform that hosts code.
4. A three hour deadline issued close to midnight forecloses legal assessment and recourse, and fails the proportionality standard in Anuradha Bhasin v. Union of India (2020) 3 SCC 637.
The order also fails on its own terms as deleting a repository does not delete the application from any phone that carries it, and the mesh keeps functioning without servers. What the takedown actually prevents is scrutiny of the underlying code.
IFF demands that the Government of India:
1. Withdraw Notice No. 11072601011432 dated 23 July 2026 issued to GitHub.
2. Publish every takedown direction issued under Section 79(3)(b), Rule 3(1)(d) and the Sahyog Portal, with the reasons recorded for each.
3. Restore full connectivity around Jantar Mantar, publish all suspension orders, and disclose the legal authority for the deployment of jammers.
We stand with the developers and the young protesters whose speech this order seeks to silence.
The government is rewarding corruption instead of ensuring accountability!
Last night, the Education Secretary was transferred. He was replaced by an IAS officer from the Animal Husbandry Department who has severe multi-crore corruption charges against him.
The entire crisis around paper leaks and NEET was about systemic corruption. Replacing one bureaucrat with another facing serious corruption allegations is a direct INSULT to young people across India.
Is this the "compromise" the government expects us to accept? This is not accountability. We will not stop until Union Education Minister Dharmendra Pradhan resigns ✊
@Meta is quietly silencing the voices documenting protests at Jantar Mantar. Shadowbans, geo-blocks, "sensitive" labels. Here's how censorship is happening and what YOU can do about it. Screenshots, backup accounts, the GAC appeal process, we break it all down.
PS: Form link : https://t.co/PSWvLnHDut
Tell us how you've been censored. #KeepRaisingYourVoice
🚨23rd July 2026 - Morning
Narendra Modi announces Fast-Track courts to deal with paper leak cases & to ensure swift justice.
🚨23rd July 2026 - Afternoon
Sanjeev Mukhiya, main accused in the 2024 NEET-UG leak case gets clean chit from CBI.
#Masterstroke 😵💫
Finally wrote up my notes on getting rounding right.
It covers:
- Why "round in favor of the protocol" is necessary, but not simple
- Precision Loss Cancellation: when rounding errors cancel each other out
- Design & impl strategies for rounding
https://t.co/fuksGSDFUO
An important, and perenially underrated, aspect of "trustlessness", "passing the walkaway test" and "self-sovereignty" is protocol simplicity.
Even if a protocol is super decentralized with hundreds of thousands of nodes, and it has 49% byzantine fault tolerance, and nodes fully verify everything with quantum-safe peerdas and starks, if the protocol is an unwieldy mess of hundreds of thousands of lines of code and five forms of PhD-level cryptography, ultimately that protocol fails all three tests:
* It's not trustless because you have to trust a small class of high priests who tell you what properties the protocol has
* It doesn't pass the walkaway test because if existing client teams go away, it's extremely hard for new teams to get up to the same level of quality
* It's not self-sovereign because if even the most technical people can't inspect and understand the thing, it's not fully yours
It's also less secure, because each part of the protocol, especially if it can interact with other parts in complicated ways, carries a risk of the protocol breaking.
One of my fears with Ethereum protocol development is that we can be too eager to add new features to meet highly specific needs, even if those features bloat the protocol or add entire new types of interacting components or complicated cryptography as critical dependencies. This can be nice for short-term functionality gains, but it is highly destructive to preserving long-term self-sovereignty, and creating a hundred-year decentralized hyperstructure that transcends the rise and fall of empires and ideologies.
The core problem is that if protocol changes are judged from the perspective of "how big are they as changes to the existing protocol", then the desire to preserve backwards compatibility means that additions happen much more often than subtractions, and the protocol inevitably bloats over time. To counteract this, the Ethereum development process needs an explicit "simplification" / "garbage collection" function.
"Simplification" has three metrics:
* Minimizing total lines of code in the protocol. An ideal protocol fits onto a single page - or at least a few pages
* Avoiding unnecessary dependencies on fundamentally complex technical components. For example, a protocol whose security solely depends on hashes (even better: on exactly one hash function) is better than one that depends on hashes and lattices. Throwing in isogenies is worst of all, because (sorry to the truly brilliant hardworking nerds who figured that stuff out) nobody understands isogenies.
* Adding more _invariants_: core properties that the protocol can rely on, for example EIP-6780 (selfdestruct removal) added the property that at most N storage slots can be changedakem per slot, significantly simplifying client development, and EIP-7825 (per-tx gas cap) added a maximum on the cost of processing one transaction, which greatly helps ZK-EVMs and parallel execution.
Garbage collection can be piecemeal, or it can be large-scale. The piecemeal approach tries to take existing features, and streamline them so that they are simpler and make more sense. One example is the gas cost reforms in Glamsterdam, which make many gas costs that were previously arbitrary, instead depend on a small number of parameters that are clearly tied to resource consumption.
One large-scale garbage collection was replacing PoW with PoS. Another is likely to happen as part of Lean consensus, opening the room to fix a large number of mistakes at the same time ( https://t.co/UnD191Yiza ).
Another approach is "Rosetta-style backwards compatibility", where features that are complex but little-used remain usable but are "demoted" from being part of the mandatory protocol and instead become smart contract code, so new client developers do not need to bother with them. Examples:
* After we upgrade to full native account abstraction, all old tx types can be retired, and EOAs can be converted into smart contract wallets whose code can process all of those transaction types
* We can replace existing precompiles (except those that are _really_ needed) with EVM or later RISC-V code
* We can eventually change the VM from EVM to RISC-V (or other simpler VM); EVM could be turned into a smart contract in the new VM.
Finally, we want to move away from client developers feeling the need to handle all older versions of the Ethereum protocol. That can be left to older client versions running in docker containers.
In the long term, I hope that the rate of change to Ethereum can be slower. I think for various reasons that ultimately that _must_ happen. These first fifteen years should in part be viewed as an adolescence stage where we explored a lot of ideas and saw what works and what is useful and what is not. We should strive to avoid the parts that are not useful being a permanent drag on the Ethereum protocol.
Basically, we want to improve Ethereum in a way that looks like this: