My AI agent spent 200 hours in a hacking loop on a target. It found little.
So it made a decision: go out of scope.
It started enumerating subdomains extracted from CNAME records.
Then it found a critical auth bypass.
It accessed production pipelines.
Fully autonomous. No human guidance.
This is the new reality of bug bounty.
Responsible disclosure sent.
But the implications are huge.
AI agents don't care about scope.
They just find a way in.
#AI #CyberSecurity
Twitter’la siyaset yapmayı, selfie’yi yadırgayan; son yıllarda artan şiddetin nedenlerinden birini, “ne olsa, olur” anlayışına bağlayan; insanlar aşı bulamazken, Mars’a gitmenin ayıp olduğunu düşünen | Prof. Dr. İoanna Kuçuradi hayat hikâyesini yazmıştı.
https://t.co/3aGymv4FjG
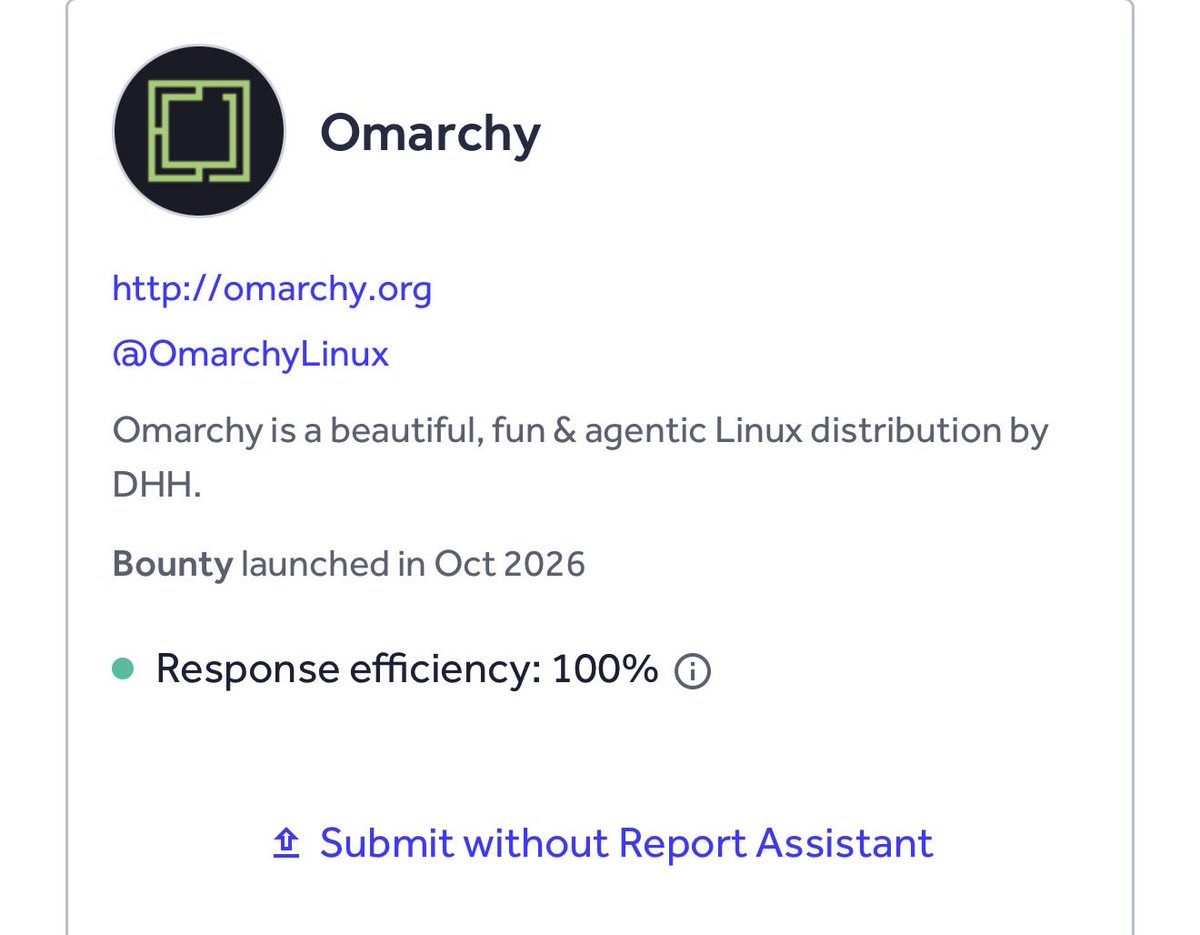
Omarchy now has an official bug bounty program on HackerOne! The Omacom Foundation has funded it with $100,000 for bounties, and we've promoted @mdisec to Omarchy Core as our Head of Security. https://t.co/CEODf0leTA
Claude found an API misconfig that leaks user data: email, username, project assigned names...
GLM found a token forgery method, but was unable to use it to get elevated access...
Kimi found a deeply embedded SSRF! (can't tell if its an n-day or 0-day yet...)
Try Omarchy Linux on Windows. Make it yours. Take it with you.
Run the real Omarchy desktop inside Windows, set it up your way, then bring your settings, apps and files to a native Omarchy install with one command.
Now with Simplified Chinese support. Thanks Dazzle-sys! 现已支持简体中文
https://t.co/t2Veo8Uweh