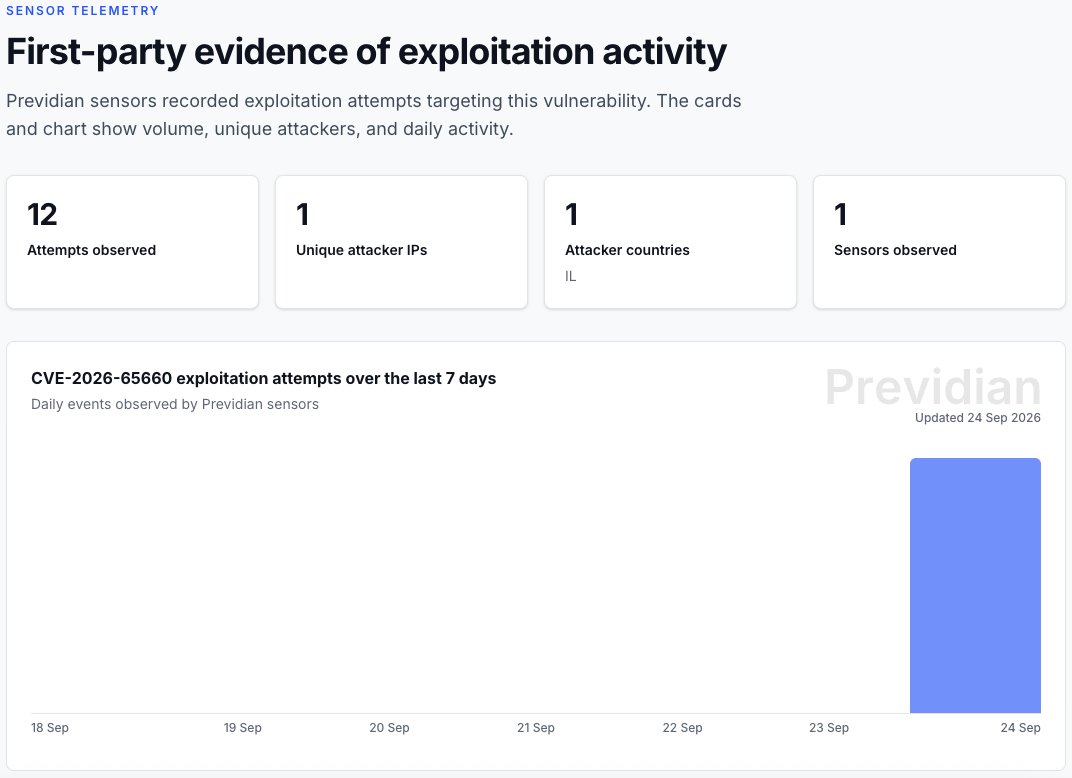
Previdian observed SharePoint exploit attempts chaining CVE-2026-65660 (authenticated) with a separate anonymous delivery bug documented by @vcslab.
Attempts were carrying an encrypted .NET loader. Anonymous viewing required.
We’re seeing this PHP webshell used in Issabel exploitation attempts (CVE-2026-89026) by a Threat Actor.
A hard-coded JWT key lets attackers forge tokens and execute commands without logging in.
Patch exposed systems and check for manage_hysumzem.php post-compromise webshells.
CISA KEV is a great baseline, but it isn't the full picture.
Yesterday, it added 4 vulnerabilities.
Previdian customers had between 5 hours and a week of early warning before those additions.
More time to assess exposure, mitigate or patch.
Seems highly likely this was the vuln used to hack the FBI.
CVE-2026-35273 - Missing Authentication for Critical Function
It came out June 11th and was immediately added to the CISA Known Exploited list - which means it was seen in real world attacks all the way back then.
New unauthenticated no user interaction RCE in WordPress. Some pre-conditions. Not click2shell.
CVE-2026-87902
Ensure auto-updates enabled. Update to 7.1.2.
People are telling me that a new Wordpress cve is hitting the news, and what I’m doing? A repro for you!
CVE-2026-87902: WordPress Core unauthenticated path traversal in get page template page-template resolution leading to conditional RCE
https://t.co/y7V1bOzfq0
WordPress 7.1.2 is now available. This security release fixes a critical vulnerability. Update your sites immediately from Dashboard > Updates, and read the release details: https://t.co/QDOBK470yS
Yesterday we saw first exploitation attempt for OpenCTI (CVE-2026-27960) in our honeypot network using the public Nuclei template.
Attacker IP located in Yemen (109.200.170[.]0)
Link in comments 👇