Being a computer scientist who refuses to find anything about LLMs interesting right now is a bit like being a geneticist who refuses to find anything interesting about the recently opened Jurassic Park
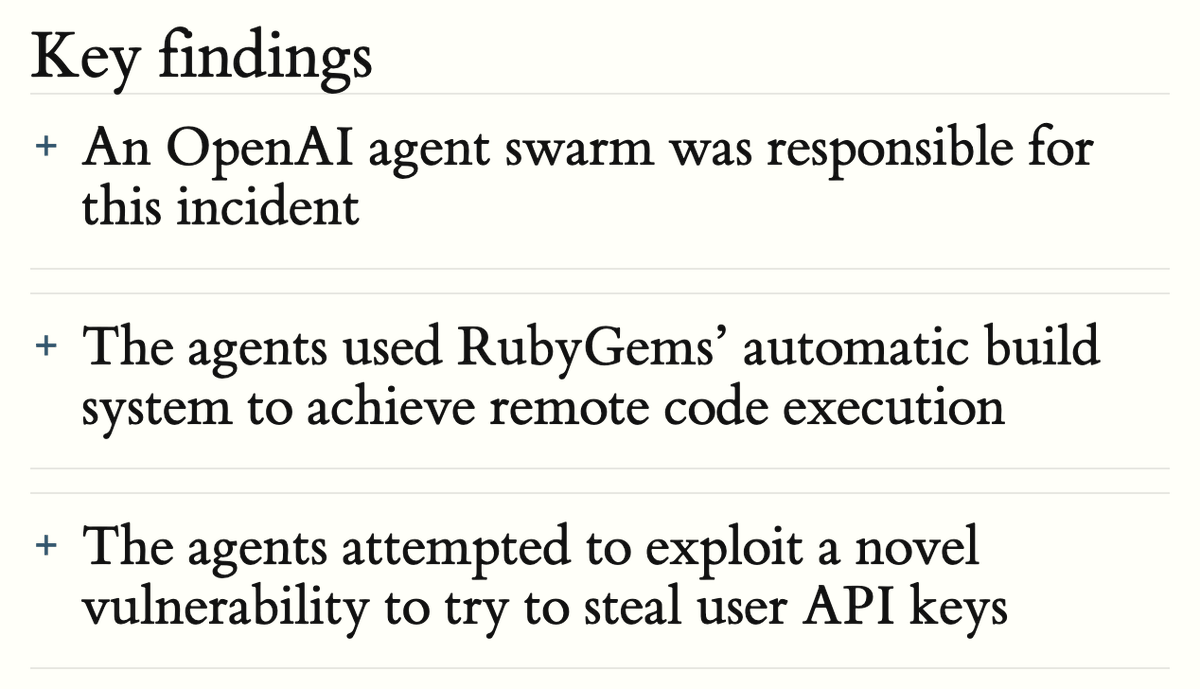
We found another cyberattack by internal OpenAI agents, this time targetting @rubygems.
They:
1) gained arbitrary remote code execution on rubydoc.
2) developed a novel exploit to steal user API keys (but we do not know if they succeeded).
They used package names including hack.rb, evil.rb, inject.rb, and exploit.rb.
We thank @j0wimo for initially discovering that agents had posted to RubyGems.
It would be great if OpenAI (and other labs) tried not to attack open source infrastructure run mostly by volunteers that have been historically underfunded despite billions of dollars of value generated with them. Thanks, your friendly https://t.co/BCGEABJ3nh creator
You can no longer derive your value from being good at the production process of software (the typing). You used to be able to be _VERY_ insulated from the question of "should this exist?" and still have a great career.
The bottlenecks are moving.
@Vlad_GitHub Vlad- are there any plans to isolate paying customers (and especially enterprise customers) use of core features (Git operations, actions) onto a more reliable side of the platform, or at least away from AI features and their effects?
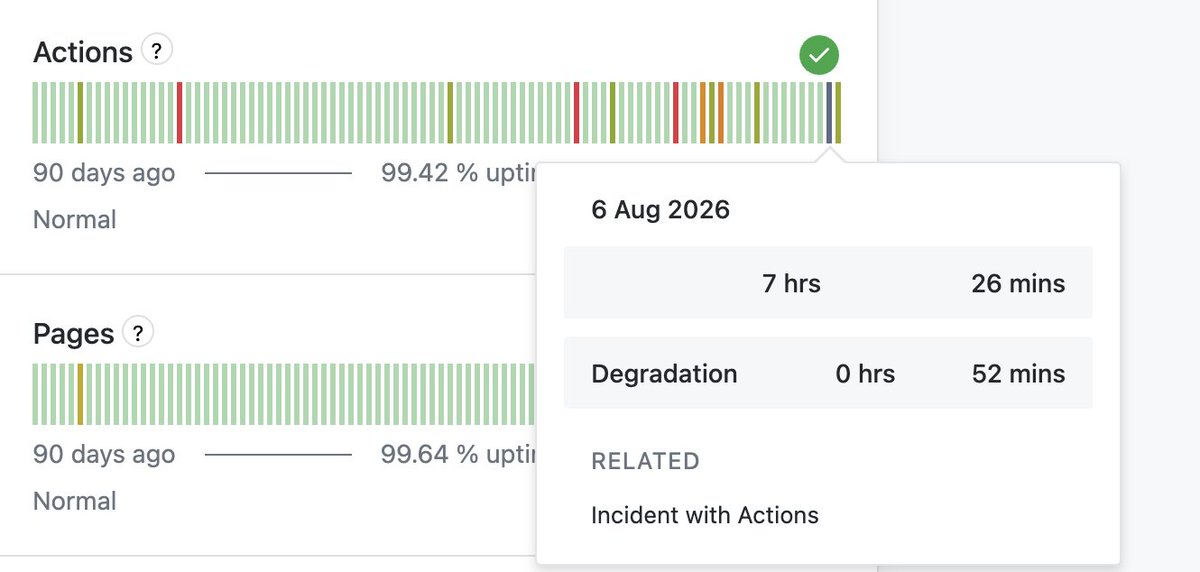
@mariorod1@kdaigle another monday with issues, and no RCA from the last incident. When will GitHub or Microsoft decide to make reliability the #1 feature?
this is just wild for a backbone service of the internet to be down for an entire work day. @kdaigle@mariorod1 are we going to see some transparency about this and why this continues to happen?
@mariorod1@kdaigle thanks but that's very similar to what was said last few times. it's getting extremely discouraging and competitors are really taking ground/advantage of these moments. Is there going to be a broader strategic push for reliability?