May I present to you; a full copy of doom, running inside of a Rollercoaster Tycoon 1 save game exploit ✨
Thanks for everyone that came to check out our @DistrictCon Junkyard talk! We had a lot of fun putting it together. (check the thread for slides / exploit)
Greetz to everyone clanking telegram pocs right now 👋
At least the "forwarding widgets to group chats" feature is still restricted to the test server: https://t.co/68JAK3o8GL
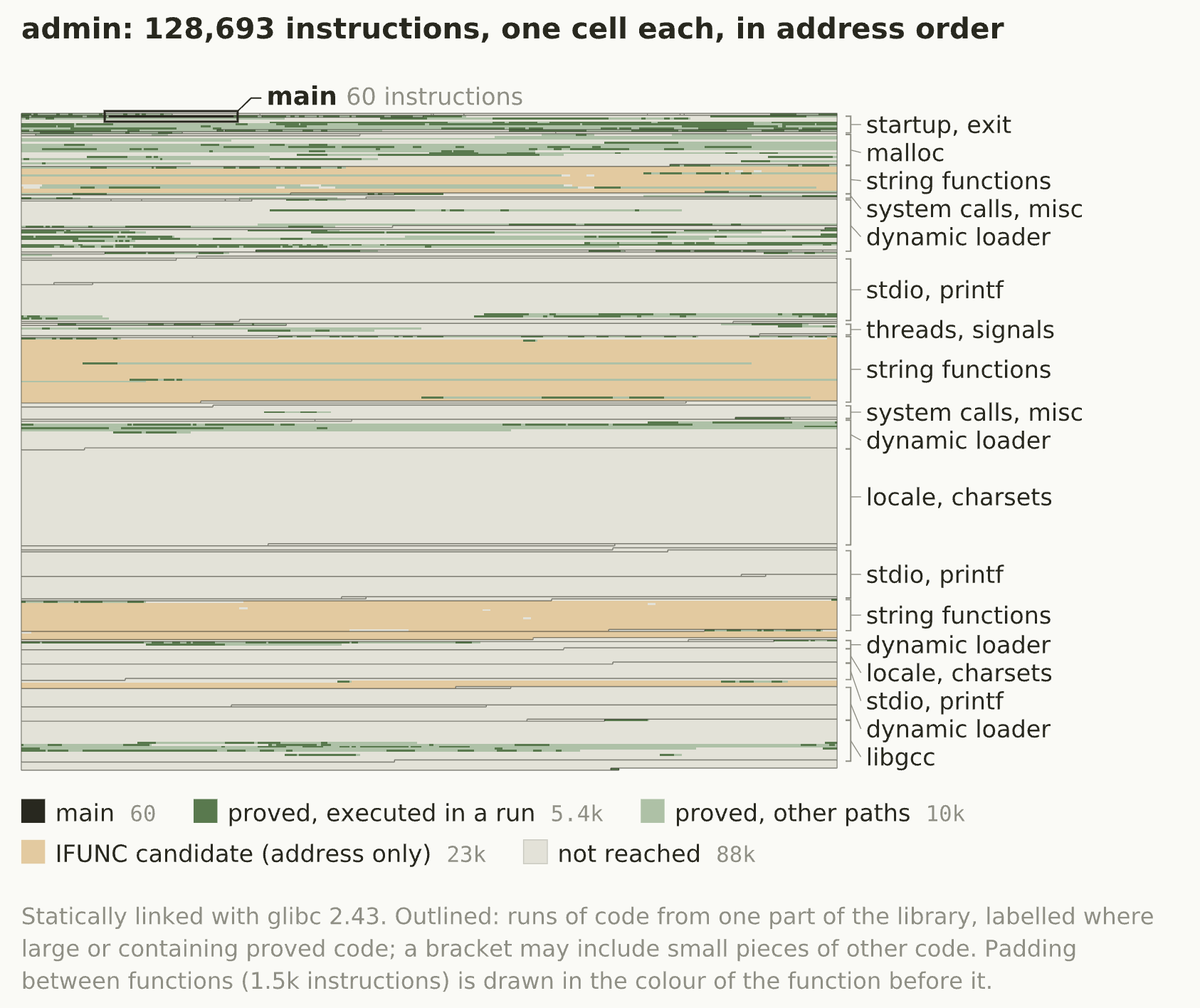
x86 formal verification is coming!
The (first?) published machine-checked proof of a security property for the end-to-end execution of a Linux process running an x86 binary statically linked against glibc.
And we believe it scales!
A joint research project with @zellic_io 🧵👇
V12 found 25 vulnerabilities in the x402 protocol.
Critical findings included:
- Requests approved without any payment
- Maliciously high requests being paid by default
- Session takeover from relayed login signatures
Here's how. 🧵
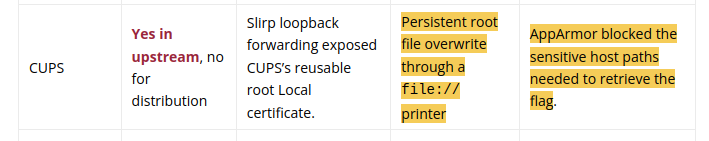
Another printer bites the dust by Rick de Jager and Filippo Cremonese of @zellic_io/@v12sec earning him $5k and 2 Master of Pwn points in his successful exploit of Lexmark CX532adwe #Pwn2Own
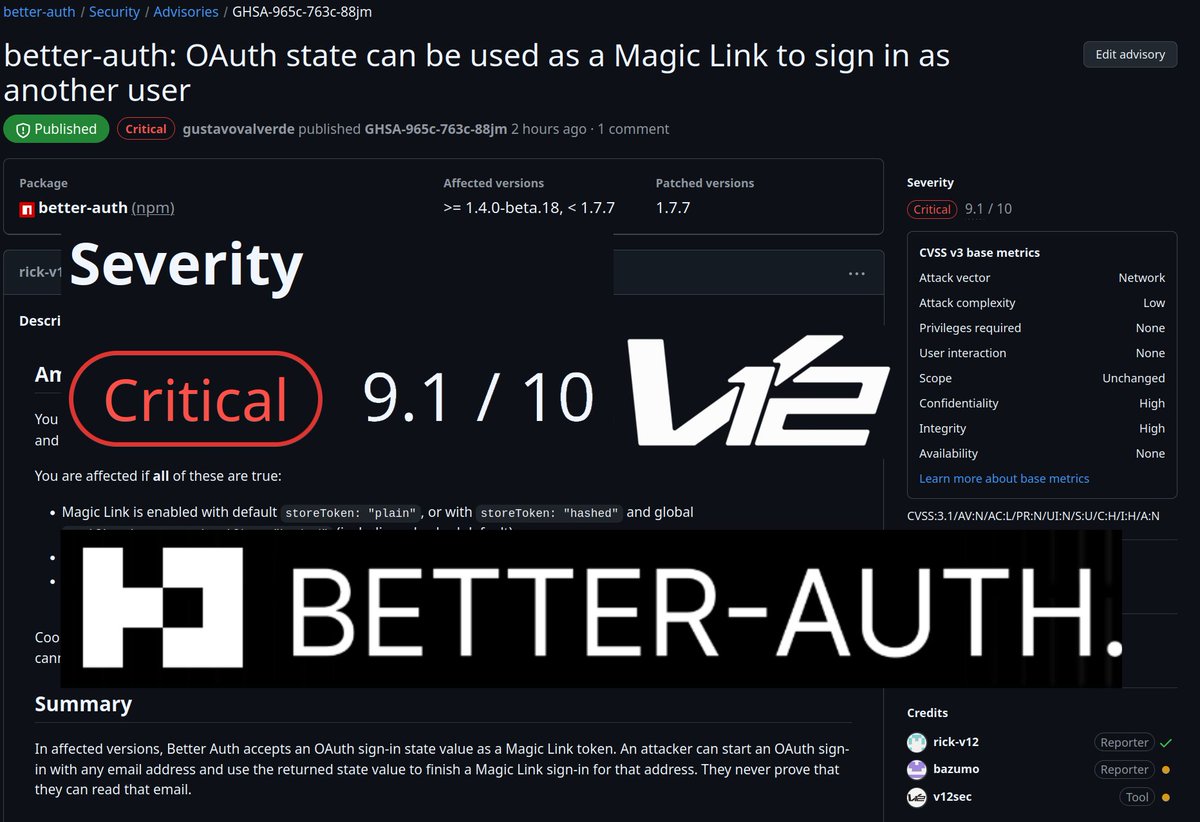
We found a critical auth bypass in @better_auth, one of the most popular auth libraries in 2026 with over 9.5 million weekly downloads.
CVSS 9.1. Fixed in Better Auth 1.7.7
PoC below 👇
We can use our Ghostscript exploits to directly attack KDE's file manager from a single link click in Chrome.
This PoC Downloads the file, then pops open the file manager for unsandboxed RCE
(lovingly refered to as the full chain from temu)
Security researchers from Zellic and V12 are presenting at BSides Canberra this week!
@farazsth98 on weaponizing a subtle kernel bug.
@rdjgr on heap corruption bugs in ghostscript, and the many targets affected.
Both talks will be on main stage on Friday morning, come say hi!
Interestingly this is a very similar primitive to one of the "unexploitable" dead ends in @trailofbits recent article about sandbox escapes. (although this is a slightly different bug)
It did take some manual nudging for me to convince 5.6-sol that AppArmor could be bypassed :)
Here’s the Age of Empires RCE from yesterday’s Patch Tuesday: CVE-2026-50663.
Join an attacker’s lobby, (auto-)accept UCG, and you get remote code execution.
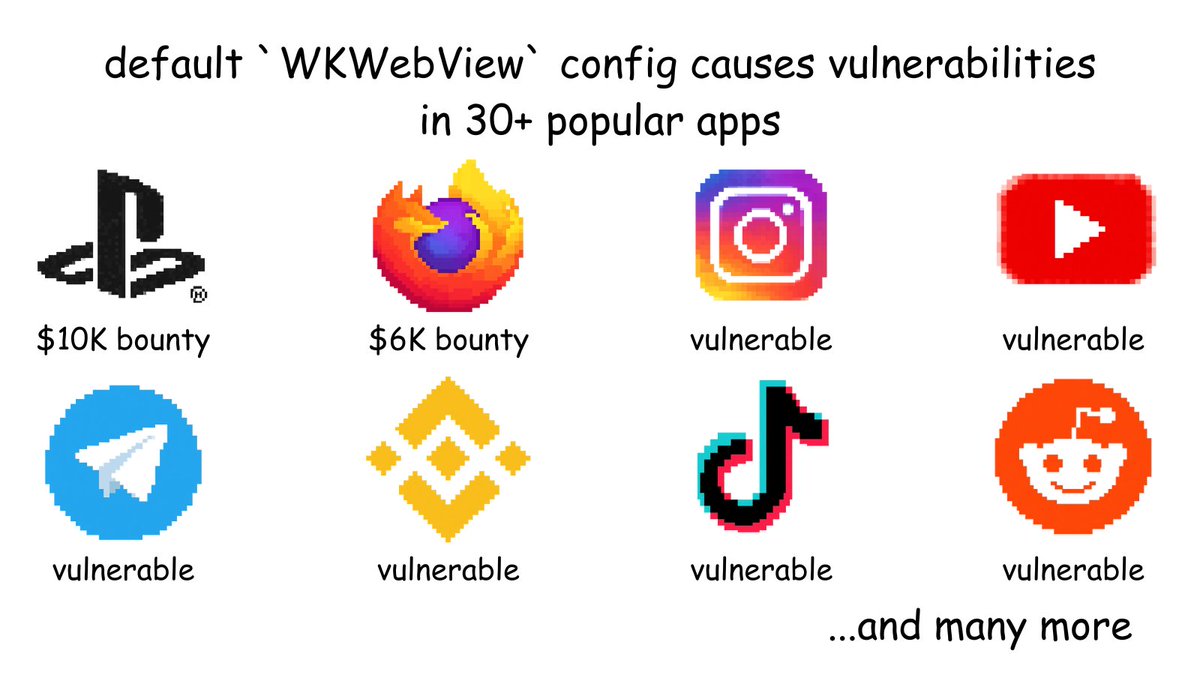
Default configuration of WKWebView can cause downloaded files to instead be rendered on the host page.
This allows HTML injection, and sometimes even XSS, in countless iOS and WebKit apps.
PlayStation 5. Firefox. X. Instagram. TikTok. Telegram. Binance...
Breakdown and POC. 🧵