V Česku roste nový a dost zajímavý investor do evropských claudů a kyberbezpečnosti. Je mu teprve 26 let, ale už teď se pohybuje v poměrně vysokých českých kruzích na pomezí podnikatelů v IT, AI a politiky. Jmenuje se Ilja Meškov.
Meškov odjel z Ruska ve svých 18 letech a studoval VŠE. Za studia si dal ještě prestižní a drahou školu v Texasu. Poté během dvou let pak raketově vyrostl v české firmě, která připravuje miliardové investice do datových center pro provoz umělé inteligence po celé Evropě. Teď je v ní partnerem odpovědným za rizikový kapitál. Po šesti letech v Česku také získal občanství.
Byl to příběh obrovského úspěchu mladého člověka, který odjel z Ruska a teď roste raketovou rychlostí. Jediná šmouha na tom celém je, že otec Ilji je ruský vojenský plukovník, který vede katedru na ruské Baumance - elitní univerzitě, které se občas přezdívá škola špiónů.
V armádě s přístupem k tajným informacím a následně na stejné škole pracovala donedávna i Iljova matka. Ta už sice nepracuje a je v důchodu, ale místo toho má od letoška české vízum a jezdí za Iljou jako manželka aktivního ruského plukovníka a kariérní vojačka do Prahy. Mimochodem, české vízum je pro běžné Rusy po roce 2022 prakticky nereálné získat.
Celý tenhle příběh od @veinbender vyvolává obrovské množství otázek. Mimo jiné o tom, jak je možné, že i v pátém roce války sice nedostane víza z Ruska prakticky nikdo kromě vojačky a ženy plukovníka? Ale taky jak moc bychom měli dohlížet na to, kdo vidí v téhle době do klíčové datové infrastruktury zemí v EU?
Případně jak moc máme řešit soukromí úspěšných mladých Rusů v Evropě, když pochází z armádních rodin, které jsou blízké tajným službám? A když se od jejich činnosti nikdy reálně nedistancovali.
Když si článek přečtete, budu rád za vaše názory a myšlenky, které u něj budete mít. Je v dalším postu👇
Did you know macOS binaries can run on iOS? It needs rewriting architecture information and adjusting library paths. I automated this, including DYLD shared cache library extraction and replacement, allowing many macOS command line tools to run on iOS.
https://t.co/QFz1n7guOo
Liebe Berliner:innen, bitte beendet diese Farce. Ihr könnt dieses Haus sicherlich sinnvoller nutzen, und ganz Deutschland will, dass es endlich geschlossen wird.
Die Entscheidung liegt in den Händen eurer Verwaltung. Fragt nach, sprecht darüber und macht Druck.
Jeder Schritt, der den Abzug der Russen näherbringt, ist ein weiterer Schritt in Richtung Frieden.
Herzlichen Dank!
#SlavaUkraini
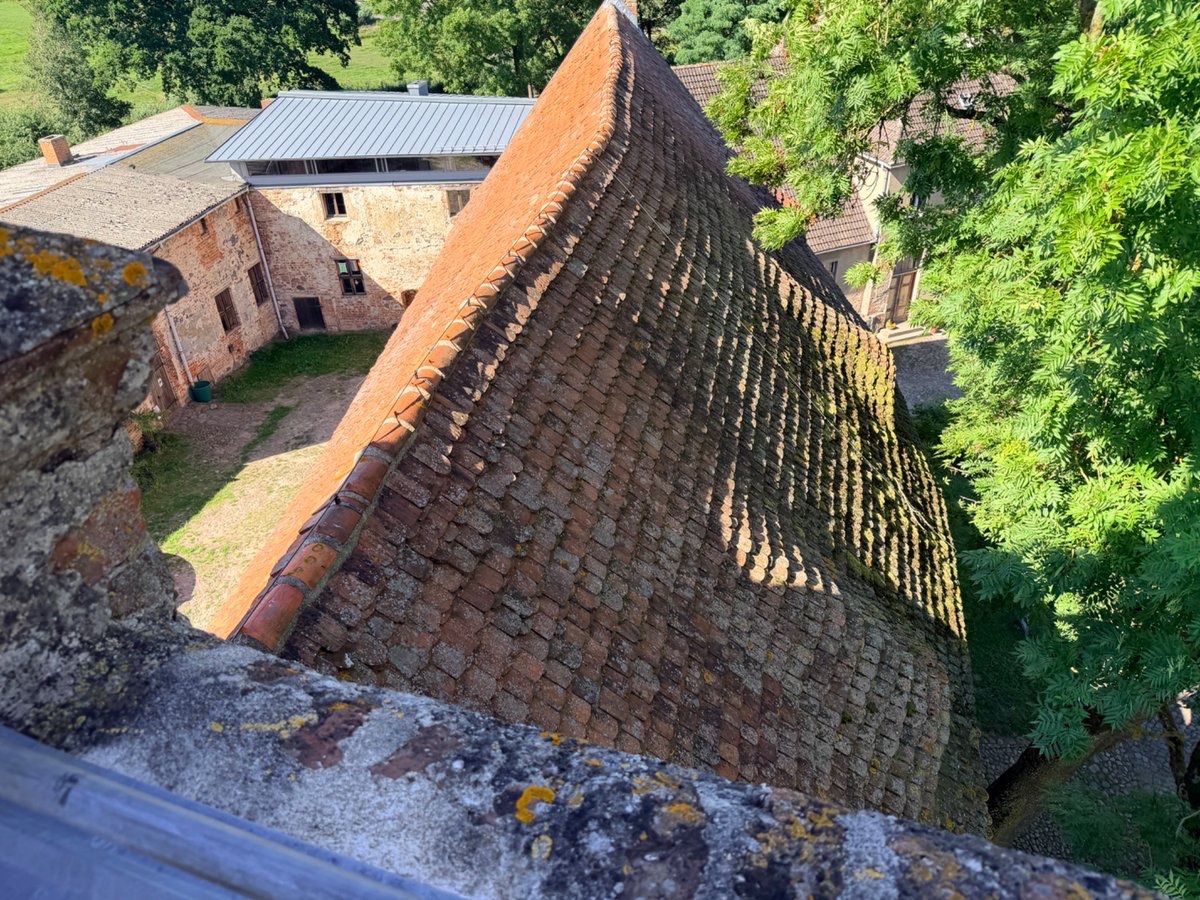
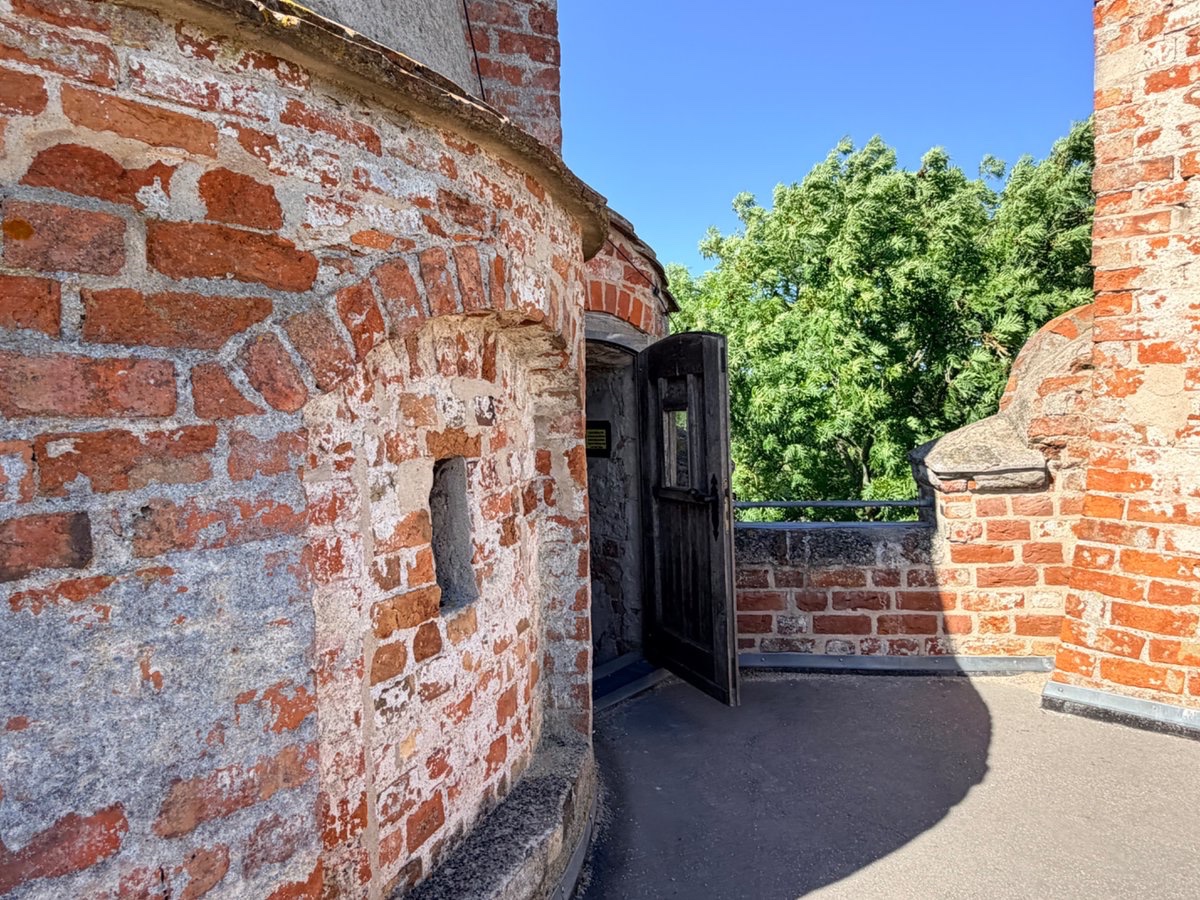
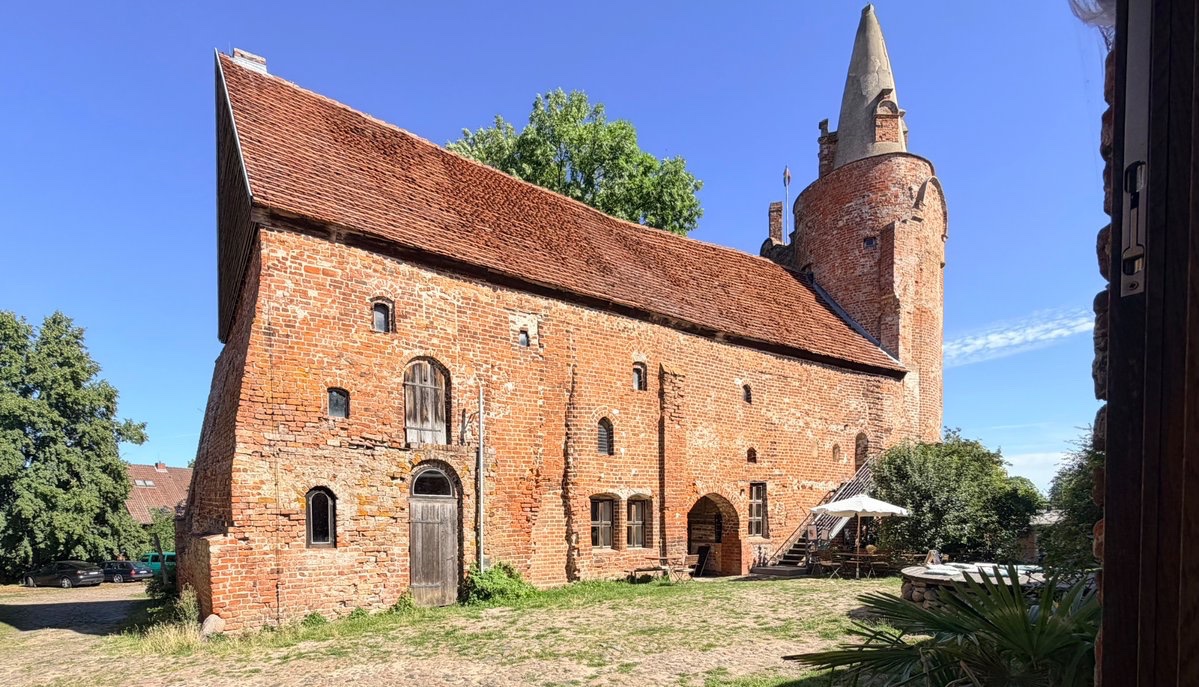
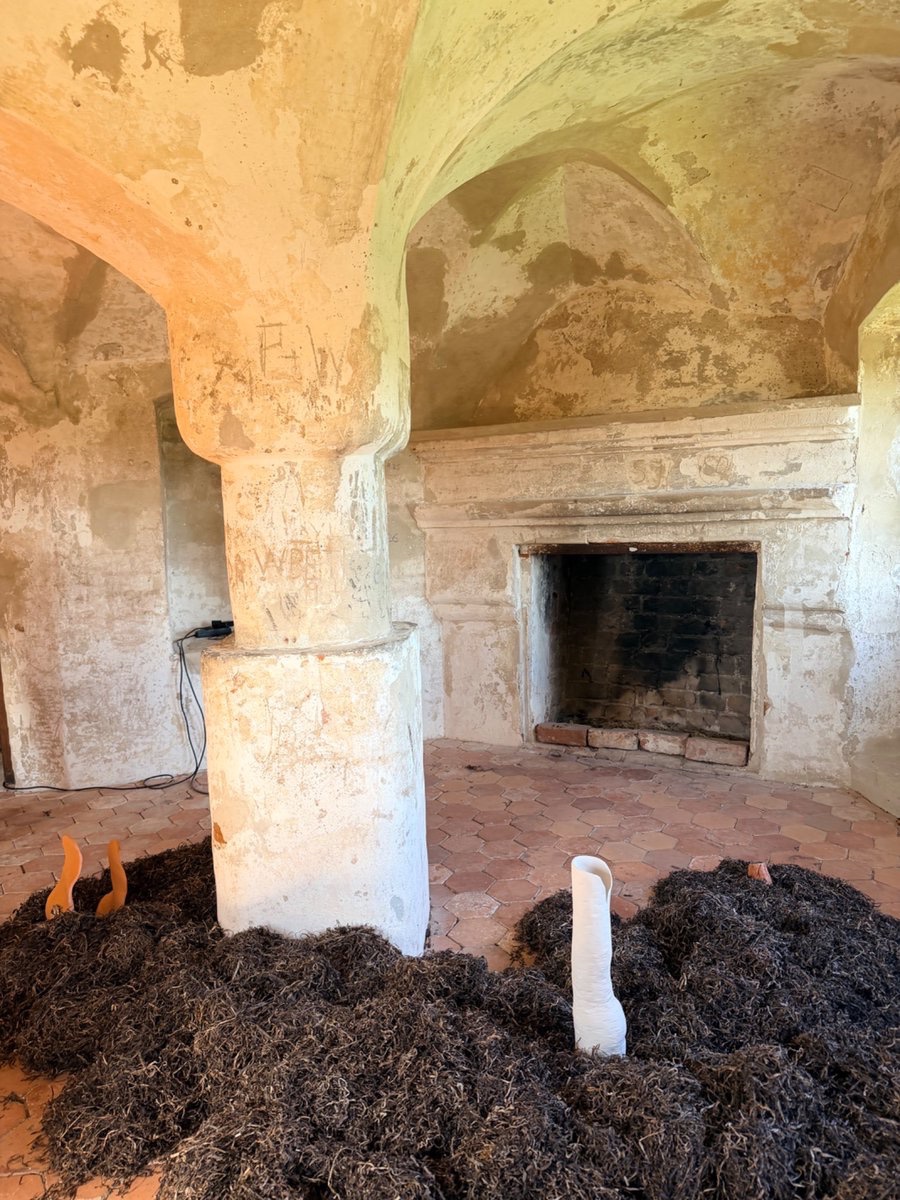
Jedesmal, wenn wir auf der Ostseeautobahn nach Usedom oder Rügen fahren, fiel mir ein eigenartiger Turm in einem kleinen Dorf auf. Heute hielten wir mal an und waren richtig überrascht. Das ist keine Kirche, sondern die einzige mittelalterliche Niederungsburg in Meck-Pomm. Errichtet bereits im 13. Jahrhundert, im Tollensetal im Ort Klempenow gelegen. Nach der Wende von Künstlern wiederhergerichtet. Es finden Ausstellungen statt, ein Café bietet neben Kaffee und Kuchen auch Mittagessen an.
Die Burg kann für kleines Geld besichtigt werden. Imposant auch der markante Turm. Der Raum mit dem rustikalen Gewölbe befindet sich im Turm.
Um die Burg schöne kleine historische Gebäude, in denen ein Verkauf stattfindet. Hinter der Burg kann man Kanus ausleihen und auf kleinen Fluss Tollense entlangpaddeln.
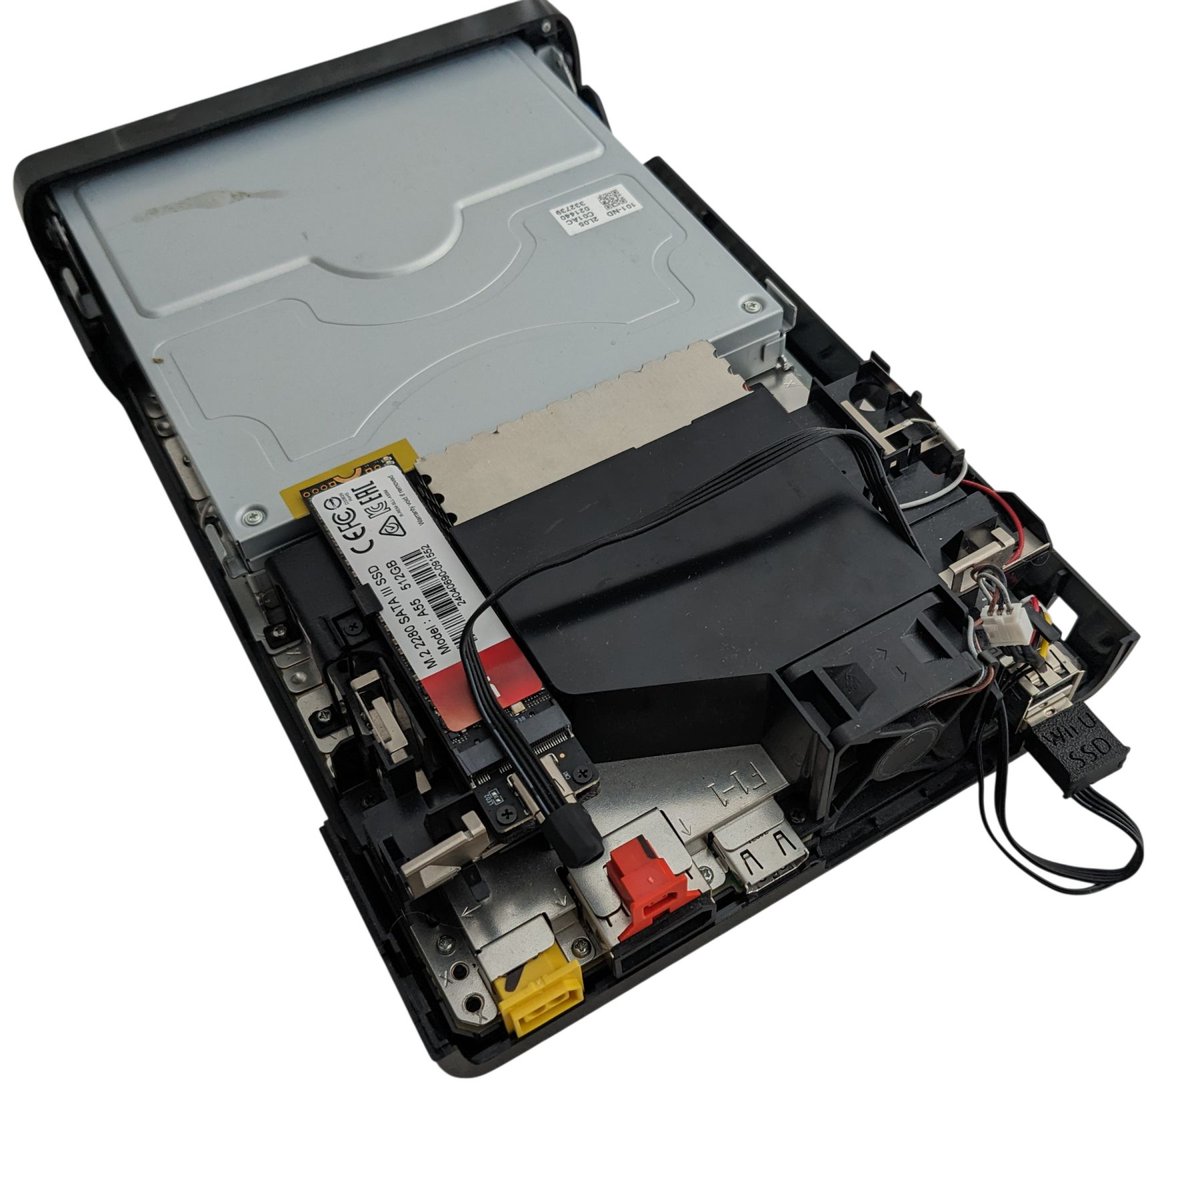
The m.22WiiU now supports NVMe drives as well as SATA.
https://t.co/MNboMXIjnH
For clarity, there is no improvement in speed or any other aspect going from SATA to NVMe on the Wii U. Its just going to be easier to find m.2 NVMe drives in the future, so we wanted to expand the compatibility.
For those who have already purchased a kit, we will be offering the updated parts for the cost of shipping. The updates include a new grill and wire harness. You will also need to update the firmware on the interposer board.
Once again, thanks to @nintygametube for his help on this.
I've started a new company: @superlogical! We're going to begin by building a terminal multiplexer. The entire vision is much larger, but the multiplexer is the foundation. Sign up for the newsletter to get beta access and devlogs (product updates only I promise).
https://t.co/XJuqufkmCd
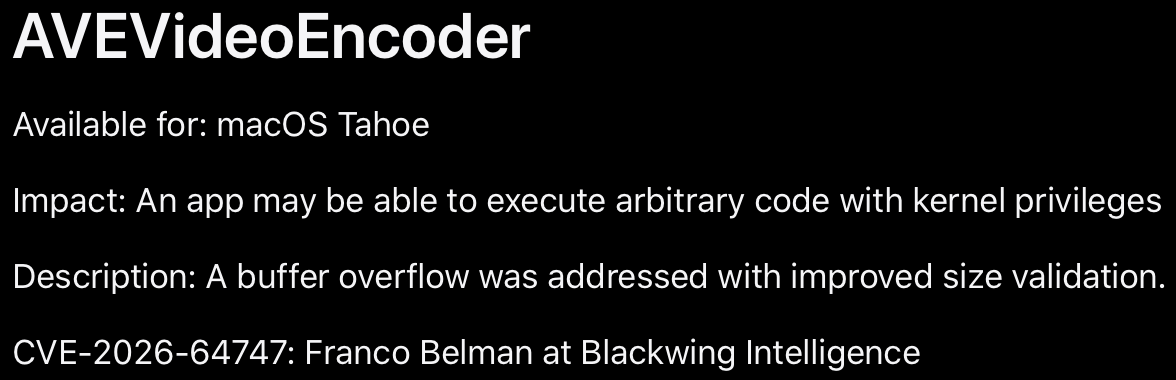
Apple credited me today for CVE-2026-64747, a vulnerability in AVEVideoEncoder affecting macOS/iOS. It earned a $60K accelerated bounty after I captured an Apple Target Flag.
Write-up coming soon.
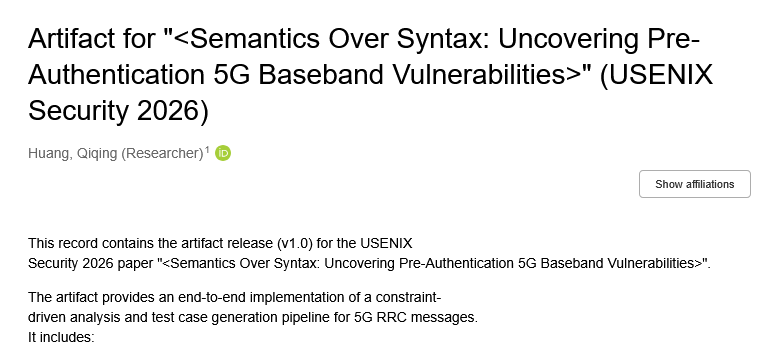
Ai found 7 new 5G baseband vulns without sending a single malformed message.
3 new high-severity CVEs in 5G basebands.
Even a syntactically perfect 5G RRC message can crash your baseband.
New research shows that semantic violations breaking hidden field constraints and cross-IE dependencies in pre-authentication messages are enough to destabilize modems.
They built CONSET, a framework that:
- Extracts real constraints from 3GPP specs (with LLM assistance)
- Generates valid-looking but semantically broken test cases
- Found 7 previously unknown vulnerabilities on commercial devices
Including 3 high-severity CVEs affecting 64 chipset models and 500+ smartphones.
This proves syntax was never the only attack surface in 5G.
Als Vorsitzender der CDU Deutschlands werde ich in Abstimmung mit dem Vorsitzenden der CSU einen Vorschlag für die Neubesetzung im Fraktionsvorsitz machen. Verfahren und Zeitplan werden jetzt mit den Gremien der Partei und der Fraktion abgestimmt.
We recently achieved 1.3 micron features on our DIY photolithography setup @hackerfabindia
We are pushing the limits of what's possible in a college dorm, on a budget!
found a verifier/interpreter mismatch in the Linux BPF subsystem (CVE-2026-31525, CVSS 7.8). arbitrary kernel read/write; become root, escape containers, disable SELinux, read TLS keys out of other processes' memory.
anyway, it starts with the math bars, the absolute value.
computers store negative numbers in two's complement. the smallest 32-bit signed integer is -2,147,483,648, and the largest positive is +2,147,483,647. there is no +2,147,483,648, since it simply does not fit. so when you call abs(-2,147,483,648), the C specification thinks about it for a moment, says "undefined," and leaves the room. on x86 and arm64, what you actually get back is -2,147,483,648. you asked for the absolute value of a negative number, you got back the same negative number. thank you computer :D
the BPF interpreter implements signed 32-bit division (BPF_ALU | BPF_DIV/MOD, off == 1, added in ec0e2da95f72) by decomposing it into unsigned division: take abs() of both operands, divide via do_div(), reapply the sign. the handler in ___bpf_prog_run (kernel/bpf/core.c):
AX = abs((s32)DST);
AX = do_div(AX, abs((s32)SRC));
and look, the kernel even documents this. include/linux/math.h: "the return value is undefined when the input is the minimum value of the type." when DST = 0x80000000 (S32_MIN), abs() tries to negate it. -(-2,147,483,648) overflows s32, the C spec calls it undefined behavior, and the CPU hands back 0x80000000 unchanged. still negative. abs() had one job.
this s32 then gets assigned into AX, a u64 BPF register. s32 → u64 sign-extends: 0x80000000 becomes 0xFFFFFFFF80000000. that's 18,446,744,071,562,067,968. you wanted 2,147,483,648, you got 18.4 quintillion; a rounding error of about 18.4 quintillion. do_div() is a 64-by-32-bit unsigned division macro and it operates on this full u64 numerator. the quotient is off by a factor of 2³². the smod path has the same problem since do_div() modifies the dividend in place and returns the remainder, both wrong. 8 call sites across sdiv32/smod32 src/imm handlers, all quietly producing nonsense whenever S32_MIN shows up.
the BPF verifier is the safety system that statically analyzes every BPF program before allowing it to run. it exists specifically to guarantee that nothing bad can happen. scalar32_min_max_sdiv() in kernel/bpf/verifier.c tracks value ranges through abstract interpretation. it handles signed division correctly, including S32_MIN. computes tight, mathematically correct bounds. the interpreter, as we've established, computes whatever it feels like. so the verifier thinks register R0 is in range X. the interpreter puts value Y in R0. the safety system and the execution engine disagree about what a program does. in BPF security research, this is where you set down your coffee.
concretely: load S32_MIN into R1, load 2 into R2, execute SDIV32 R1 R2. verifier determines R1 ∈ [-1,073,741,824, -1,073,741,824]. interpreter computes do_div(0xFFFFFFFF80000000, 2) = 0x7FFFFFFFC0000000, reapplies the sign, produces a completely unrelated value. use R1 as an index into a BPF map. verifier approves the access, bounds check passes against its calculated range. interpreter uses the actual value. out-of-bounds read/write on a kernel data structure. on every Linux machine running the BPF interpreter.
the root cause of all of this: the absolute value function doesn't handle one number. one specific number, out of 4.2 billion possible inputs, and it's the one that gives you kernel read/write. the fix is:
c
static u32 abs_s32(s32 x)
{
return x >= 0 ? (u32)x : -(u32)x;
}
cast to u32 before negating. -(u32)0x80000000 = 0x80000000 unsigned. correct absolute value, no overflow, no undefined behavior. the kind of function you'd assume already exists somewhere in 30 million lines of kernel code. it did not. I got to write it. :D
I reported this, wrote the patch, got it through 5 revisions of review. acked by Yonghong Song and Mykyta Yatsenko. now patched in stable 6.6, 6.12, 6.18, 6.19. if you haven't updated your kernel: maybe do that.
If LLMs really made workers more productive in a general way, as is claimed, and this had been going on for a couple of years, as is claimed, wouldn’t we expect to see a boost to the economy and an uptick in consumer sentiment, rather than like, historic lows?
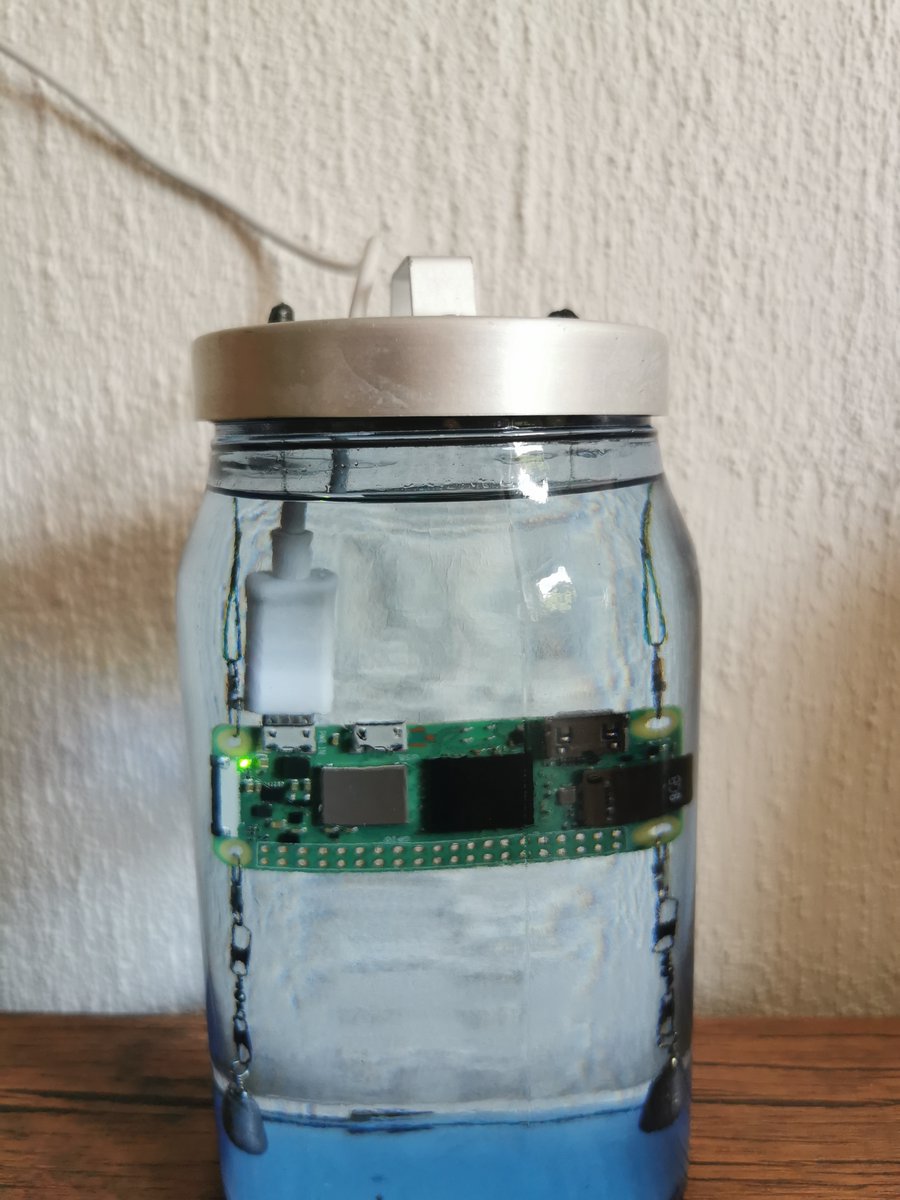
Vor genau einem Jahr habe ich einen Raspberry Zero2 W in Paraffinöl versenkt.
Das Öl sorgt dafür, dass der Prozessor auch unter Höchstlast kaum wärmer wird als Zimmertemperatur.
Seitdem berechnet er mit einem BOINC-Client für die Mathematisch-Physikalische Fakultät in Prag 24/7 Asteroidendaten.
So ermitteln wir die Umlaufbahnen aller Asteroiden und wissen, wo die ihre Bahnen ziehen und auch, ob wir uns Sorgen machen müssen, dass uns einer in Zukunft trifft.
Ein genau baugleicher Zero2 W mit genau der gleichen Software führt genau die gleiche Aufgabe ungekühlt aus.
Und jetzt stellt sich die Frage: Macht perfekte Kühlung einen Leistungsunterschied aus?
Und die Antwort ist: Ja!
Und zwar signifikant! – 5,97 %
So das wäre auch geklärt. 😀
For the first time in over 20 years, you’ll be able to board a train in Oslo and get off in Copenhagen, Hamburg, or Berlin, without a single train transfer! Starting in summer 2028, Vy will launch this route in collaboration with DSB and Deutsche Bahn.
https://t.co/36TtEHbC1K