@signorina37H@securityaffairs Aziende che fatturano i fantastiliardi l'anno, con dirigenti e manager che prendono i milioni, e poi su Linkedin nelle offerte di lavoro cercano persone in sede 5 giorni a Milano con seniority di 10 anni per 35K di RAL. Questo paese é composto solo da pagliacci.
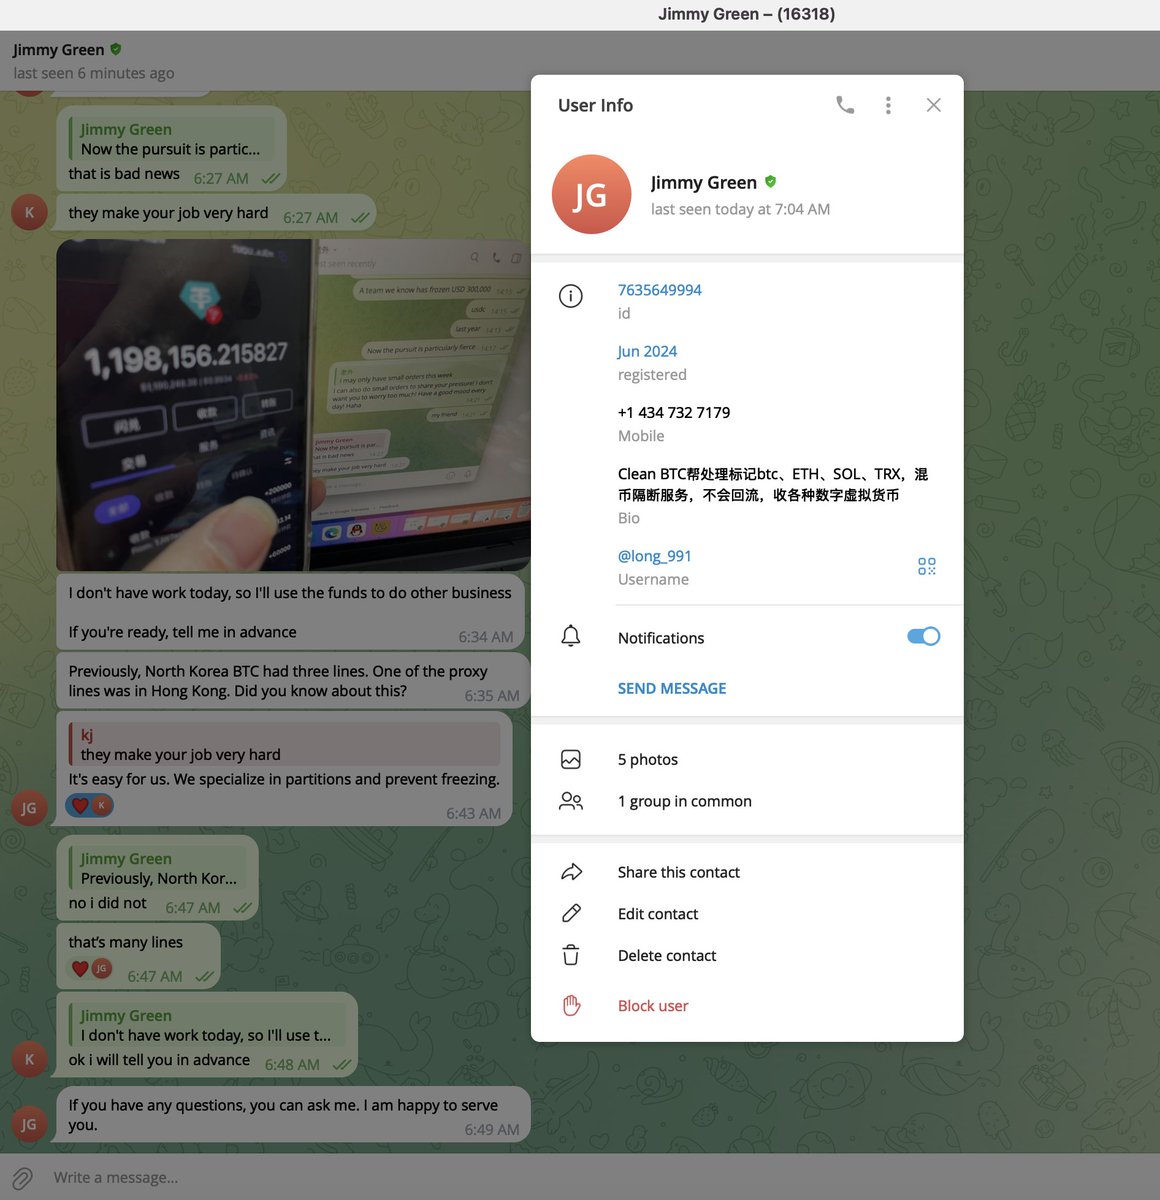
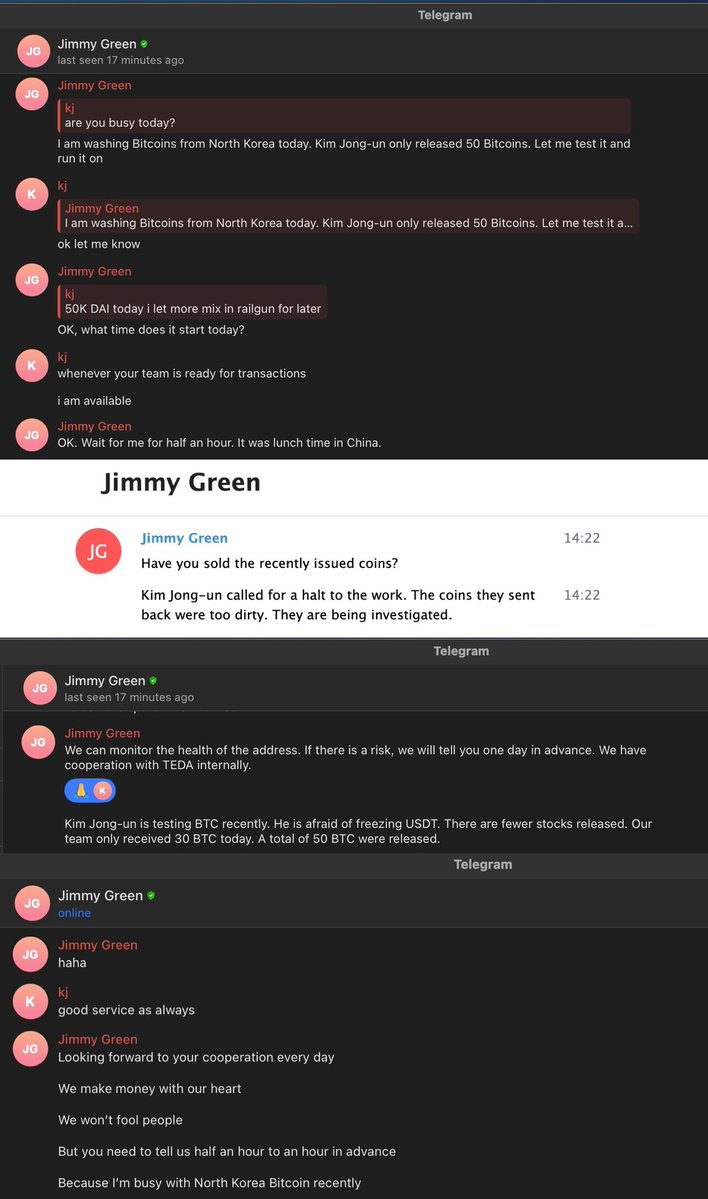
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
1/5
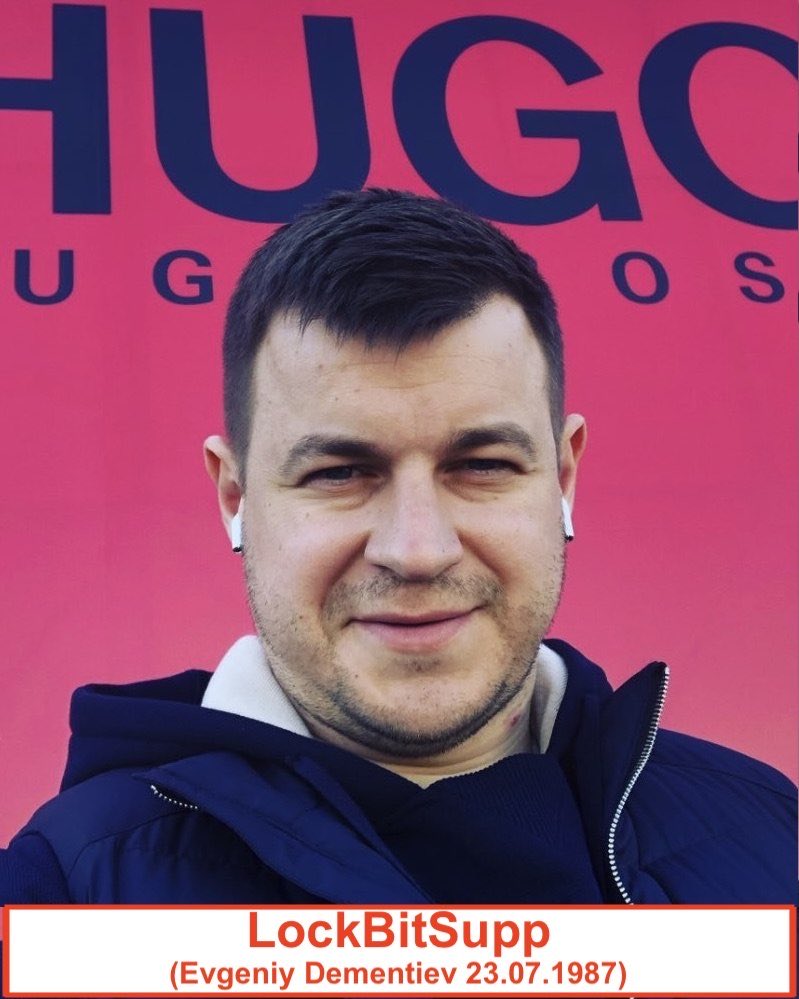
I have something new on LockBitSupp.
This is Evgeny Dementyev - the leader of LockBit.
Instagram username: dementev23
Photo from 2019.
Initially, I was skeptical about this finding. 👇
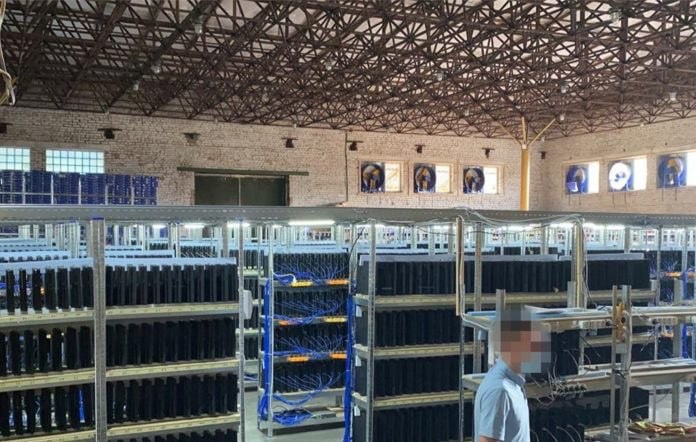
The Police once raided a warehouse and found 3,800 PlayStations running FIFA
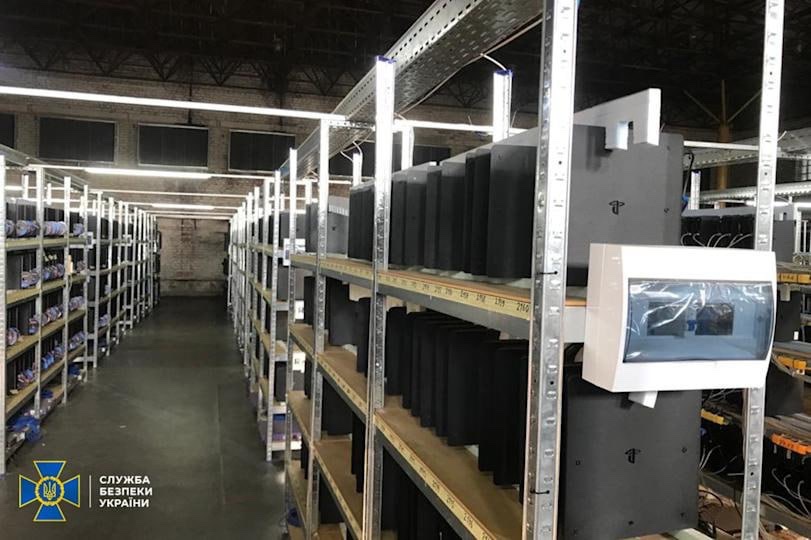
Ukraine's security service raided a warehouse in Vinnytsia expecting to find a crypto mining farm
Instead they found PS4 consoles stacked on racks from floor to ceiling
Every single one was running FIFA 21 on autopilot, farming Ultimate Team coins 24 hours a day to sell on the black market
The operation was stealing $259,000 a month in electricity and causing power blackouts across the entire city
The consoles alone were worth $1.5 million
EA makes $1.6 billion a year from Ultimate Team
The FIFA coin black market is worth over $200 million a year
At black market rates, 3,800 consoles farming coins 24/7 could pull in $3 to $5 million a year
Around the same time an actual EA employee got caught selling rare Ultimate Team cards for $1,000 each on the side
Even the people who made the game were running the same hustle
1/12 Lots of people asking if I make every Asian male I interview insult Kim Jong Un - for the avoidance of doubt, I only ask someone to insult Marshal Kim when I'm already confident they're North Korean and trying to defraud.
But how did I know Taro was North Korean? 🧵
Bias in CTI attribution is harder to shake than you think.
The DPRK/cybercrime boundary has always been blurry, but today I got a personal reminder of just how biased I still am.
Here's what happened:
1⃣ First look: I encountered a compiled AppleScript malware (Zoom Audio SDK Update.scpt, MD5: 743f60f02d352201e2df36805f1ec00d). I suspected a link to `APT38` due to their known use of similar social engineering lures, including ClickFix techniques.
2⃣ Deeper dive: I checked the 2nd and 3rd stage payloads. I told myself they'd just changed their tradecraft. Still convinced it was DPRK.
3⃣ Final payload: The last-stage AppleScript was focused on stealing a wide range of sensitive data from the victim. Something felt off. I ran it through my IOC search bot. Result: `SHub Infostealer`, known crimeware, nothing to do with DPRK. DataDog published a solid write-up on it: 🔗 https://t.co/5LJasT2xbx
If I had stopped at stage 1 or 2, I would have published a completely wrong attribution. Attribution requires full context. Our prior knowledge is a lens that helps us work faster, but it's also a blindfold. The more deeply you specialize in one actor, the more you'll see that actor everywhere. Stay humble. Follow the evidence to the end.
The Canadian Negotiator with a Russian Accent: Conti’s Shadow Diplomat
In the article:
• the “triple extortion” scheme — how victims ended up directly in the hands of Conti negotiators;
• instructions on how to independently verify dates and flights.
• screenshots from Conti chats and direct identification;
• flights to the UAE and links to key group members;
This material can serve as a foundation for criminal and journalistic investigations.
👉 Read full article: https://t.co/GzKejmgfs5
Next👇
It is a deep dish ransomware lasagna. A ransomware dork impersonating a ransomware dork by using dorky ransomware source code stuff that was leaked.
I'll still share this code with vendors if they're still interested
https://t.co/fjnv9KPwT3
NOW: US court permanently bans Pegasus spyware maker from hacking WhatsApp.
NSO Group can't help their customers hack @WhatsApp, etc ether. Must delete exploits...
Bad news for NSO. Huge competitive disadvantage for the notorious company.
Big additional win for WhatsApp 1 /
🔎 EU sees surge in hacktivism, DDoS & ransomware
ENISA’s 2025 threat report finds most attacks are now driven by hacktivist motives, with DDoS composing 77% of cases.
Ransomware remains a leading tool for damage, while phishing and supply-chain threats persist.
🔗 read the full report: https://t.co/yniLWE5qT9
#ransomNews #EUthreats #Hacktivism
I have been tracking the Bitcoin address of the ShinyHunters leader. During a negotiation, the actor (‘shinycorp’) provided this wallet (bc1q5530apqz86eywm2f84mpcyuux3dv9mmztsdxt2) as a payment option. Blockchain analysis shows that on September 15, 2025, this wallet received 4.25 BTC (≈$491,000 at the time) in a single transaction.