Most hacks don't break the code. They break an assumption the code was built on.
A protocol always rests on things that must stay true. Total supply matches the sum of balances. An oracle price drops below a threshold. When one of those quietly stops being true, the exploit has usually already started.
Glider Monitor lets you track exactly those conditions. Write your own invariants for your contracts, or use the ones we ship by default, and get alerted the moment one breaks, while there's still time to act.
An exploit is loud. A broken invariant is the quiet signal that comes first
Standard monitoring isn't enough anymore. So we built on top of it.
Today we're launching Glider Monitor, built for everyone in Web3 deploying Contracts or Capital.
At its core is Glider - which recognizes any on-chain pattern and tracks it across your contracts continuously, protecting you on multiple fronts.
• Exposure replay: when an exploit hits another protocol, or a novel attack vector surfaces in public research, we replay it against your contracts and tell you if you share the vulnerability - before it reaches you.
• Dependency risk & invariants: your contracts trust oracles, vaults, and third-party code. Glider Monitor maps your full dependency graph automatically and monitors invariants for known risk classes - stale oracles, vault health, stablecoin depegs - plus custom invariants built for your specific risk profile.
• Real-time attack monitoring: continuous observation of your contracts, alerting you the moment you're targeted.
Threats in web3 are continuous.
Now your security matches the pace.
Start with our free tier, <10 contracts, 60 seconds onboarding.
Breaking down the Aptos bug - LIVE
Sitting down with @kemmio, CTO of Hexens, to talk through the Aptos Move VM bug that put up to $70B at systemic risk.
We'll go through how it was discovered, what the real attack chain looked like, and how something that cost $3K to build hit a ~90% success rate in simulations.
Tomorrow, July 14 at 15:00 UTC, live right here.
Set a reminder and bring your questions.
Cross-chain bridges remain critical infrastructure, proof verification is the core of their security model.
New disclosure on our research page: a vulnerability in the Polygon Plasma bridge that allowed transaction proofs to be forged.
At the time of discovery, $800M in POL was at risk, exploitable in a single transaction with no prerequisites.
The research covers how the proof verification breaks, how the exploit was built, and what it means for bridge security.
Full technical deep-dive: https://t.co/Zigi7VwNes
This wasn’t planned to be the first article on our new Research page, but the publishing dates aligned.
I inexcusably took that right from @0xkasper who has a billion-dollar-banger article coming on there… so definitely stay tuned
A bug is a bug, they will always come and go, but setting up security infra and processes is whats crucial, so some lessons learned:
For ecosystem - smart contract data IS CRUCIAL, potentially cycle-ending bugs can be timely mitigated if the datas there and searchable
For me - need to add filtering for via-ir flags and compiler flags to Glider, and some other filters too
PS: was pleasure to work with @solidity_lang@_SEAL_Org teams once again.
(not a lot of you know but @rootNad skillz in querying data and processing it in short period of time is insane)
For the first time in history, researchers will compete to build a permanent security knowledge base.
Every contribution from the contest will become part of a lasting and evolving resource, designed to serve not just today, but also future generations of builders.
We're so happy that @ethereumfndn is contributing to the prize pool for the Glider Contest.
Other chains and protocols can still join this historic event to help shape the future of blockchain security.
Proud to become a SR team leader at @certora and to work with such a brilliant team.
Grateful for the trust, support, and the opportunity to keep pushing harder to help secure the space.
Proud to be the first auditor on the @bountyhunt3rz the most popular one, I haven’t missed a single episode.
Cutting weight these days, so I might’ve sounded a bit tense xD
Huge thanks to @0xriptide for having me on 🫡
Web3 security beginner mistake #1
Don’t read past audit reports without context, it is a WASTE OF TIME.
Instead, read the code first, understand it, try to find something on your own, then read the report.
Advanced researchers mainly use audit reports as an opportunity to find new attack vectors or new issue ideas on the types of projects they are ALREADY familiar with.
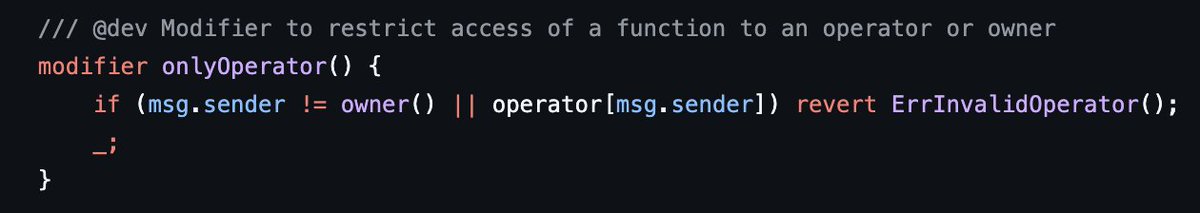
Most of the time, developers mess up when there are multiple conditions in the `if / revert()` logic. Always double-check the logic, as it can lead to even critical issues.
One example, I saw this modifier in a past contest:
It was supposed to restrict access to an operator or the owner, but instead, it only allowed the owner who is not an operator, as a result operators could never call functions using this modifier.
Here is the fix:
.
if you want to boost your auditing performance (and not only that), keep a student’s mindset. it helps me both at work and in jiu-jitsu
even if it's your 10th time auditing an ERC4626 and you know it like the back of your hand, always read the code as if you're learning. ask yourself why is this here? why did they write it this way? the moment you think you know everything and start “doing your job,” your performance will be low
i apply the same approach in sports, everyone knows i’m good at armbars, but i still do them with curiosity, always looking for ways to improve and do them even better, and more correct
1st competition on @HatsFinance. Didn’t know submissions are on-chain, it gives a bug bounty vibe. Enjoyed this one.
Thanks to @HatsFinance for the opportunity and @MentoLabs for their strong commitment to security. Afair, this was their 4th audit. 🫡
Glider AMA loading ⏳
Tomorrow we’re hosting an exclusive AMA on Glider, our first-of-its-kind sec research tool.
Learn how to write queries, get onboarded, ask away.
🗓️ Feb 5, 2 PM utc
👾 Set reminders: https://t.co/5bPFdWrsDw
New challenge added: "Healthcheck as a Service" 🩺
Authored by @p0wn4j (@hexens), this web challenge comes with a reminder: "Check yo' self before you wreck yo' self."
The challenge link is live—are you ready to dive in and solve it?
500 points up for grabs.
#remedyctf2025 #remedyctf
New challenge added: "Memorable Onlyowner"
Authored by @rootNad, this one dives into smart contract mistakes—some small, and some... well, memorable.
A developer wrote an onlyowner modifier but left something crucial out. can you find what’s missing?
500 points are on the line. the first blood has already been claimed.
#remedyctf2025 #remedyctf