Cloud hacking tools for bug bounty hunters:
CloudFox
https://t.co/htfw49SLGM
Pacu
https://t.co/CXdO5YRnIG
S3Scanner
https://t.co/cIb5YdxfI8
Extra tools, not purely cloud but used a lot in this workflow:
Nuclei
https://t.co/UiXI7zZFT1
TruffleHog
https://t.co/lEqC1BzIyj
#BugBounty #CloudSecurity #Pentesting #InfoSec #EthicalHacking #CyberSecurity
The best Linux resources that are FREE to learn in 2026:
1. Linux Foundation Training
https://t.co/lb0u5E5ptl
2. Linux Journey
https://t.co/jtGd0Muzi8
3. Ubuntu Tutorials
https://t.co/Bzzqyvh5ay
4. Red Hat Training Resources
https://t.co/czdQ2HZkI9
5. GNU Documentation
https://t.co/Fr8DYYHP9p
6. OverTheWire Bandit (Linux Wargames)
https://t.co/fEVqANSlkV
7. The Linux Command Line Book
https://t.co/Vzk5I7x9Vj
8. MIT Missing Semester (Linux & CLI)
https://t.co/mGRZgMjgi2
9. DigitalOcean Linux Tutorials
https://t.co/Gewym4sg2b
10. Linux From Scratch
https://t.co/2HPp4ZLj4r
11. Arch Linux Wiki
https://t.co/CdfA9gOOGg
12. freeCodeCamp Linux Course
https://t.co/i8ZbNPhXYw
13. Linux Survival
https://t.co/a94ZVchlJp
14. NDG Linux Essentials
https://t.co/IBMbsG2xTQ
15. Bash Guide
https://t.co/q6wAtVeRVB
Everything you need is already free.
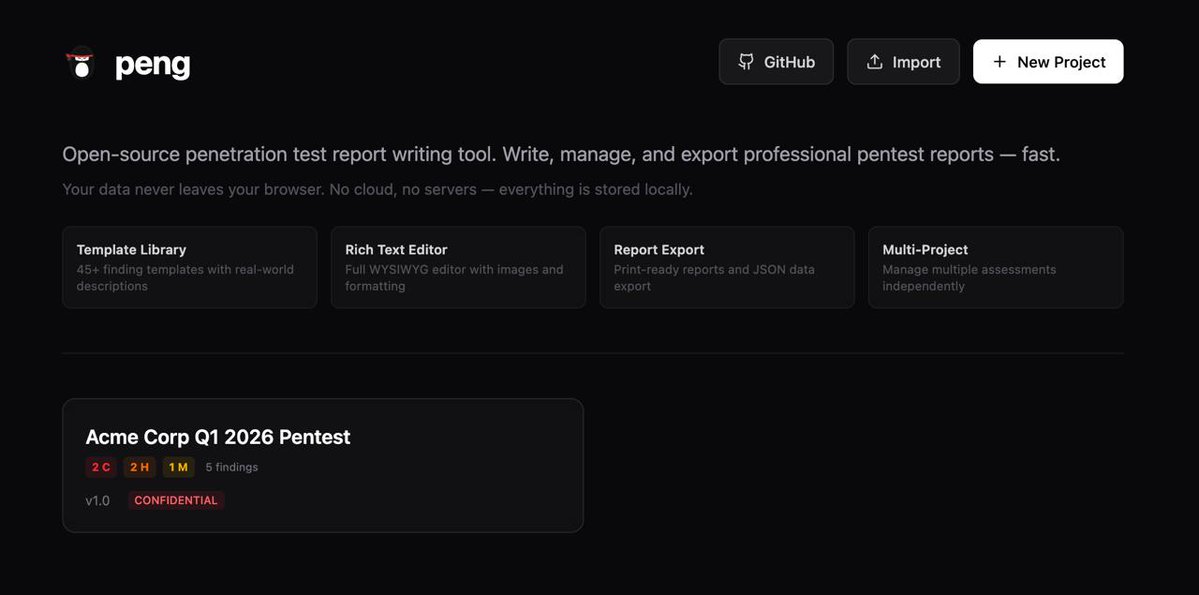
Tired of copy-pasting Word templates for your pentest reports? 😩 We fixed it! 🚀
Meet Peng 🥷 — our new open-source penetration test report writing tool!
We originally created Peng to help Hackviser users easily write their reports after passing our certification exams. But we loved the result so much, we decided to make it open-source for the entire cybersecurity community! 🌍
Here is why you'll love it:
🔒 Privacy First: Zero cloud, 100% local. Your data never leaves your browser.
📝 Template Library: 45+ real-world finding templates ready to use.
⚙️ Easy Export: Get print-ready professional reports in seconds.
🔗 Try it out now: https://t.co/eUM1tD7req
''Proof-of-concept for CVE-2025-48593: No, this Android Bluetooth issue does NOT affect your phone or tablet''
#infosec#pentest#redteam#blueteam
https://t.co/iAUHRrRWhI
ATO via OAuth unsanitized schema
This is such a sneaky finding. Bugs like this just continue to prove that thinking away from the norm will go a long way. Get weird.
Blog link👇
https://t.co/4HmygB2FAh
My favorite vulnerability this year didn’t look dangerous at all at first.
While I did find things like SQL injection, RCEs, race conditions, and broken access control, the one that really stood out to me was a blind SSRF that slowly turned into a critical issue, exposing AWS metadata and credentials. It started as something easy to overlook, and that’s exactly what made it special.
This finding taught me an important lesson: some of the most impactful vulnerabilities only reveal their true severity if you stay patient and keep testing beyond the obvious.
I’ve documented this entire journey in a dedicated SSRF video on my channel, from finding SSRFs on real-world applications to breaking down this exact complex case step by step.
If SSRF has ever felt confusing, this should help:
https://t.co/FReH7ORg0s
(Image attached just to represent the vulnerability & taken from here: https://t.co/DYQ17Oie0q)
Alhamdulillah for everything Allah has given me.
📊 Bug Bounty Yearly Report — 2025
Total Reports: 27
• Info: 5
• Low: 19
• Medium: 2
• High: 1
• Critical: 0
Duplicates: 18
N/A: 1
💰 Total Reward: $2860
In Sha Allah, I will do better in 2026.
#BugBounty#CyberSecurity
reconTricks # Underrated Technique
1. Go to YouTube.
2. Search for “test org poc”.
3. Search for “test org bug bounty poc”.
4. Search for “test org vulnerability”.
5. Search for “test org x api setup”.
6. Search for “test org x api usage”.
7. Quickly review all the videos. You can quickly learn the company’s API usage and its many vulnerabilities, and focus on the relevant ones there. Many hunters may miss important points when focusing on Google dorks and GitHub dorks. When hacking, I love using YouTube.
#bugbountytips #BugBounty #EthicalHacking #CyberSecurity
SSRF in pdf generation!
this api endpoint send the pdf generation request:
POST /api/v1/convert/markdown/pdf
Add this payload:
<img src=‘burp collab url’ />
comes 200ok and hit request in burp collaborator.
For more join my BugBounty telegram channel👉🏼 https://t.co/J6uPf8H57o
Day 144 - Bug Bounty
- Went today deep in authentication flows
- Learned a lot about different edge cases using different encoding/null bytes
- Found this repo, which constantly updates the best ATO H1 reports:
https://t.co/5pkC7VGFzB
Total earned so far: $5425
A smarter web fuzzing tool that combines local LLM models and ffuf to optimize directory and file discovery⚔️
- https://t.co/pVFw2sWTtd
#infosec#cybersec#bugbountytips