For over 20 years, our CEO @MehowHacks has been finding security flaws before they become global problems.
From hacking electronic voting machines for the U.S. government to building one of crypto's most ambitious security companies, his mission has stayed the same: fix the infrastructure before it fails.
Read his latest profile by @Entrepreneur UK on why he believes crypto's biggest vulnerability isn't the blockchain, it's how people actually use it.
A crypto address was meant to be a destination.
It became an identity.
Share it once and you've handed over a permanent, searchable record of everything you've done and will do.
No other financial system works this way.
Your account number isn't your public profile.
The single reusable address was a technical shortcut in 2009.
It became crypto's biggest privacy failure by default.
The pace of crypto development is also its biggest vulnerability.
Protocols ship before they're battle-tested.
New features open new attack surfaces faster than anyone can audit them.
Every innovation is also an unexamined door.
The industry rewards being first.
Attackers reward everyone who was first and unprepared.
Q2 2026 just became the most hacked quarter in crypto history.
83 incidents.
Double the previous record for attack frequency.
But the dollar losses weren't record-breaking.
The shift is the story: not a few giant exploits anymore. A constant stream of smaller ones.
The attack surface didn't shrink as the industry matured. It multiplied.
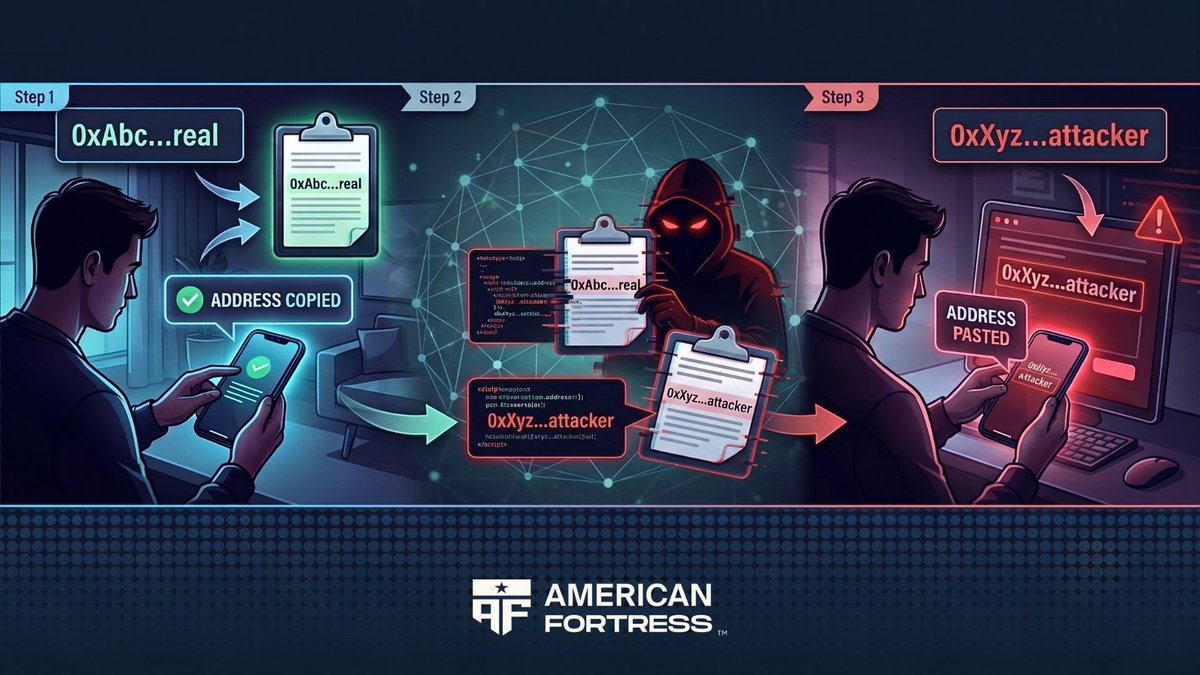
A new strain of malware is quietly rewriting crypto addresses on infected devices.
You copy a legitimate address. The malware swaps it for the attacker's before you paste. You confirm a transaction that looks right and isn't.
One recent campaign targeted 217 banking and crypto apps with this exact technique.
Before any transfer: verify the pasted address against a separate trusted source.
The clipboard is not a safe place to trust an address.
"Decentralized" is doing a lot of heavy lifting in crypto right now.
How decentralized is decentralized enough?
DeFi platforms are facing pressure to add identity-attestation, which raises the obvious problem: if a protocol can verify identity, how decentralized is it really?
The answer isn't more centralization or less. It's identity that can be proven cryptographically without a central party holding the records.
Verification and decentralization aren't opposites. The infrastructure just hasn't caught up to that yet.
After the year's biggest hacks, the stolen funds followed the same path.
Cross-chain liquidity protocols with no KYC.
Privacy tools to obscure wallet links.
Conversion to Bitcoin through intermediaries.
The exploit gets the headlines. The laundering infrastructure is what makes it worth doing.
As long as anonymous rails exist for moving stolen funds, the incentive to steal them never goes away.