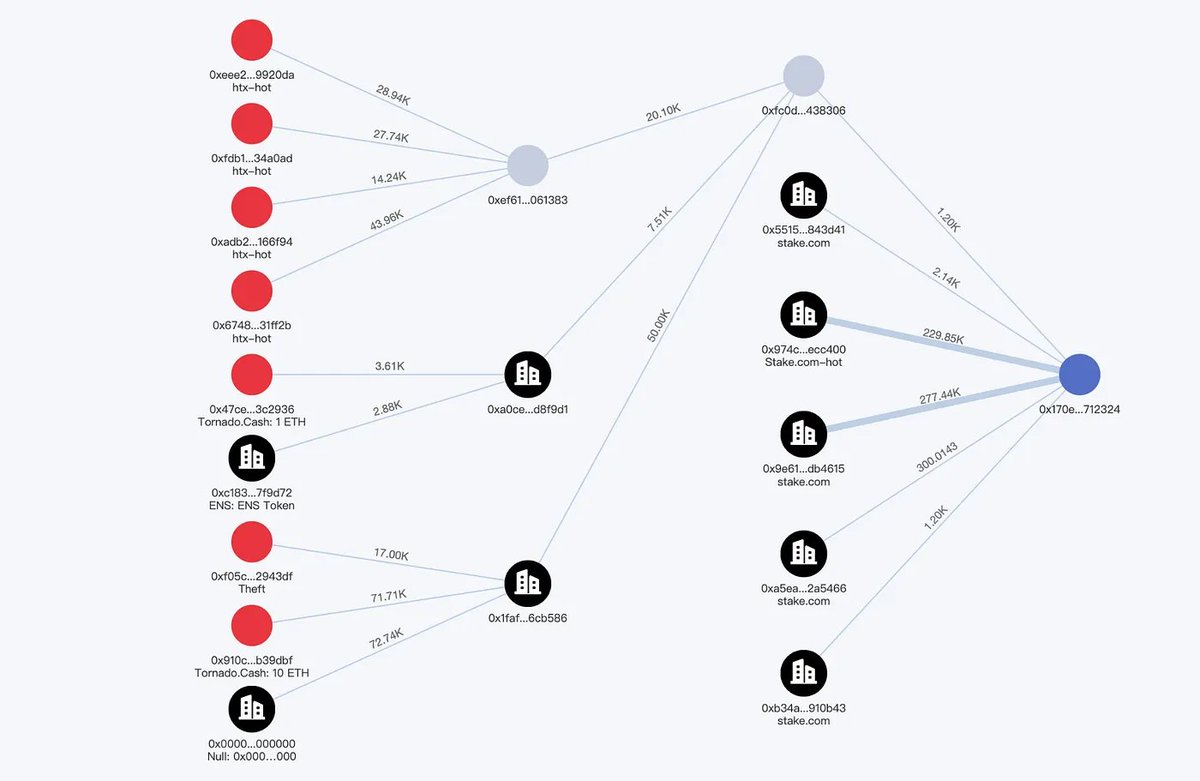
Crypto doesn’t just disappear — every transaction leaves a blockchain trail.
Wallets & transfers are traced step by step using technical analysis + documented evidence.
Recovery is real, not guesswork. Hacks are real too.
Reminder: @XamanWallet support is ONLY available in-app via the "Xaman Support" xApp.
We will NEVER email, call, DM, or contact you through any other channel.
No exceptions. Protect your $XRP.
Get world-class support directly in Xaman.
This takes DECEPTION to whole new level.
Scammers just pulled over $2 MILLION by creating a FAKE GIWA blockchain and tricking users into sending more than 766 ETH through a fraudulent bridge.
GIWA is a legitimate Ethereum L2 connected to Upbit. Its mainnet had been teased, but had NOT launched.
Scammers exploited that anticipation by copying GIWA’s Chain ID, 9134, and setting up a working RPC and fake bridge.
Users could connect wallets and transact, making everything appear legitimate while real assets flowed into scammer-controlled infrastructure.
DYOR Swap’s listing of the fake chain added to its apparent credibility.
The team now says it is preparing to use treasury funds to compensate affected users, with details pending investigation and verification.
A working network can still be a scam. Check official launch announcements, RPC details, and bridge addresses.
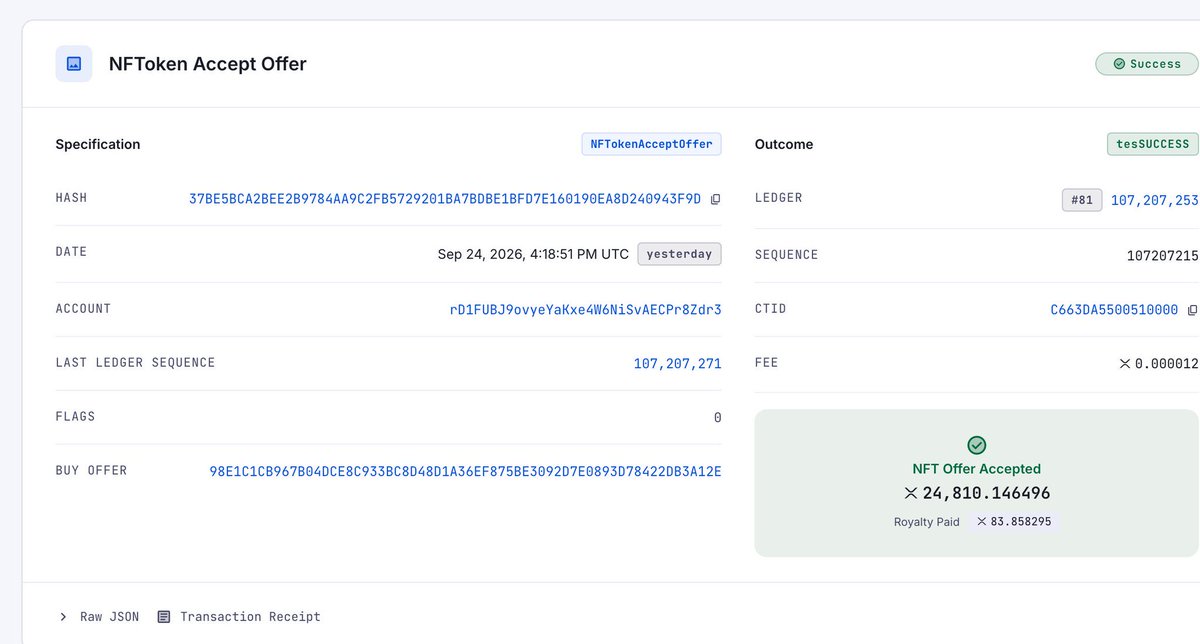
🚨 Someone lost $37,927 in XRP after signing a phishing transaction on XRP Ledger. 🎣
victim: rGtghKcmYY8gdUQwQerY5Ruww2LvdbgWVh
scammer: rNQHNruofKSCVNcatVieq5iBPjxSzFHNmx
tx: https://t.co/QMThTjwE6l…
🚨 Someone lost $37,927 in XRP after signing a phishing transaction on XRP Ledger. 🎣
victim: rGtghKcmYY8gdUQwQerY5Ruww2LvdbgWVh
scammer: rNQHNruofKSCVNcatVieq5iBPjxSzFHNmx
tx: https://t.co/XCDOqyjkrV
LATEST: 🚨 Magic Eden says legacy EVM approvals exposed over $5.7M in NFTs to an exploit against Limit Break's Payment Processor V2, though a whitehat operation was able to rescue 23,155 NFTs.
⚠️ALERT: US charges man accused of laundering $53 MILLION from crypto "pig butchering" scams.
Federal authorities say Vietnamese national Trung Nguyen Van's wallets took in about $53 MILLION from crypto scams targeting Americans since 2018.
One victim alone lost around $16 MILLION after being steered into a fake crypto platform called "Triangle."
Van allegedly moved that victim's funds into private wallets immediately after receiving them.
In pig butchering scams, fraudsters build a friendship or romance online, then lure victims into fake crypto investments.
🇺🇸JUST IN: The US government is reportedly weighing joint ventures with private firms to push dollar stablecoins overseas.
The Treasury, State Department and US International Development Finance Corp. could all be involved, as Washington aims to reinforce the dollar's reserve status and boost demand for US Treasuries, per Bloomberg.
The move comes as China pushes its digital yuan through Project mBridge and the ECB advances its own digital euro.
ICYMI: 🚨 Coinbase helped trace a $1.1M crypto trail linked to EvilTokens, an AI-powered phishing service that hit 12,000+ inboxes across 10,000+ organizations worldwide.
Growth milestone, the unusual kind!
100,000+ Xaman accounts with push on, past what xrpld's nodes were built to handle.
The XRPL's node tooling wasn't built for the scale @XamanWallet users bring to it.
But we have a fix coming in minutes! Push notifications are briefly down.
#Scottschuffer Specter has reported that @payy_link's Rollup (0x367C1...85270) may have been drained of ~$1.83M in $USDC.
The attacker has swapped the stolen funds for 683.38 $ETH and split it mainly into 3 addresses
Where's your $XRP price alert set? 👇
Price Alerts in Xaman: exact price, % move, one-time or recurring, get a notification the moment it hits.
The market doesn't wait. Neither should your notification. Be ahead.
Thanks to @Cointelegraph for covering our investigation into the FomoPeek App Store poisoning and iOS kernel exploitation, conducted together with the @wallet security team. 🫡
We appreciate the opportunity to share our findings and help users better understand the risks and recommended response. 🌟
Read more 👉:
https://t.co/6aNna4xz4n
LATEST: 🚨 A malicious iOS App Store app called FomoPeek used kernel exploits to escape Apple's sandbox and steal crypto wallet data, with SlowMist tracing ~$580K in stolen USDT to a linked hacker address.
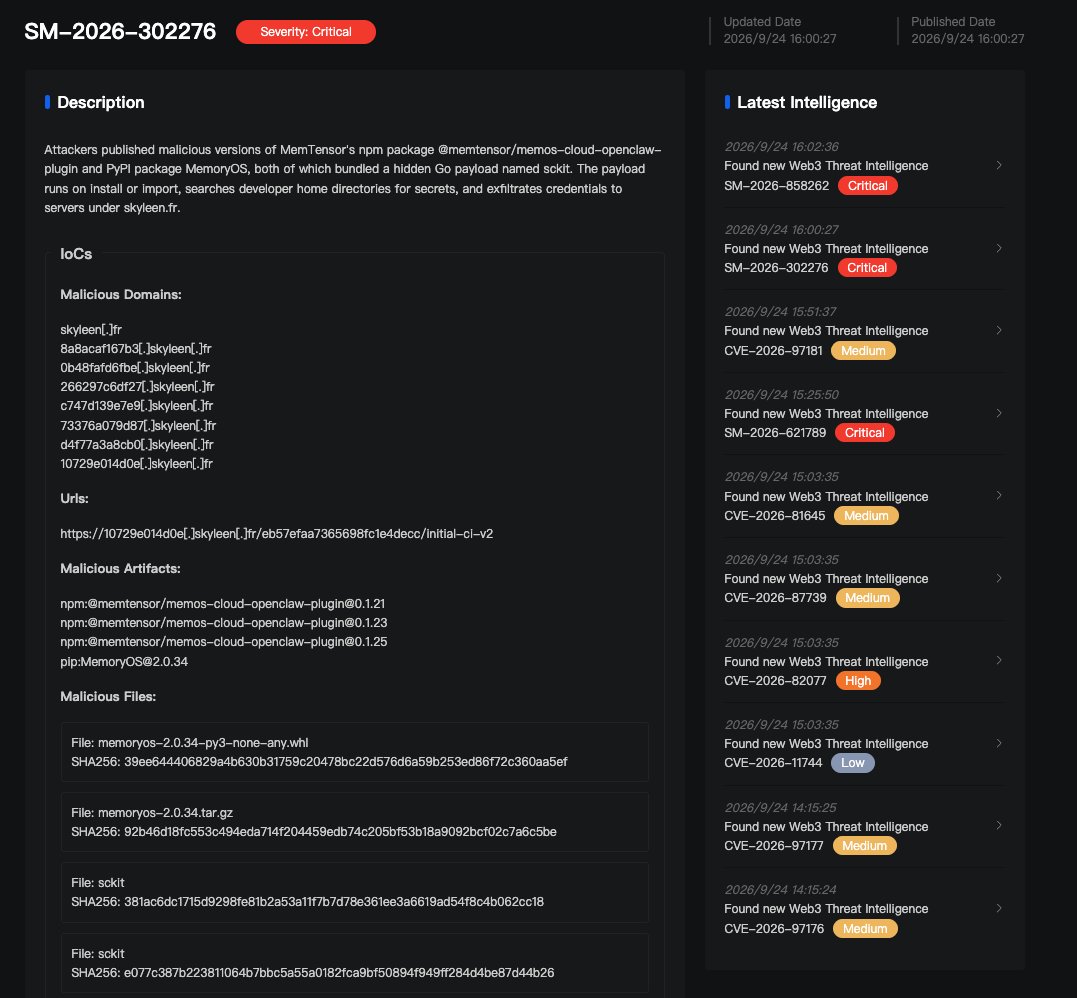
🚨 SlowMist TI Alert 🚨
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime.
Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway has been started.
Potential attacker actions include harvesting npm/PyPI tokens, GitHub/GitLab credentials, AWS keys, SSH keys, API tokens, environment secrets, and other developer credentials, with data sent to infrastructure under skyleen[.]fr. The affected npm plugin may also expose user prompt content.
Users should remove or downgrade affected packages to known-good versions (0.1.20 for npm and 2.0.33 for PyPI), terminate sckit processes, block associated infrastructure, review network activity, and rotate credentials accessible from affected environments.
You can also visit https://t.co/ft6lerUm0y to check for free whether the npm packages, pip packages, domains, or IPs you use are safe.
Reference: https://t.co/gOPP214PF8
As always, stay vigilant!
https://t.co/mXSQ8d6gyf
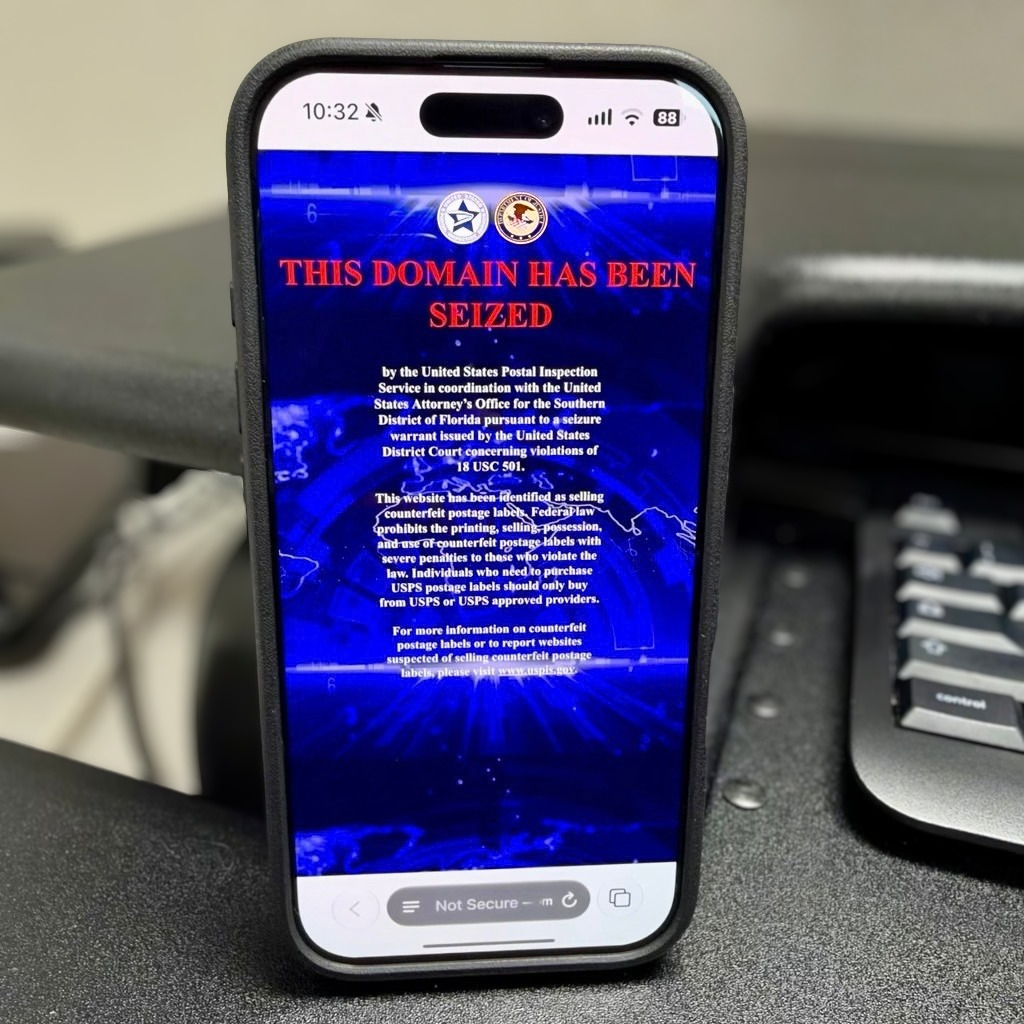
⛔️ DOMAIN HAS BEEN SEIZED ⛔️
Earlier today, the U.S. Postal Inspection Service seized a website that created millions of fake shipping labels with an estimated loss of $126 million to USPS. It is ILLEGAL to print, sell, possess, or use counterfeit postage.
Play it safe. Always purchase from USPS or Approved Postal Providers. ✅
Learn more at https://t.co/WClN36zryn.
📖 FATF Report | How to Understand and Address Risks in Gaming and Gambling
FATF’s latest report examines the money laundering, terrorist financing, and proliferation financing risks across the gaming and gambling ecosystem.
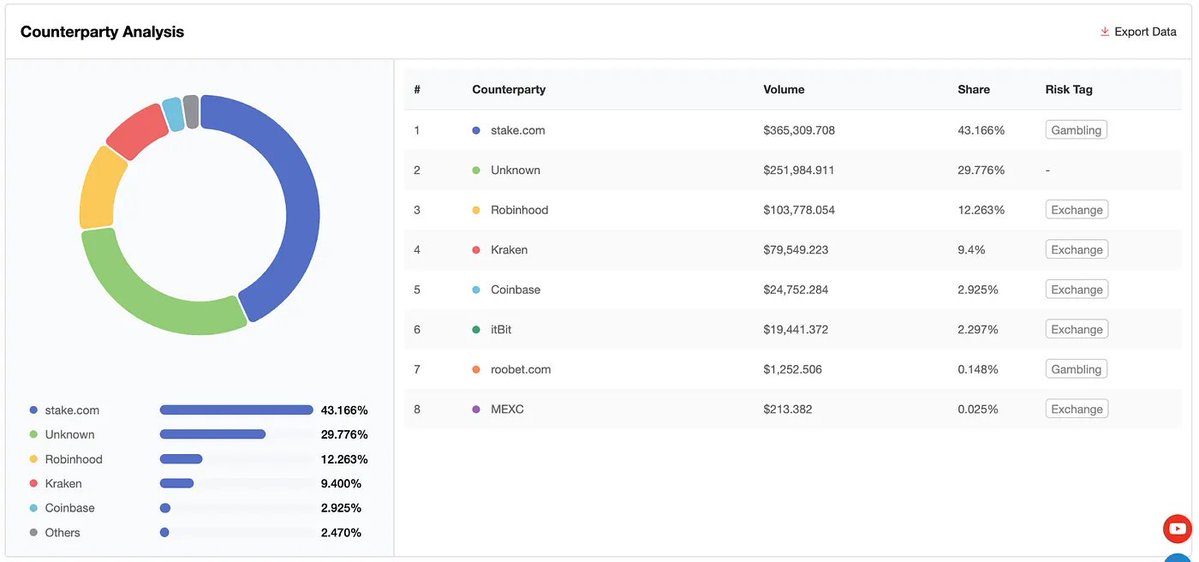
🎰 As gambling platforms increasingly connect with online, cross-border operations and multiple payment methods, including virtual assets, related fund flows can extend beyond gambling platforms to exchanges, payment institutions, and other #VASPs.
🔍 For VASPs, identifying an address linked to gambling is only the starting point. A more meaningful risk assessment requires understanding where the funds come from, who they interact with, how they move, and whether the transaction behavior is consistent with historical activity.
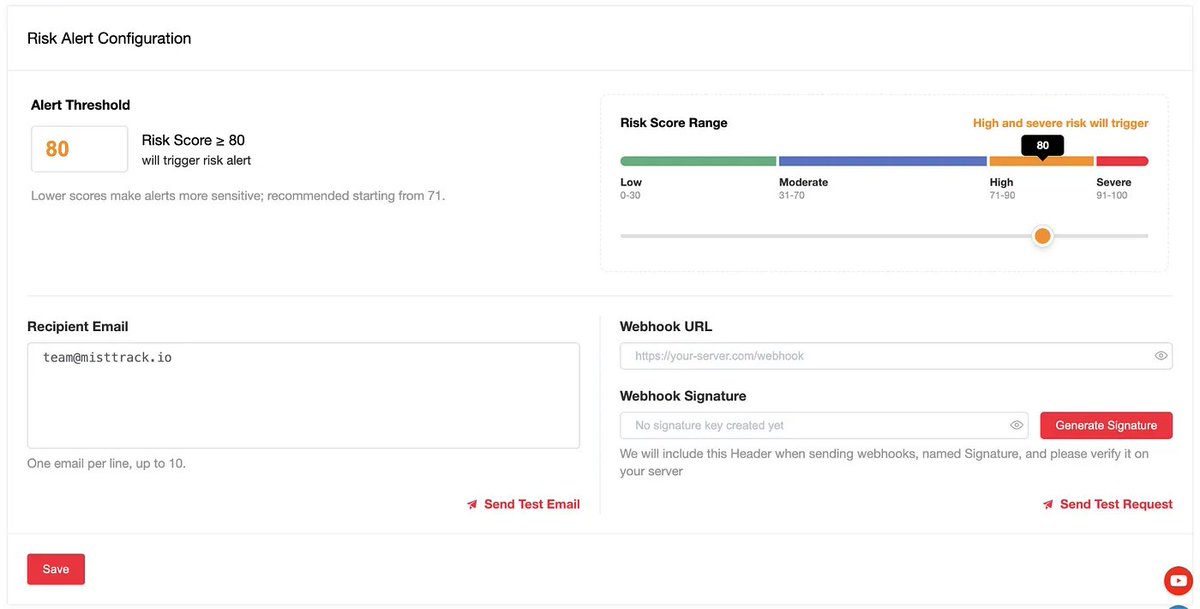
🧩 In our latest article, SlowMist breaks down #FATF’s key risk indicators and explores how on-chain analysis can help institutions move from one-time screening to continuous risk management with @MistTrack_io .
🔗 Read the full analysis:
https://t.co/xU808NYtwJ
‼️ BREAKING: An app on Apple's official App Store was serving iPhone users malware designed to steal crypto wallet keys.
SlowMist and OKX found FomoPeek versions 1.1 and 1.2, distributed Sept 9–17, hid a kernel exploit framework built to escape the iOS sandbox, decrypt the Keychain and pull data from 19 apps, including MetaMask, Trust Wallet and Apple Notes.
SlowMist traced nearly 580,000 USDT to the attacker's main wallet.