Physical security remains the most glaring blind spot for digital purists. Day 1 of Covert Methods of Entry forced attendees to confront mechanical and electronic vulnerabilities head-on. Lock manipulation, bypasses, and operational reconnaissance aren't magic tricks—they are execution-driven methodologies. Hard realities taught by @Tatramaco and Jiří Vanek.
#x33fcon #PhysicalSecurity #RedTeaming
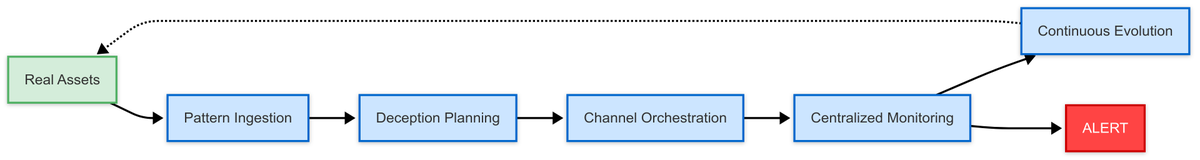
Modern C2 implants use sleep masking & metamorphic code to stay hidden. We’re revealing how to unmask them using low-level runtime telemetry (ETW & CPU profiling) live in production including a POC with a lightweight sensor.
My team will be presenting our research at x33fcon:
https://t.co/qhtckSyxx5
New post: Field Notes on Malware
A look at how C2 frameworks are evolving their evasion techniques and what it means for detection.
https://t.co/93vAnlxMar
Tainting logs coming from ETW providers?
Absolutely! In many cases it can be done from an unelevated process in userland, depending on security descriptor set on ETW_GUID_ENTRY (taken from registry).
Impact? Sending fake events on behalf of almost any ETW provider, including Microsoft-Windows-Threat-Intelligence (elevated token needed though).
And it's just few Win API calls away...
Post: https://t.co/8400UFHkIg
Also, a great presentation by Olaf Hartong (@olafhartong): https://t.co/IlmrE6zzWn
#redteam #blueteam #maldev #malwaredevelopment
We know the #x33fcon 2026 dates:
🔥Conference: onsite in Gdynia and online, June 11-12.
🚀Training: onsite in Gdynia, June 8-10.
This is the 10th edition! Reserve time in your calendars :)
Well, it happened. The company I worked at for 6 years will be closing and thus I got laid off. This doesn't affect @octopwn operations in any negative ways, but I'm actively looking for a new day job. If someone has something please DM me.
Retweets are appreciated.
Hey #x33fcon fam! 👋 We've got a lost and found situation. One of our attendees misplaced their glasses during the conference. 👓 If you happened to find them, please let us know! You can reply here, send us a DM, or shoot us an email. Thanks for helping us out! 🙏
I'm excited to announce that @C5pider and I will present a workshop at @x33fcon this June on:
"Build-Your-Own Ransomware: Hands-On Offensive and Defensive Insights"
Expect cool tricks and tips for both the Red and Blue team.
🚨 Evilginx Pro is finally here! 🚨🪝🐟
This is it! After over two years of development, countless delays, and hundreds of manual company verifications, Evilginx Pro is finally live!
Thank you all for your invaluable support 💗
https://t.co/RJI623XhtT
Want to start earning $$$ with bug bounties but don’t know where to begin? 🕵️♂️
Start with PentesterLab! Free labs, structured training, & a roadmap to success. Begin today and join the hunt!
Read more 👇
And so... Black Friday begins!
20% off on all RED TEAM Operator courses.
Coupon code: BF24
Link: https://t.co/qOr1IrCzgK
Validity: end of Cyber Monday (Dec 2nd)
#redteam
In our new #blog, Senior Security Consultant James Williams expands on his recent conference talk by breaking down how to use deserialization to backdoor a workstation with the new TrustedSec tool, #Specula. Read it now! https://t.co/Syg47Jp2ts
Aaaaaaand... We have a lift-off!
Pre-sale of RTO: MalDev Advanced (Vol.2) is now open!
Ends: Sep 30th (20:00 Zulu)
Course release date: Oct 1st (12:00 Zulu)
Diving into Windows kernel...
You can't miss it!
https://t.co/JZt5wBlE8R
#RTO#redteam#onlinelearning
If you are interested in what's coming in the Evilginx PRO phishing framework - I had the great pleasure of being invited to @Flangvik stream and demoing the new features! 🪝🐟
Feels great to finally be able to showcase the things I've been working on. 🥳
https://t.co/Dc4EAuQNuT