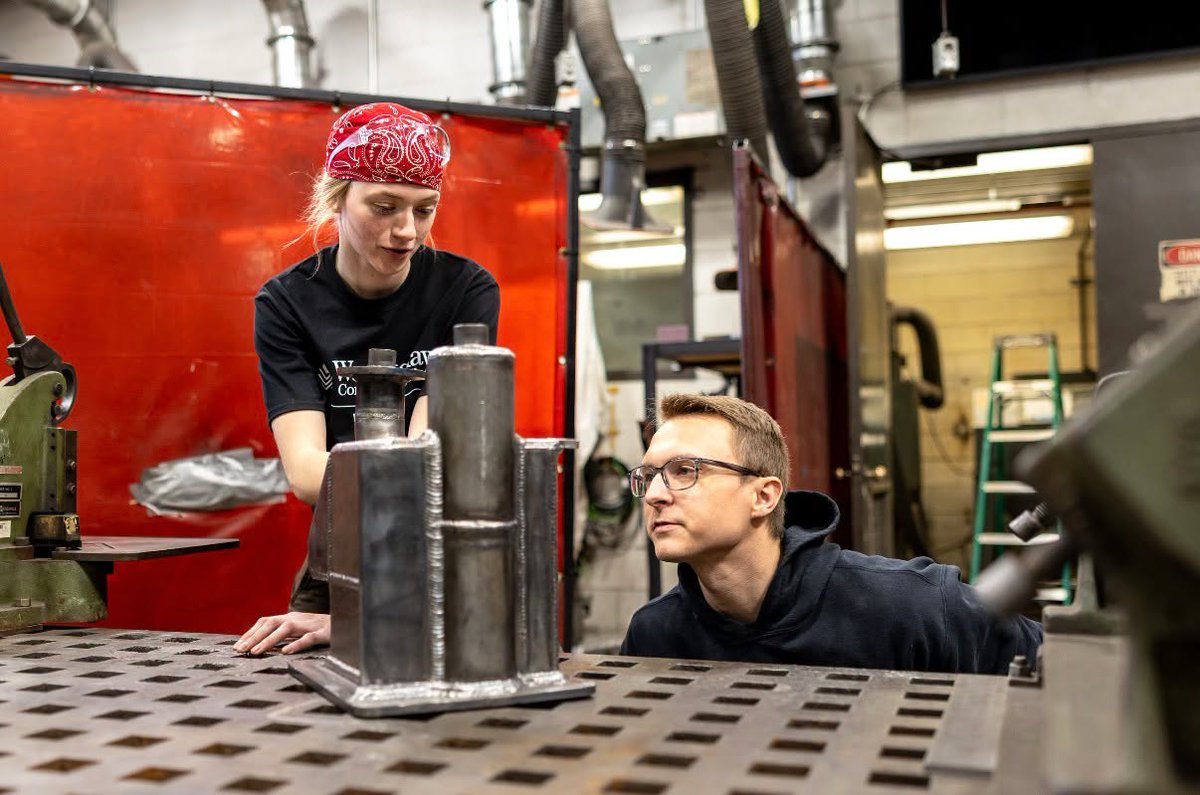
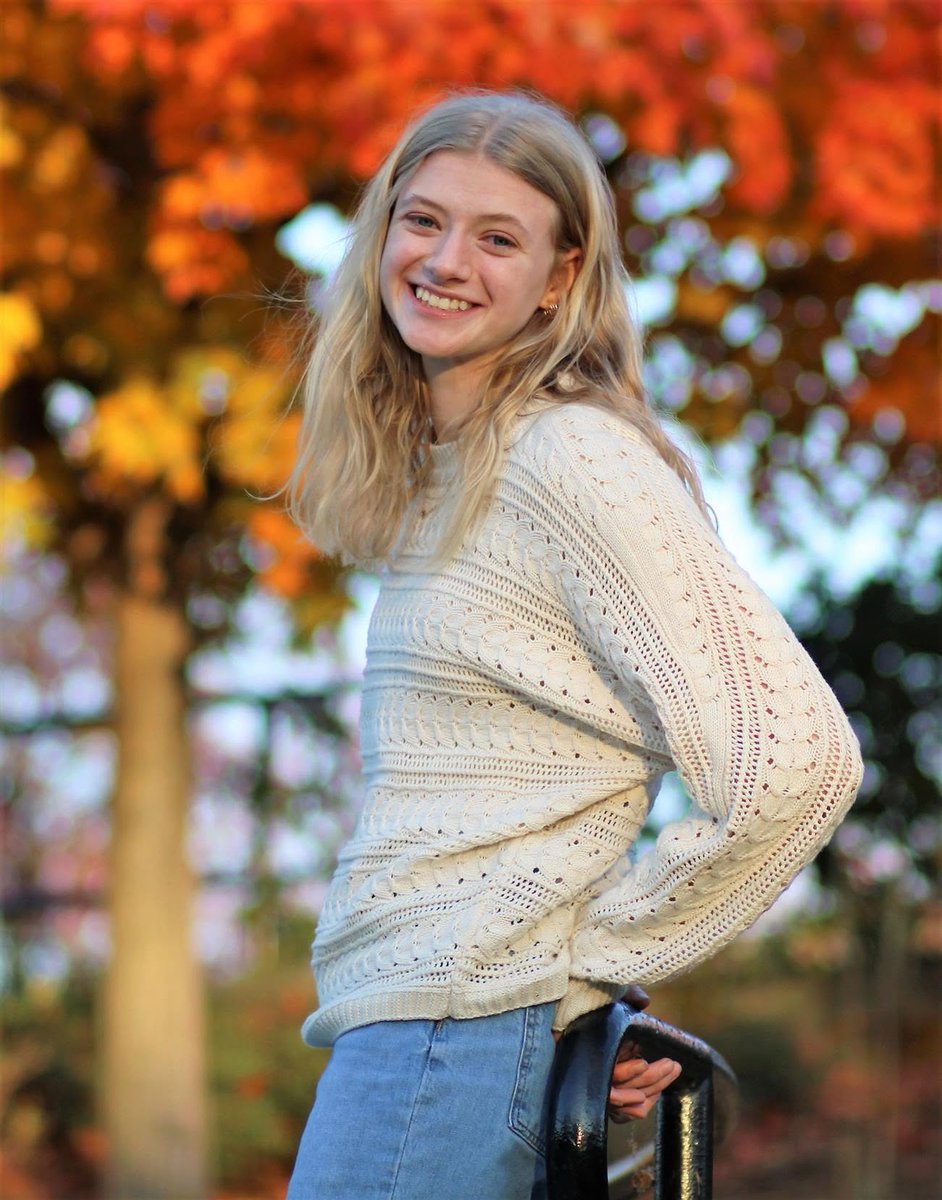
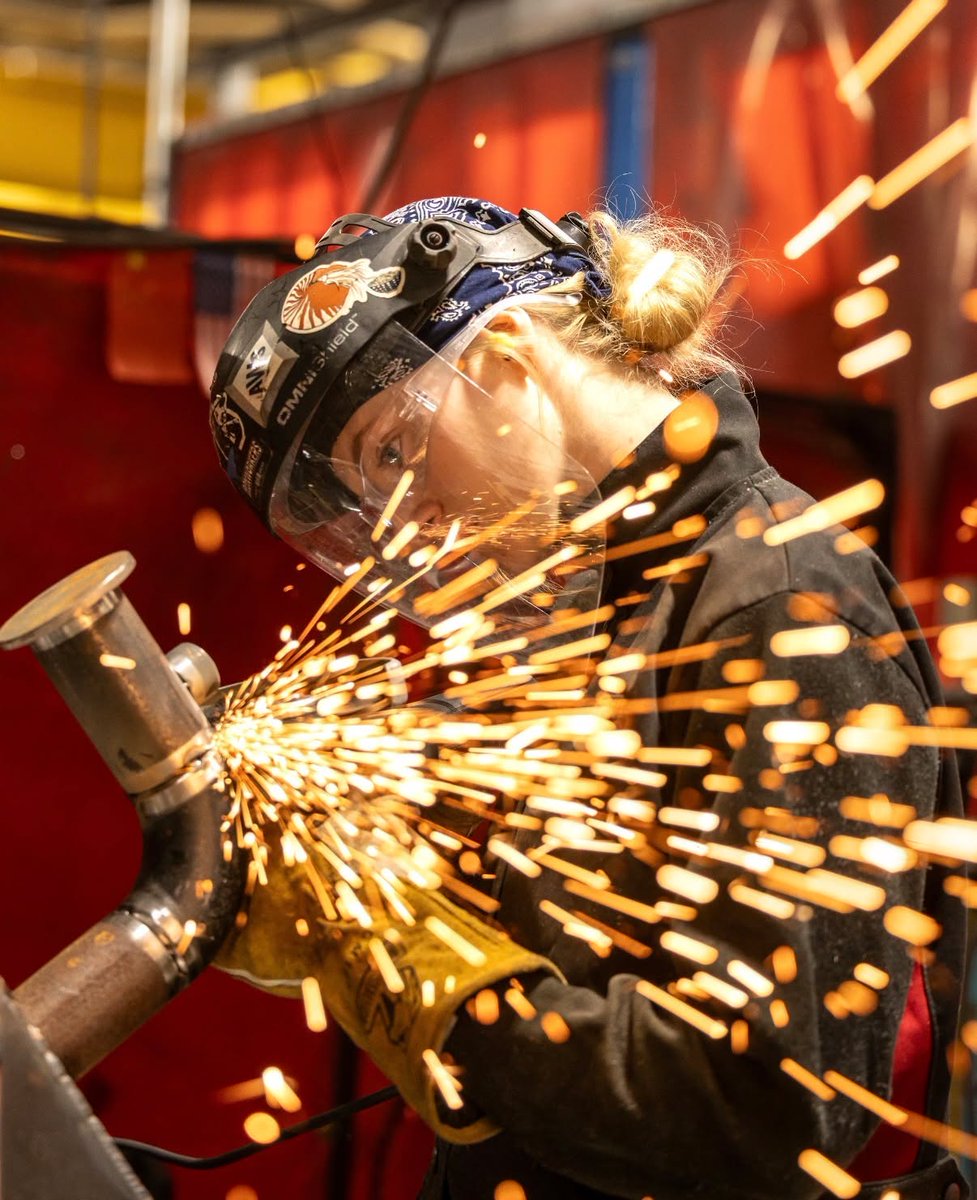
A couple years ago, Mikala Sposito applied for a work ethic scholarship from my foundation. She asked for $2,700.00 to help realize her dream of becoming a welder. (Actually, her first dream was to become an Olympian. As a kid, she excelled at horseback riding, dance, soccer, and track, but not quite at the Olympic level. So, Mikala adjusted her dream and focused on something within her reach. Precisely the kind of commonsense approach to making a living we try to encourage.) Toward that end, Mikala filled out the application, jumped through all the necessary hoops, and signed the S.W.E.A.T. Pledge, as all applicants must.
According to our internal ranking system, which is inherently subjective and relative to each batch of new applicants, Mikala scored a 94, and was awarded $2,100.00, or roughly 80% of what she asked for. This is typical of the average percentage awarded to an excellent applicant. As a rule, we almost never award the entire amount requested. We want our recipients to have some skin in the game, and we encourage all applicants to apply for additional scholarship funds elsewhere, which Mikala did. But in this case, if I had it to do over again, I think I’d have awarded Mikala the full $2,700.00. Why? Because this woman is precisely why I award work ethic scholarships in the first place, as recent headlines prove. Headlines all over the country that identify Mikala Sposito as the sole welder to represent Team USA in the upcoming @WorldSkills Competition in Shanghai.
This is a very big deal. The World Skills competition is often referred to as the Olympics of the skilled trades, so it looks like Mikala’s dream is coming true after all. And it seems to me her journey is worth a brief encapsulation. Before she applied for a scholarship from mikeroweWORKS, Mikala demonstrated an affinity for welding in SkillsUSA. As a senior at Dexter High School, she won 1st Place at the SkillsUSA Michigan high school competition and went on to place 14th nationally. Then, as a freshman at Washtenaw Community College, she repeated her success by taking 1st Place in the Michigan college division. She then advanced to nationals, where she finished 8th in the country. That earned her an invitation to the Team USA pre-trials, which whittled the nation's top 16 young welders down to three. At the final USA Weld Trials at the Robotics Technology Park in Huntsville, Alabama, each competitor was evaluated on precision, safety, technical execution, craftsmanship, and multi-process capabilities under extreme time constraints. Mikala Sposito took the Gold, officially becoming the first woman to represent the United States in welding at WorldSkills. Next week, she’ll face off against the absolute best of the best from all over the world.
I should point out that Mikala would prefer it if the press didn’t make a big deal of her gender, and I completely understand. (She’s a welder – not a “weld-her.”) But today, the industry is in desperate need of proof that women can and do excel in the trades. Nationally, just 4.3% of tradespeople are female. At mikeroweWORKS, our female applicants are closer to 20%, but I assure you that percentage could be much higher. Companies are anxious to recruit talented welders of any gender, and women need to understand and believe the opportunities are real. Mikala prove that in spades, and I want to offer her my sincere congratulations, and invite all of you to do the same. Because Mikala Sposito is exactly what our country needs a lot more of. People who understand that talent is never enough to compensate for laziness.
In her application, she wrote, “Hard work beats talent any day of the week, and nobody is going to outwork me. Period.”
She also connected with every point of the S.W.E.A.T. Pledge but said the final tenet resonated with her the most. “Some people choose to be lazy. Some people choose to sleep in. I choose to work my butt off.”
My favorite quote, however, is Mikala’s response to seasoned professionals who see her wield a torch and call her a “natural.”
“I’m not a natural,” she says. Far from it. And none of this came easy. I worked and trained 60-80 hours a week for two years to get here.”
Regardless of what happens in Shanghai, the job offers are already piling up, including the most recent from SpaceX. She hasn’t graduated yet, but the future looks bright, and I for one would not bet against her.
PS. I never do this, but since my name is in the title of the foundation, I suppose I can. Mikala – please accept the additional $600 you requested from mikeroweWORKS two years ago. Shanghai is expensive, and since you’re representing all of us, we’d like to provide you with a little walking around money. The check is in the mail.
Now…go get the gold!
Hunting CVE-2026-85706 in GitLab logs?
A 400 saying "branch is required" is not a failed attempt. It means the file was read.
We proved it by planting files with known contents and watching the error change.
https://t.co/pCd9WnJiEN
We are pleased to release tmp.0ut 5 Volume!
Get your viruses, rootkits, strange ELFs, weird machines, tiny files, cool art, and phresh beats here!!
https://t.co/tZLM50HOc0
Two new logical flaws in Kerberos just dropped at Black Hat. Low-privileged user to full domain takeover, including domain admins.
If you're doing Active Directory pentesting, Kerberos attacks, red teaming, identity security, or detection engineering, read this.
KerberLoss (CVE-2026-25177) and ResetNightmare (CVE-2026-27912). Both are logical bugs, not memory corruption. Described as surprisingly easy to exploit.
https://t.co/dgJC3JHjOf
#Infosec #RedTeam #DetectionEngineering
"If you love regex and app testing, Swapper can be worked into your testing flow for easily matching and replacing items sent in requests."
Read more: https://t.co/C7CgLQkMPu
Swapper - A Pure Regex Match/Replace Burp Extension
by: Dave Blandford
Published: 5/6/2026
To all the other veteran hackers out there, be like @Jhaddix. You don’t realize how important your words and attitude are to the next generation. You can make the difference between success and failure for them
Today I arrived at the office turnstiles at 9:15 AM.
I realized I left my badge in the Tesla.
Policy states: "No Badge, No Entry."
A Junior Dev saw me waiting.
He hesitated.
He knows the rule is "No Tailgating."
I stared him down through the glass.
I didn't speak.
I just tapped my wrist.
He panicked.
He scanned his badge and held the door for me.
I walked through without saying thank you.
When I got to my desk, I sent an email to HR.
I reported him for a security violation.
He compromised the physical perimeter.
He let an unauthenticated user (me) into the network.
He came to my office crying.
I told him: I am the vulnerability.
I am the penetration test.
You failed.
Security is not about being nice.
It’s about Zero Trust.
Oracle Cloud was breached in Jan 2025 through vulns in Oracle Access Manager. @SLCyberSec's Research team found a new pre-auth RCE vulnerability in Oracle Identity Manager (CVE-2025-61757). This is a critical vulnerability and is trivial to exploit. https://t.co/hXdzU4TJVP
Signal boosting on this for Sergeant Kevin Lloyd, who I did two deployments with.
A record correction package has been sitting on the Naval Board of Corrections for over a month.
It would update his record to reflect that he’s dying from an instrumentality of war, which would ensure his family receives full benefits as if he were killed in combat.
Because of the government shutdown, that package still hasn’t been approved.
This Marine is on his deathbed because of cancer directly related to burn pits.
@SenTedCruz and @RepLuttrell, you represent this Marine and his family. He’s in his final hours. Move heaven and Earth to make sure his family is taken care of, because I know you’ve already seen the messages my brothers have left on your phone lines.
Stop talking about it. Be about it, for once.
It would be a huge mistake to keep thinking of China as the same cyber threat actor we were dealing with ten years ago. Let's talk about it.
See you on Thursday for a more in-depth discussion.
https://t.co/EYP8nJ6YDX
Cloudflare has recently started blocking proxy tools like Burp Suite by identifying their unique TLS and request fingerprints.
If you encounter this issue, install the “Bypass Bot Detection” extension from the BApp Store. This extension spoofs Burp’s TLS fingerprint, making it appear like normal browser traffic and bypass it.
Let me pass on to you that which is of primary importance: that Jesus Christ, God come in the flesh, died for our sins according to the Scriptures, that He was buried in tomb, and that He was raised on the third day, putting death to death, according to the Scriptures. And that this genuine and historical event — the life, death, and resurrection of Jesus — is both intellectually credible and existentially satisfying.
I was just on the @SWANCapital podcast with @AndrewMcNairRYP, he asked me "if you could write one post on X that would be read by everyone in the world, what would it say?" my answer (posted above), combined a paraphrase of 1 Cor. 15:3-4 and the words that supposedly pushed @timkellernyc over the edge of belief.
Get started with iOS Mobile Application Testing with Cameron and Dave next Wednesday on the Antisyphon Anti-Cast starting at 11:30 AM EDT with our Pre-Show Banter!
To get your CPE credits be sure to register here: https://t.co/vPubaoYm4b
CVE-2025-55315, a 9.9 HTTP smuggling vulnerability in dotnet Kestrel webserver disclosed this week, caught my attention this morning due to lack of information, so I put together a very limited analysis of it. https://t.co/9y5CH2qezK
More to be done here for those interested!
Today, we publish our analysis of CVE-2025-3600 that we discovered in Telerik UI, a prolific library used in hundreds of thousands of applications.
Tagged as a Denial of Service vulnerability, today we go deeper and demonstrate RCE scenarios..
https://t.co/RzHmW1Mrgu