

Search results for ledger
People
Ledger
@Ledger

Ledger 🇺🇸 
@ledgerstatus

Block Ledger Pro™
@HypeBeastCash23

The Star-Ledger
@starledger

LEDGER
@JenLedger

Web Design Ledger
@webdesignledger

Clarion Ledger
@clarionledger

Grey Ledger
@Airdrops_one

Ledger Support
@Ledger_Support

XRP Ledger Foundation
@XRPLF

.
@Ledgerlive_CTO

Graham Ledger
@GrahamLedger

Ledger Nova
@LedgerNov_

First Ledger
@First_Ledger

The Chairman's Ledger
@ChairmansLedger

XRP Ledger Announces
@XRPL__A

Crypto Ledger
@ArcaneCryptoLd

Pascal Gauthier @Ledger
@_pgauthier

Henry Ledger
@HenryLedgerReal
mrcriminal
@LedgerNano_CT
Tweets including ledger


Does this mean the current ledger hack everywhere is because people bought a ledger device from a RESELLER?
NEVER BUY HARDWARE WALLETS FROM RESELLERS!
And a few days ago at Token 2049 (Or was it KBW) people got drained because they connected to a public WIFI?
NEVER CONNECT TO PUBLIC WIFI EVER!

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: https://t.co/4p918UH8yb

@XMRVoid Understand context, don’t be dumb. Ledger says it only affected those who purchased from an unauthorised reseller crypto billis. Ledger wasn’t hacked - it’s a fake ledger

Quantum FUD (again) and now Ledger FUD (again)
When USDT FUD? (again)
Same shit as always. Just bid the coins and stop fear mongering, pussies.

Ledger is hacked 🚨
This is what happens when you trust third party vendors with your assets:
- ledger gets exploited for $86M
- users report losing entire portfolios
- exploit linked to asian ledger reseller
If you didn’t buy your Ledger from the official site, go remove the crypto now.


@bitcoinPalmer I’m shaking, I bought my ledger at Cryptobilis and now some Indian is spending my internet moneys on Korean hookers

@CryptoWendyO It’s a hack from a retailer of Ledger . Always buy direct.

@cz_binance 我用keystone,官网可以验证有无串改过,Ledger不知道有没有这个功能


Breathing is the only way to stay on the ledger.
Joining the @BreathFi20 whitelist.
Code: BR-MQD9X7
Hold is not enough. Breathe, or it decays.
#Breath20 #Brc20

🚨🚨 يتم سرقة مستخدمين محفظة @Ledger الباردة حاليا 🚨🚨
المستخدمين خسروا اكثر من 90M$ مليون دولار حاليا
المشكلة في المحافظ اللي تم شرائها من الموزع اسمه CryptoBillis في جنوب شرق آسيا
اذا تستخدم محفظة Ledger شيك عليها ضروري و اسحب فلوسك منها حاليا لحد ما يتم توضيح الامر
قبل مدة تم تهكير ColdCard و الان Ledger الله يستر


@The_1Cryptonian @cryptobilis @Trezor @Tangem @SafePal @imKeyOfficial @OneKeyHQ @thisisarculus @Ledger Need update @tangem. Is the card safe from cryptobilis, it is also your authorized reseller

@Ledger_Support I was kind of relieved when I thought that Ledger didn't get hit by any supply-chain attack or so and boom! here we are.
Not sure whom to trust again. But again, Whenever you purchase anything, make sure you do hard-resets twice or thrice as security measures.

Ledger Investigating Reports of Drained Crypto Wallets as Estimated Losses Hit $86M
https://t.co/3Ch6eAGh4Q

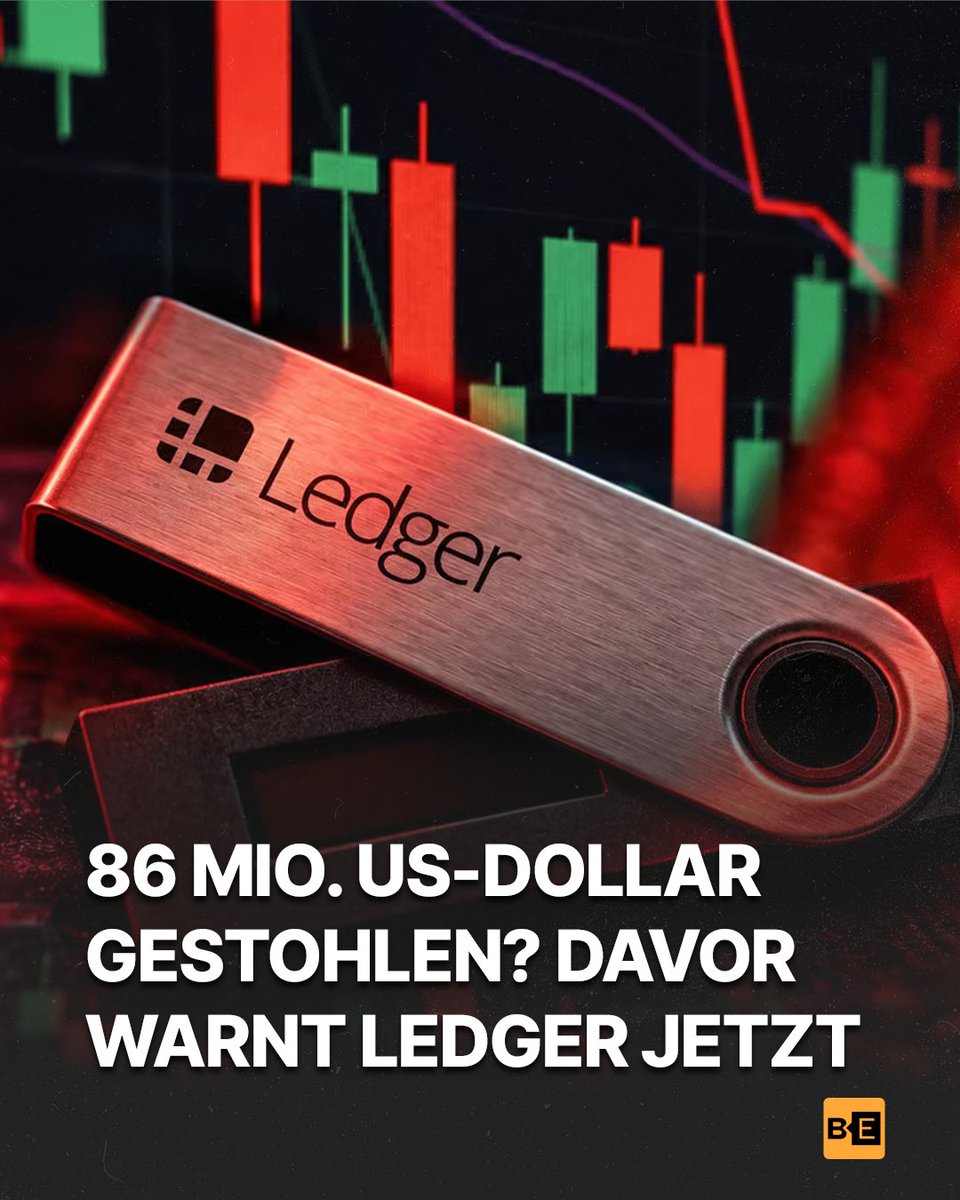
🚨 86 Millionen US-Dollar gestohlen? Ledger warnt seine Nutzer.
Auf X kursieren Berichte über mögliche Krypto-Diebstähle in Millionenhöhe. Ein Onchain-Analyst spricht von über 86 Millionen US-Dollar, die Ledger-Nutzern entwendet worden sein sollen. Bestätigt ist diese Summe bislang nicht.
Ledger selbst untersucht Berichte über Vermögensverluste bei Kunden in Südostasien, die ihre Hardware-Wallet über den Reseller CryptoBillis gekauft haben.
⚠️ Betroffenen Käufern der vergangenen 90 Tage empfiehlt Ledger, noch nicht eingerichtete Geräte vorerst nicht zu aktivieren. Wer sein Gerät bereits eingerichtet hat, sollte einen Umzug auf ein neues Gerät mit neuer Recovery Phrase erwägen.
Gleichzeitig kursieren gefälschte Ledger-Mails, die ein dringendes Sicherheitsupdate verlangen.
Wichtig: Gebt eure Recovery Phrase niemals auf einer Webseite ein oder an angebliche Support-Mitarbeiter weiter.
#Ledger #Bitcoin #Krypto #Phishing #CryptoSecurity

@hedera @GregoryLBell @Finextra @hashgraph Ledger-to-ledger trust with no bridge in the middle removes the piece institutions keep getting burned on. CLPR is one to follow closely.


The Ledger/CryptoBilis reports are a reminder to revisit this video.
Your seed phrase should NEVER arrive in the box or already be set up on the device.
For a new wallet, always generate it on the device during setup.
If someone else supplied it, it's their wallet too.
The seed phrase was already in the box.
Had so much fun scratching it off!
Amazing customer service.
Very time efficient.
⏸ Except this is exactly how people lose everything.
10/10 scam experience.

🚨⚠️ $ICP $86 MILLION+ IN REPORTED CRYPTO LOSSES — LEDGER INVESTIGATES POSSIBLE HARDWARE WALLET SUPPLY-CHAIN EXPOSURE.
And this is exactly why security must extend beyond the blockchain itself.
Ledger is investigating reports of stolen funds associated with devices purchased through its Southeast Asian reseller CryptoBilis.
📂 INCIDENT DETAILS
┃
┣ 💰 Reported losses: $86M+
┣ 🔐 Wallet provider: Ledger
┣ 📦 Reseller: CryptoBilis
┣ 🌏 Region: Southeast Asia
┣ ⛔ Reseller sales and shipments paused
┣ 🔑 Fresh recovery phrases advised for affected buyers
┗ 🔎 Root cause: NOT YET CONFIRMED
Let’s be precise.
The $86 million figure comes from on-chain analysis. Ledger has not independently confirmed that loss total or established that its hardware devices were compromised.
But the wider security implications are serious.
A blockchain can have excellent cryptography and still suffer losses when private keys, recovery phrases, devices or distribution channels are compromised.
SO WHERE DOES $ICP FIT INTO THIS CONVERSATION?
Internet Computer provides an alternative architecture for certain applications through:
🔹 Chain-key cryptography
🔹 Threshold ECDSA and Schnorr signatures
🔹 Internet Identity authentication
🔹 Canister-controlled execution
🔹 On-chain governance
🔹 Cryptographic key management across distributed nodes
With threshold signing, a complete private signing key does not need to exist on a single node.
That’s an important architectural capability.
But it does NOT make ICP wallets immune to compromised devices, stolen recovery phrases, malicious transactions or phishing.
And that’s the point.
REAL SECURITY IS NOT A MARKETING CLAIM.
It’s a combination of cryptography, secure hardware, software engineering, operational controls and supply-chain integrity.
If institutions are going to entrust blockchain infrastructure with significant assets, they need independently verifiable security, not promises of being unhackable.
The Ledger investigation deserves facts, transparency and a properly established root cause.
♾️ $ICP — THE FUTURE OF DIGITAL ASSET SECURITY WILL BE BUILT ON VERIFIABLE ENGINEERING, NOT HEADLINES.
@dfinity @Ledger
#ICP #InternetComputer #Ledger #CyberSecurity #ChainKey #CryptoSecurity #Blockchain
🏴 Welsh ICP Conviction | @ICPLEGEND1966
❤️ LIKE | 🔁 REPOST | 💬 COMMENT
♾️ ICP Donation Address:
1e672d038cebc619d93186418fa98f6499dbdb9cfdfac54f366c61a4a4ee4362