12 anos depois de ter trabalhado com o @miguel_milhao na @prozisofficial, é dia de contar a história desse capítulo do meu percurso. 💪
Sai hoje à noite o "meu" episódio do podcast CdK. Conversa longa, honesta, e acima de tudo...super divertida! 😀
Obrigado @miguel_milhao uma vez mais pelo convite, foi top!
Hot take: most companies cancelling their SaaS to vibe-code their own version will end up paying for that software twice.
The argument on here this week is that software is disposable now.
Everything is a prompt away, so why pay a vendor $100K a year?
For some tools, sure. But we've seen a lot of these at PE-backed companies, and the reality is the weekend build is cheap. Owning it is where the money goes.
A head of innovation at a PE fund-services firm told us vibe-coded prototypes are piling up in every portfolio company.
When you cancel the vendor, you sign up for all of this:
1. One owner, with a name. When that person leaves, the software leaves with them.
2. Hosting, backups, and somebody who gets the call at 3am.
3. Logins and permissions. Who sees payroll and who doesn't. The vendor used to handle that.
4. Tests, so the next change doesn't break the last one.
5. Security patches, and answers ready when your auditor asks.
6. Moving the data out of the old tool, plus every report finance built on top of it.
7. Every integration the old tool had with your other systems.
8. Drift checks, if there's a model inside it.
9. Every feature request the vendor used to absorb. That's your backlog now.
None of that shows up in the weekend demo.
In my view the split is simple. Vibe-code the disposable stuff: internal tools, one-off reports, anything you'd happily throw away in six months.
Never vibe-code your ERP, your billing, or anything your auditor or your customers touch.
The first time it breaks, you can't invoice anyone and nobody on your team knows how to fix it.
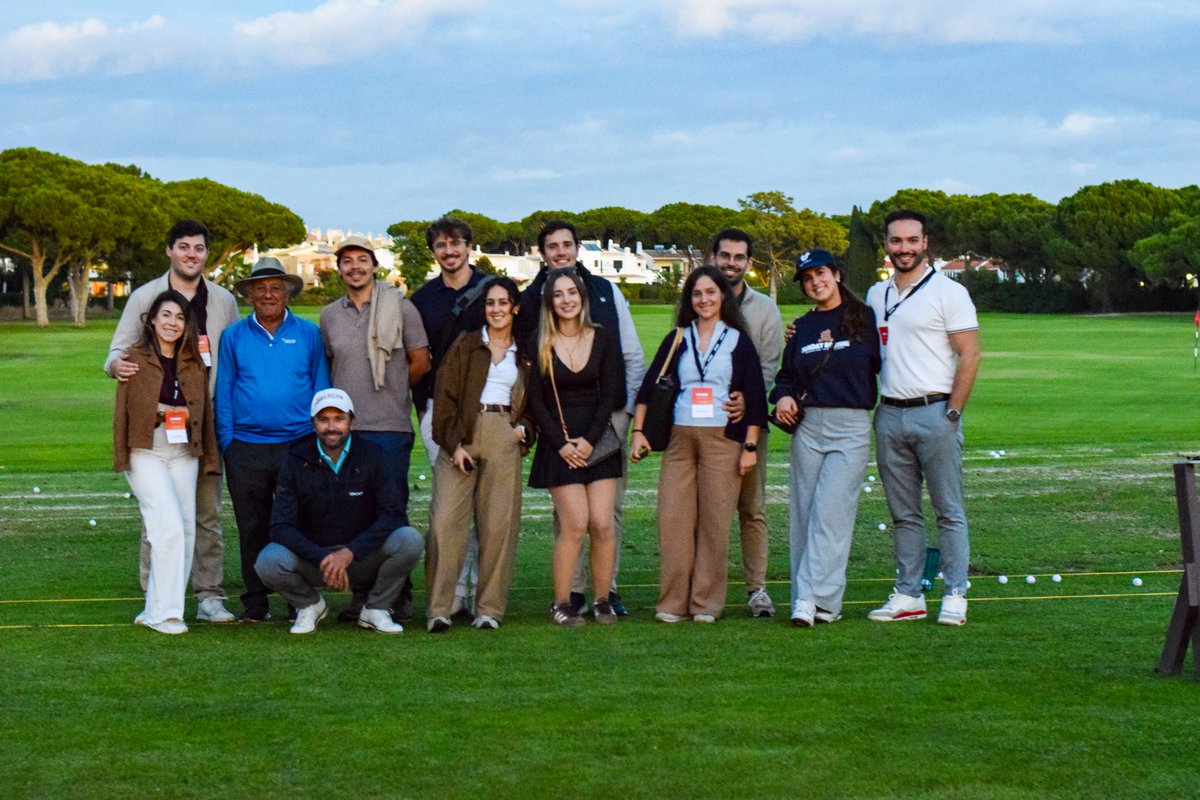
Our first Upside Weekend in Vilamoura. We brought founders and their partners, played golf, laughed all weekend and went home as friends.
That’s what Upside is for. No secrets, just founders helping founders.
https://t.co/sui8DTjuM2
To say that this past weekend was amazing is an understatement.
The 1st @joinupsideclub Weekend took place in Vilamoura, Algarve. 🇵🇹 ☀️
I was slightly tense about this event format, as for the first time ever we invited Founders to bring their partners. All while also hosting a 2-day event...also for the first time ever! 😅
Experimentation is great, and myself and @edupinto1012 love it, but it always carries some risk.
It turns out that people being with their partners just brings the experience into a whole new level. ⭐ I was nervous for no reason. We talked about work, family, friends, money, dealing with success, dealing with failure, and a whole variety of subjects.
Learning how to play 🏌♂️ Golf was definitely one of the highlights.
During the course, the most repeated sentence was: "I had no idea this was so much fun!" 🤣
Above all — the sense that we arrived as colleagues and left as friends. 🫶
No networking community comes even close to that, but it is intentionally part of what we do, which one of the reasons why I'm so excited with our @joinupsideclub 2027 plans. 🔥
BREAKING: Europe is under a massive cyber attack, with supermarket fridges and freezers in Belgium, Sweden, Luxembourg, Ireland, the Netherlands, Finland and Estonia all hacked today by raising temperatures to up to 50°C, destroying huge quantities of food, per Reuters.
"Everything is destroyed," a sales manager in Sweden said, adding that "there has been a cyberattack and all our freezers reached 50 degrees."
More than 40 supermarkets in Belgium and Luxembourg were affected. "I only have two words for them: wake up, please, because there's something going on," a store manager in Belgium said.
This follows a similar cyberattack last month that hit hundreds of supermarkets in France, raising freezers as high as 80°C and causing major food losses.
It also comes after freezers at 6 US military bases mysteriously malfunctioned, spoiling large quantities of food, which the Pentagon is investigating as a suspected cyberattack.
Friday, 2pm. In the @joinupsideclub Townhall chat, multiple Founders speak about the desire to know more about AI Search.
Friday, 6pm: an AI Search - Tips & Tricks by experts Focused Session is LIVE. 📆
Four hours from “it would be great if you guys did this” to an event in the calendar. Faster than most companies approve a meeting invite. 😅
This is the @joinupsideclub doing exactly what we built it to do.
We get people to speak and share their challenges. → We then organize events that help people overcome those challenges. → And those events are hosted by other Upside Club members.
30+ people already signed up. This one’s going to be good. 🔥
November 24, 5pm GMT+0, online. https://t.co/59xIXvVWqp
Habitação é o tema do momento. 🏠
O @Rodrigopessoaj, que é uma máquina, está por sua própria iniciativa a tentar contribuir de forma concreta para a resolução deste problema, com o seu projeto Arvilea.
O objetivo é construir o máximo de casas a preços acessíveis, com a ambição de chegar a 1.000 casas em 5 anos.
Quer fazer T2 com Jardim a ~240.000€ a 45 minutos de Lisboa. Brutal.
Para atingir este objetivo e materializar este projeto, o Rodrigo está no terreno, a fazer coisas, enquanto tenta levantar o capital para fazer isto acontecer.
Segundo sei, tem sido desafiante. E como não seria de admirar, apoio ou interesse público é perto de zero. 🤷♂️
Para resolver este problema da habitação - que existe e é obviamente um assunto sério - precisamos de mais Rodrigos e menos "acampadas".
Quem tiver interesse em investir e contribuir ativamente para a resolução do problema da habitação, fale com ele.
Any form of security through obscurity is fully over. This barely worked as a method with humans, but just simply is over in a world of autonomous systems that will look through every crevice and try every permutation of attack possible.
As a result, years and years of legacy enterprise infrastructure will need to be upgraded, security practices modernized, data pipelines cleaned up, access controls better managed, and much more. Agents will help on the defensive side because they can both accelerate this work and equally simulate the risk vectors.
But there’s a long road ahead to prepare for this future. This is also partially why diffusion timelines will take longer than some realize.
🚨 THE INTERNET IS FACING ONE OF THE WORST WAVES OF CYBERSECURITY THREATS EVER.
More than 20 major cyber incidents and security warnings have been reported in recent days, affecting banks, governments, cloud platforms and widely used software.
And some of the details are shocking.
1. PHP, used by a huge part of the web, had 2 critical flaws (CVSS 9.2) that let attackers run code remotely
2. Governments in 9+ countries took websites offline as a precaution, including France, the Netherlands, Finland, Germany, Belgium, Denmark and the UK
3. eMudhra, a certificate authority, had the keys of 8 certificates exposed. One key was the number 4
4. Railway says hackers may have accessed decrypted customer secrets
5. Zeabur was breached, with 321,810 accounts affected, and is shutting down
6. Japan's Onamae Desktop Cloud stopped up to 26,739 servers after malware was found
7. LiteLLM, a popular AI library, was poisoned and stole cloud and AI keys
8. OVHcloud's CLI tool was backdoored
9. GitLab disclosed a CVSS 10 flaw that lets attackers take over servers without logging in
10. State Bank of India confirmed 3,897 customer records on the dark web
11. Data of California students was stolen from ETS, with the intruder inside for about 4 months
12. Bullhorn took its platform offline after a cyber incident
13. Palo Alto firewalls are still being exploited by ransomware groups Qilin and Inc
14. Researchers say AI agents were used to target 400+ banks and payment companies in Latin America
15. Axios reports US banks are finding unauthorized AI agents inside customer accounts
16. Reuters reports one hacker used AI agents to break into 100+ company websites, including Deere
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
A few months ago, I posted something about @Pixelmatters_ CEO transition, and someone asked me:
What's the emotional impact of no longer being the CEO of the company you started? 🤯
I can only speak about my experience. So, please take it with a grain of salt.
My thoughts... 🧠
1️⃣ The transition from me being at the center of everything to becoming close to irrelevant happened much faster than I anticipated. I think this is due to a combination of factors, namely the outstanding work @bmfteixeira is doing but also the disruptive changes that AI is forcing every company to go through.
2️⃣ It takes a while to adapt yourself to a slower daily rythm. Not sure if I'll ever adapt to it, honestly. 😀
3️⃣ A slower day-to-day made me realize that I'll work... forever! People say that "To stop is to die" and it really is. A balance between high-intensity work and time for your stuff is clearly the sweet spot.
4️⃣ Also takes a while to adapt to an open calendar. You get so used to not having time nor being the owner of your own time that it's strange when you have it back. And of course, hard to decide what to do with it, which is one of those luxury problems to have! 😂
5️⃣ You get to do much less decisions, but the ones you make — often strategic — are both more impactful but also more long-term. So there's a delay until results come up. Gotta be patient!
6️⃣ It's phenomenal to see the culture you've helped to create and shape from the outside, especially when it actually sticks together even when you're not really around. Gives me a big feeling of accomplishment.
7️⃣ Overall, it's a step I'm increasingly proud of having made and don't regret at all. If anyone is wondering about doing it or not, feel free to send me a DM.