OWASP has adopted my open source tool CVE Lite CLI.
A lightweight, local-first vulnerability scanner for JS/TS projects focused on real fixes - not just CVE lists.
https://t.co/Wb0oFVCBNm
warpdom 0.1.12 is out: a drop-in DOM for Vitest and Jest. Same test results as jsdom, ~1.27x faster (median, 13 OSS suites). New: dark-mode system colors, shadow-tree styles, fast mode on Vitest 3.2.
Try it on your suite: npx warpdom compare
https://t.co/8XA04ZuCng
🎙️ New episode of The Ai Dev Craft Show!
@rainerhahnekamp & Murat Sari join to talk local #AI models, loop engineering, autonomous agents, & when open-weight models are ready for real development work.
🟢https://t.co/DerI8RBCMd
🍎https://t.co/ZT9FrzgLHr
📺 https://t.co/vzWUTCAiEG
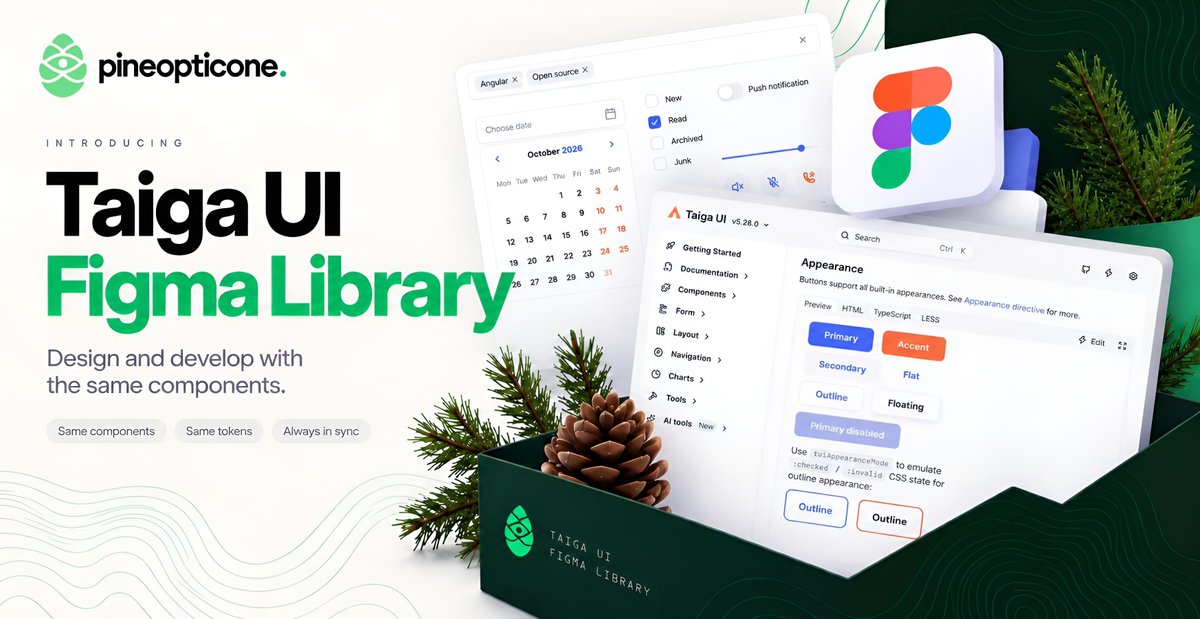
Huge news for Taiga UI!
We've heard many times that people really like the library, but without enterprise support, they don't feel comfortable adopting it within their companies. After the v5 release, we decided we're in good enough shape to vouch for it.
So we've established a dedicated company called Pineopticone to take official ownership of Taiga UI, Maskito, and other projects we develop. There is NO change to the license. Everything IS and WILL REMAIN open source and free for commercial use under Apache 2.0.
What's new is our ability to offer paid services to those who want more than just the libraries themselves and our usual support and communication channels.
Our first product available for purchase is the Taiga UI v5 Figma library. Get an individual license or a company bundle and give your designers a tool to build interfaces using Taiga UI components, with all their props and customization options at their fingertips.
If this sounds interesting to you, or you'd like to explore other partnership opportunities, such as SLAs, LTS guarantees, priority support, and whatnot – reach out using the form below:
https://t.co/Y1RbI5oQ0Z
Presented by All Knight Access in partnership with YWCA Yonkers, Shefik presents Invocation, Yonkers Public Schools, Yonkers Voice, Harlem Film House, and other notable stakeholders, NASA Space Apps Yonkers invites innovators of all ages to register for the NASA Space Apps Challenge, taking place November 14–15, 2026. The 2026 theme is "The Next Frontier", and participants from Yonkers, New York, and surrounding areas throughout Westchester County will work alongside a vibrant community of scientists, technologists, and storytellers while competing with teams at hundreds of events worldwide.
Over two days, participants will use data from NASA - National Aeronautics and Space Administration and its 17 Space Agency Partners to address pressing challenges scientists face in Earth and space exploration. In 2025, 114,000+ registered participants joined NASA Space Apps Challenge from 551 Local Events worldwide.
This year's Space Agency Partners include Angola National Space Programme; Bahrain Space Agency; Brazilian Space Agency; Canadian Space Agency | Agence spatiale canadienne; European Space Agency - ESA); Indian Space Research Organisation (ISRO); Italian Space Agency; JAXA: Japan Aerospace Exploration Agency; KASA (Korea AeroSpace Administration); Mohammed Bin Rashid Space Centre of the United Arab Emirates; National Space Activities Commission of Argentina; Nigeria National Space Research and Development Agency; Paraguayan Space Agency; Senegalese Space Studies Agency; Spanish Space Agency; Turkish Space Agency; and the UK Space Agency.
For 2026, NASA Space Apps Yonkers appoints Sonu Kapoor as Judge.
Sonu is a Microsoft MVP and Google Developer Expert for Angular with more than two decades of experience building high-performance web applications and leading technology initiatives across enterprise software, financial services, retail, media, and open source.
At Citigroup, Sonu architected the frontend of a $4 billion global trading platform, bringing real-time data streaming capabilities to traders. At American Apparel, he directed engineering for the company's pioneering RFID retail rollout, transforming supply-chain visibility and inventory accuracy. At Sony Music Publishing, he led Angular migrations and AI-driven digital transformation initiatives. He has also contributed directly to the Angular framework and worked with Cisco on frontend engineering.
Emmy® Award winner and technology maven Sir Shefik Macauley serves as Managing Director and Local Lead of NASA Space Apps Yonkers, bringing the NASA Space Apps Challenge to the Yonkers, New York community for its second consecutive year.
The event will be held in-person on November 14–15, 2026, at YWCA of Yonkers, located at 87 South Broadway, Yonkers, New York 10701, United States. Free registration is available for both in-person and virtual activities.
Activities start each day at 9 a.m. ET.
All participants of NASA Space Apps Yonkers will receive a Certificate of Participation.
Participation does not require a particular academic or professional background. A participant may contribute through programming, science, engineering, design, project management, research, communication, storytelling, business strategy, or simply a willingness to learn and collaborate. NASA specifically describes the Challenge as open to all ages.
Free Registration: https://t.co/rGGSRLMd1f
#SpaceApps #Technology #Science @shefik_info@SpaceApps@NASA@AllKnightAccess@YWCAYonkers@harlemfilmhouse@YonkersVoice@YonkersSchools@nutrioz@GriffoProd@SonuKapoor1978
https://t.co/tppy59kITJ
CVE Lite CLI has 692 GitHub stars. Help us reach 700. Free, local, OWASP-recognized dependency scanner for JS/TS projects. Gives you copy-and-run fix commands, not just CVE IDs. If you've found it useful, a star goes a long way. https://t.co/Wb0oFVCBNm #OpenSource#OWASP
CVE Lite CLI opened a security fix PR on its own repo while I was sleeping.
Found CVE-2026-45820 in fflate, validated the fix, opened the PR. Findings: 2 → 0.
The tool patched itself. That's the goal.
https://t.co/Gx9k2AjmfD
Formisch v1 is here. 🎁
A schema-first form library for 8 frameworks:
React, Vue, Svelte, Solid, Angular, Qwik, Preact & React Native.
✅ One Valibot schema = types + validation
✅ Native performance across all 8 frameworks
✅ Headless — works with your existing UI
✅ Bundle size starts at just 2.5 kB
After a lot of work, Formisch is officially stable. https://t.co/CAXQ2Xbckb
Fixed a subtle npm parser bug in CVE Lite CLI v1.29.0: transitive deps reached only through a workspace's own deps or a peer dep were showing "No parent identified" even with a real parent chain. Fixed at the graph layer, flows to every output format.
https://t.co/CX2YVgVv8C
AI security doesn’t need another checklist.
When an agent crosses a trust boundary, leaks data, or misuses a tool, that failure should become a repeatable regression test.
My latest @InfoWorld article:
https://t.co/dD5LBdNIvh
#AISecurity#OWASP
Most scanners tell you to upgrade the parent to fix a transitive CVE, even when the newer parent still pulls the vulnerable version.
CVE Lite CLI v1.28.0 (OWASP) now verifies the fix actually resolves the CVE before recommending it. Honest remediation.
https://t.co/XfFTWSmKPB
Every install is a trust decision.
We catch bad dependencies in CI. By then the package is in and the decision is made. The scanner just confirms what you shipped.
Node.js security will be won, or lost, before CI runs.
InfoWorld: https://t.co/J8V2tJiIw5
---A dependency can pass every CVE check and still be one of the riskiest things in your tree.
Abandonware pinning a transitive dep below its fix. No advisory, so scanners stay quiet. No newer version, so bots can't help.
The gap I'm closing next in CVE Lite CLI. More soon...
CVE Lite CLI was accepted into @AnthropicAI's Claude for Open Source Program.
OWASP Lab Project. 25k+ npm downloads since March. Adopted by teams at Moodys, DINUM, Discord, and BC Government.
One more external validator for the work.
https://t.co/Wb0oFVCBNm
Security doesn't fail at detection. It fails at timing.
When the scanner fires in CI, the developer is already somewhere else. The fix becomes a ticket, not a decision.
Wrote about why dependency security needs to move before the push: https://t.co/J8V2tJiIw5
OWASP CVE Lite CLI— Escanea vulnerabilidades en tus dependencias directo desde la terminal, sin que ningún dato salga de tu máquina.
✅ Gratuito y open source ✅ Proyecto incubador de OWASP ✅ npm install -g cve-lite-cli
https://t.co/6H23ThbJL7
#Ciberseguridad#OWASP#DevSecOps #VulnerabilityScanning #OpenSource #CVE
CVE Lite CLI is at 630 GitHub stars. Help us reach 700. Free, local, OWASP-recognized dependency scanner for JS/TS projects. Gives you copy-and-run fix commands, not just CVE IDs. If you've found it useful, a star goes a long way. https://t.co/wDjmf1yuq9 #OpenSource#OWASP
In the modern enterprise software development life cycle, when delivery speed is the most closely watched metric, security is often treated as an afterthought, to be run at the end of the… https://t.co/b7cTLRHAHK #ShiftLeft#DeveloperSecurity#CVE#DevOps#SoftwareDevelopment