We have an epic bug to show off soon, but after seeing the marketing and branding of the PHP bugs (it's well done and I enjoyed much), I'm not convinced we can beat that level of branding despite our bug being "holy grail of web server pwn" 😭
LLM-based AppSec vendors are converging on features, so how are customers supposed to differentiate between them?
The difference is ultimately the offensive security expertise encoded into the core of the product, and the quality and relevance of the findings that come out of it.
We have world-class hackers who have spent years finding in-the-wild vulnerabilities in real-world software and systems, as well as working directly with customers through offensive security engagements. They have accumulated practical knowledge about where meaningful vulnerabilities tend to hide, how real attackers approach complex systems, and how to distinguish an interesting weakness from something that is actually exploitable.
That expertise — and how we harness it — is fundamental to Xint. Some of these researchers are directly involved in developing, experimenting with, and improving the core engine itself, so the knowledge they gained from finding real-world vulnerabilities is continuously being translated into the product.
‼️ BREAKING: Google's Pixel 10 was remotely hacked three times in one day at Pwn2Own Ireland.
Three separate teams broke into the phone. Ikotas Labs chained multiple bugs for $300,000, the contest's top prize, and won Master of Pwn. Xint earned $150,000 and a CENSUS Labs and Mobile Hacking Lab team $112,500 for their own Pixel 10 exploits.
Google has 90 days to patch.
Had a blast competing as part of team @xint_official! Proud that all our exploits succeeded on the first try!
As always it was great meeting old and new friends! Until next time!
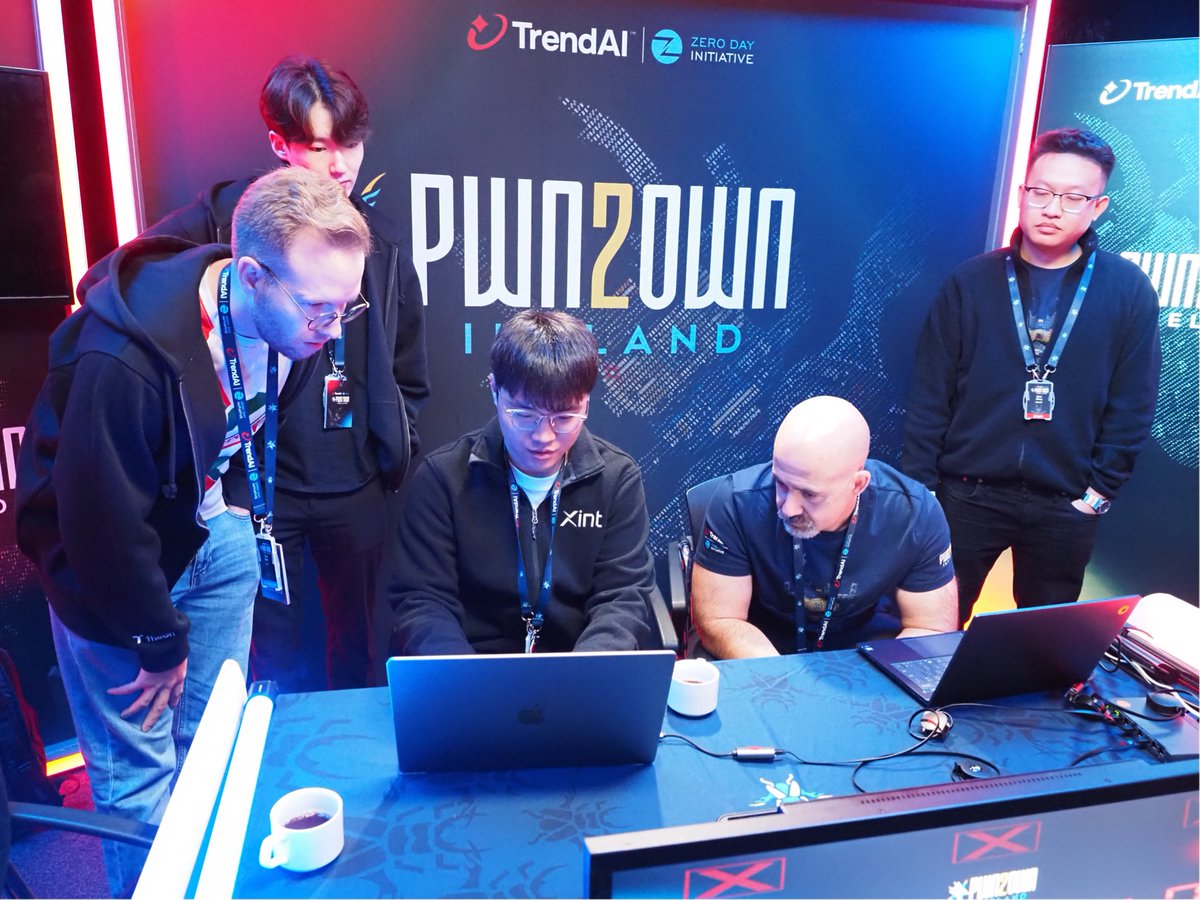
Congratulations to Team Xint (@yves_bieri@cdor1@tjbecker@taisic_) for their 2nd place finish + $240k in winnings at #Pwn2Own Ireland:
🎯 5/5 on their exploit submissions, including the Home Assistant Green, Google Pixel 10, Oracle Autonomous AI Database, LiteLLM, and Philips Hue Bridge Pro
📲 First team to hack the Pixel 10 (and might have won us the whole thing if it didn't turn out to have been a known bug)
🤝 First time we competed as team Xint
And special thank you to all the organizers and judges at @thezdi for their work making such a high quality event happen and bringing together the best talent from around the world to compete
And of course congrats to @ikotas00 on their first place finish (first Japanese team to win Master of Pwn!)
Success!! Tim Becker (@tjbecker) and Yves Bieri (@yves_bieri) of Xint (@xint_official) just remotely exploited the targeting Google Pixel 10! Stay tuned for confirmation if they will secure the total of $300,000 and 30 Master of Pwn points!
Boom! With 3 collisions and 2 unique zero-days Taisic Yun (@taisic_) of Xint (@xint_official) breached Oracle Autonomous AI Database capturing their pot of gold of $14k at #Pwn2OwnIreland and 3 Master of Pwn points #Pwn2Own
The grass may not be greener but the exploits sure were as Yves Bieri (@yves_bieri) of Xint (@xint_official) just won $30k and 3 Master of Pwn points in his takedown of Home Assistant Green #Pwn2Own
Sweet! Joohyun Park (@cdor1) of Xint (@xint_official) successfully exploited the Philips Hue Bridge Pro on his first attempt. He's off to the disclosure room with all of the details of his exploit. #Pwn2Own
Verified! Taisic Yun (@taisic_) of Xint (@xint_official) used a Improper Input Validation bug along with code injection to get his reverse shell on LiteLLM. He earns $40,000 and 4 Master of Pwn points. #Pwn2Own
Verified! Taisic Yun (@taisic_) of Xint (@xint_official) used a Improper Input Validation bug along with code injection to get his reverse shell on LiteLLM. He earns $40,000 and 4 Master of Pwn points. #Pwn2Own