🚨New arXiv preprint🚨
Unveiling ECC Vulnerabilities: LSTM Networks for Operation Recognition in Side-Channel Attacks
A joint collab with @SecPattern
Authors: A. Battistello, G. Bertoni, @0xrocky, L. Nava, @pisquo_, @teozoia, @fbpierazzi and @lanziandrea
https://t.co/Iaj3EKfsCp
On October 18th, I presented EmbedWatch: Fat Pointer Solution for Detecting Spatial Memory Errors in Embedded Systems at the CPSIoTSec2024 Workshop, co-located with @acm_ccs 2024 in Salt Lake City, Utah. Go check out the paper here https://t.co/VtLBikt7i5
Congrats to our @0xrocky on earning the https://t.co/41j4jdVAdI. last Thursday! Full marks with honors for him with his thesis: "Neural network attacks using side-channel leakages to break ECC implementations on customer electronics".
All lab members wish you the best!
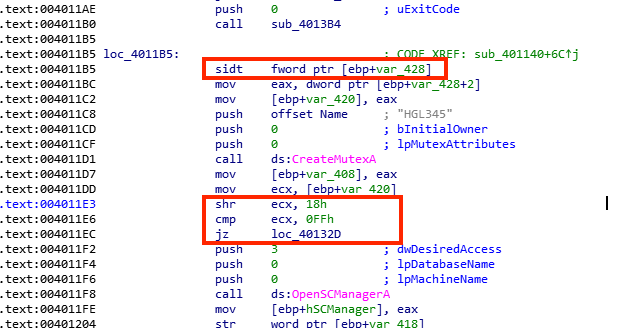
1\ Malware Analysis: Anti-VM Detection Technique
Malware can use the following instructions to detect virtualisation
> sidt, sgft, sldt, smsw, cpuid, str
These instructions are not privileged in x86 and can access hardware information to differentiate between a host vs VM 😉
Congrats to our Alberto Crosta for obtaining last Friday his MSc, full marks with honors, with the thesis "Study, comparison and evaluation of security aspects for Industrial Ethernet communication protocols".
All lab members wish you good luck!
Exciting daaay! Today I have the honor to present my 80-page thesis on Arm exploit mitigation bypasses and TrustZone attacks in front of @Arm engineers in Cambridge. ✨👩🏼💻
New video about the suidbash challenge from the Google CTF Finals 2019. It's about an actual zero-day in /bin/bash - CVE-2019-18276
🔴 https://t.co/qd02EPiuZI
Shiny Pokémon rarity has been split! Same 1:4096 odds to obtain a shiny, but there are two types of shiny. 15/16 show stars, 1/16 show squares. Square rarity is 1 in 65536!
Basically, if your Trainer ID cleanly matches the PID (xor), it will be squares rather than stars.
My first ARM project is done: bare-metal kernel to blink a LED. A deep dive into OS booting on ARM64. Special thanks to @Fox0x01 and @azeria_labs for tutorials and inspiration to build it from scratch.
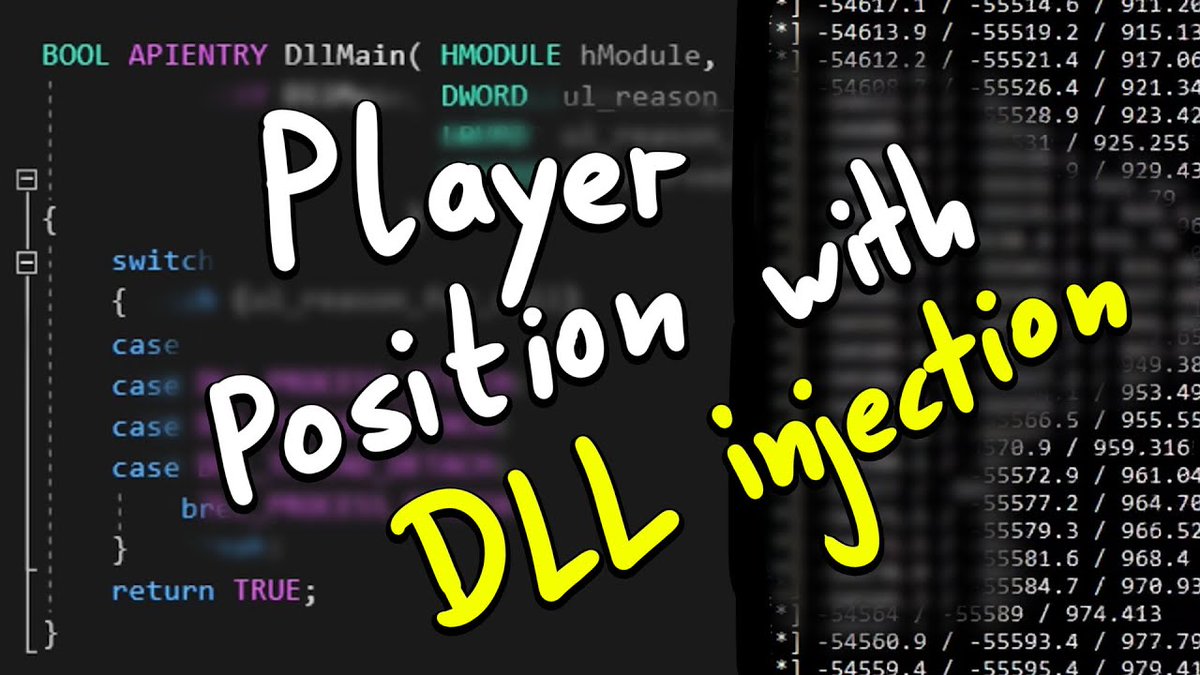
With the help from @GuidedHacking we are getting closer to a fly hack in 🌴 Pwn Adventure 3!
In this episode we create a DLL that can access the player's position in the game's memory.
https://t.co/TKhfJmOFYl
Impressive and funny talk by @b1ack0wl about his exploit development journey of a unauthenticated heap-based buffer overflow vulnerability he found.
Best talk I’ve seen in a long time! #bluehatseattle