The concerns over AI safety and cybersecurity are legitimate, but we’re risking talking America, the global AI leader, into self-inflicted obsolescence and the obscurity of bureaucracy.
The OpenAI hacking HuggingFace argument is spurious. An agent in “ExploitGym”… exploited. Our adversaries have the training techniques, the data, and the will to attack. And they won’t be slowed down with “embedded evaluators.” They’ll likely have embedded accelerators!
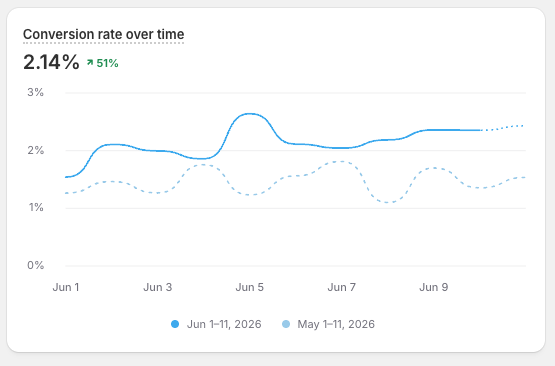
@rauchg We’ve been running https://t.co/gbw9dm198O on Next.js for a little while now and have seen a 50%+ increase in CVR month to date.
We’re able to A/B test and ship extremely fast.
Vercel + Shopify is too good…
https://t.co/DHNo9pIOaK by @foda:
◾ 500+ orders processed in *2 minutes*
◾ Built with @v0 + @cursor_ai
◾ Fully custom @nextjs storefront on headless
So long on the web.
Anyone can now dream → build → ship → sell
@austriker27 I looked into the Cloudflare route, but apparently Shopify doesn’t let you proxy Cloudflare in front of their services since they’re already running their own Cloudflare protection
I haven’t, that’s interesting. I’ll have to look into that more.
My initial thought is that it’s someone monitoring our product catalog for new products, price changes, etc., so they can generate AI versions of our designs and post them on Amazon almost immediately.
If you search our product names on Amazon, there are cheap, print-on-demand AI knockoffs.