Around one month ago I started my OSED journey.
If you want to get into binexp as well, feel free to check out my OSED GitHub repository containing lots of resources & practice binaries:
https://t.co/iSLlgUBDoe
The @x33fcon conference was once again a complete success!
I wanted to share the slides and demo videos from the "Downgrading FIDO MFA With AI Slop" talk I gave on the second day (the next day after the pirate ship party... ugh). 😵💫
Slides: https://t.co/zJ2JdLazbQ
Feel free to reuse the images and demo videos from the talk in your own presentations.
Extremely happy to have had a chance to hang out with old friends and meet new faces from the Evilginx community.
See you most definitely next year in Gdynia! 💗
Doxing people from the pirate ship photo:
Front: @bongoalex@BigM1ke_oNe@thenopcode
Back: @Jean_Maes_1994@TimMedin
I'll be @BSidesVienna next week to talk about uhhh things.
There probably will be: assembly, bugs, exploits, AI obviously.... actually, we will see about those details when I find the time to create the slides, so most likely ~5 hours before the con
Anyways, see you there!
After more than 3 years, I finally found the time to update my blog and write something new.
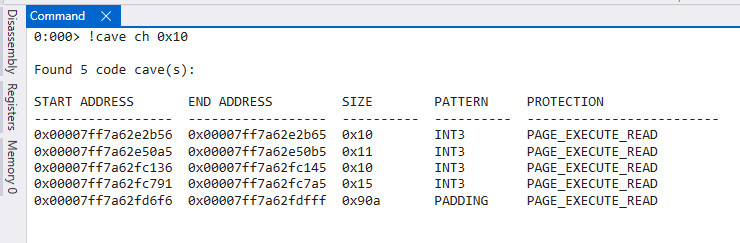
So here is a short post about a simple WinDbg extension I wrote to find code caves (definitely an improvement from the messy Python code I wrote back then):
https://t.co/8f9C6YGN1i
Our newest blog post for CVE-2026-22601, CVE-2026-22602, CVE-2026-22603 and CVE-2026-22604 is live:
https://t.co/J6Ck4fKc2c
@kingcope_MTD found some nice vulnerabilities in OpenProject. Great work! 💪
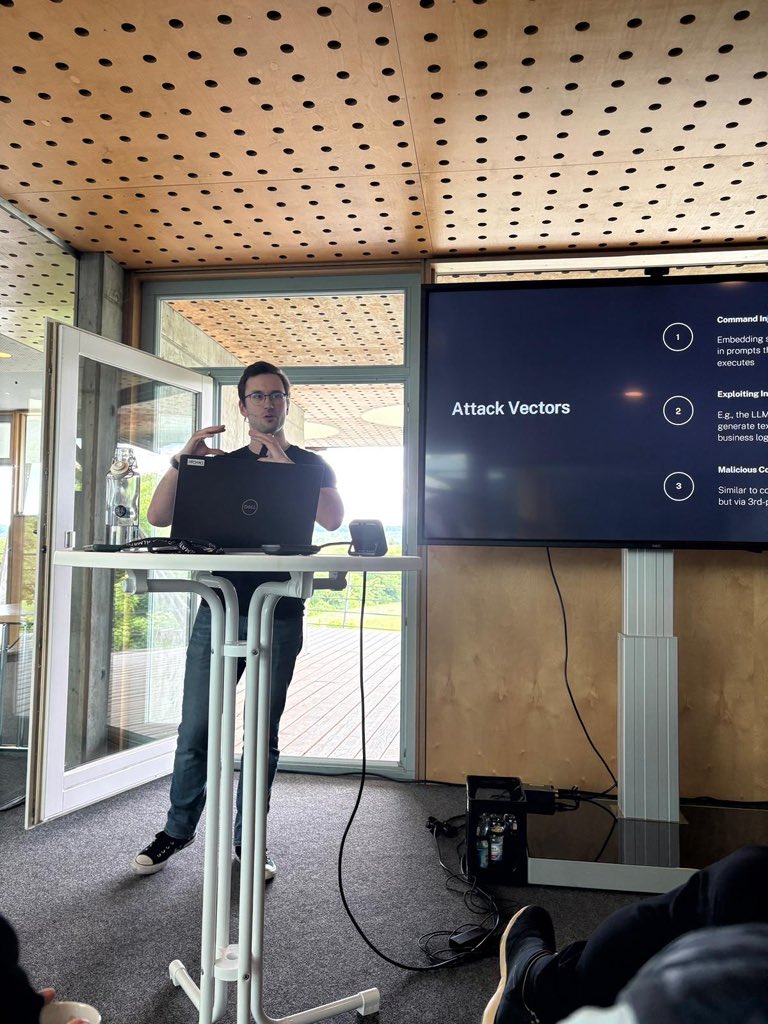
„Generative AI in the Crosshairs - Angriffe auf KI & LLMs“ - @thenopcode hat einen interessanten Talk im Rahmen der heutigen #AlmatoDevCon gehalten! 😎
Back to reality after another amazing edition of @offensive_con
Thank you to everyone that made this conference and the parties as great as usual and see you again next time!