Fifteen years ago, I co-founded MDSec. Today, that journey comes to an end.
In that time, we’ve written books, spoken at almost every major conference, and discovered and exploited more 0-days than I could count. We’ve hacked banks, $tock exchanges, tech giants, frontier AI orgs and all manner of companies in between. We’ve jackpotted ATMs, intercepted money from payment systems, compromised mainframes, beaconed mobile devices and got r00t more times than I can remember.
A huge thank you to everyone on the MDSec team and all the MDSec alumni, who helped make it such a wild ride. I’m immensely proud of what we built. And to all our customers, past and present, thank you for the trust and opportunities you gave us.
I’m excited for the next chapter. If the next 15 years are anything like the last, it’s time to strap in.
Working RCE against PHP 8.5.12 (the 2026-10-21 security release that fixed CVE-2026-109618/109619).
Pure logic bug — no memory corruption,
ASAN-clean, orthogonal to the CVE-2026-109618/19 class.
Receipt: uid=33(www-data) over HTTP, one-shot
#infosec#php2shell#php
"On October 21st at 07:41 UTC, more than six hours before the coordinated release, Chainguard unilaterally broke the embargo and published built images containing the fix. Like other distributors, Chainguard had received the patch in advance so its users could update the moment the vulnerabilities were disclosed. Any attacker could now study the fix in binary form while every other PHP user was still waiting for the release. This disregarded weeks of work by many parties toward a coordinated disclosure."
https://t.co/hszd7sh0NI
Phantom Killer: EDR evasion via Lenovo driver
Researcher Jehad Abu Dagga from e& UAE (etisalat and) reverse-engineered the "BootRepair.sys" driver used by Lenovo PC Manager and uncovered critical security flaws that can be abused:
📌 The device" \Device\BootRepair" created by the driver has no defined DACL, allowing any low-privileged user to interact with it.
📌 The IOCTL dispatcher doesn’t verify permissions when invoking the process termination function ("sub_14000198C")
📌 A symbolic link "\DosDevices\BootRepair" is created in user space, allowing direct access to the device from user space.
⚠️ The developed PoC can terminate any process by specifying its PID.
🥷 Key advantage for an attacker: the driver is legitimate and signed by Lenovo, allowing it to bypass Driver Signature Enforcement (DSE) checks.
🎯 Attack scenarios:
✅ If the driver is already loaded on the system: any low-privileged user can access it without restrictions and terminate any process, including EDR/AV.
✅ If the driver isn’t loaded: an attacker can load the trusted, signed driver (Bring Your Own Vulnerable Driver — BYOVD attack) and then use it to kill protected processes.
📎Article: https://t.co/55b3p0i5jR
🦠PoC: https://t.co/PsxH2XCoG8 -> (https://t.co/Qv6Homv0gX), https://t.co/Qv6Homv0gX
#dbugs_attacks
Introducing nginx-poolslip, a fresh RCE for the the latest nginx release 1.31.0.
nginx-rift has been patched, but our security agent Vega has found a new 0 day.
We will release the full technical writeup with ASLR bypass 30 days after the patch on https://t.co/LAhOC5UHrp.
Security things from the last few days:
- CopyFail (linux pwn'd)
- CopyFail 2/Dirty Frag
- 13 advisories in Next.js
- Over 70 CVEs addressed in MacOS 26.5
- ~50 CVEs addressed in iOS 26.5
- YellowKey (Windows Bitlocker pwn'd entirely)
- GreenPlasma (Windows privilege escalation)
- CVE-2026-21510 and CVE-2026-21513 confirmed to be used by Russia for Windows RCE
- CVE-2026-32202 separately confirmed to be used by Russia for sensitive document access
- Mini-Shai Hulud (over 300 JS and Python packages compromised via GitHub Action cache poisoning)
- Google confirms they have identified AI-powered exploitation of zero days in an unidentified "open-source, web-based system administration too"
- Canvas (popular LMS used in most schools) pwn'd entirely
- PAN-OS (palo alto networks) pwn'd with a 9.3 severity CVE-2026-0300
Are you scared yet?
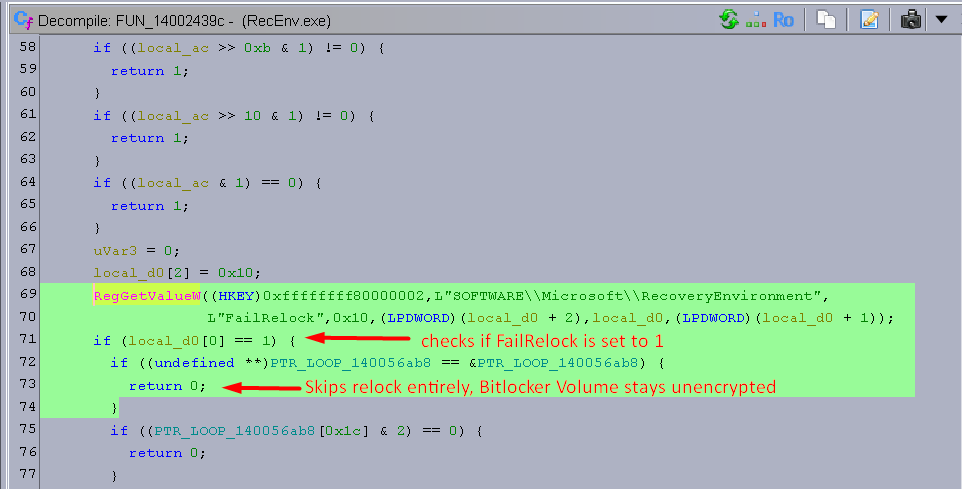
I just reverse engineered the YellowKey BitLocker bypass
Microsoft shipped code that checks for a flag called "FailRelock" in every Windows 11 recovery image. When it's set to 1, after recovery unlocks your BitLocker drive, it never relocks it. All you need is a USB stick.
This code only exists in the recovery environment. Not in normal Windows. They left an entire debug testing framework in production.
I'm using AI to find vulnerabilities (for 2 days), and its crazy how easy it is... currently fuzzing libpng which is being used by practically anything, already 3 different CVEs, memory corruption, memory leak and DoS.
$20 is cheaper than a full time vuln researcher
The man who killed the $10,000 GPU myth.
He did it alone, from Bulgaria, with one C file. 🤯
>Meet Georgi Gerganov.
>Bulgarian developer. Nobody had heard of him.
>In March 2023, Meta’s LLaMA model leaked online
>Within days he wrote a single C file
>Called it llama.cpp
>It ran a full AI model on a MacBook. No GPU. No cloud.
>The entire AI industry said you needed $10,000 GPUs to run LLMs 🔥
>He proved you didn’t. On a laptop. Alone.
>Also built whisper.cpp ~ same thing for voice AI
> His code is the foundation of Ollama, LM Studio, and GPT4All
>107,000+ GitHub stars. Fastest open-source AI project to hit 100K ever. 🚀
>In 2026 Hugging Face hired his entire team
>Still ships code. Still open source. Still free.
Every time you run AI locally, you’re running his work.
Absolute Legend 🐐